
oracle-xxe-sqli
 securityartwork/oracle-xxe-sqli
Automated Oracle CVE-2014-6577 exploitation via SQLi
database-securityexploitationpenetration-testing+2
securityartwork/oracle-xxe-sqliAutomated Oracle CVE-2014-6577 exploitation via SQLi
 rockmelodies/django_sqli_target_cve-2025-64459
Exploit tool for CVE-2025-64459, targeting SQL injection vulnerabilities in Django applications. Enables automated testing and exploitation of…
 osvaldotenorio/cve-2024-48325
Proof-of-concept for SQL injection in Portabilis i-Educar 2.8.0, demonstrating unauthenticated database access via the getDocuments endpoint with…
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
 betterdb-inc/monitor
Real-time monitoring and slowlog analysis for Valkey and Redis databases with anomaly detection, ACL auditing, and Prometheus metrics export.
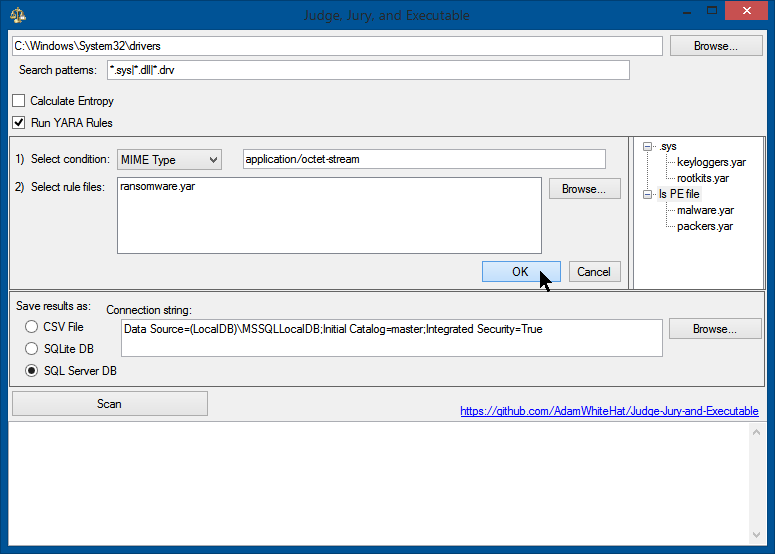 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 ishwardeepp/cve-2025-1094-poc-postgre-sqli
Proof-of-concept emulation and analysis of CVE-2025-1094, a critical PostgreSQL SQL injection vulnerability. Includes Docker-based lab setup, exploit…
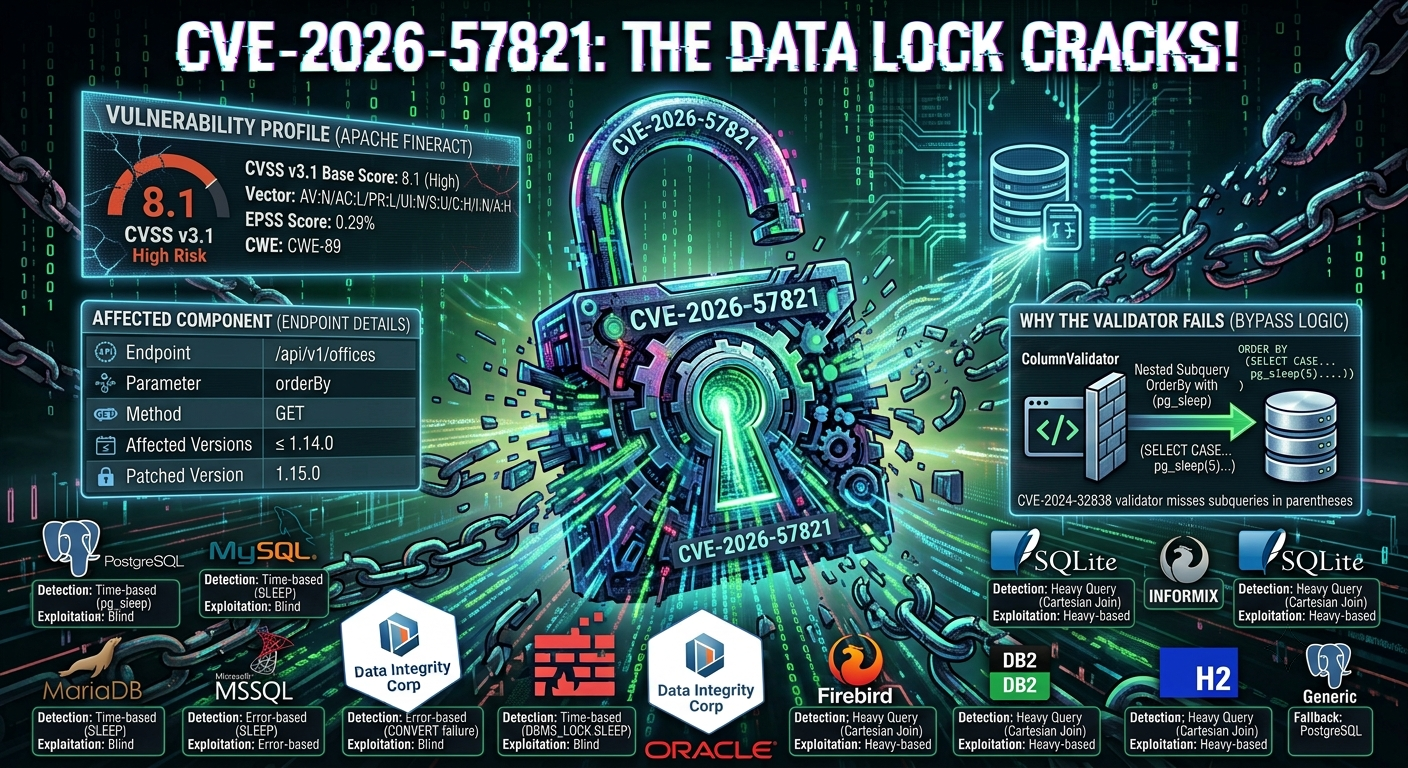 tc4dy/cve-2026-57821-poc-exploit
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
 sw0rd1ight/cve-2025-57833
Analysis and reproduction of CVE-2025-57833
 biitts/cve-2026-52887-nocobase-sqli-rce
CVE-2026-52887 — NocoBase SQL injection -> PostgreSQL-superuser RCE (myInAppChannels:list filter, CVSS 10.0). Author PoC + source analysis + docker…
 afnaan-ahmed/cve-2025-14598
Technical advisory and analysis of CVE-2025-14598, a critical unauthenticated SQL injection in BET e-Portal enabling database manipulation and…
 joakimbulow/cve-2026-34308
Proof-of-concept for CVE-2026-34308, a MySQL Server JSON component denial-of-service vulnerability. Demonstrates stack exhaustion via deep $ref…
 giangdurian/cve-2023-25157-geoserver-sqli-lab
Docker-based vulnerable lab and detailed PoC report for CVE-2023-25157/25158 SQL injection in GeoServer & GeoTools, with 4 verified attack vectors…