
-CVE-2021-26904
 security-avs/-cve-2021-26904
LMA ISIDA Retriever 5.2 allows SQL Injection
database-securityexploitationpenetration-testing+2
security-avs/-cve-2021-26904LMA ISIDA Retriever 5.2 allows SQL Injection
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 sqlancer/sqlancer
Automated testing to find logic and performance bugs in database systems
 sqlmapproject/testenv
A collection of web pages vulnerable to SQL injection flaws
 saferman/cve-2020-7471
django 漏洞:CVE-2020-7471 Potential SQL injection via StringAgg(delimiter) 的漏洞环境和 POC
 t0x1cx/cve-2021-36396-moodle-time-based-sqli-exploit
This script demonstrates a time-based blind SQL injection on Moodle platforms, exploiting response delays to extract data.
 deepingh0st/cve-2022-28346
Django QuerySet.annotate(), aggregate(), extra() SQL 注入
 0xsemz/magento-cve-2019-7139-sqli-poc
Python proof-of-concept exploit for CVE-2019-7139, an unauthenticated SQL injection in Magento's product_frontend_action endpoint, enumerating…
 dinosn/ghost-cve-2026-26980
CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)
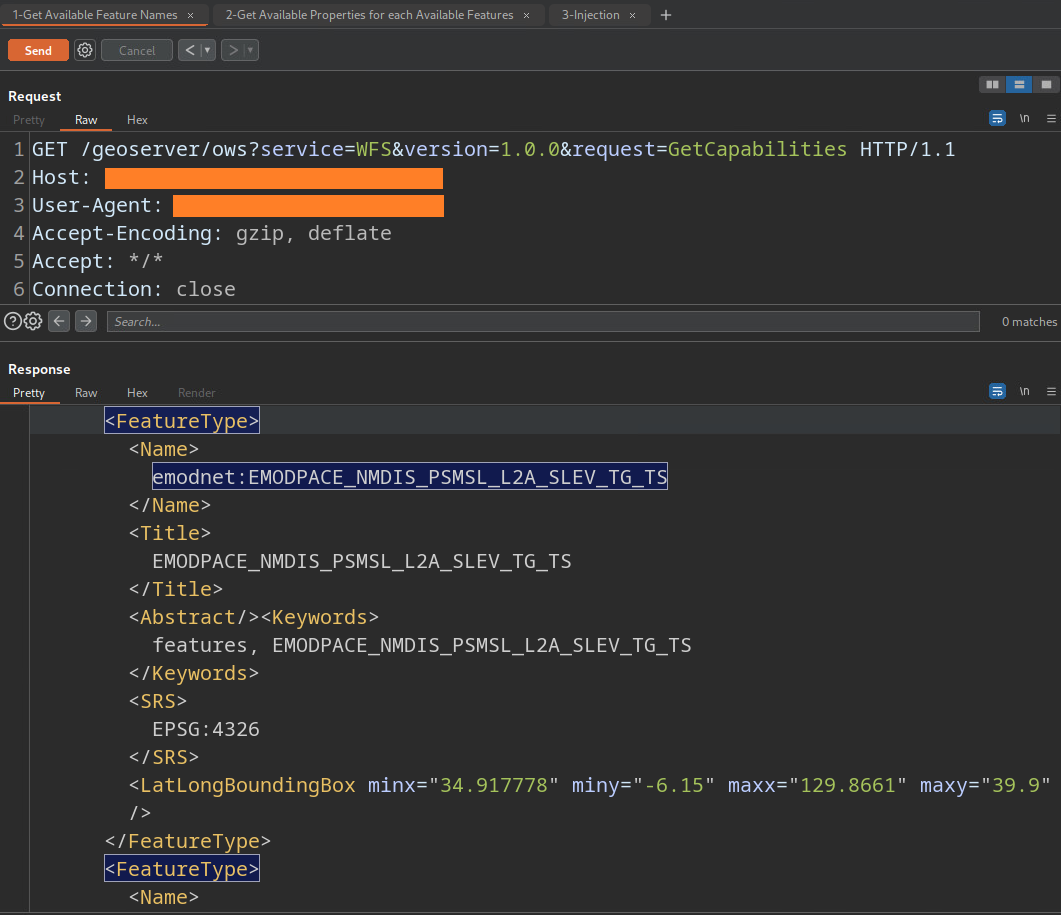 murataydemir/cve-2023-25157-and-cve-2023-25158
GeoServer & GeoTools SQL Injection (CVE-2023-25157 & CVE-2023-25158)
 assalielmehdi/cve-2017-12635
Case study and POC of CVE-2017-12635: Apache CouchDB 1.7.0 / 2.x < 2.1.1 - Remote Privilege Escalation
 oscarbataille/cve-2025-26794
CVE-2025-26794: Blind SQL injection in Exim 4.98 (SQLite DBM)- exploit writeup
 gbrsh/cve-2024-1071
Ultimate Member Unauthorized Database Access / SQLi
 abraxas/cve-2026-79752
CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
 0xdaeras/cve-2024-51482-poc
Time-based SQL injection PoC for CVE-2024-51482 in ZoneMinder, with reproducible Docker lab and automated data extraction.
 bridgeralderson/cve-2024-51482
ZenoMinder Blind SQL Injection PoC
 geniuszly/cve-2019-9193
is a PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in specific versions of PostgreSQL (9.3 - 11.7)
 sw0rd1ight/cve-2025-57833
Analysis and reproduction of CVE-2025-57833