
CVE-2025-70828
 xiaoxiaoranxxx/cve-2025-70828
Datart v1.0.0-rc.3 JDBC Connection String Injection Leading to Arbitrary File Read
database-securityexploitationinformation-gathering+3
4
xiaoxiaoranxxx/cve-2025-70828Datart v1.0.0-rc.3 JDBC Connection String Injection Leading to Arbitrary File Read
 ywh-jfellus/cve-2026-65761
Proof of Concept for CVE-2026-65761 - EasyStore Pro Unauthenticated SQL Injection via `filter_sortby`
 shad0w0sec/cve-2023-1454-exp
JeecgBoot SQL(CVE-2023-1454)sqlmap 注入不出来的情况可以使用该脚本
 romain-deperne/cve-2026-41490
Detailed CVE-2026-41490 disclosure with PoC demonstrating unauthenticated SQL injection in Dagster database I/O managers via dynamic partition keys,…
 rahulreddykarne/cve-2026-65321-pyathena
SQL injection in PyAthena via DefaultParameterFormatter (CVE-2026-65321)
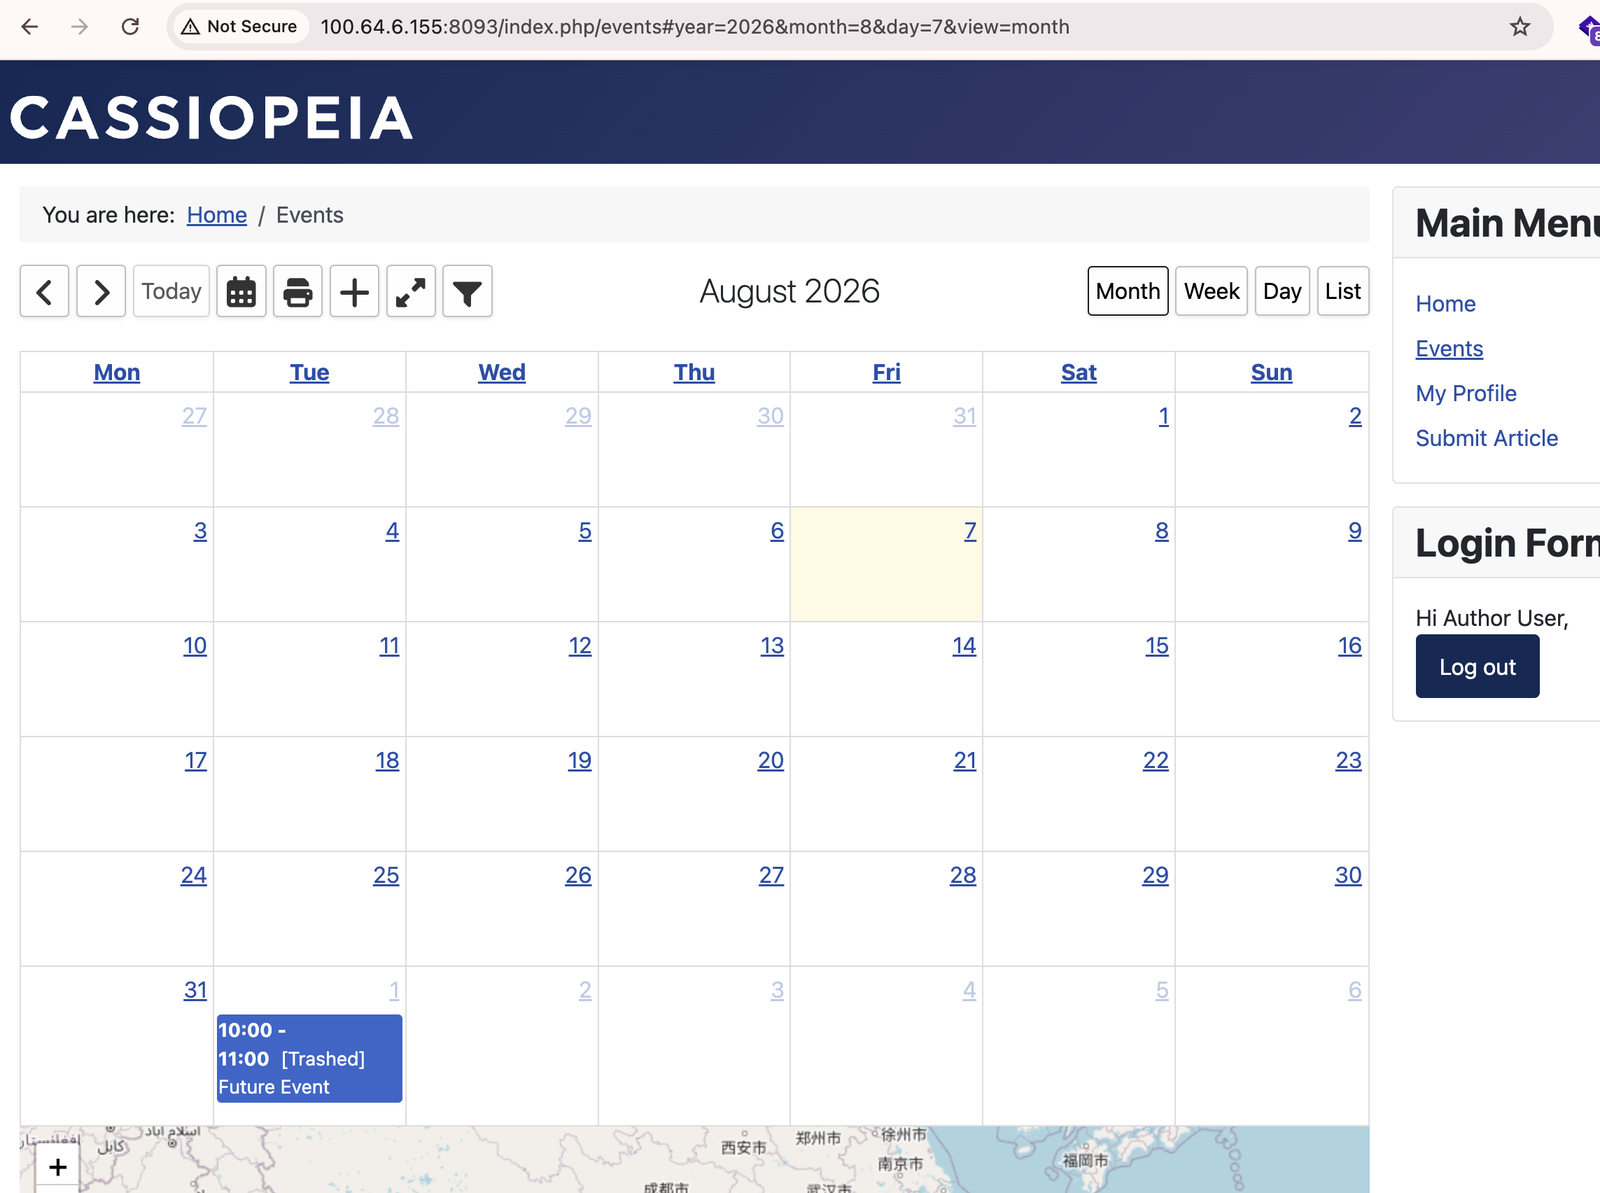 toanln-cov/cve-2026-78070
SQL Injection via ORDER BY Shortcode in plg_content_dpcalendar — DPCalendar Free ≤ 10.11.2
 l0lsec/cve-2021-3262
CVE-2021-3262 - Blind SQL Injection in the editOEN parameter of TripSpark VEO Transportation / NovusEDU. Unauthenticated, internet-facing. Payloads,…
 nabeelmkhan/cve-2026-78837
Proof-of-concept exploit for CVE-2026-78837, an unauthenticated SQL injection in AppNitro MachForm v30 allowing enumeration of database column names…
 xbz0n/cve-2024-32136
Proof-of-concept exploit for CVE-2024-32136, a post-authenticated SQL injection in BWL Advanced FAQ Manager 2.0.3, demonstrating time-based database…
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
 anusha-khan29/cve-2025-70149-sql-injection
Security research project — SQL Injection vulnerability exploitation and mitigation
 20000419/cve-2026-39113
Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…
 xiaoxiaoranxxx/cve-2025-70829
An information exposure vulnerability in Datart v1.0.0-rc.3 allows authenticated attackers to access sensitive data via a custom H2 JDBC connection…
 5170temp/cve-2026-25212
POC for CVE-2026-25212
 straightsang/h2-database-cve-2022-23221
vulhub/H2-database/CVE-2022-23221
 isaca0315/cve-2026-44840-poc
Docker lab reproducing CVE-2026-44840, a DQL injection in Dgraph's checkUserPassword GraphQL query, with exploit script and vulnerable vs patched…
 romain-deperne/cve-2026-33980
Proof-of-concept exploit for KQL injection in adx-mcp-server via the table_name parameter, enabling data exfiltration and destructive commands in…
 luckybool1020/cve-2018-8045
Joomla内核SQL注入漏洞原理、docker及poc[基于pocsuite框架]