

CVE-2017-12635
 assalielmehdi/cve-2017-12635
Case study and POC of CVE-2017-12635: Apache CouchDB 1.7.0 / 2.x < 2.1.1 - Remote Privilege Escalation
database-securityeducationexploitation+4
10
assalielmehdi/cve-2017-12635Case study and POC of CVE-2017-12635: Apache CouchDB 1.7.0 / 2.x < 2.1.1 - Remote Privilege Escalation
 ishwardeepp/cve-2025-1094-poc-postgre-sqli
Proof-of-concept emulation and analysis of CVE-2025-1094, a critical PostgreSQL SQL injection vulnerability. Includes Docker-based lab setup, exploit…
 galisko/cve-2025-24799
Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
 sw0rd1ight/cve-2025-57833
Analysis and reproduction of CVE-2025-57833
 publicqi/cve-2024-46981
Proof-of-concept exploit for CVE-2024-46981 targeting Redis 6.2.11, demonstrating a remote code execution vulnerability in the in-memory data store.
 george0papasotiriou/cve-2023-3163-sql-injection-prevention
A simple and quick way to check if your SQL Developer by Oracle is vulnerable to SQL Injection (CVE-2023-3163), most commonly occurs when SQL…
 jjcjgo/cve-2026-38812-ruoyi-sql-injection
Proof-of-concept exploit for CVE-2026-38812, a SQL injection vulnerability in RuoYi v4.8.2 via the /tool/gen/createTable endpoint, enabling…
 het-kalariya/cve-2026-20253
Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…
 lauxjpn/corruptqueryaccessworkaround
The latest workaround for the "Query is corrupt" error introduced with CVE-2019-1402
 xbz0n/cve-2024-32136
Proof-of-concept exploit for CVE-2024-32136, a post-authenticated SQL injection in BWL Advanced FAQ Manager 2.0.3, demonstrating time-based database…
 0xcyberstan/cve-2025-64459-poc
Vulnerability: SQL Injection via QuerySet and Q() keyword argument unpacking. CVE ID: CVE-2025-64459 Severity: Critical (CVSS 9.1) Affected Versions:…
 lukasz-rybak/cve-2025-65950
Proof-of-concept exploit for a critical time-based blind SQL injection vulnerability in WBCE CMS, enabling low-privileged users to execute arbitrary…
 sho-luv/mongobleed
CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…
 safe3s/cve-2022-21661
The first poc video presenting the sql injection test from ( WordPress Core 5.8.2-'WP_Query' / CVE-2022-21661)
 xbz0n/cve-2024-33911
Proof-of-concept exploit for CVE-2024-33911, a post-authenticated SQL injection vulnerability in The School Management WordPress plugin v10.3.4,…
 afnaan-ahmed/cve-2025-14598
Technical advisory and analysis of CVE-2025-14598, a critical unauthenticated SQL injection in BET e-Portal enabling database manipulation and…
 msd0pe-1/cve-2023-31714
Proof-of-concept exploit for CVE-2023-31714, a pre-authentication SQL injection in Chitor-CMS < 1.1.2. Automates database enumeration and credential…
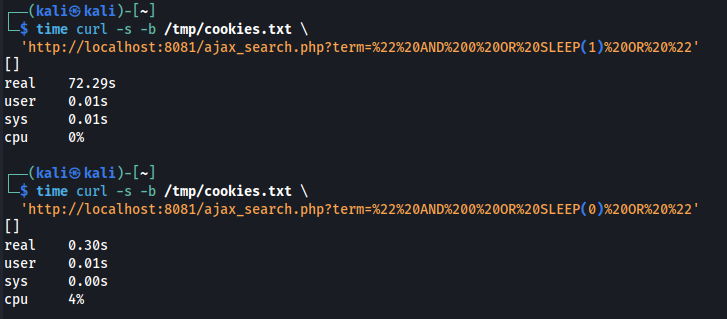 lukasz-rybak/cve-2026-24417
CVE-2026-24417 - OpenSTAManager has a Time-Based Blind SQL Injection with Amplified Denial of Service