

mongobleed-exploit-CVE-2025-14847
 franksec42/mongobleed-exploit-cve-2025-14847
Explot, Lab, Scanner - external and docker container, for SMongobleed-CVE-2025-14847 plus phoenix security uploader
cloud-securitycontainer-securitydatabase-security+6
franksec42/mongobleed-exploit-cve-2025-14847Explot, Lab, Scanner - external and docker container, for SMongobleed-CVE-2025-14847 plus phoenix security uploader
 zhaoqi99/cve-2022-34265
PoC for CVE-2022-34265
 secforce/cve-2008-1613
RedDot CMS versions 7.5 Build 7.5.0.48 and below full database enumeration exploit that takes advantage of a remote SQL injection vulnerability in…
 sudo-sakib/cve-2025-25964
A critical SQL Injection vulnerability (CVE-2025-25964) discovered in the School Information Management System v1.0
 traumatising/cve-2022-34265
CVE-2022-34265 Vulnerability
 bridgeralderson/cve-2026-24418
OpenSTAManager v2.9.8 and earlier contain a critical Error-Based SQL Injection vulnerability in the bulk operations handler for the Scadenzario…
 adarshthakur14777-cyber/cve-2026-60137
wpsqli full SQLi extractor + dumper for CVE-2026-60137
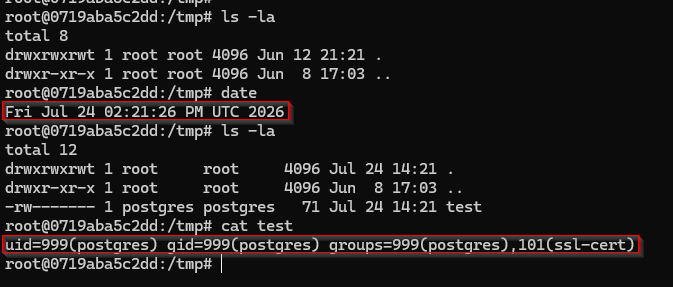 theliimbo/cve-2026-51992
Proof-of-concept and detailed writeup for CVE-2026-51992, an SQL injection vulnerability in ClickHouse PostgreSQL dictionaries allowing arbitrary…
 synacktiv/cve-2025-59213
Unauthenticated SQL injection exploit for Microsoft Configuration Manager (SCCM) 2503, enabling arbitrary SQL execution on the site database via the…
 open-flaw/cve-2026-2005
PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…
 galisko/cve-2025-24799
Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
 goldendivider/cve-2026-6471-postgres-logical-decoding-dlopen
Proof-of-concept exploit for CVE-2026-6471, demonstrating privilege escalation in PostgreSQL via logical decoding dlopen to achieve arbitrary code…
 george0papasotiriou/cve-2026-21004-sqlite-fts3-match-infoleak-via-query-crafting
Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
 joshuavanderpoll/cve-2025-14847
CVE-2025-14847 (MongoBleed)
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 jhnhnck/cve-2019-9193
PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in certain versions of PostgreSQL (9.3 - 11.7)
 34zy/cve-2026-72898
Python exploit for CVE-2026-72898, an unauthenticated SQL injection in Metabase's password reset endpoint that creates admin accounts and extracts…