metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…

Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more

High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…

This repository contains the scanner component for Greenbone Community Edition.

Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…

Python PoC for CVE-2026-48842, a pre-auth SQL injection in Roundcube's virtuser_query plugin. Confirms the flaw via time-based differential and…

🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…

Web vulnerability scanner written in Python3

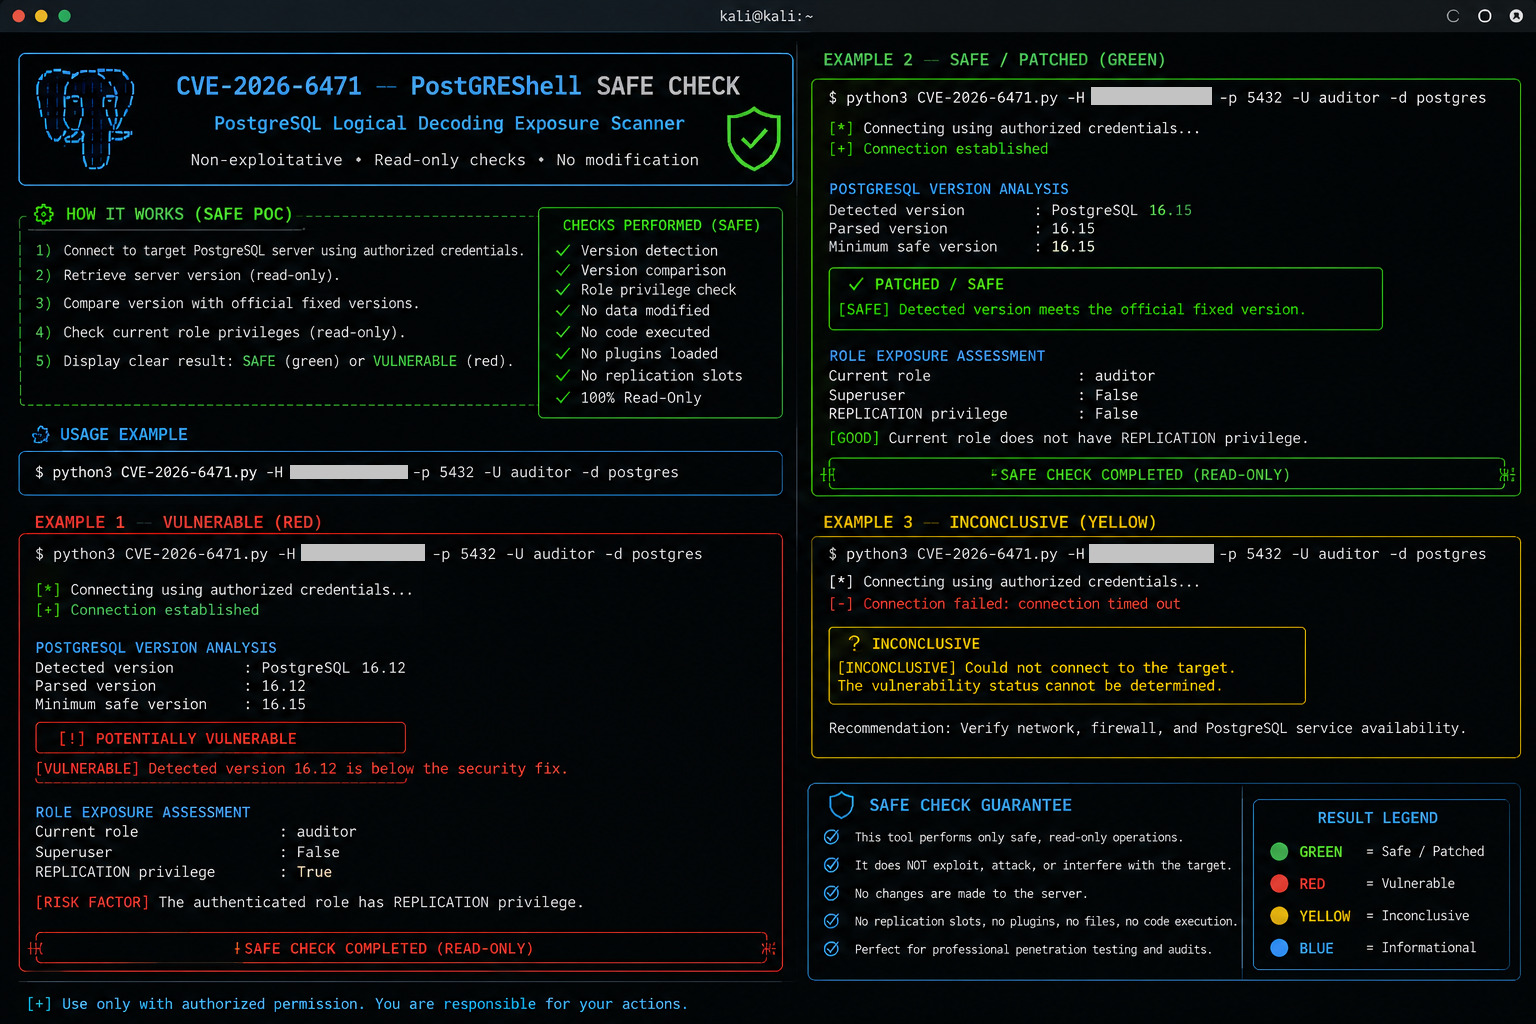
Non-destructive PostgreSQL vulnerability checker for CVE-2026-6471. Audits server version and REPLICATION privileges to identify exposure to logical…

Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.

Proof-of-concept and vulnerable Node.js/Express/Sequelize app demonstrating CVE-2026-30951, a JSON cast-type SQL injection in Sequelize v6 where…

Sequelize JSON Cast SQL Injection

Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…

Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…

wpsqli full SQLi extractor + dumper for CVE-2026-60137