CVE-2026-57588-Nessus-XML-Import-SQL-Injection-PoC

PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…

PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…

Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…

Time-based blind SQL injection proof-of-concept for LiteLLM v1.65.4. Exploits the `/key/block` endpoint to extract database contents and read server…

Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…

Java JDBC driver for SQLite databases with native library support across major operating systems, enabling standard database connectivity without…

Curated collection of Google dork queries for advanced search engine reconnaissance, uncovering exposed databases, configuration files, admin panels,…

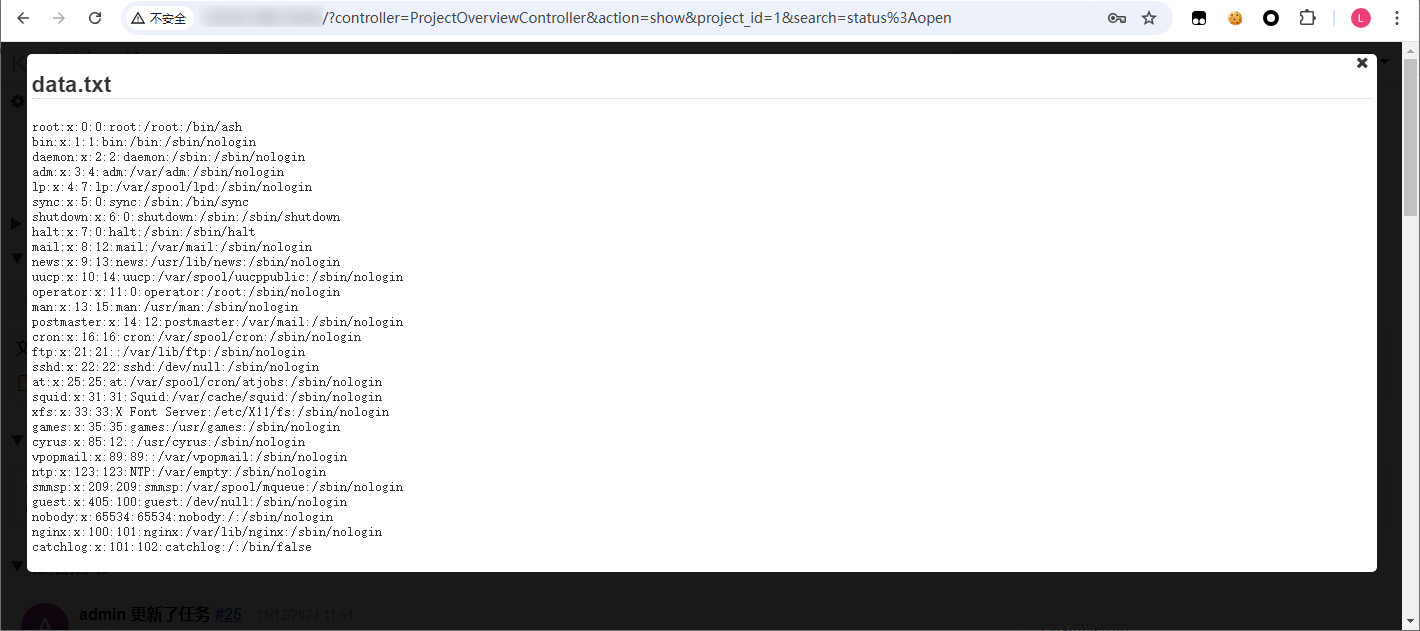
Proof-of-concept exploit for CVE-2024-51747 enabling authenticated file read and deletion via SQLite database manipulation in a web application's…

Remotely delete access logs, Windows event logs, databases, and files on target machines using automated scanning or manual attack selection for…

CVE-2024-22369 Reproducer


A collection of web pages vulnerable to SQL injection flaws

This Python 3 script is for uploading shell (and other files) to Windows Server / Linux via Oracle 11g R2 (CVE-2010-3600).


MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…