vulnerablecode
Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…

Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…

🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…

Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.

Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…

wpsqli full SQLi extractor + dumper for CVE-2026-60137

CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database

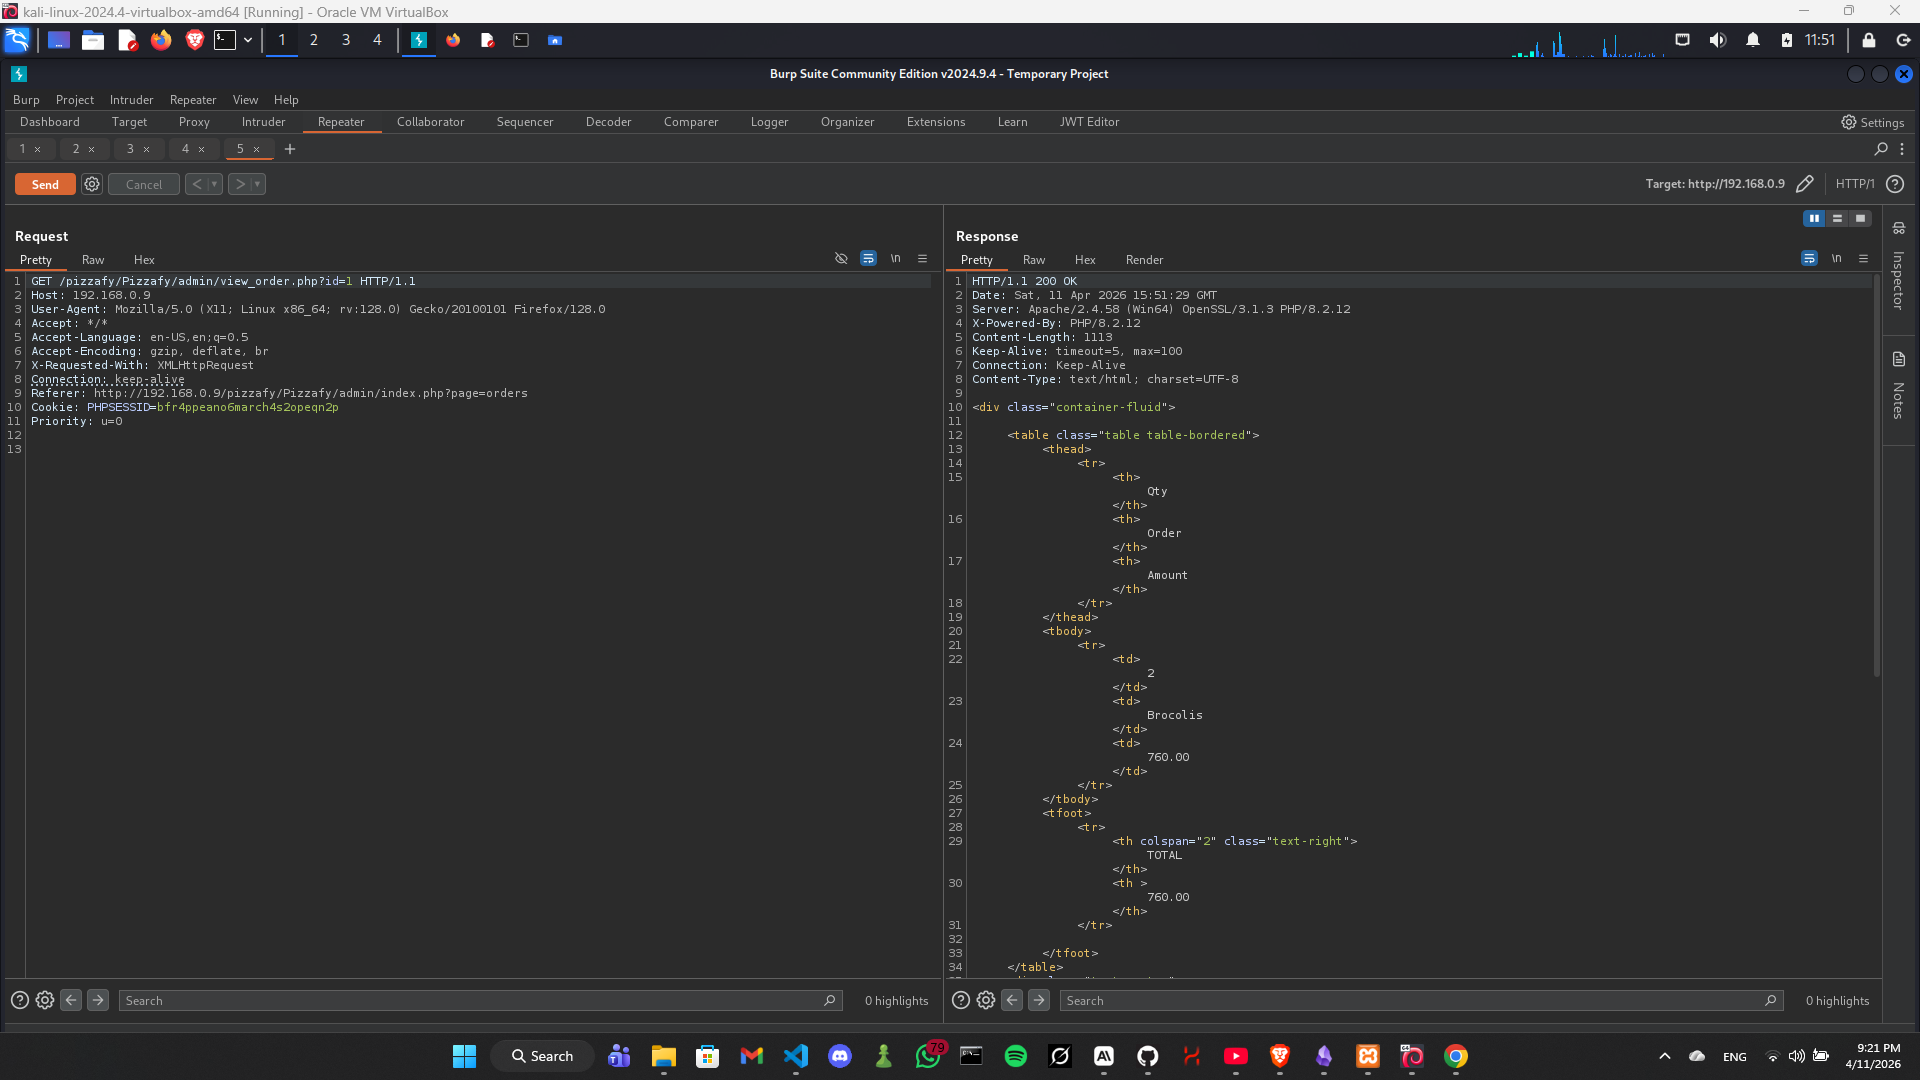
Proof-of-concept exploit for CVE-2026-7394, a SQL injection vulnerability in SourceCodester Pizzafy Ecommerce System 1.0. Demonstrates authenticated…

SQL Injection vulnerability in NASA EOSDIS MODAPS due to improper input validation in the `category` parameter. This flaw allows attackers to…

CVE-2026-29187: SQL Injection Vulnerability in OpenEMR <8.0.0.3

CVE-2026-32127: SQL Injection Vulnerability in OpenEMR <8.0.0.1

CVE-2026-25746 - SQL Injection Vulnerability in OpenEMR <8.0.0

Security advisory for CVE-2026-30655: unauthenticated SQL injection in esiclivre (/reset/index.php).

🛠 Exploit the CVE-2025-14847 MongoDB vulnerability to reveal sensitive information through crafted zlib-compressed packets and real-time output.

An information exposure vulnerability in Datart v1.0.0-rc.3 allows authenticated attackers to access sensitive data via a custom H2 JDBC connection…

Datart v1.0.0-rc.3 JDBC Connection String Injection Leading to Arbitrary File Read

Exploit for CVE-2025-10351. SQL Injection on Melis Platform Framework

Mongobleed Detector CVE-2025-14847

MongoBleed CVE-2025-14847 Vulnerability Checker