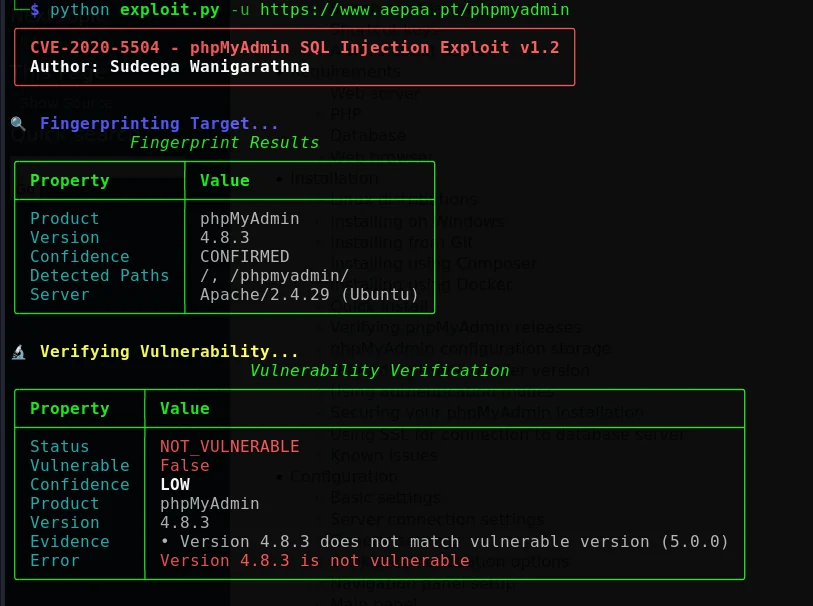
phpMyAdmin-CVE-2020-5504-Exploit

Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…

Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…

Proof-of-concept exploit for CVE-2020-2969 targeting unauthorized access to Oracle Database password hashes. Enables security researchers to test and…

A Poc for CVE-2020-24913, a SQL injection vulnerability in qcubed (all versions including 3.1.1) in profile.php via the strQuery parameter allows an…

PoC of SQL Injection vul(CVE-2020-9483,Apache SkyWalking)

Proof-of-concept exploit for CVE-2020-2978 targeting Oracle RMAN audit table point-in-time recovery bypass, enabling unauthorized database access.

CVE-2020-7471 Potential SQL injection via StringAgg(delimiter)

django 漏洞:CVE-2020-7471 Potential SQL injection via StringAgg(delimiter) 的漏洞环境和 POC

Django StringAgg SQL Injection (CVE-2020-7471)