
CyberChef
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
binary-analysiscryptographyctf+9
gchq/cyberchefThe Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 abraxas/cve-2026-79752
CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
 0xsemz/magento-cve-2019-7139-sqli-poc
Python proof-of-concept exploit for CVE-2019-7139, an unauthenticated SQL injection in Magento's product_frontend_action endpoint, enumerating…
 sqlancer/sqlancer
Automated testing to find logic and performance bugs in database systems
 jhnhnck/cve-2019-9193
PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in certain versions of PostgreSQL (9.3 - 11.7)
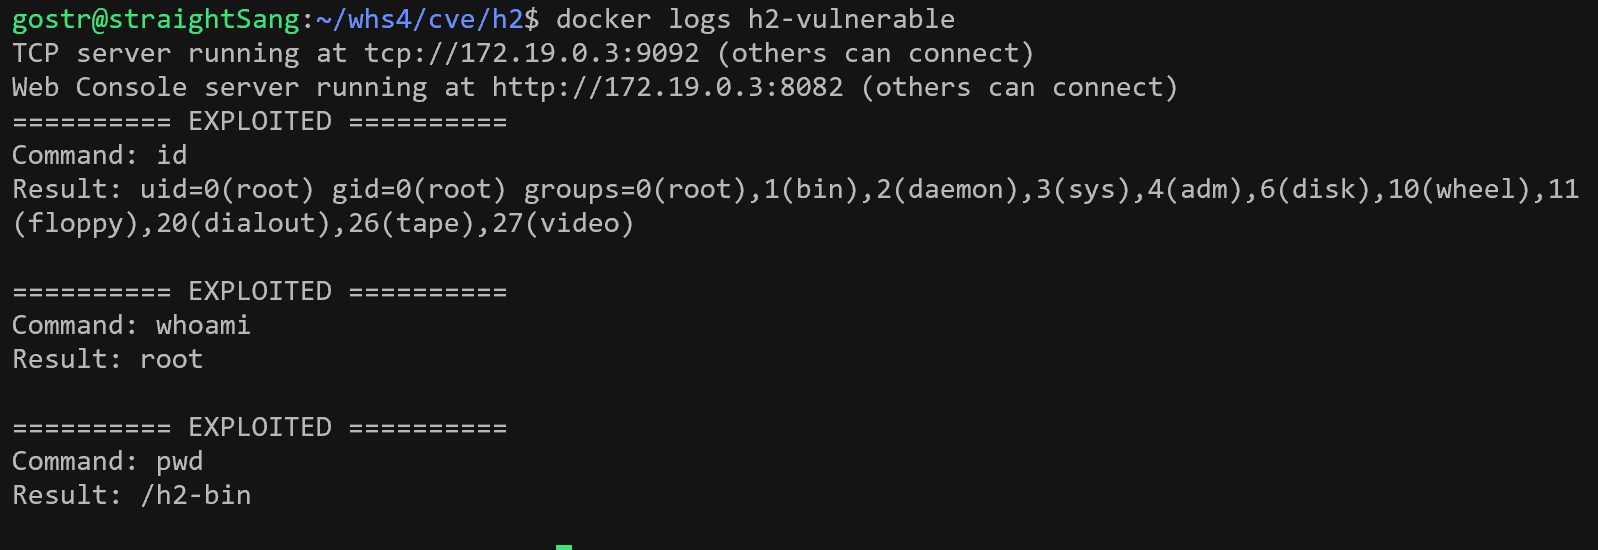 straightsang/h2-database-cve-2022-23221
vulhub/H2-database/CVE-2022-23221
 ivanesk315/cve-2023-25157
Local GeoServer/PostGIS lab reproducing OGC Filter SQL injection (CVE-2023-25157/25158) with vulnerable, patched, and mitigated A/B test modes.
 romain-deperne/cve-2026-41490
Detailed CVE-2026-41490 disclosure with PoC demonstrating unauthenticated SQL injection in Dagster database I/O managers via dynamic partition keys,…
 yym8538/cve-2026-30951
Proof-of-concept and vulnerable Node.js/Express/Sequelize app demonstrating CVE-2026-30951, a JSON cast-type SQL injection in Sequelize v6 where…
 yym8538/cve-2026-0603
Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
 hackspeak/cve-2026-23479
Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…
 eqstlab/cve-2026-30951
Sequelize JSON Cast SQL Injection
 eqstlab/cve-2026-34220
SQL Injection vulnerability in MikroORM
 eqstlab/cve-2026-0603
Hibernate ORM Second-Order SQL Injection
 hunt-benito/e-is-for-exploit-cve-2026-17543-php-pgsql-sql-injection-backslash-breakout
PoC exploit for CVE-2026-17543: SQL injection in PHP ext/pgsql via backslash breakout, with data exfiltration and admin privilege-escalation payloads…
 george0papasotiriou/cve-2026-11115-database-connection-string-injection-via-env-variable
 rahulreddykarne/cve-2026-65321-pyathena
SQL injection in PyAthena via DefaultParameterFormatter (CVE-2026-65321)