metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…

Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…

PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…

Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…

Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…

POC for CVE-2026-25212

CVE-2026-23631 (DarkReplica) Redis Exploit

Offensive MSSQL toolkit written in Python, based off SQLRecon

A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself

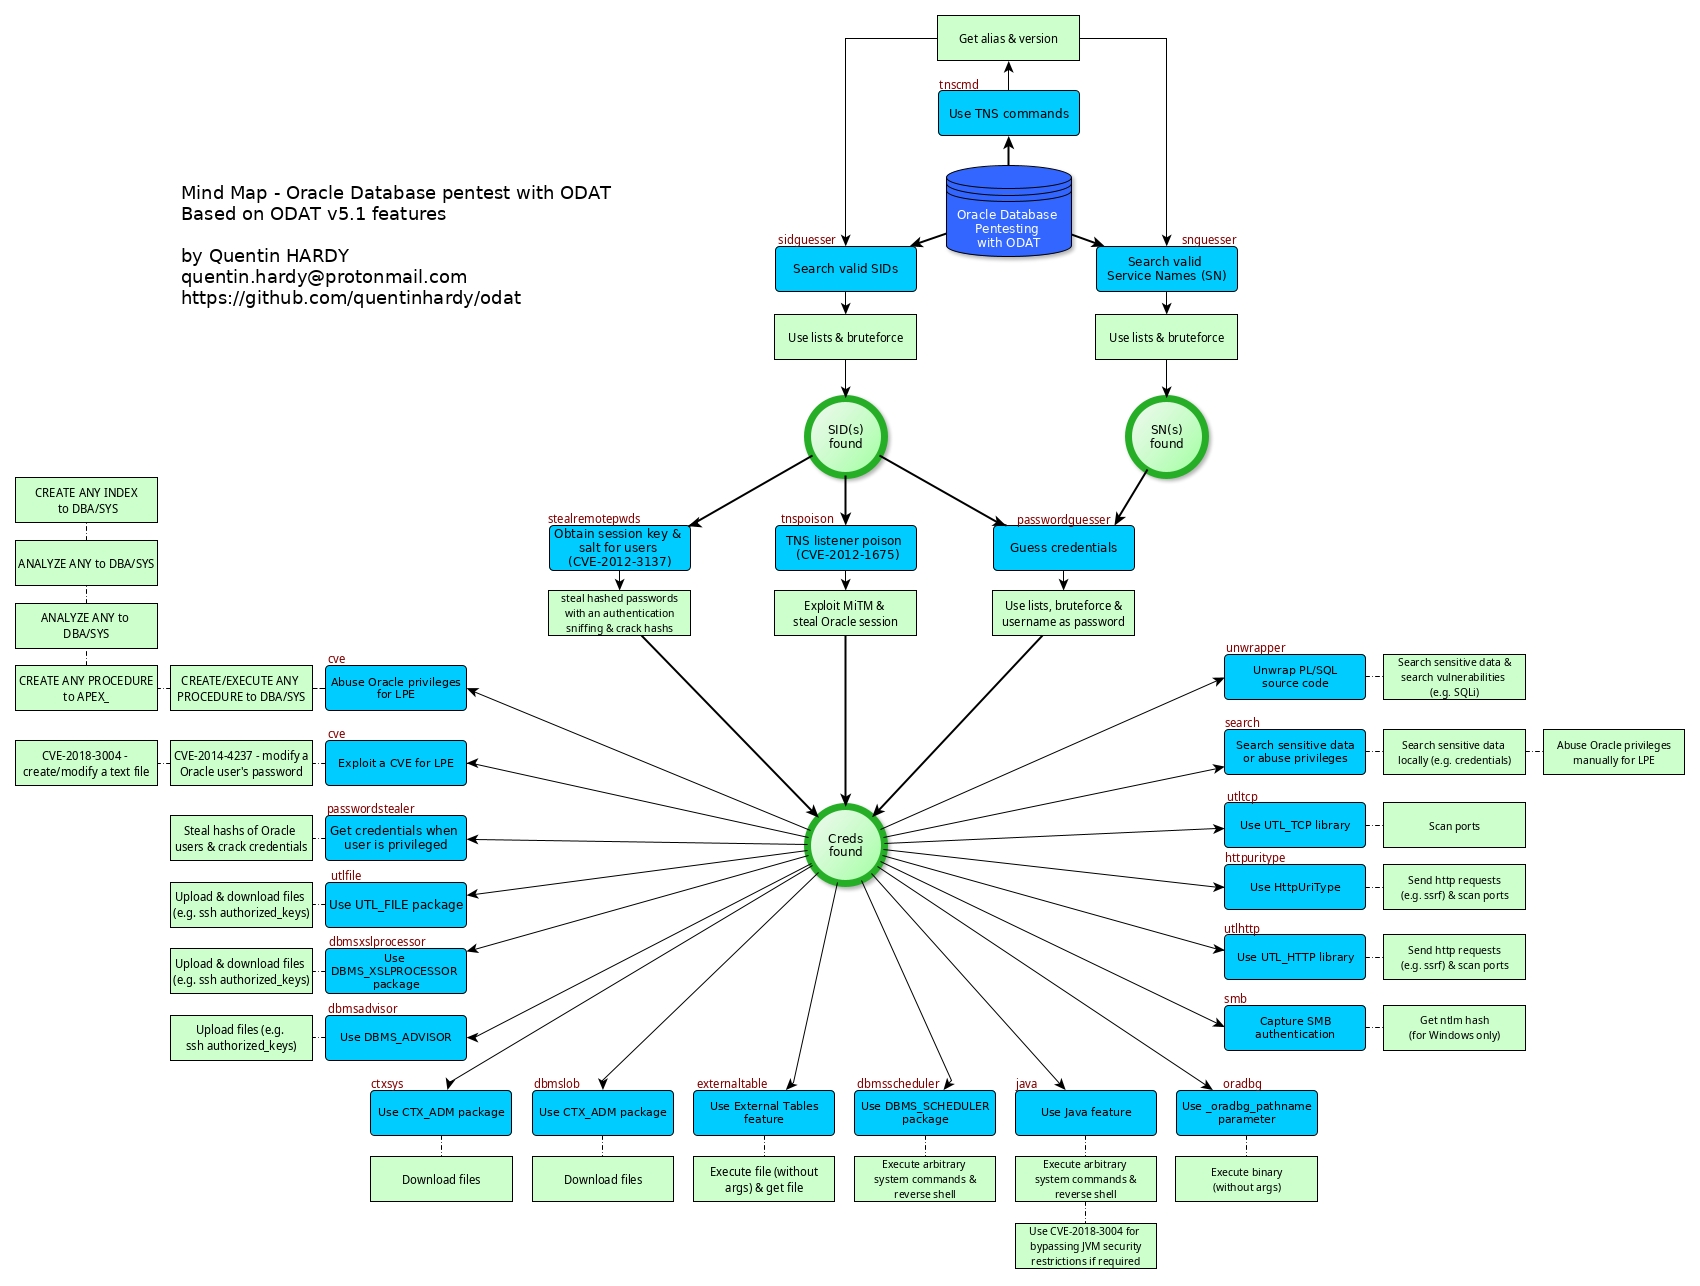
Penetration testing tool for Oracle Databases that discovers valid SIDs, brute-forces credentials, escalates privileges to DBA, executes system…

Python exploit script for CVE-2019-9193, enabling remote code execution on vulnerable PostgreSQL databases via authenticated command injection.

Proof-of-concept exploit for CVE-2025-66224 demonstrating remote code execution in OrangeHRM via command injection in the sendmail_path parameter,…

Nacos Derby命令执行漏洞利用脚本

Database authenticated code execution

CVE-2021-27928 MariaDB/MySQL-'wsrep provider' 命令注入漏洞

PHP Webshell with handy features