
CVE-2026-0603
 yym8538/cve-2026-0603
Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
database-securityeducationexploitation+4
1
yym8538/cve-2026-0603Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
 abraxas/cve-2026-22599
Python PoC and Docker lab for CVE-2026-22599, an authenticated SQL injection in Strapi's Content-Type Builder write API via Knex raw defaultTo.
 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
 yym8538/cve-2026-34220
Proof-of-concept and Docker lab reproducing CVE-2026-43220, a MikroORM SQL injection via unvalidated __raw properties in custom type columns, with…
 yym8538/cve-2026-30951
Proof-of-concept and vulnerable Node.js/Express/Sequelize app demonstrating CVE-2026-30951, a JSON cast-type SQL injection in Sequelize v6 where…
 4minx/cve-2026-48842
Python PoC for CVE-2026-48842, a pre-auth SQL injection in Roundcube's virtuser_query plugin. Confirms the flaw via time-based differential and…
 0xsemz/magento-cve-2019-7139-sqli-poc
Python proof-of-concept exploit for CVE-2019-7139, an unauthenticated SQL injection in Magento's product_frontend_action endpoint, enumerating…
 qucklecrabik/cve-2026-23921
Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…
 abraxas/cve-2026-77635
Disclosure pack and Python PoC for CVE-2026-77635, an unauthenticated SQL injection in CakePHP's jsonValue() with PostgresDriver, including a…
 abraxas/cve-2026-79752
CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0
 hex0user/cve-2025-69295
Documents CVE-2025-69295, a blind SQL injection in the TeconceTheme Coven Core WordPress component, covering technical details, impact, and detection…
 isaca0315/cve-2026-44840-poc
Docker lab reproducing CVE-2026-44840, a DQL injection in Dgraph's checkUserPassword GraphQL query, with exploit script and vulnerable vs patched…
 34zy/cve-2026-72898
Python exploit for CVE-2026-72898, an unauthenticated SQL injection in Metabase's password reset endpoint that creates admin accounts and extracts…
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 ivanesk315/cve-2023-25157
Local GeoServer/PostGIS lab reproducing OGC Filter SQL injection (CVE-2023-25157/25158) with vulnerable, patched, and mitigated A/B test modes.
 jithinkrishnanrs/cve-2026-67401-cpanel-emailtrack-sqli
Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…
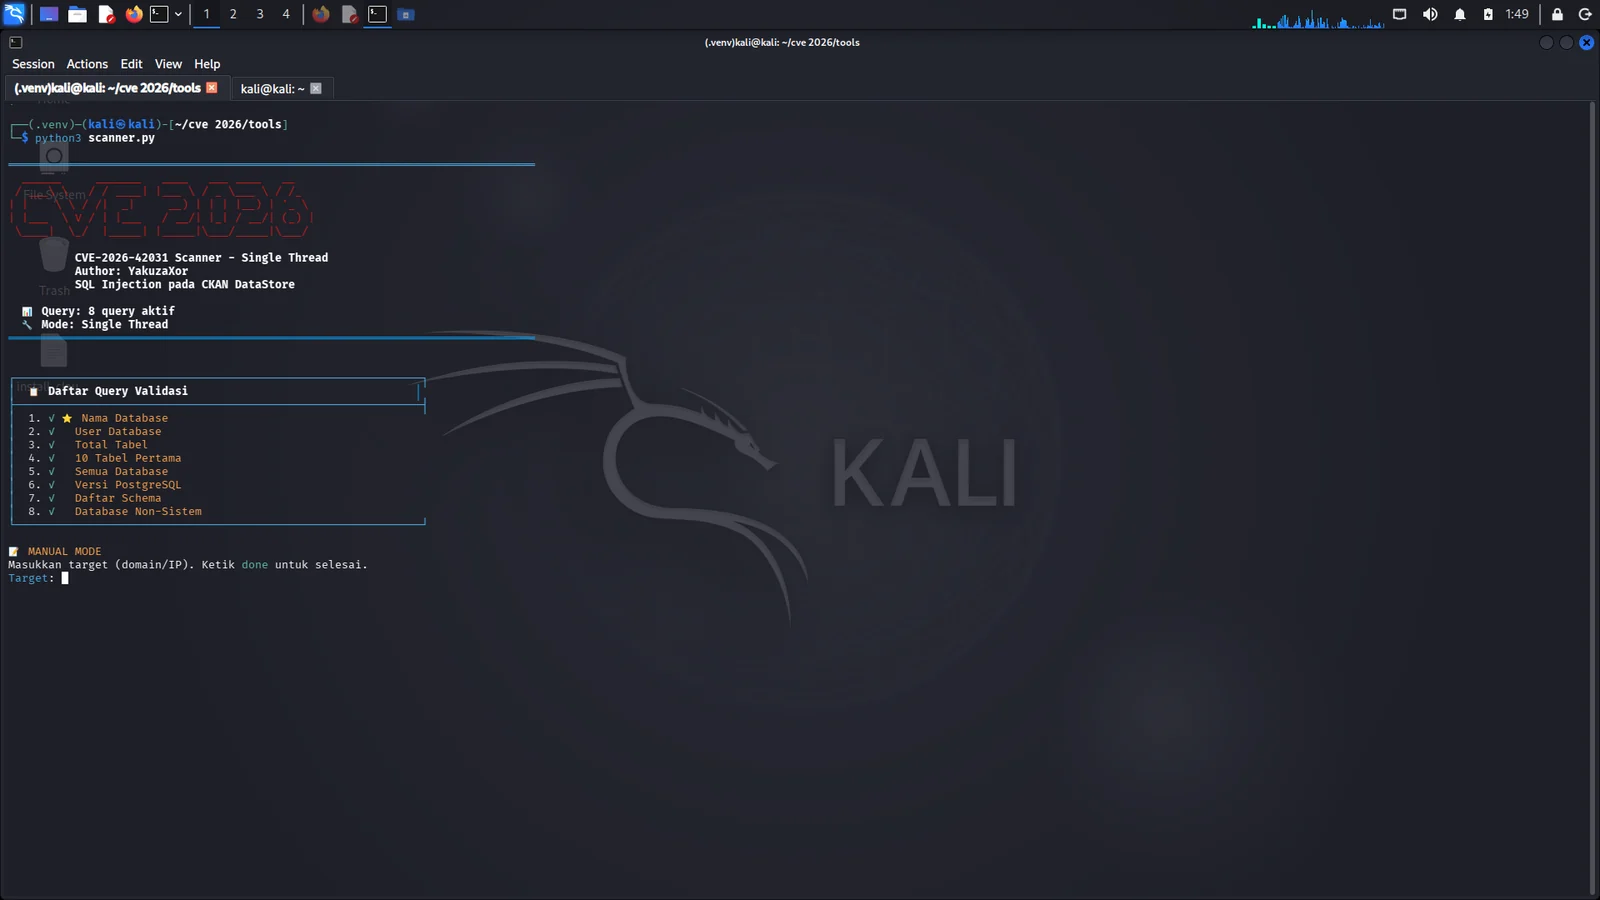 ddrvahandzo90-hue/cve-2026-42031-sql-injection-scanner
Automated SQL injection scanner for CKAN DataStore, detecting and validating CVE-2026-42031 with multi-target scanning, data dumping, and report…