
cakephp-collate-sqli
 abraxas/cakephp-collate-sqli
CakePHP 5.4.2 - High - Remote - SQLi - COLLATE collation is a raw SQL fragment
database-securityexploitationpenetration-testing+4
abraxas/cakephp-collate-sqliCakePHP 5.4.2 - High - Remote - SQLi - COLLATE collation is a raw SQL fragment
 abraxas/cakephp-window-sqli
CakePHP 5.4.2 - High - Remote - SQLi - WindowExpression range/frame offsets spliced into SQL
 abraxas/phpmyadmin-auth-plugin-unquoted
phpMyAdmin 5.2.3 - High - Remote - SQLi - auth plugin identifier unquoted
 yym8538/cve-2026-0603
Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
 yym8538/cve-2026-30951
Proof-of-concept and vulnerable Node.js/Express/Sequelize app demonstrating CVE-2026-30951, a JSON cast-type SQL injection in Sequelize v6 where…
 4minx/cve-2026-48842
Python PoC for CVE-2026-48842, a pre-auth SQL injection in Roundcube's virtuser_query plugin. Confirms the flaw via time-based differential and…
 hex0user/cve-2025-69295
Documents CVE-2025-69295, a blind SQL injection in the TeconceTheme Coven Core WordPress component, covering technical details, impact, and detection…
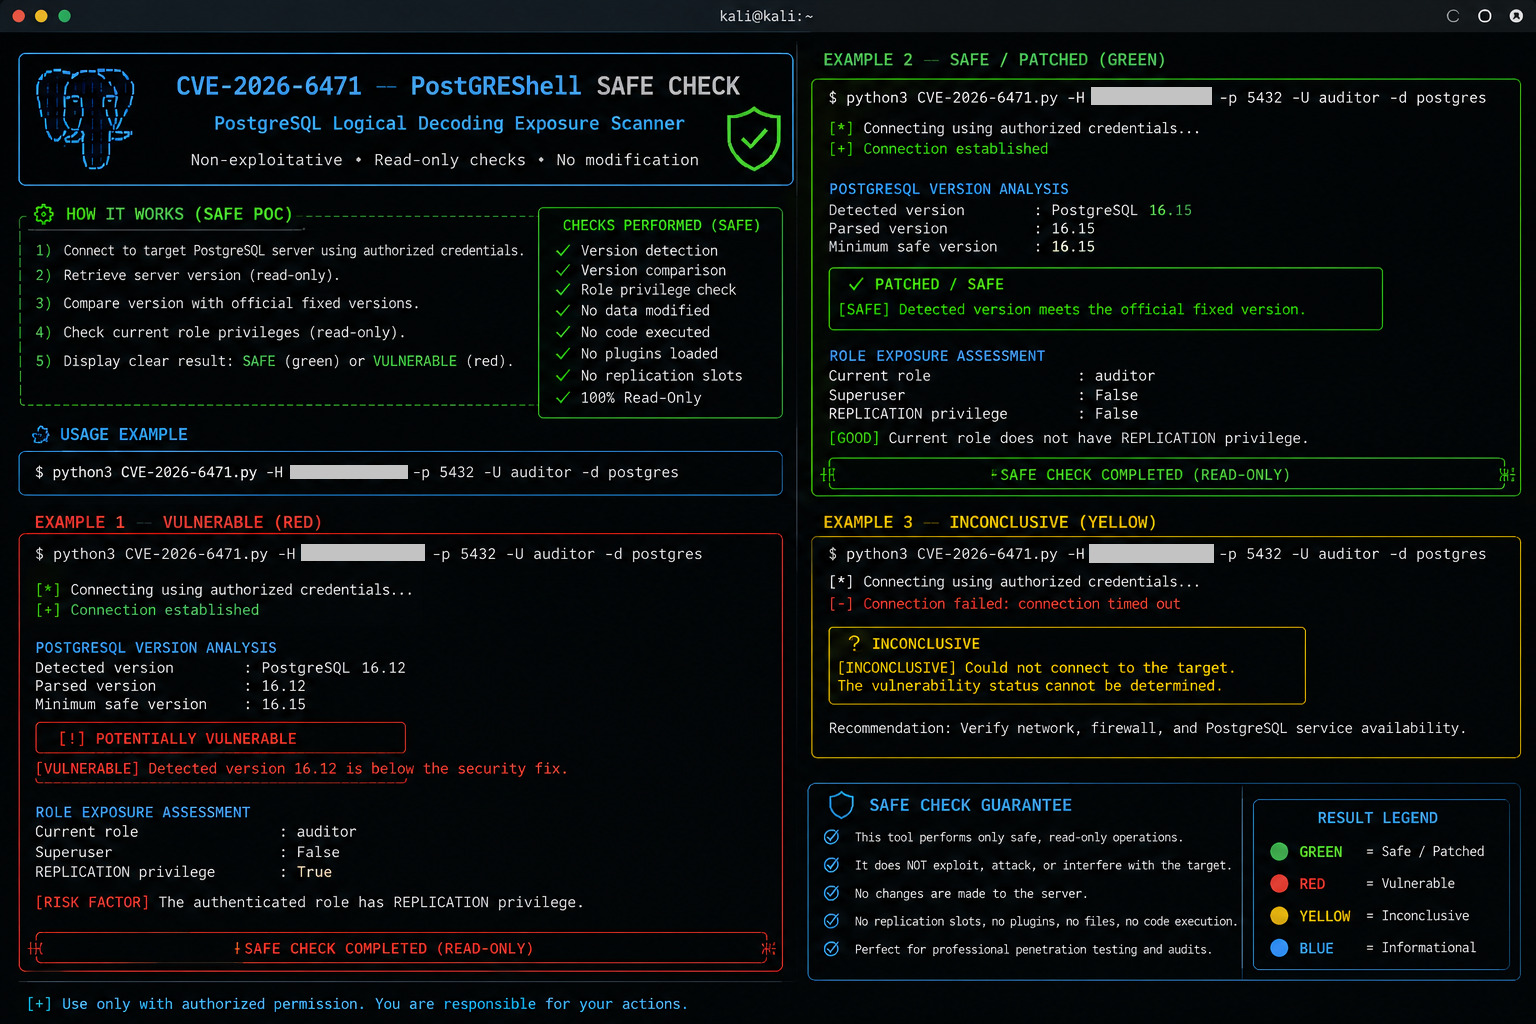 0xblackash/cve-2026-6471
Non-destructive PostgreSQL vulnerability checker for CVE-2026-6471. Audits server version and REPLICATION privileges to identify exposure to logical…
 emad-almousa/cve-2021-2175
Proof-of-concept exploit for CVE-2021-2175, an Oracle Database Vault metadata exposure vulnerability, demonstrating unauthorized access to sensitive…
 angelusrivera/cve-2025-49844
Scanner and educational guide for CVE-2025-49844 (RediShell), a Redis Lua scripting use-after-free vulnerability. Checks Redis servers for exposure,…
 trailofbits/cvedb
CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
 adarshthakur14777-cyber/cve-2026-60137
wpsqli full SQLi extractor + dumper for CVE-2026-60137
 randomrobbiebf/cve-2024-55982
Share Buttons – Social Media <= 1.0.2 - Unauthenticated SQL Injection
 xploitgh0st/cve-2025-26794-exploit
SQL injection exploit for CVE-2025-26794 in Exim 4.98. Automated data extraction via time-based blind SQLi. For authorized penetration testing only.
 chrissub08/cve-2026-25746_sqlinjectionvulnerabilityopenemr7.0.4
CVE-2026-25746 - SQL Injection Vulnerability in OpenEMR <8.0.0