
ATTACK-Tools
 nshalabi/attack-tools
SQLite relational data model for MITRE ATT&CK plus an adversary emulation planning tool, enriched with Red Canary ATOMIC tests and APT3 emulation…
adversarial-attackcurated-resourcesdatabase-security+5
1.1k
nshalabi/attack-toolsSQLite relational data model for MITRE ATT&CK plus an adversary emulation planning tool, enriched with Red Canary ATOMIC tests and APT3 emulation…
 owasp/piihunter
Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
 abraxas/cakephp-collate-sqli
CakePHP 5.4.2 - High - Remote - SQLi - COLLATE collation is a raw SQL fragment
 yym8538/cve-2026-0603
Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
 yym8538/cve-2026-34220
Proof-of-concept and Docker lab reproducing CVE-2026-43220, a MikroORM SQL injection via unvalidated __raw properties in custom type columns, with…
 yym8538/cve-2026-30951
Proof-of-concept and vulnerable Node.js/Express/Sequelize app demonstrating CVE-2026-30951, a JSON cast-type SQL injection in Sequelize v6 where…
 dev-sec/chef-mysql-hardening
This chef cookbook provides security configuration for mysql.
 hex0user/cve-2025-69295
Documents CVE-2025-69295, a blind SQL injection in the TeconceTheme Coven Core WordPress component, covering technical details, impact, and detection…
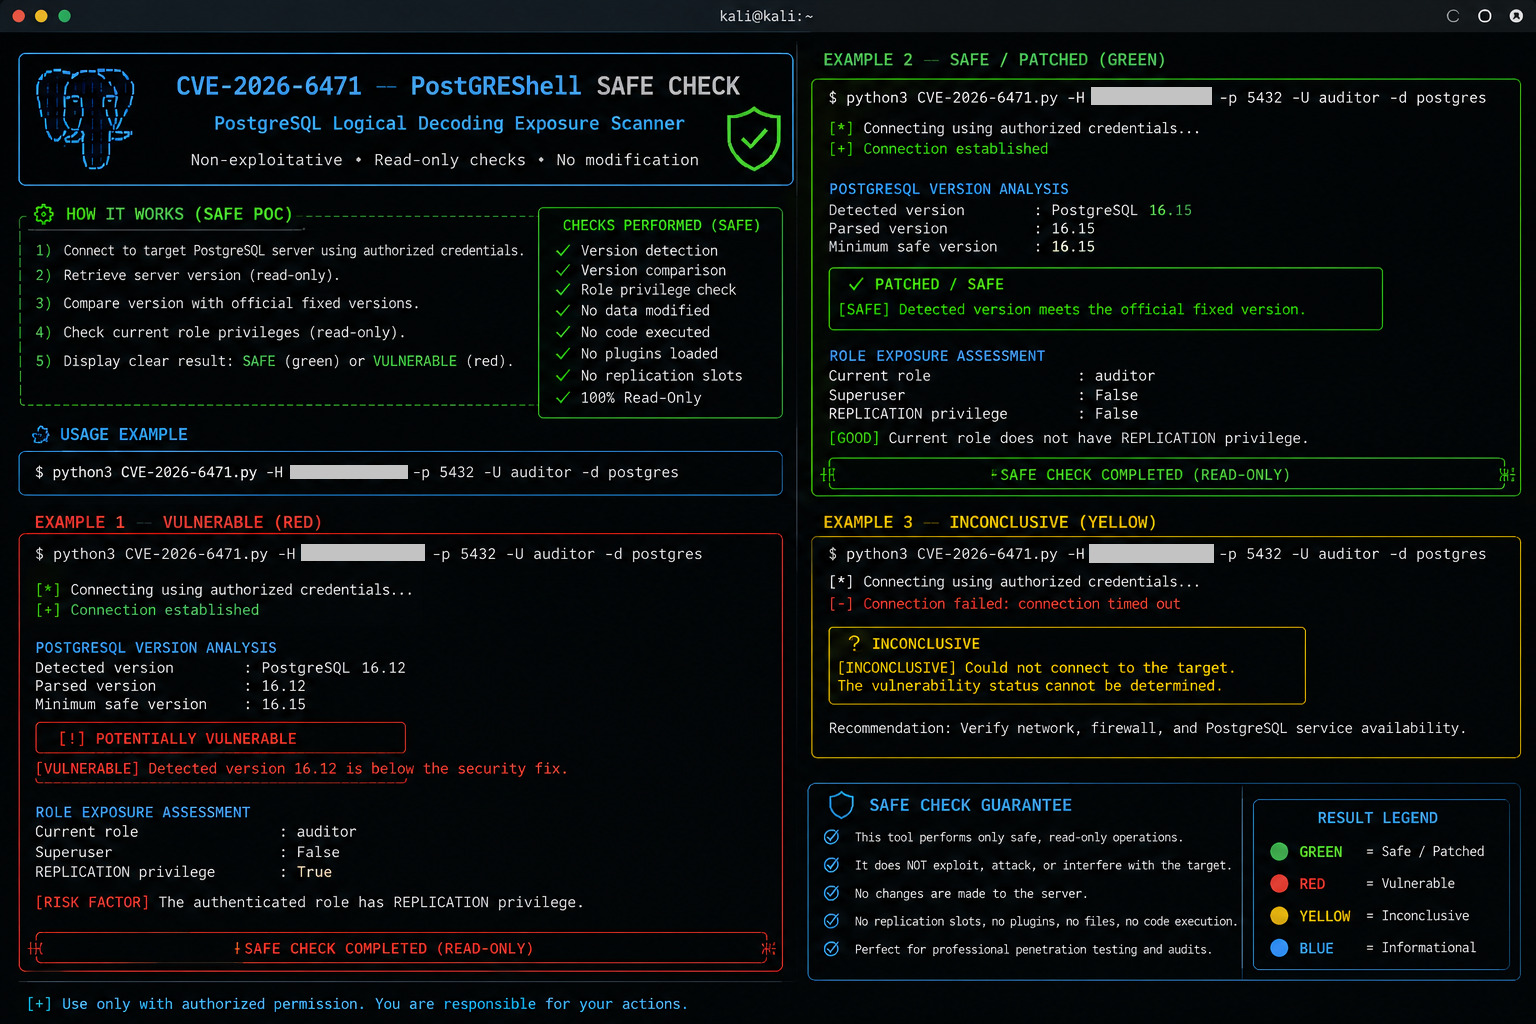 0xblackash/cve-2026-6471
Non-destructive PostgreSQL vulnerability checker for CVE-2026-6471. Audits server version and REPLICATION privileges to identify exposure to logical…
 emad-almousa/cve-2021-2175
Proof-of-concept exploit for CVE-2021-2175, an Oracle Database Vault metadata exposure vulnerability, demonstrating unauthorized access to sensitive…
 angelusrivera/cve-2025-49844
Scanner and educational guide for CVE-2025-49844 (RediShell), a Redis Lua scripting use-after-free vulnerability. Checks Redis servers for exposure,…
 trailofbits/cvedb
CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
 0xblackash/cve-2026-72898
CVE-2026-72898
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
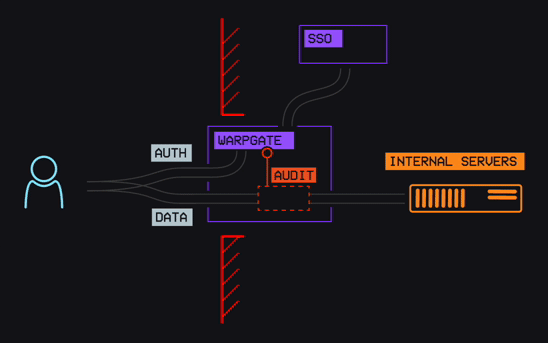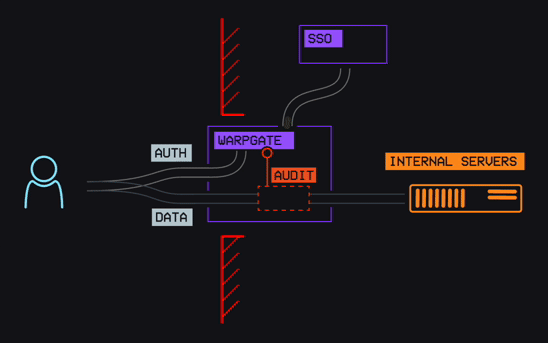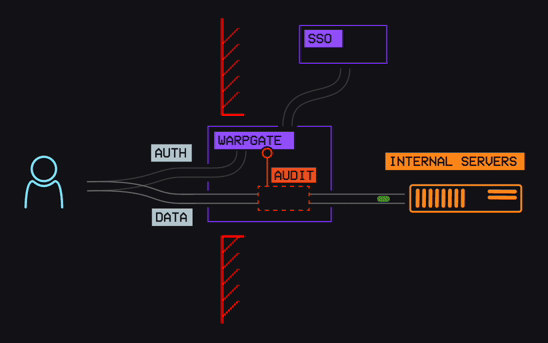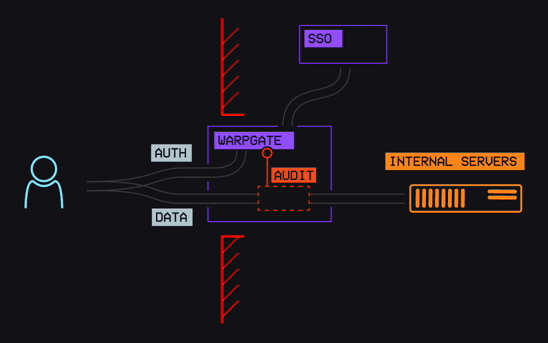 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)