

CVE-2026-118383
 googlesky/cve-2026-118383
Proof-of-concept for CVE-2026-118383, an unauthenticated MongoDB use-after-free in replication catch-up, with wire-protocol exploit scripts, a gdb…
database-securitydebuggersexploitation+3
googlesky/cve-2026-118383Proof-of-concept for CVE-2026-118383, an unauthenticated MongoDB use-after-free in replication catch-up, with wire-protocol exploit scripts, a gdb…
 abraxas/cve-2026-22599
Python PoC and Docker lab for CVE-2026-22599, an authenticated SQL injection in Strapi's Content-Type Builder write API via Knex raw defaultTo.
 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
 4minx/cve-2026-48842
Python PoC for CVE-2026-48842, a pre-auth SQL injection in Roundcube's virtuser_query plugin. Confirms the flaw via time-based differential and…
 dev-sec/chef-mysql-hardening
This chef cookbook provides security configuration for mysql.
 0xsemz/magento-cve-2019-7139-sqli-poc
Python proof-of-concept exploit for CVE-2019-7139, an unauthenticated SQL injection in Magento's product_frontend_action endpoint, enumerating…
 abraxas/cve-2026-77635
Disclosure pack and Python PoC for CVE-2026-77635, an unauthenticated SQL injection in CakePHP's jsonValue() with PostgresDriver, including a…
 abraxas/cve-2026-79752
CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
 34zy/cve-2026-72898
Python exploit for CVE-2026-72898, an unauthenticated SQL injection in Metabase's password reset endpoint that creates admin accounts and extracts…
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
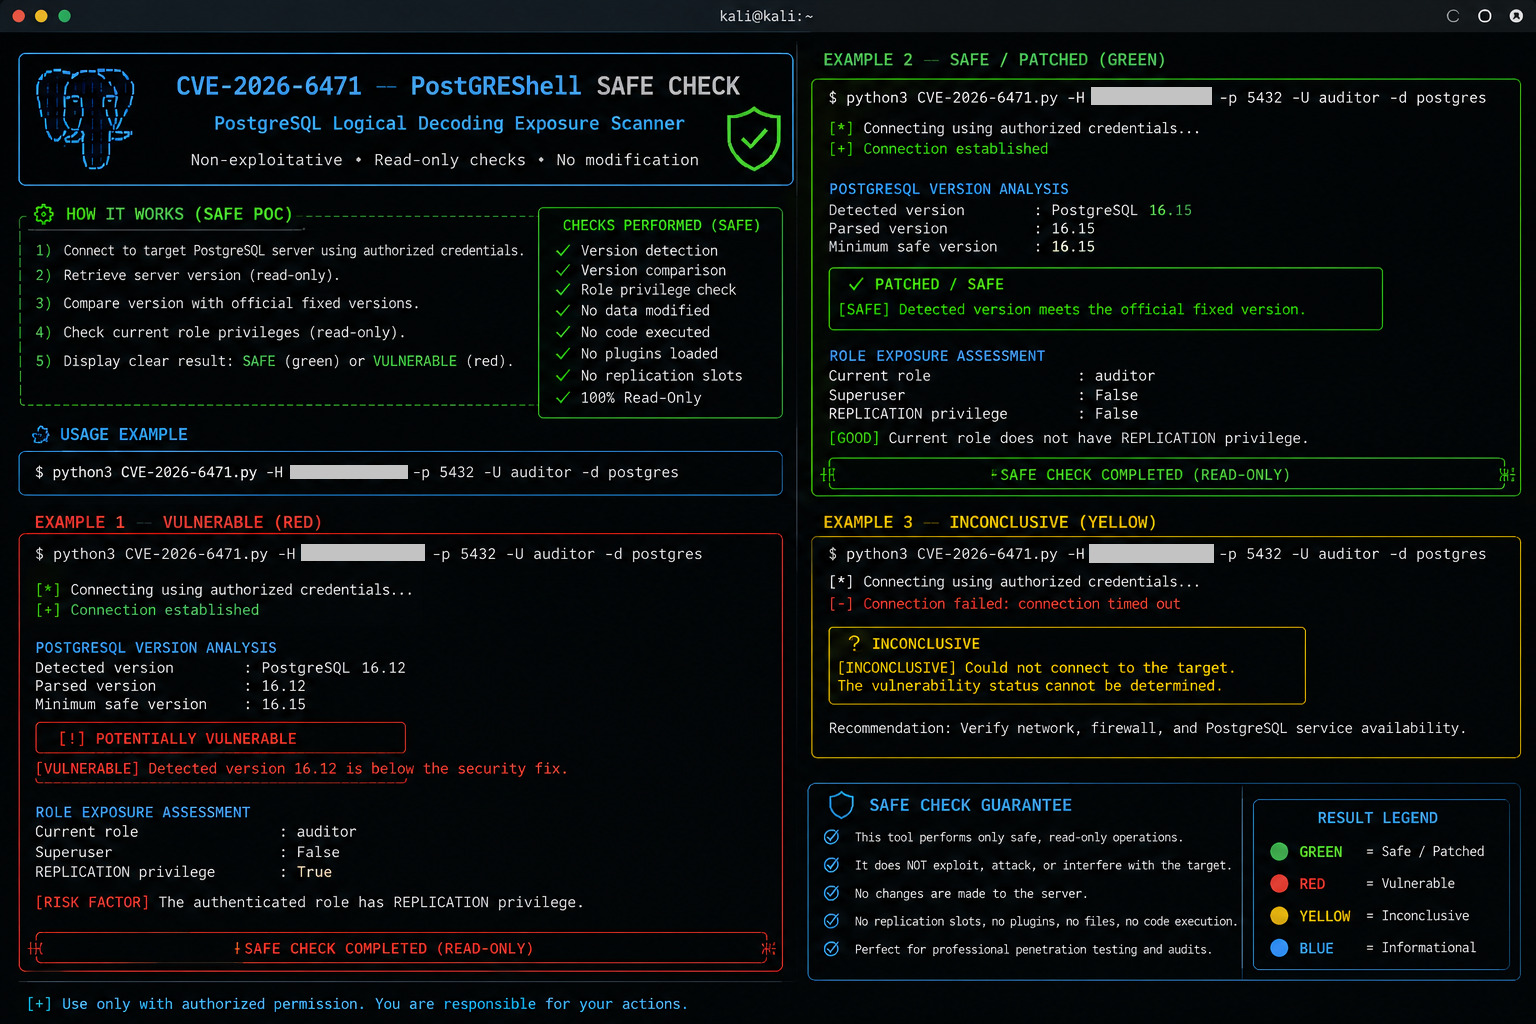 0xblackash/cve-2026-6471
Non-destructive PostgreSQL vulnerability checker for CVE-2026-6471. Audits server version and REPLICATION privileges to identify exposure to logical…
 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 joakimbulow/cve-2026-34308
Proof-of-concept for CVE-2026-34308, a MySQL Server JSON component denial-of-service vulnerability. Demonstrates stack exhaustion via deep $ref…
 trailofbits/cvedb
CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database
 cossacklabs/themis
Easy to use cryptographic framework for data protection: secure messaging with forward secrecy and secure data storage. Has unified APIs across 14…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3

 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…