
CVE-2026-72898
 34zy/cve-2026-72898
Python exploit for CVE-2026-72898, an unauthenticated SQL injection in Metabase's password reset endpoint that creates admin accounts and extracts…
database-securityexploitationpenetration-testing+6
34zy/cve-2026-72898Python exploit for CVE-2026-72898, an unauthenticated SQL injection in Metabase's password reset endpoint that creates admin accounts and extracts…
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 galisko/cve-2025-24799
Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
 goldendivider/cve-2026-6471-postgres-logical-decoding-dlopen
Proof-of-concept exploit for CVE-2026-6471, demonstrating privilege escalation in PostgreSQL via logical decoding dlopen to achieve arbitrary code…
 toanln-cov/cve-2026-78070
SQL Injection via ORDER BY Shortcode in plg_content_dpcalendar — DPCalendar Free ≤ 10.11.2
 nabeelmkhan/cve-2026-78837
Proof-of-concept exploit for CVE-2026-78837, an unauthenticated SQL injection in AppNitro MachForm v30 allowing enumeration of database column names…
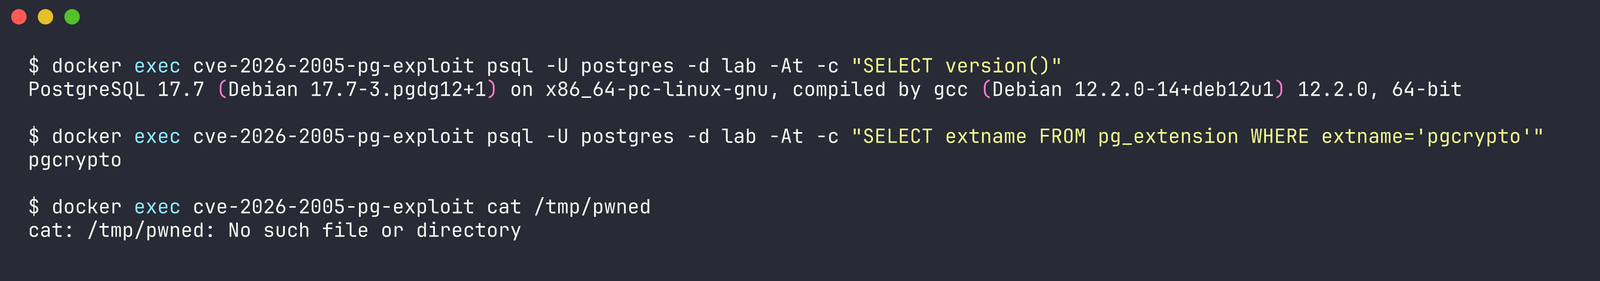 dinosn/cve-2026-2005
Exploit for CVE-2026-2005, a heap overflow in PostgreSQL's pgcrypto extension leading to remote code execution. Includes PoC generators, Docker lab,…
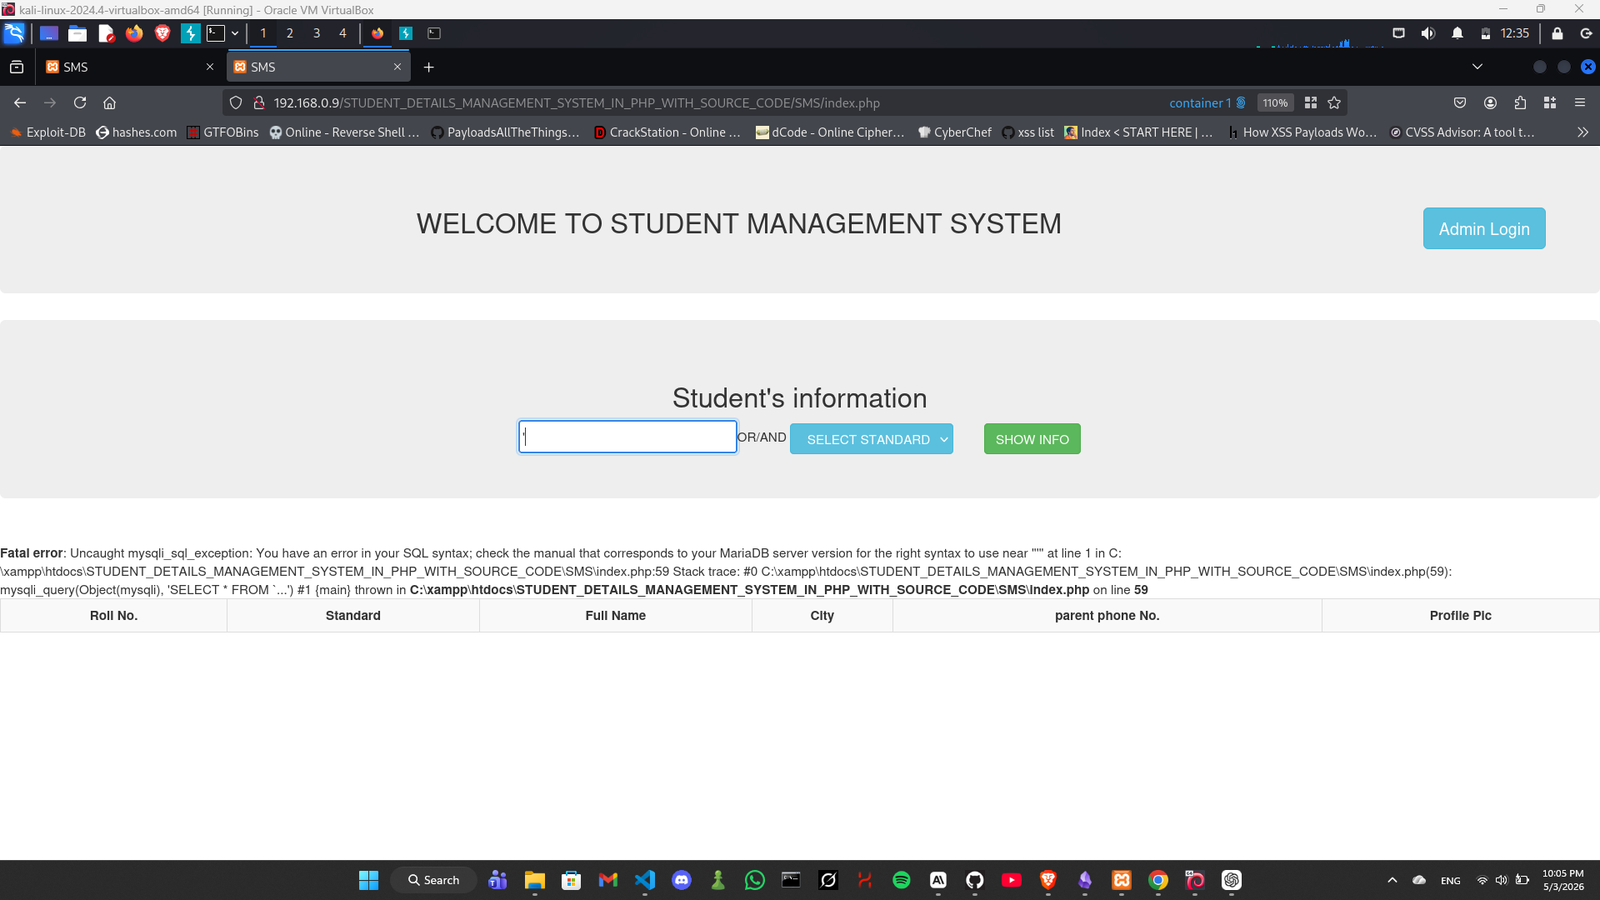 xmyronn/cve-2026-10110-sqli
Proof-of-concept for unauthenticated SQL injection in Student Details Management System 1.0, demonstrating UNION-based data extraction and credential…
 slayerkkkk/cve-2025-46817-poc
C-based exploit for CVE-2025-46817, a Redis integer overflow vulnerability, enabling crash detection and potential RCE via Lua unpack() payload.
 ffasterss/cve-2026-31891
SQL Injection in MongoLite Aggregation Optimizer via toJsonExtractRaw()
 xmyronn/cve-2026-7229-sqli
Proof of concept for authenticated SQL injection in Coaching Management System, demonstrating database dump via unsanitized complaintreply parameter.
 joakimbulow/cve-2026-34308
Proof-of-concept for CVE-2026-34308, a MySQL Server JSON component denial-of-service vulnerability. Demonstrates stack exhaustion via deep $ref…
 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 boreas37/cve-2026-69084-poc
CVE-2026-69084/69085 — SiYuan arbitrary SQL execution via searchEmbedBlock + searchDocs SQLi (CVSS 9.9). Verified on v3.7.2, rejected on v3.7.3.
 ignitetechnologies/mssql-pentest-cheatsheet
Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…
 dwisiswant0/cve-2025-49844
Proof-of-concept exploit for Redis 8.2.1 Lua parser use-after-free, racing garbage collection via crafted loadstring calls to achieve remote code…
 captain-woof/cve-2026-25243
Stable POC for CVE-2026-25243 (Redis RESTORE double-free -> remote code execution)