

nuclei
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
anti-botapi-securityapi-security-testing+21
30.4k
projectdiscovery/nucleiFast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 nanaao/cve-2021-29442-nacos-derby-rce-exp
Nacos Derby命令执行漏洞利用脚本
 oscarbataille/cve-2025-26794
CVE-2025-26794: Blind SQL injection in Exim 4.98 (SQLite DBM)- exploit writeup
 0xwhoami35/cve-2024-4879
Exploit script for ServiceNow CVE-2024-4879 that enables unauthenticated remote code execution, with mass target scanning and database dumping…
 dovankha/cve-2024-34222
Proof-of-concept for SQL injection vulnerability in SourceCodester Human Resource Management System 1.0, demonstrating arbitrary SQL command…
 akhlak2511/cve-2024-50971
Proof-of-concept for CVE-2024-50971, a SQL injection vulnerability in Itsourcecode Construction Management System 1.0, with exploitation steps and…
 shadowbyte1/cve-2024-48245
SQL Injection Vulnerability in Vehicle Management System 1.0 - 1.3
 ron190/jsql-injection
Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
 geraldoalcantara/cve-2023-49970
Customer Support System 1.0 - SQL Injection Vulnerability in the "subject" Parameter During "save_ticket" Operation
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
 bridgeralderson/cve-2024-51482
ZenoMinder Blind SQL Injection PoC
 saferman/cve-2020-7471
django 漏洞:CVE-2020-7471 Potential SQL injection via StringAgg(delimiter) 的漏洞环境和 POC
 jakabakos/cve-2023-27524-apache-superset-auth-bypass-and-rce
Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…
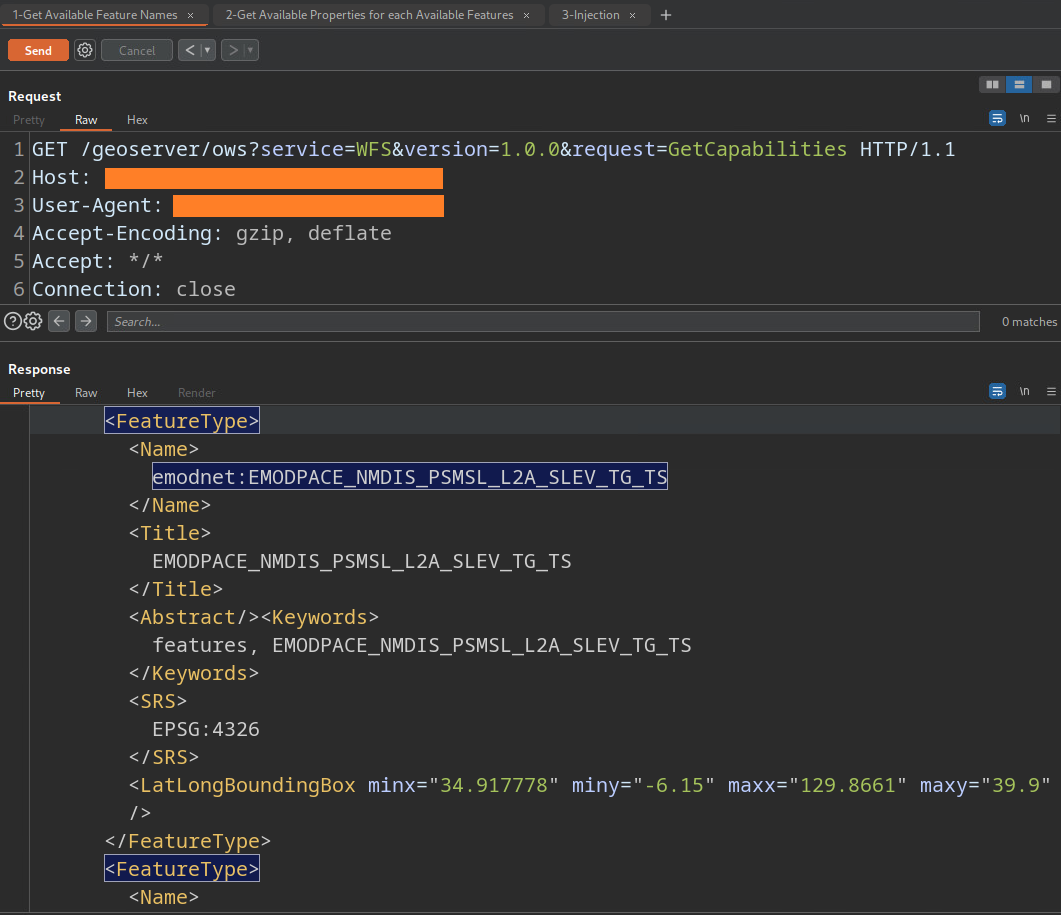 murataydemir/cve-2023-25157-and-cve-2023-25158
GeoServer & GeoTools SQL Injection (CVE-2023-25157 & CVE-2023-25158)