
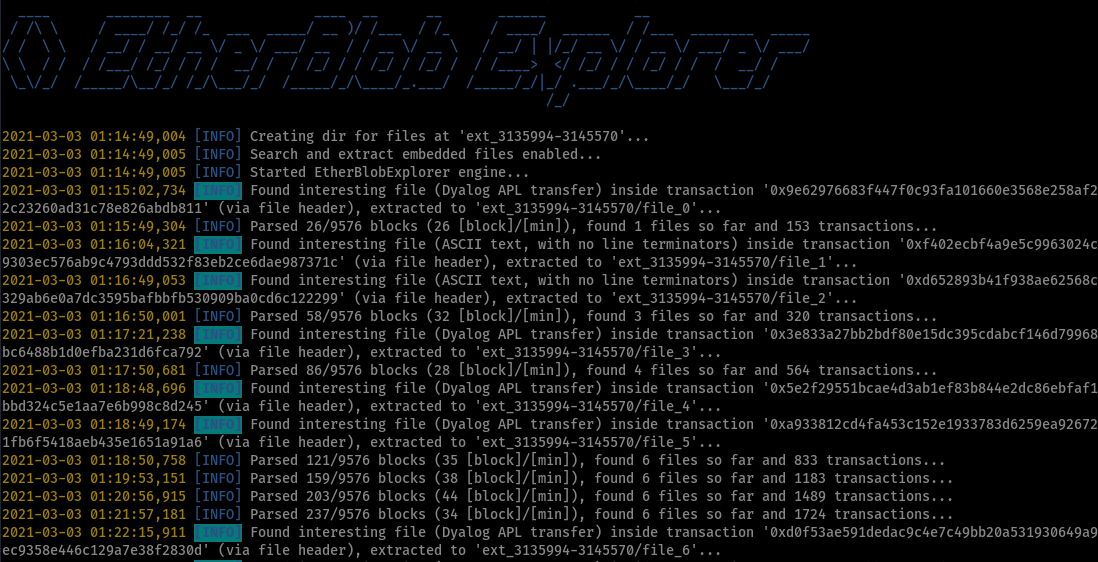
etherblob-explorer
 litneet64/etherblob-explorer
Search and extract blob files on the Ethereum Blockchain network
ctfdata-recoveryforensics+2
435 years ago
litneet64/etherblob-explorerSearch and extract blob files on the Ethereum Blockchain network
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response

 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:

 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 juanceresa/sift-kg
Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…
 cristianzsh/forensictools
Collection of forensic tools
 kvasirsecurity/kvasir
Kvasir: Penetration Test Data Management
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
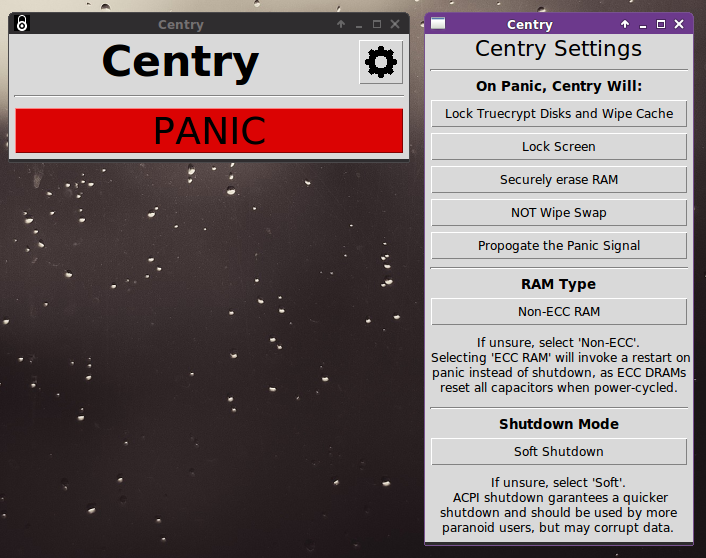 0xpoly/centry
Panic button for protection against cold boot attacks
 packetlss/android-locdump
android location service cache dumper
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
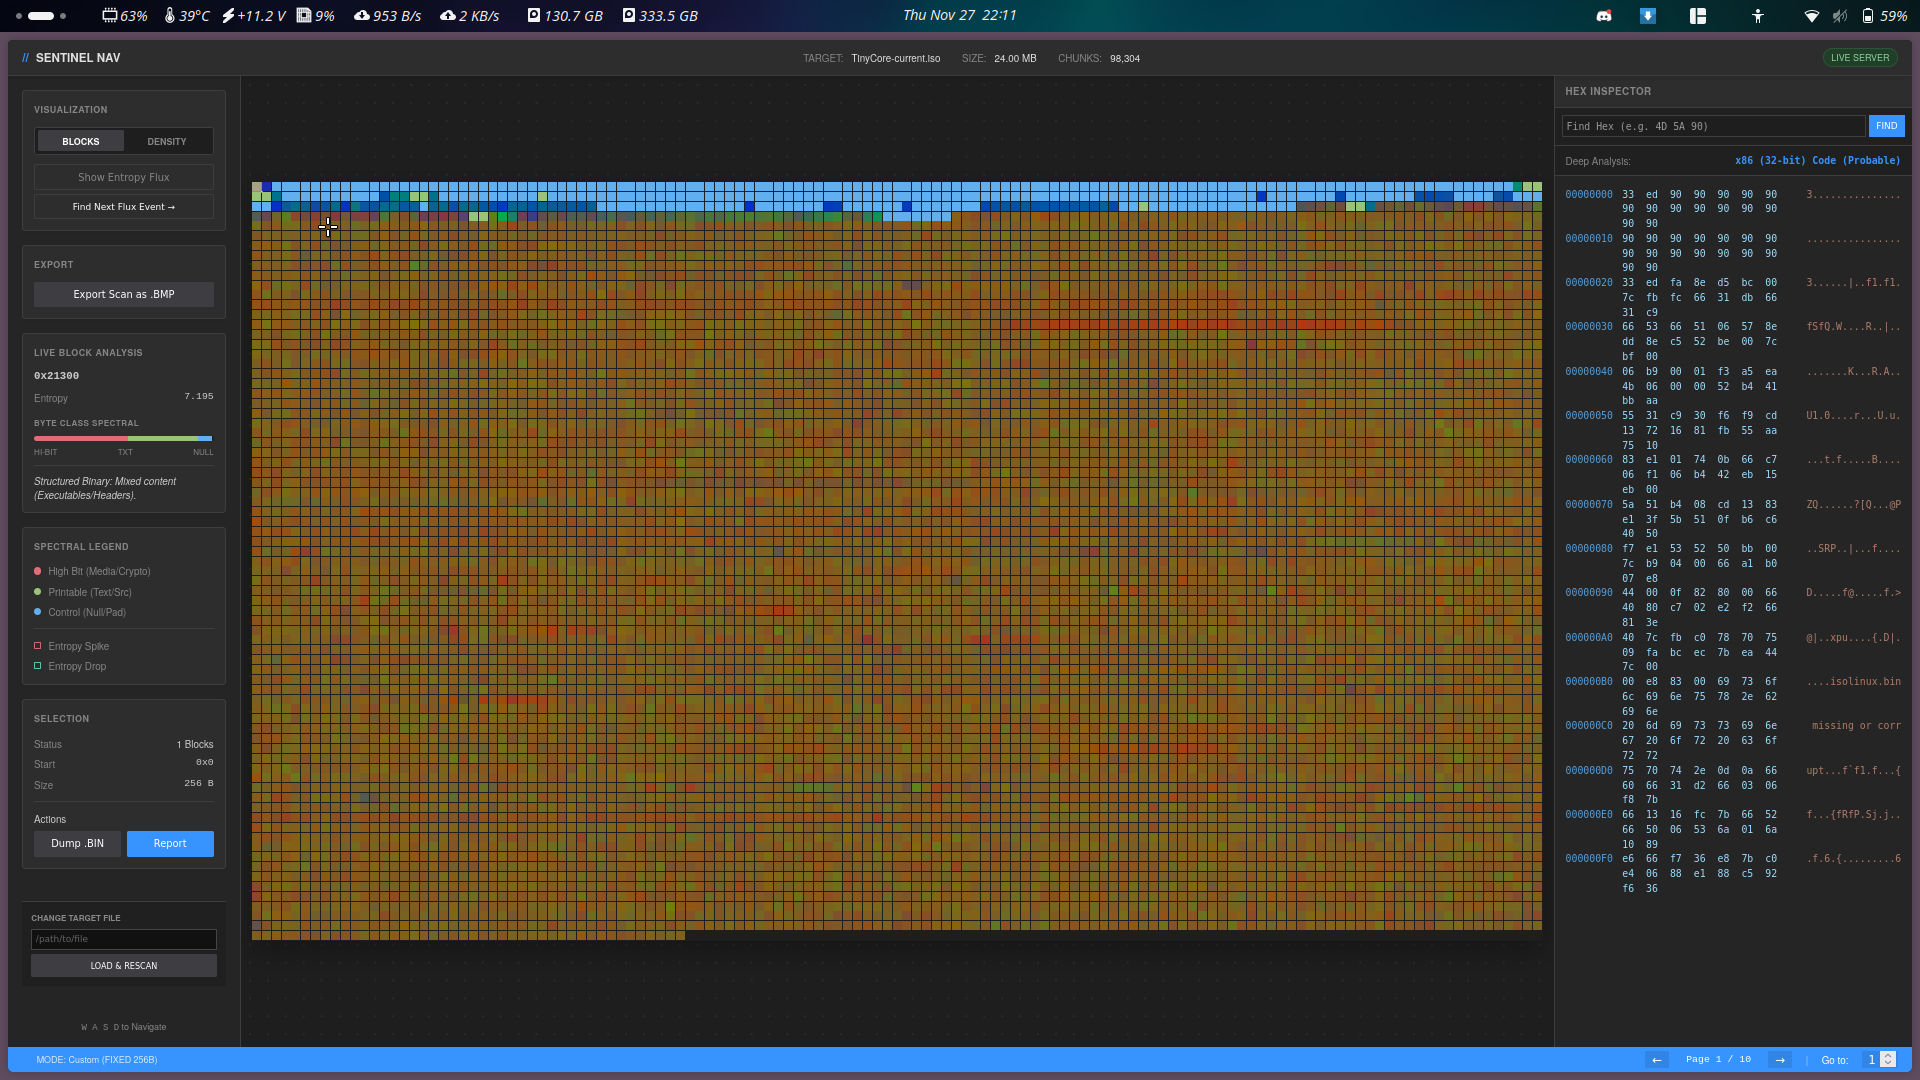 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.