
MEAT
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
data-recoverydigital-forensicsforensics+2
jfarley248/meatThis toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 sleuthkit/scalpel
File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…
 jschicht/logfileparser
Parser for $LogFile on NTFS
 patrickdw123/paranoidf
ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
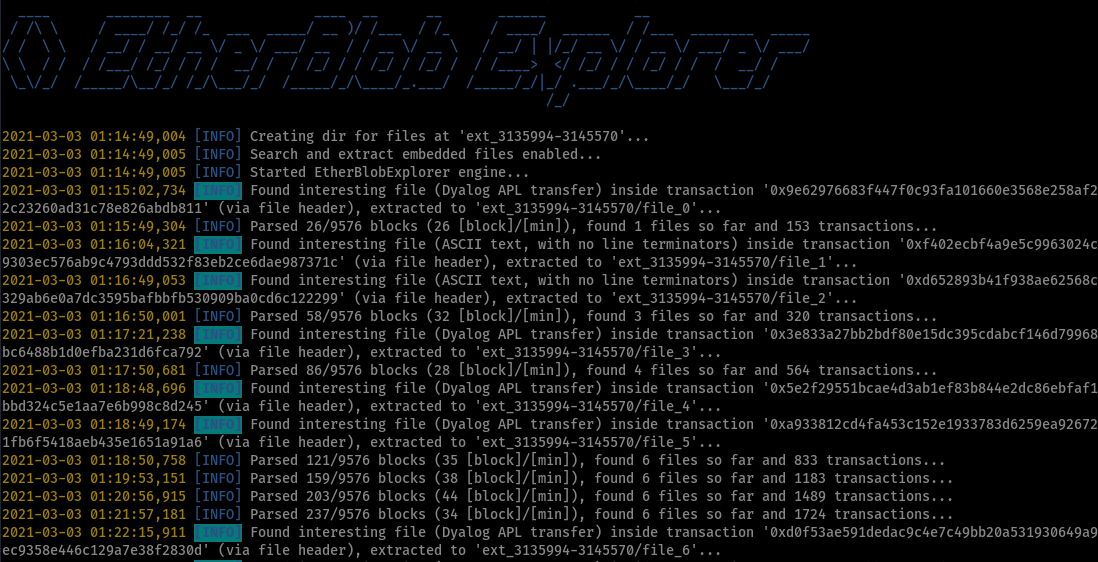 litneet64/etherblob-explorer
Search and extract blob files on the Ethereum Blockchain network
 elevenpaths/iphonerestrictionspasscodebf
Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.
 tchuin2609/yellowkey-bitlocker
Manage BitLocker encrypted drives on Windows. Extract recovery keys, check encryption status, and apply security mitigations for CVE-2026-45585.
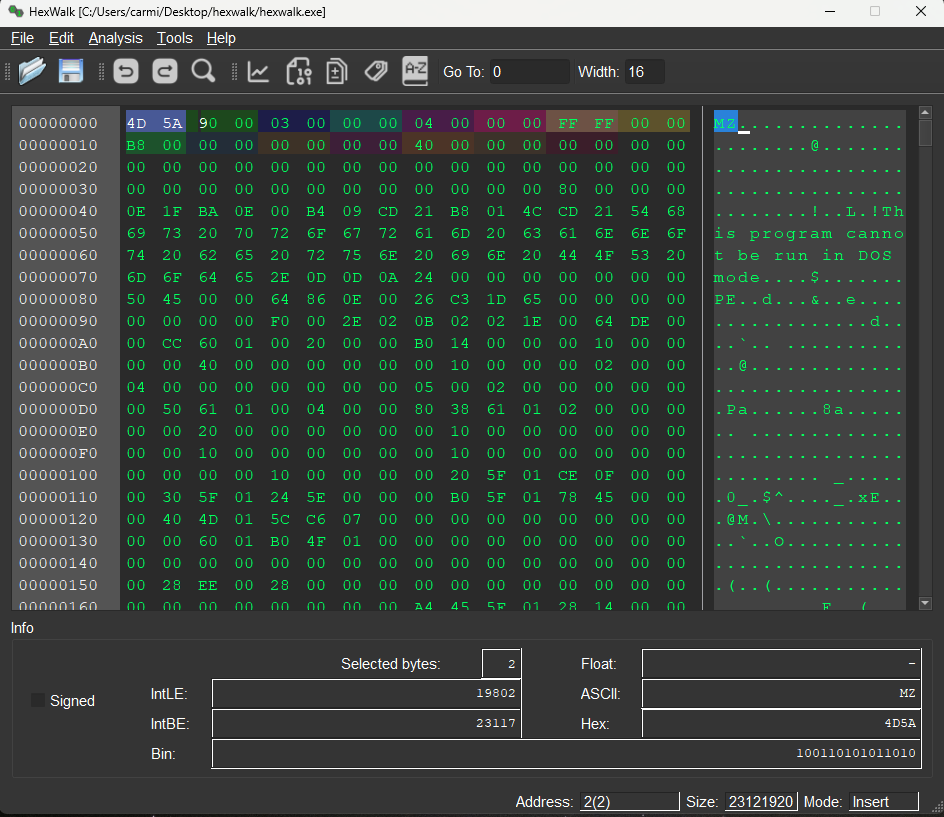 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 thewhiteninja/ntfstool
Forensics tool for NTFS (parser, mft, bitlocker, deleted files)
 threatlabz/tools
Tools developed by the Zscaler ThreatLabz Threat Intelligence team
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 trimstray/reload.sh
Wipe, reinstall or restore your system from running GNU/Linux distribution. Via SSH, without rebooting.
 jschicht/extractusnjrnl
Tool to extract the $UsnJrnl from an NTFS volume
 libyal/libqcow
Library and tools to access the QEMU Copy-On-Write (QCOW) image format
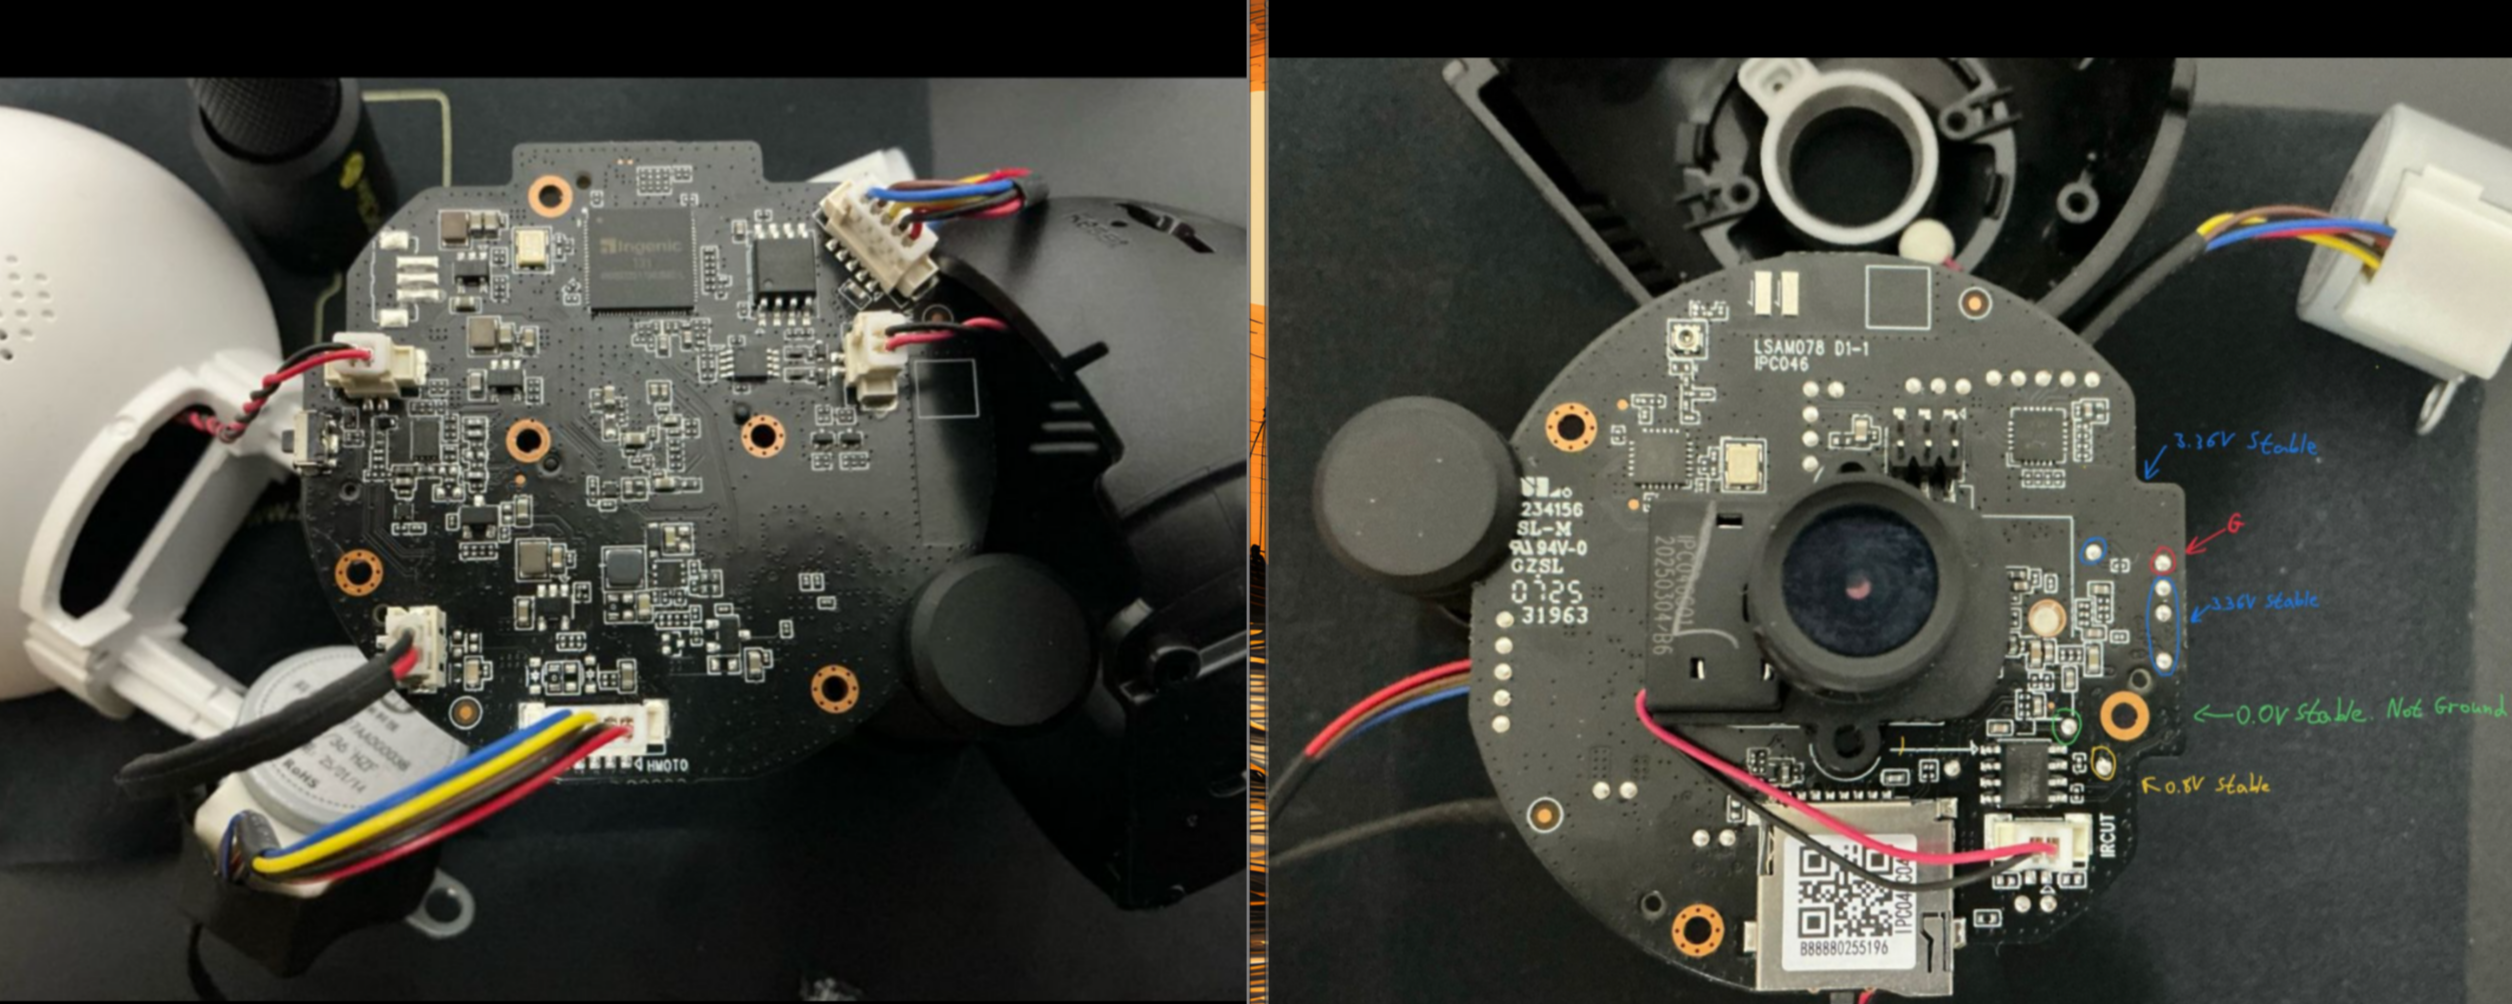 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 permanet/permanet
Cryptographically verifiable web archiving. Playwright capture → SHA-256 Merkle hash → Bitcoin-anchored OpenTimestamps → permanent Arweave storage.