
ParanoiDF
 patrickdw123/paranoidf
ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
data-recoverydigital-forensicsencryption-decryption-tools+6
112
patrickdw123/paranoidfParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 filosottile/age
A simple, modern and secure encryption tool (and Go library) with small explicit keys, no config options, and UNIX-style composability.
 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 wiltodelta/remove-ai-watermarks
Remove visible and invisible AI watermarks and provenance metadata from images and video. Python library and CLI for SynthID, C2PA, EXIF, IPTC, XMP,…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 pgbackrest/pgbackrest
Parallel backup and restore solution for PostgreSQL with encryption, delta restore, and multi-cloud object store support for enterprise disaster…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 cgsecurity/testdisk
Recovers lost partitions and repairs boot sectors; carves 480+ file formats from damaged disks and filesystems for data recovery and forensic use.
 nelenkov/android-backup-extractor
Extract and repack Android ADB backups (ICS+). Supports encrypted archives, tar conversion, and standard I/O for forensic analysis or data recovery.
 bkerler/mtkclient
Mediatek Flash and Repair Utility
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
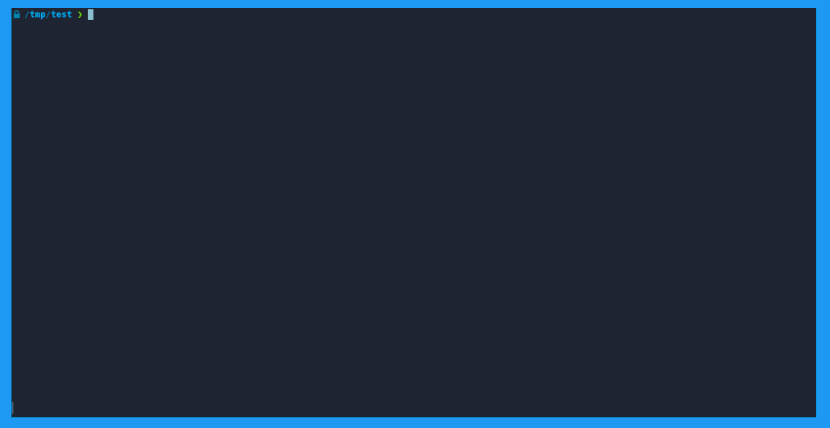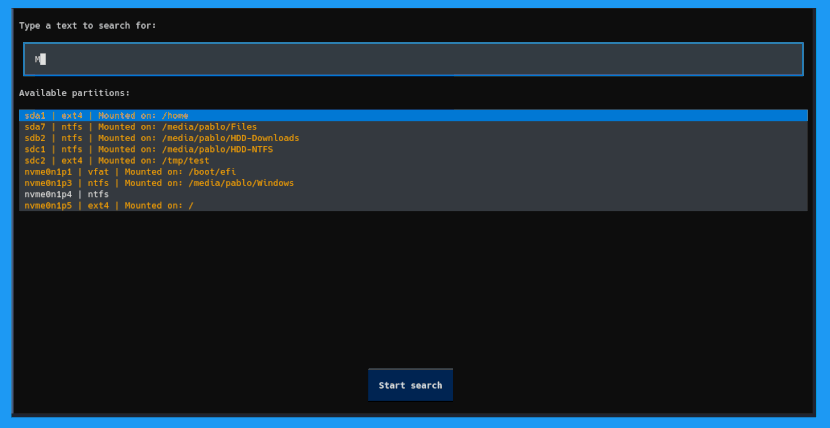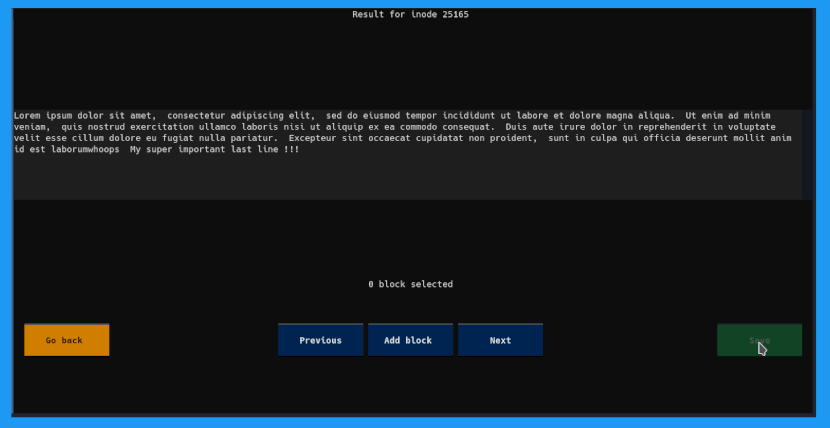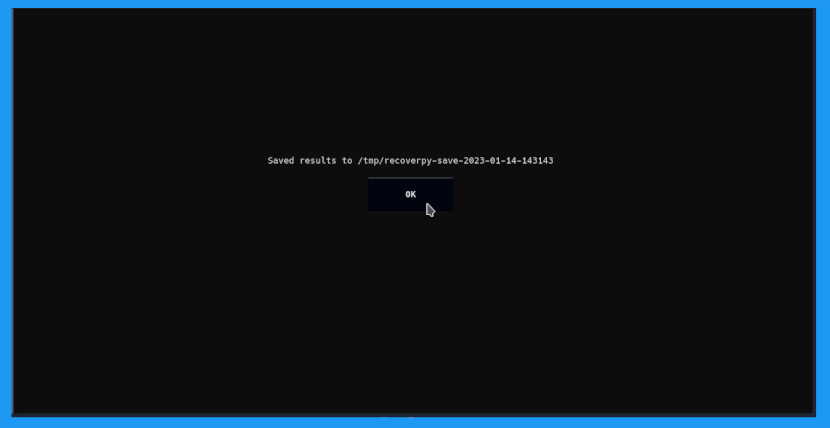 pablolec/recoverpy
Interactively find and recover deleted or :point_right: overwritten :point_left: files from your terminal