
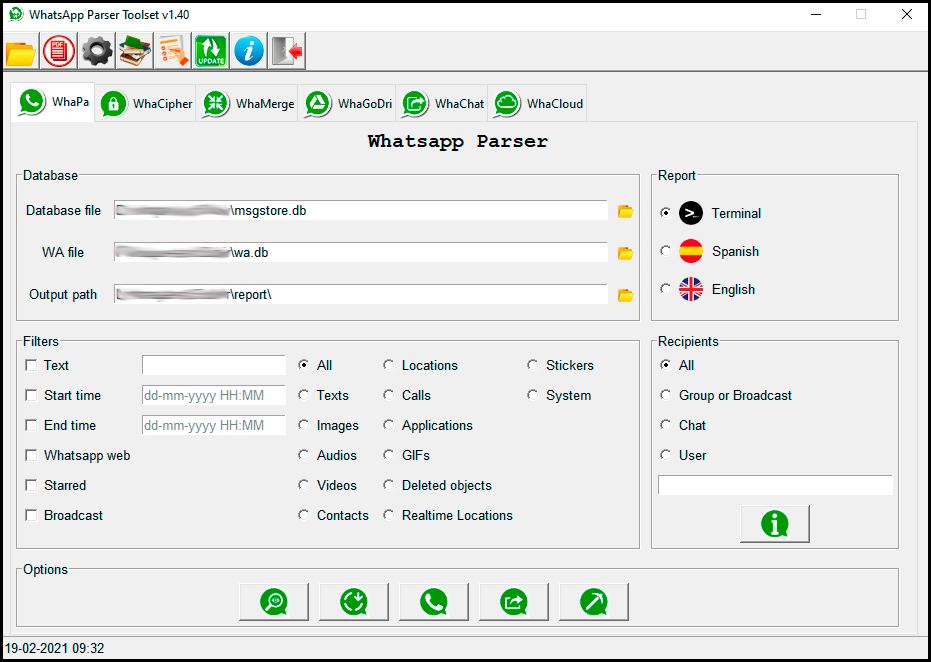
whapa
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
android-securitydata-recoverydigital-forensics+5
1.6k
b16f00t/whapaGraphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 nelenkov/android-backup-extractor
Extract and repack Android ADB backups (ICS+). Supports encrypted archives, tar conversion, and standard I/O for forensic analysis or data recovery.
 labcif/fama
Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser
 nowsecure/android-forensics
Open source Android Forensics app and framework
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 fmd-foss/fmd-android
Find your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…
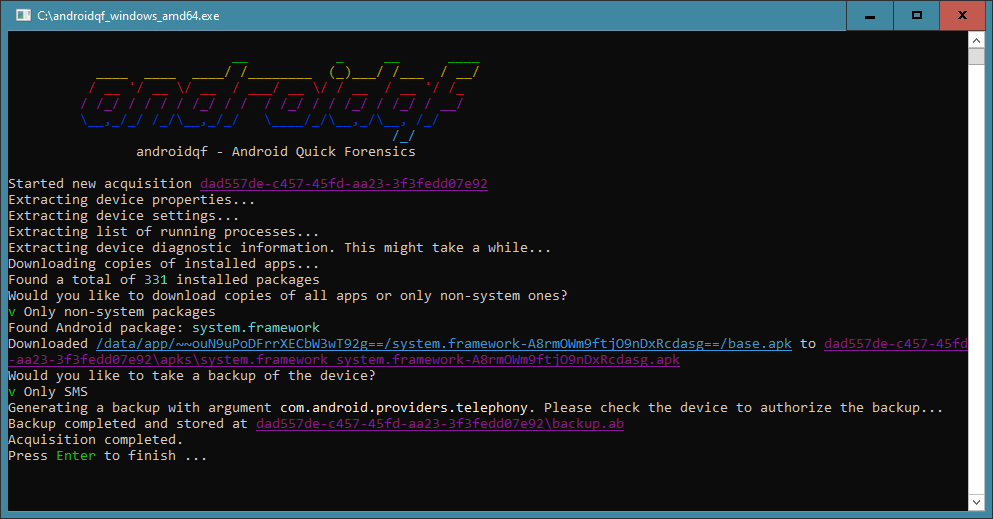 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 jacktekno/chrome-forensic_cve-2024-0044
A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices
 bkerler/mtkclient
Mediatek Flash and Repair Utility

 packetlss/android-locdump
android location service cache dumper
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
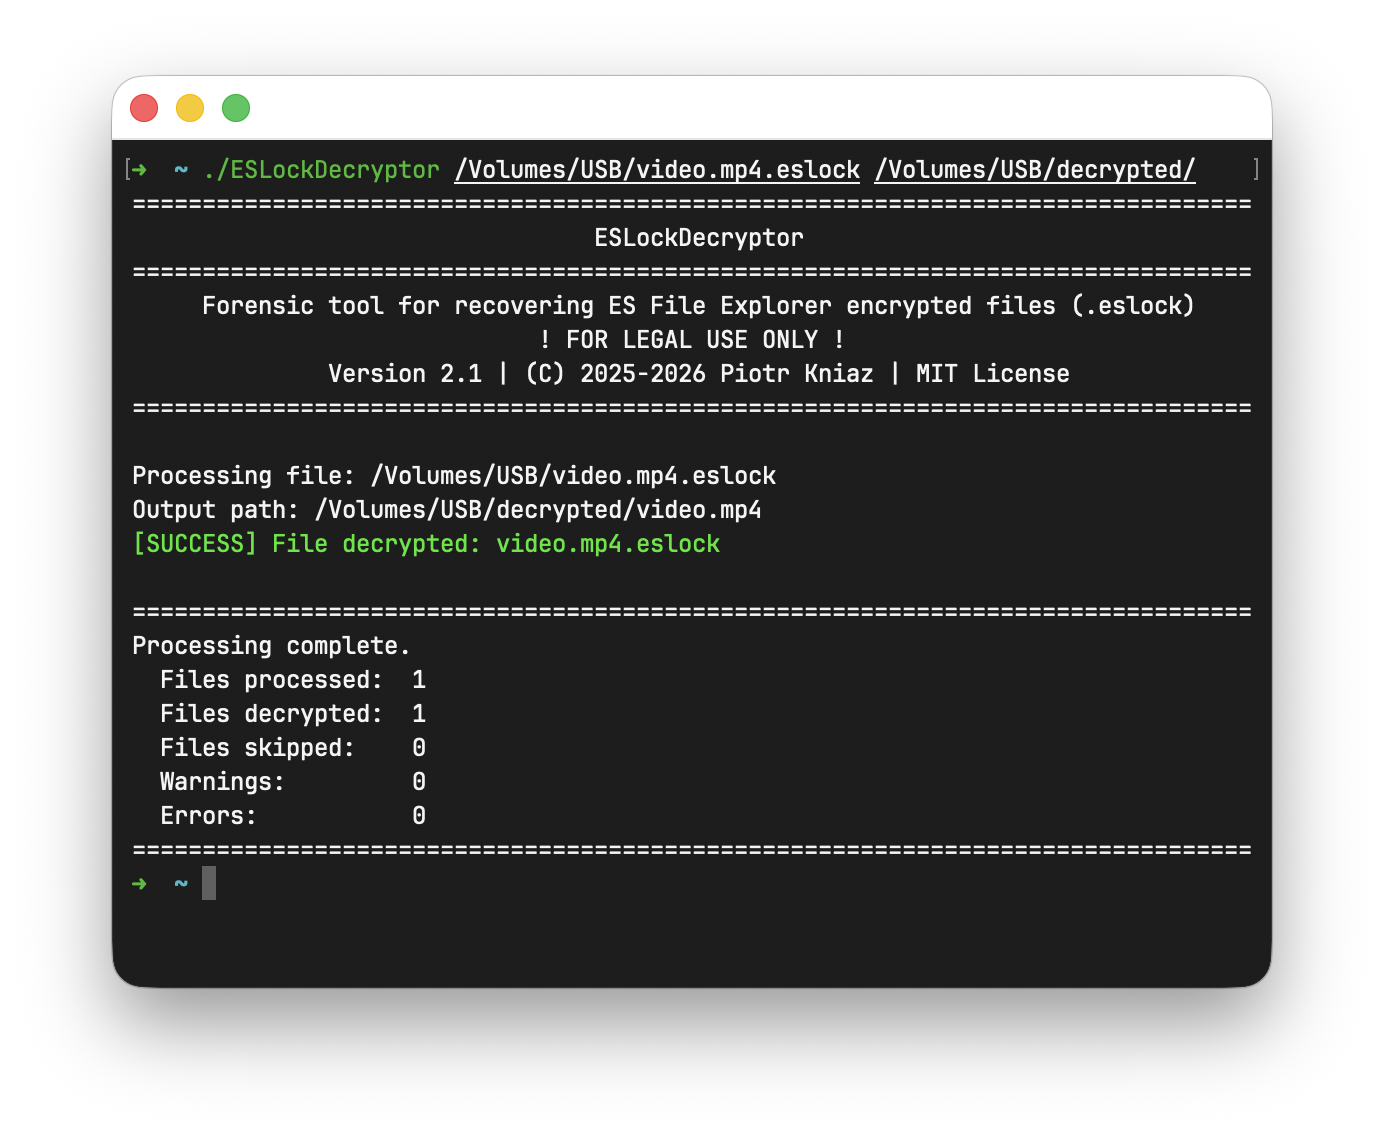 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 pelock/total-commander-ftp-password-recovery-tool-python
Total Commander FTP Password Recovery Tool for Python allows you to decrypt the FTP account password information for all Total Commander versions…
 telegrip/telegrip
GUI forensic tool for acquiring and analyzing Telegram data from Android devices. Parses messages, media, and metadata; generates integrity-verified…
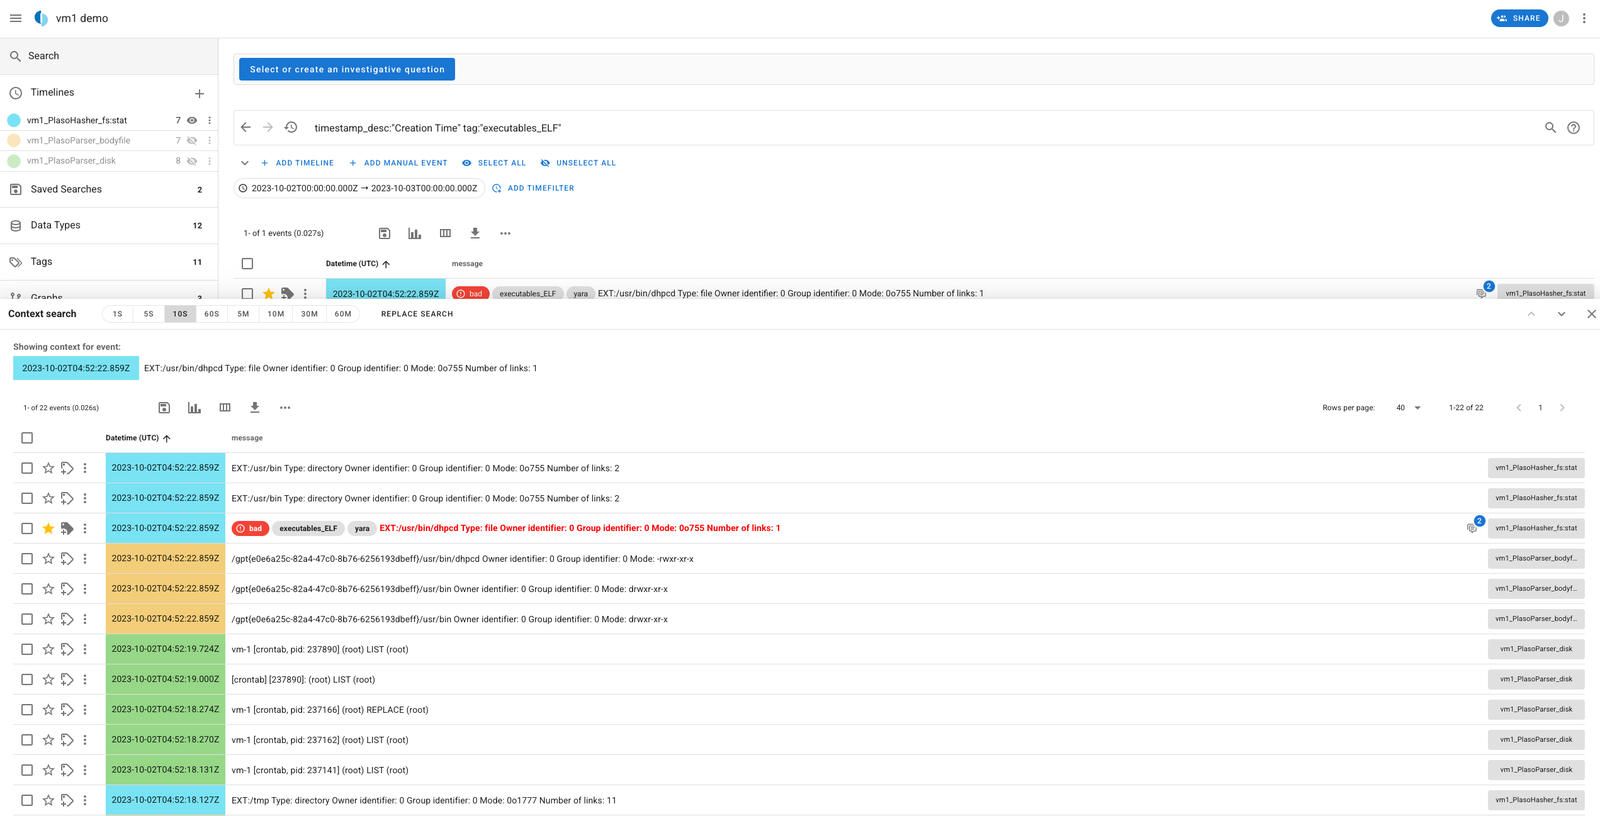 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…