

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
136 results
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k1 day ago
libfwsi preview

libfwsi

GitHublibyal/libfwsi

Library to access the Windows Shell Item format
binary-analysisdata-recoverydigital-forensics+1
752 days ago
interrogate preview

interrogate

GitHubcarmaa/interrogate

Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
binary-analysiscryptographydata-recovery+4
786 years ago
HexWalk preview

HexWalk

GitHubgcarmix/hexwalk

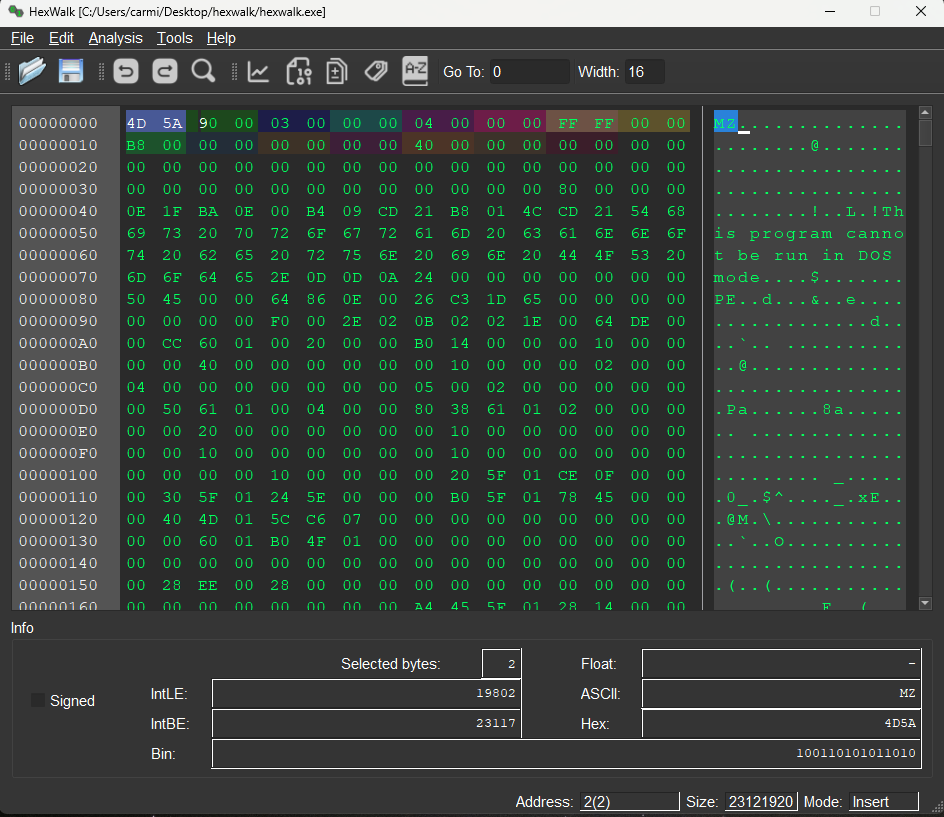
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
binary-analysisdata-recoverydebuggers+7
1.0k13 days ago
hobbits preview

hobbits

GitHubmahlet-inc/hobbits

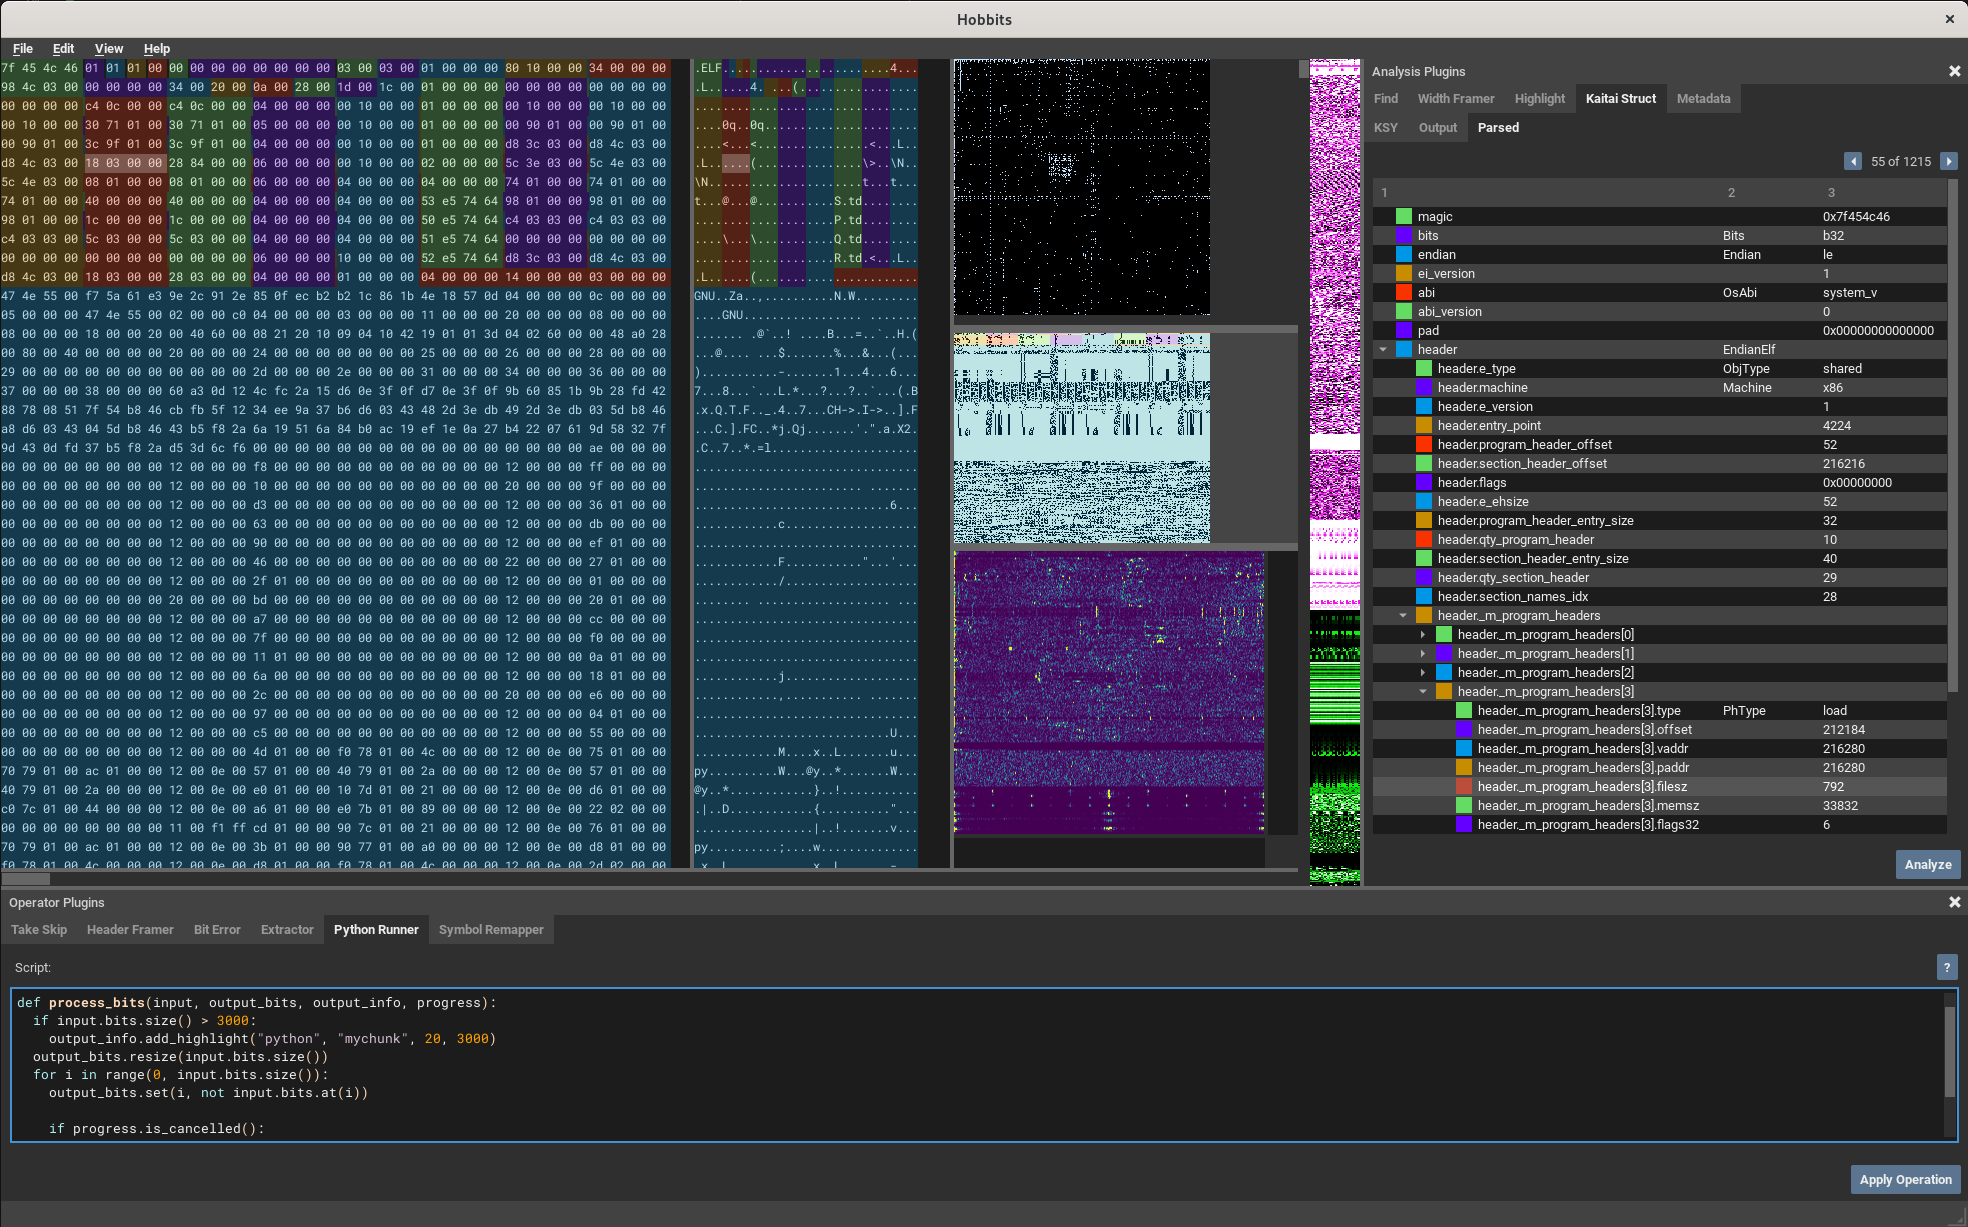
A multi-platform GUI for bit-based analysis, processing, and visualization
binary-analysisdata-recoveryforensics+1
7511 year ago
HiveV5_keystream_decryptor preview

HiveV5_keystream_decryptor

GitHubreecdeep/hivev5_keystream_decryptor

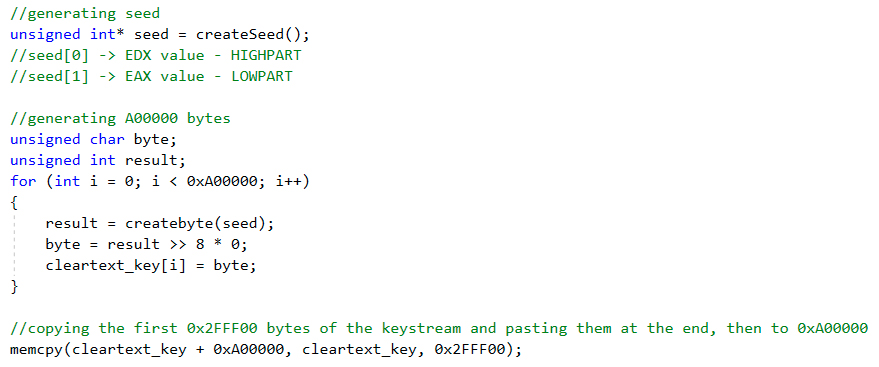
bad stuffs by bad guys

binary-analysiscryptographydata-recovery+4
494 years ago
ME2-Writeup preview

ME2-Writeup

GitHubcoremaze/me2-writeup

Reconstructing a Dead USB Protocol: A Handheld's Secrets Unlocked by a Hot Knife, a multi-disciplinary journey to reviving a forgotten USB interface
binary-analysisdata-recoveryeducation+5
505 months ago
Disk-Arbitrator preview

Disk-Arbitrator

GitHubaburgh/disk-arbitrator

A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.

data-recoverydigital-forensicsdisk-forensics+2
7161 year ago
HiveV5_file_decryptor preview

HiveV5_file_decryptor

GitHubreecdeep/hivev5_file_decryptor

Hive v5 file decryption algorithm
cryptographydata-recoveryencryption-decryption-tools+2
343 years ago
analyzeMFT preview

analyzeMFT

GitHubrowingdude/analyzemft

analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
data-recoverydigital-forensicsdisk-forensics+1
5331 year ago
Concryptor preview

Concryptor

GitHubfrogsnot/concryptor

A gigabyte-per-second, multi-threaded file encryption engine. Achieves extreme throughput using a lock-free, triple-buffered io_uring pipeline, Rayon…

cryptographydata-recoveryencryption-decryption-tools+2
752 months ago
unredactor preview

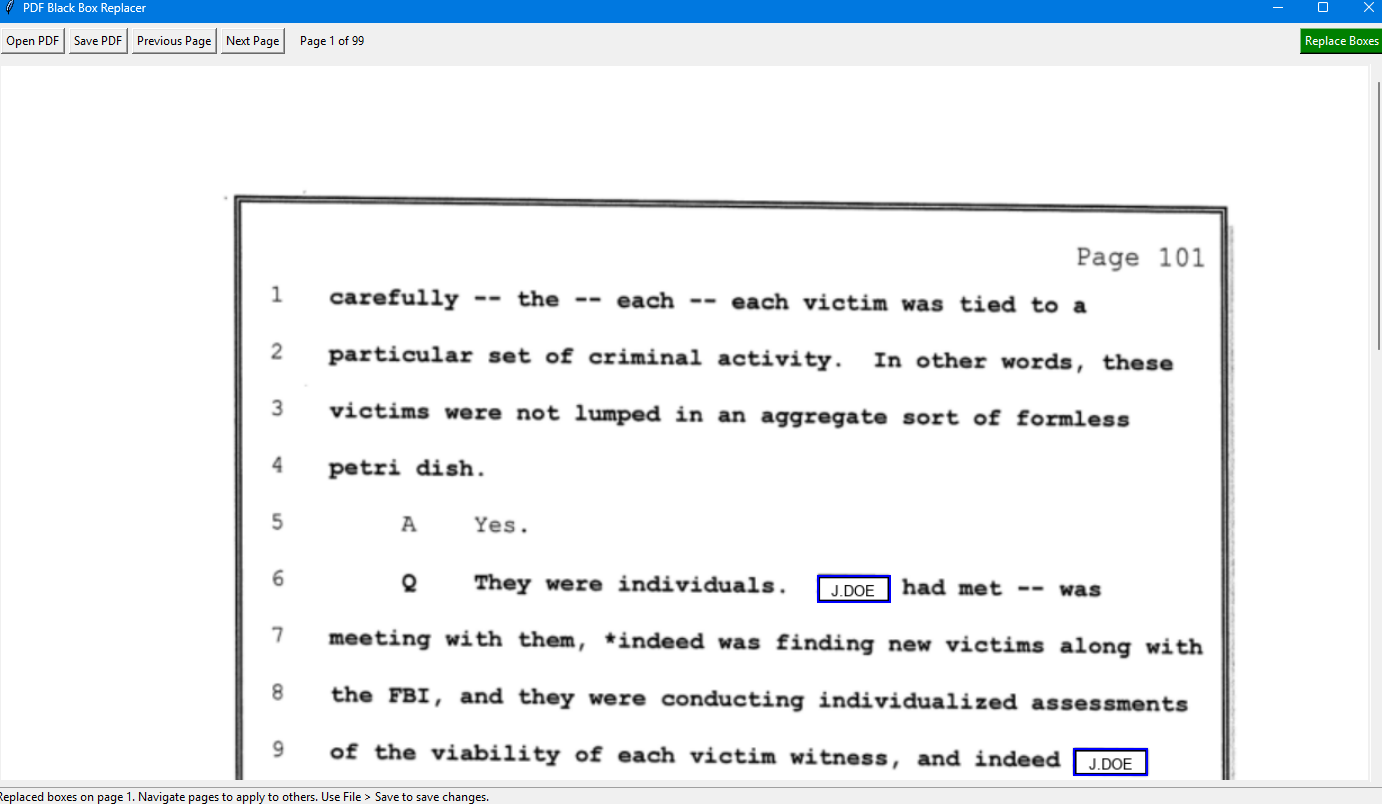
unredactor

GitHubkvthweatt/unredactor

A PDF unredactor.

data-recoverydigital-forensicsforensics+2
447 months ago
ImHex preview

ImHex

GitHubwerwolv/imhex

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

ai-assisted-reversingbinary-analysisbinary-exploitation+10
54.9k3 days ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
3.0k4h 33m ago
libewf preview

libewf

GitHublibyal/libewf

C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…
data-recoverydigital-forensicsdisk-forensics+1
3172 days ago
agent-sweep preview

agent-sweep

GitHubishannaik/agent-sweep

Find and redact secrets in AI coding agent histories (Claude Code, and more).
data-exfiltrationdata-recoveryforensics+3
8520 days ago
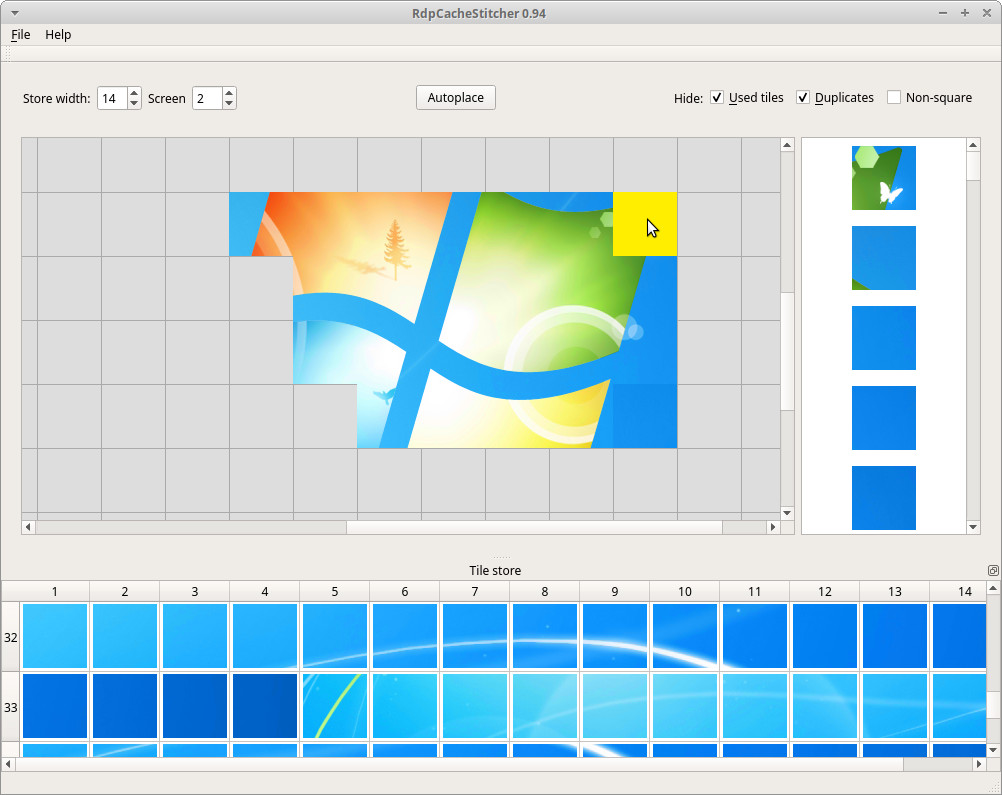
RdpCacheStitcher preview

RdpCacheStitcher

GitHubbsi-bund/rdpcachestitcher

RdpCacheStitcher is a tool that supports forensic analysts in reconstructing useful images out of RDP cache bitmaps.

data-recoverydigital-forensicsforensics+1
3345 years ago
ios_Restriction_PassCode_Crack---Python-version preview

ios_Restriction_PassCode_Crack---Python-version

GitHubyuejd/ios_restriction_passcode_crack---python-version

Crack ios Restriction PassCode in Python

data-recoveryforensicsios-security+2
4012 years ago
Previous12…8Next