
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
146 results
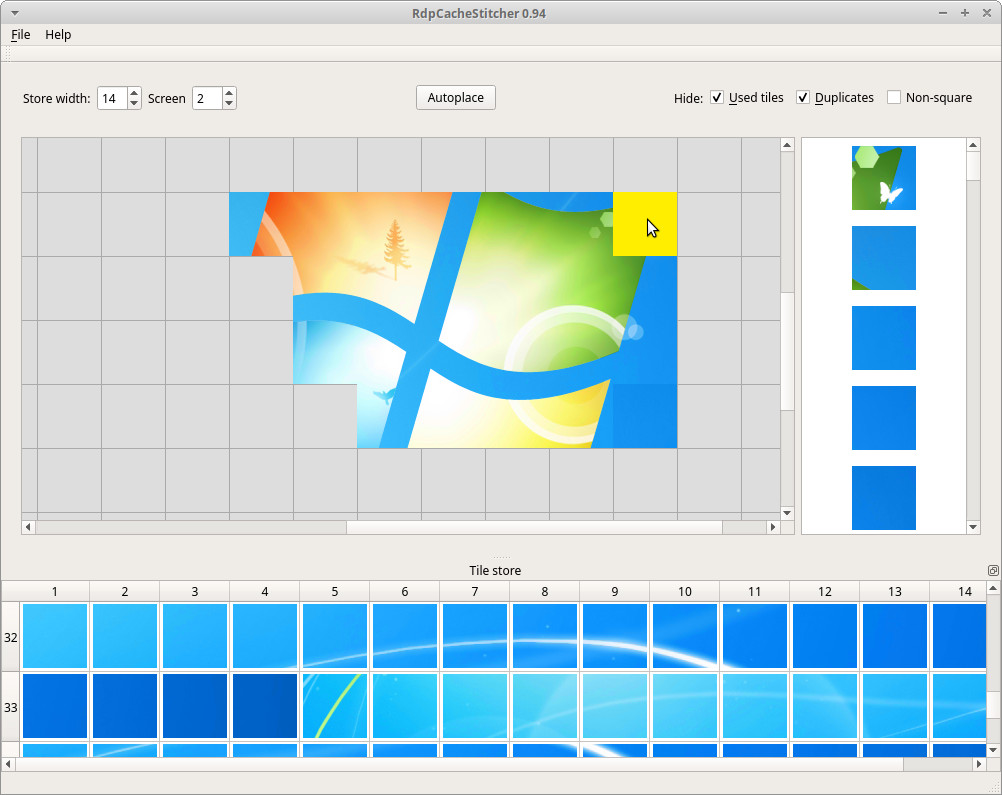
RdpCacheStitcher preview

RdpCacheStitcher

GitHubbsi-bund/rdpcachestitcher

RdpCacheStitcher is a tool that supports forensic analysts in reconstructing useful images out of RDP cache bitmaps.
data-recoverydigital-forensicsforensics+1
333
5 years ago
agent-sweep preview

agent-sweep

GitHubishannaik/agent-sweep

Find and redact secrets in AI coding agent histories (Claude Code, and more).
data-exfiltrationdata-recoveryforensics+3
8211 days ago
pcapfex preview

pcapfex

GitHubvikwin/pcapfex

'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
data-recoverydigital-forensicsforensics+2
2306 years ago
ATAboy preview

ATAboy

GitHubredrum0381/ataboy

ATAboy is a user-friendly bridge that allows legacy CHS only style IDE (PATA) hard drives to be connected to a modern computer as a standard USB Mass…

data-recoverydigital-forensicsembedded-systems-security+4
2033 months ago
libfwsi preview

libfwsi

GitHublibyal/libfwsi

Library to access the Windows Shell Item format
binary-analysisdata-recoverydigital-forensics+1
753 days ago
ExtractUsnJrnl preview

ExtractUsnJrnl

GitHubjschicht/extractusnjrnl

Tool to extract the $UsnJrnl from an NTFS volume
data-recoverydigital-forensicsdisk-forensics+1
1127 years ago
MEAT preview

MEAT

GitHubjfarley248/meat

This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
data-recoverydigital-forensicsforensics+2
1696 years ago
ntfsDump preview

ntfsDump

GitHub3gstudent/ntfsdump

Use to copy a file from an NTFS partitioned volume by reading the raw volume and parsing the NTFS structures.
data-exfiltrationdata-recoverydigital-forensics+3
1195 years ago
dbslice preview

dbslice

GitHubnabroleonx/dbslice

Extract a slice of your production database to reproduce bugs locally. Point dbslice at a record, it follows foreign keys and gives you a complete,…
configuration-auditingdatabase-securitydata-recovery+3
1432 months ago
SentinelNav preview

SentinelNav

GitHubsmolfiddle/sentinelnav

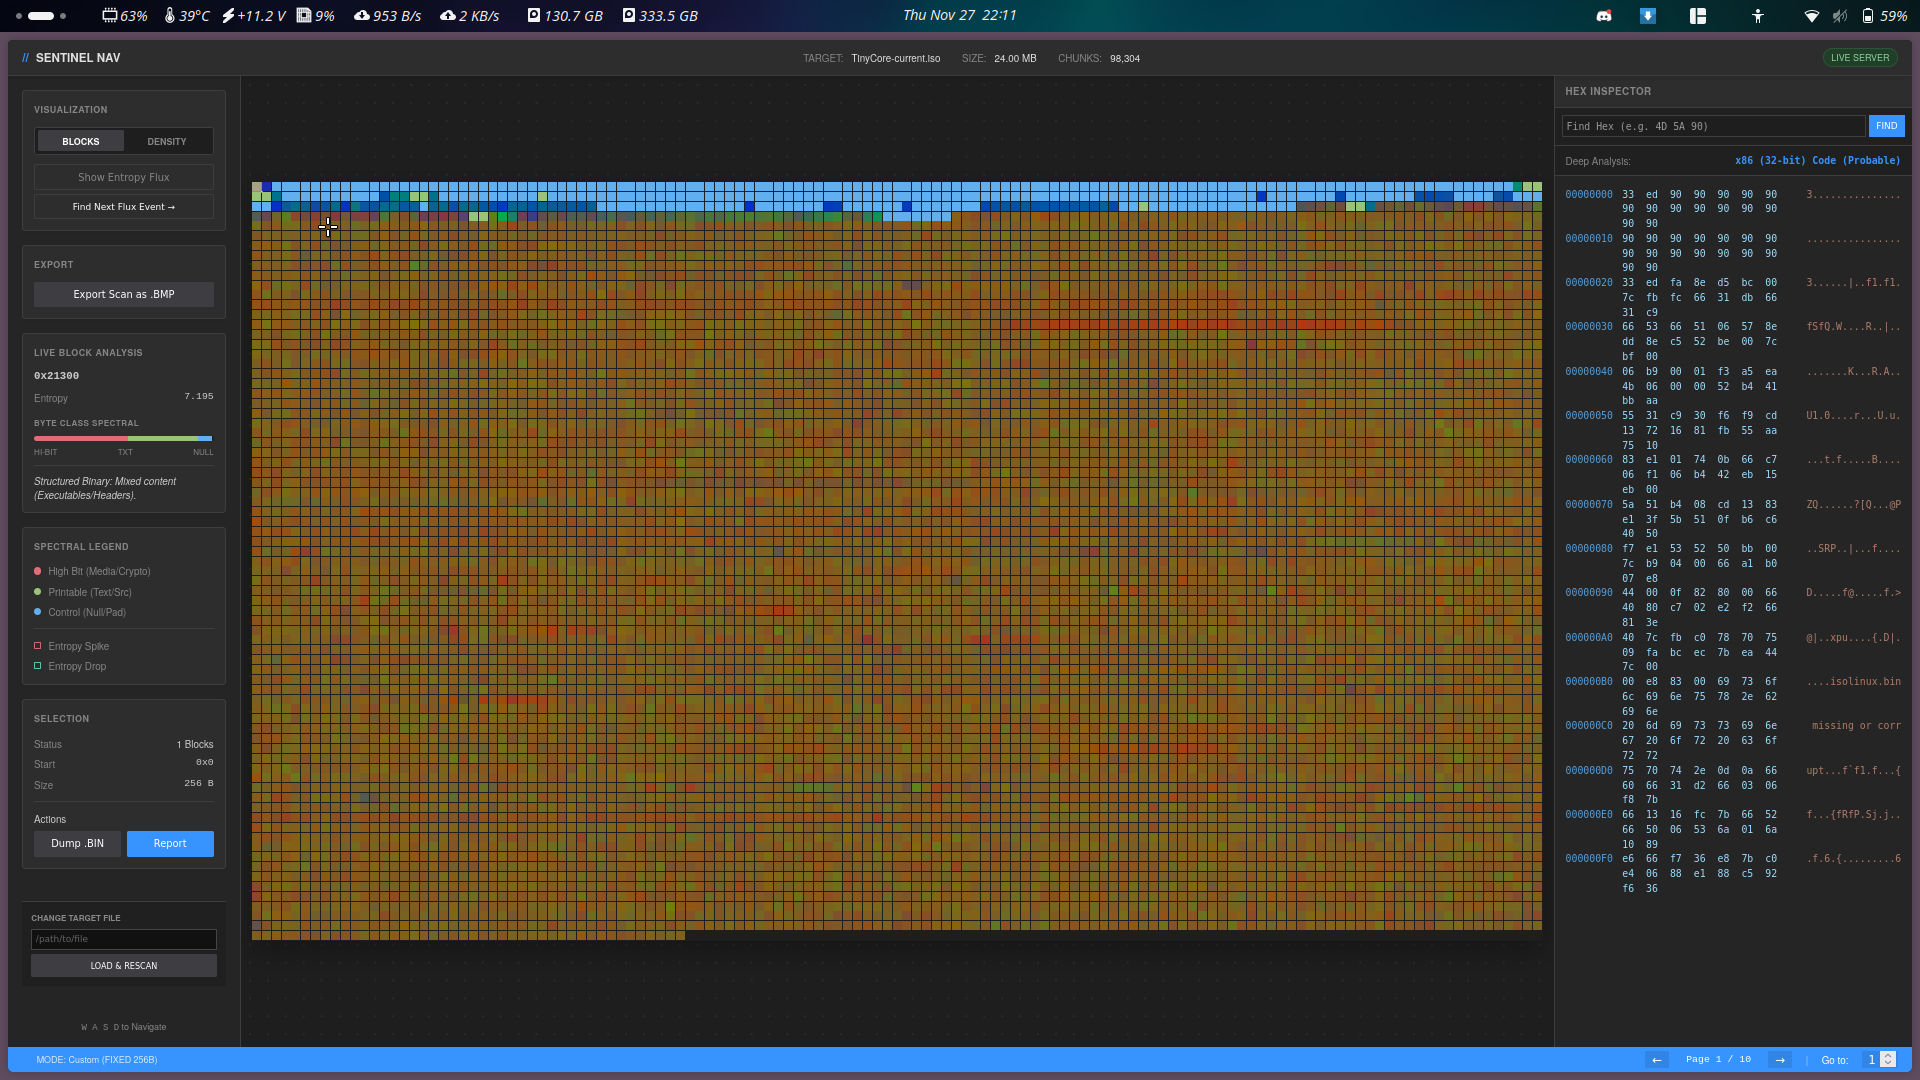
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
binary-analysisdata-recoverydigital-forensics+4
1489 months ago
Concryptor preview

Concryptor

GitHubfrogsnot/concryptor

A gigabyte-per-second, multi-threaded file encryption engine. Achieves extreme throughput using a lock-free, triple-buffered io_uring pipeline, Rayon…

cryptographydata-recoveryencryption-decryption-tools+2
752 months ago
pdfresurrect preview

pdfresurrect

GitHubenferex/pdfresurrect

Analyze and help extract older "hidden" versions of a pdf from the current pdf.
data-recoverydigital-forensicsstatic-analysis
1054 years ago
Exif-Grabber preview

Exif-Grabber

GitHubd4vinci/exif-grabber

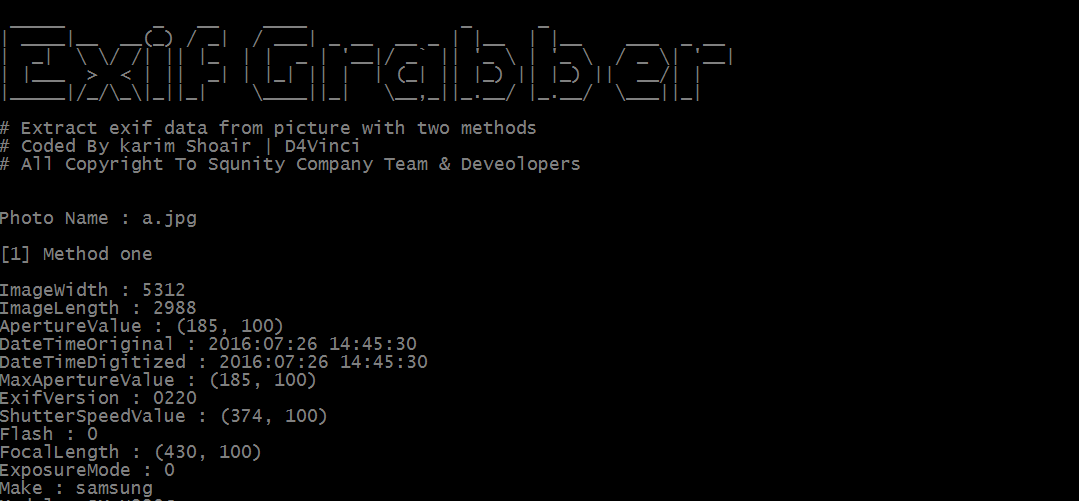
A python tool that will extract exif data from picture with two methods
data-recoverydigital-forensicsforensics+3
4310 years ago
MK4001MTD-USB-Bridge preview

MK4001MTD-USB-Bridge

GitHubwill127534/mk4001mtd-usb-bridge

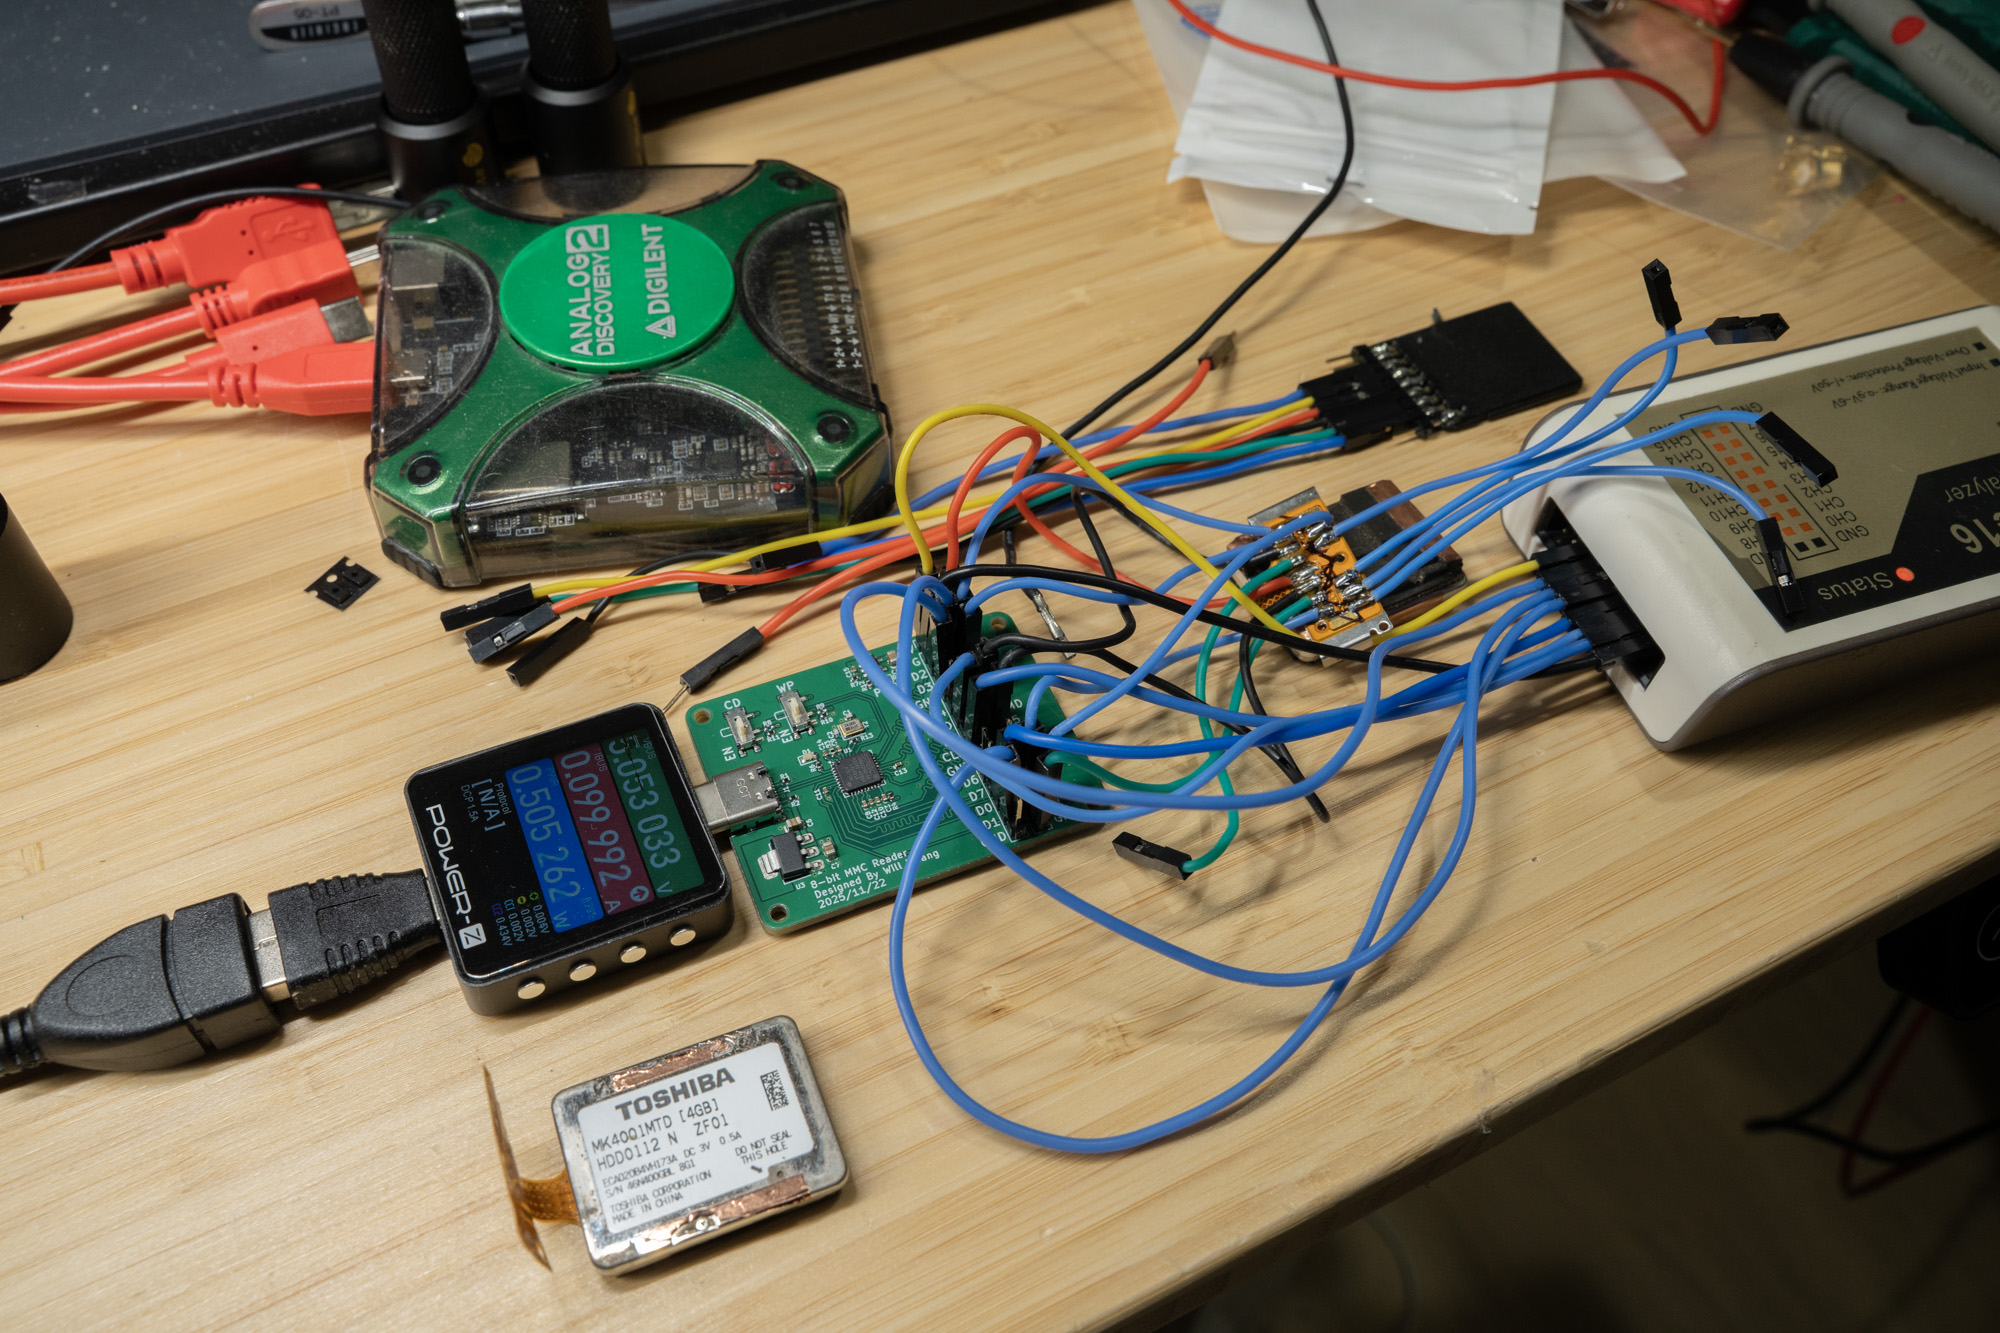
RP2040 firmware that bridges a Toshiba MK4001MTD 0.85" SDIO microdrive as a USB mass storage device, implementing the full SDIO-ATA protocol stack…
data-recoveryembedded-systems-securityfirmware-analysis+4
442 months ago
unredactor preview

unredactor

GitHubkvthweatt/unredactor

A PDF unredactor.

data-recoverydigital-forensicsforensics+2
437 months ago
HiveV5_keystream_decryptor preview

HiveV5_keystream_decryptor

GitHubreecdeep/hivev5_keystream_decryptor

bad stuffs by bad guys
binary-analysiscryptographydata-recovery+4
494 years ago
tird preview

tird

GitHubhakavlad/tird

Steganographic storage & File encryption tool
cryptographydata-recoveryencryption-decryption-tools+3
223 months ago
wcw-cyberring-pav-decryptor preview

wcw-cyberring-pav-decryptor

GitHubblakebratcher/wcw-cyberring-pav-decryptor

Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…

binary-analysiscryptographydata-recovery+5
257 months ago
Previous1…567…9Next