
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
136 results
libvmdk preview

libvmdk

GitHublibyal/libvmdk

Library and tools to access the VMware Virtual Disk (VMDK) format

data-recoverydigital-forensicsdisk-forensics
1872 days ago
DroneXtract preview

DroneXtract

GitHubang13t/dronextract

Digital forensics suite for DJI drones that parses telemetry files, extracts hidden data via steganography, visualizes flight paths, and detects…
anomaly-detectiondata-recoverydigital-forensics+3
3703 years ago
libvhdi preview

libvhdi

GitHublibyal/libvhdi

Library and tools to access the Virtual Hard Disk (VHD) image format
data-recoverydigital-forensicsdisk-forensics+1
1472 days ago
libvshadow preview

libvshadow

GitHublibyal/libvshadow

Library and tools to access the Volume Shadow Snapshot (VSS) format
data-recoverydigital-forensicsdisk-forensics+2
1192 days ago
UnderlayCopy preview

UnderlayCopy

GitHubkfallahi/underlaycopy

PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
data-recoverydigital-forensicsdisk-forensics+3
25611 months ago
dwipe preview

dwipe

GitHubjoedefen/dwipe

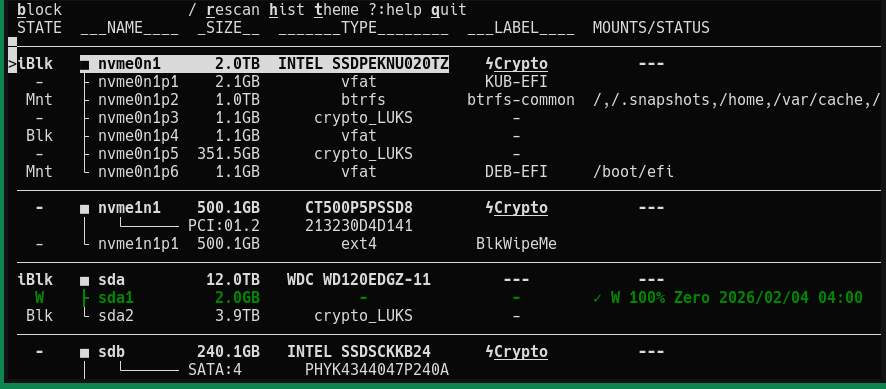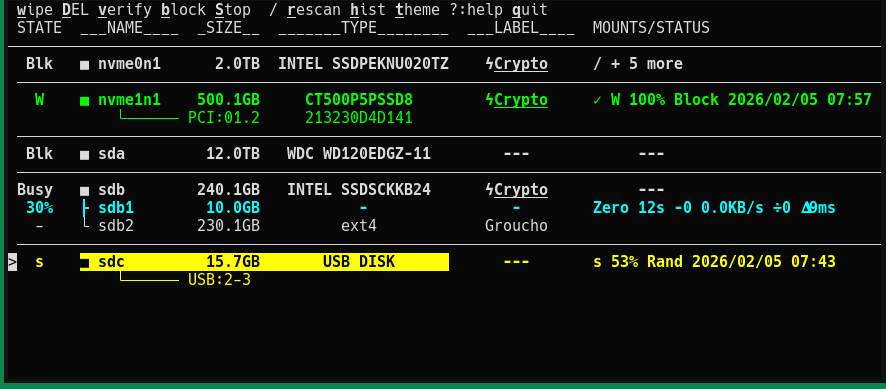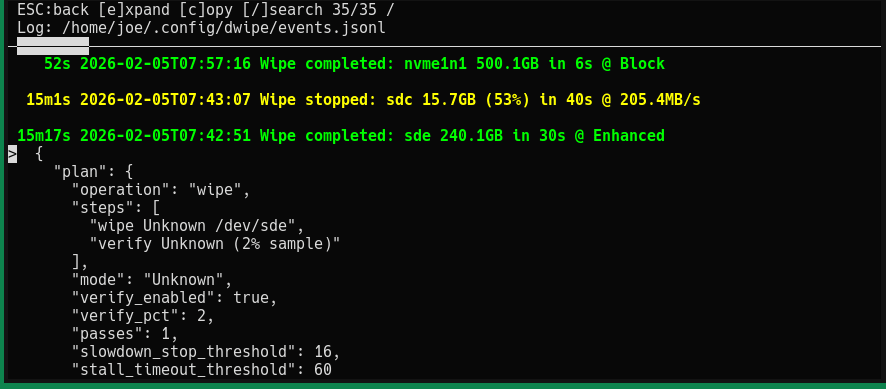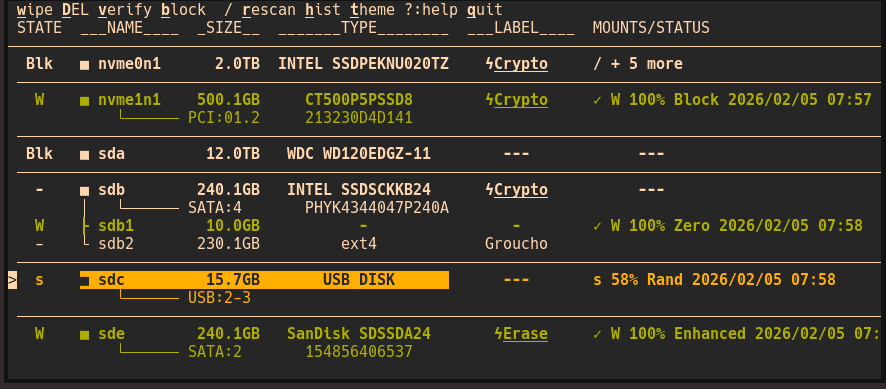
Tool to securely and efficiently wipe devices and partiitions for Linux
data-recoveryencryption-decryption-toolsforensics+3
1647 months ago
ATAboy preview

ATAboy

GitHubredrum0381/ataboy

ATAboy is a user-friendly bridge that allows legacy CHS only style IDE (PATA) hard drives to be connected to a modern computer as a standard USB Mass…
data-recoverydigital-forensicsembedded-systems-security+4
2044 months ago
pcapfex preview

pcapfex

GitHubvikwin/pcapfex

'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
data-recoverydigital-forensicsforensics+2
2306 years ago
tscopy preview

tscopy

GitHubtrustedsec/tscopy

Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…

data-recoverydigital-forensicsdisk-forensics+2
1034 years ago
Centry preview

Centry

GitHub0xpoly/centry

Panic button for protection against cold boot attacks

data-recoverydefensive-toolsencryption-decryption-tools+3
1464 years ago
reload.sh preview

reload.sh

GitHubtrimstray/reload.sh

Wipe, reinstall or restore your system from running GNU/Linux distribution. Via SSH, without rebooting.
data-recoverygeneral-purpose-utilities
2881 year ago
tools preview

tools

GitHubthreatlabz/tools

Tools developed by the Zscaler ThreatLabz Threat Intelligence team
data-recoverydigital-forensicsencryption-decryption-tools+4
1063 months ago
ParanoiDF preview

ParanoiDF

GitHubpatrickdw123/paranoidf

ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
data-recoverydigital-forensicsencryption-decryption-tools+6
1123 years ago
BareMetal-RAM-Dumper preview

BareMetal-RAM-Dumper

GitHubpiat0n/baremetal-ram-dumper

A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.

data-recoverydigital-forensicsexploitation+3
1042 months ago
pdfresurrect preview

pdfresurrect

GitHubenferex/pdfresurrect

Analyze and help extract older "hidden" versions of a pdf from the current pdf.
data-recoverydigital-forensicsstatic-analysis
1064 years ago
CVE-2023-21036 preview

CVE-2023-21036

GitHubinfobyte/cve-2023-21036

Detection and sanitization for Acropalypse Now - CVE-2023-21036
data-recoverydigital-forensicsencryption-decryption-tools+3
803 years ago
Exif-Grabber preview

Exif-Grabber

GitHubd4vinci/exif-grabber

A python tool that will extract exif data from picture with two methods
data-recoverydigital-forensicsforensics+3
4310 years ago
extundelete preview

extundelete

GitHubcherojeong/extundelete

Undelete and recover accidentally erased files from ext3 and ext4 filesystems, using inode scanning and block recovery for forensic and data-loss…

data-recoverydigital-forensicsdisk-forensics
5310 years ago
Previous1…5678Next