
FMD Android
 fmd-foss/fmd-android
Find your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…
android-securitydata-recoverydefensive-tools+3
529
fmd-foss/fmd-androidFind your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…

 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 piotr-kniaz/eslockdecryptor
Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)
 bkerler/mtkclient
Mediatek Flash and Repair Utility
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 tchuin2609/yellowkey-bitlocker
Manage BitLocker encrypted drives on Windows. Extract recovery keys, check encryption status, and apply security mitigations for CVE-2026-45585.
 threatlabz/tools
Tools developed by the Zscaler ThreatLabz Threat Intelligence team
 keerthivasan-sankar/secure-vault-for-commercial
secure vault for your files
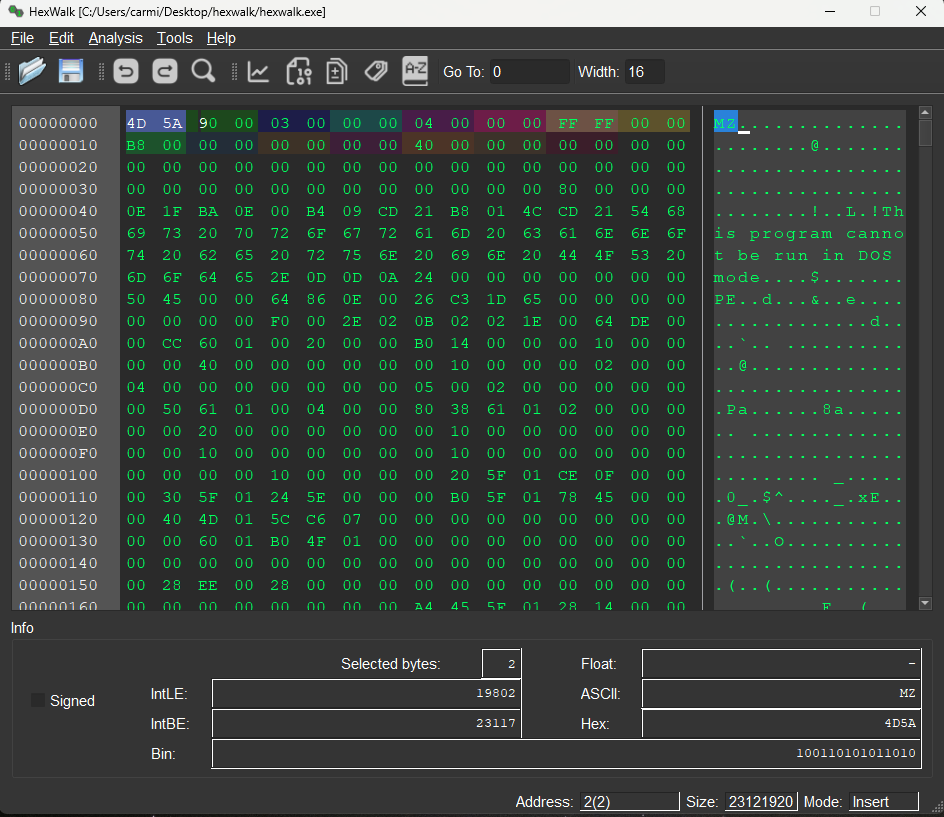 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 nelenkov/android-backup-extractor
Extract and repack Android ADB backups (ICS+). Supports encrypted archives, tar conversion, and standard I/O for forensic analysis or data recovery.
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
 c-sprinks/bitlocker-bypass-research
BitLocker full-disk encryption bypass research using CVE-2023-21563 (BitPixie). Methodology, exploit chain, and defensive recommendations.
 libyal/libqcow
Library and tools to access the QEMU Copy-On-Write (QCOW) image format
 thewhiteninja/ntfstool
Forensics tool for NTFS (parser, mft, bitlocker, deleted files)
 jschicht/logfileparser
Parser for $LogFile on NTFS