

sleuthkit
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
data-recoverydigital-forensicsdisk-forensics+3
3.2k
sleuthkit/sleuthkitForensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 g4sp4rcs/cve-2023-32784-password-combinator-fixer
After using the KeePass password dumper maybe some character parsed as ● is incorrect and you want to know the real character
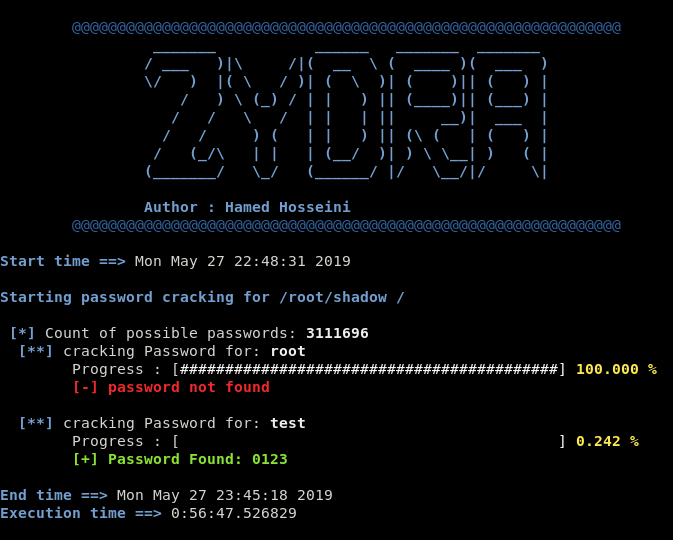 hameda2/zydra
Multi-threaded password recovery tool for RAR, ZIP, PDF, and Linux shadow files using dictionary and brute-force methods with configurable character…
 jessek/hashdeep
Cross-platform hashing toolset for computing message digests (MD5, SHA-1, SHA-256, Tiger, Whirlpool) with recursive directory traversal and file…