

memory-forensic
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
binary-analysiscontainer-escapedata-recovery+7
13
securityronin/memory-forensicWalk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
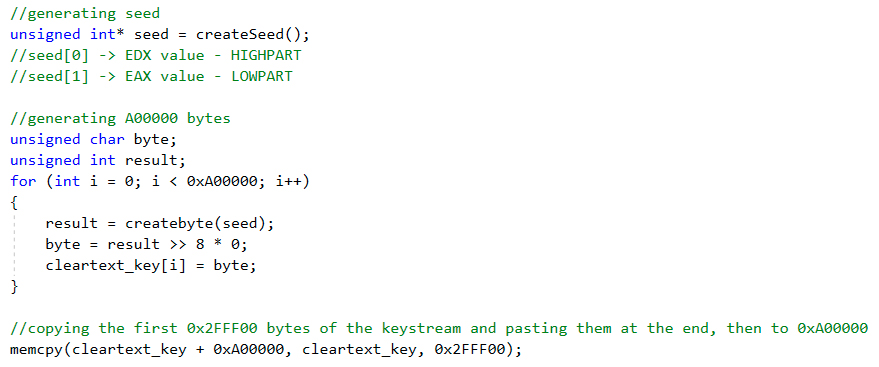 reecdeep/hivev5_keystream_decryptor
bad stuffs by bad guys
 jschicht/logfileparser
Parser for $LogFile on NTFS
 jas502n/010-editor-template
Binary template repository for 010 Editor, providing .bt scripts for parsing executables, filesystem images, registry hives, and forensic artifacts…
 libyal/libfwsi
Library to access the Windows Shell Item format
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 bmaia/binwally
Binary and Directory tree comparison tool using Fuzzy Hashing

 packetlss/android-locdump
android location service cache dumper

 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
 m31r0n/sniprecover-cli
Detection and restoration of Windows Snipping Tool PNG captures vulnerable to CVE-2023-28303
 jacktekno/chrome-forensic_cve-2024-0044
A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices
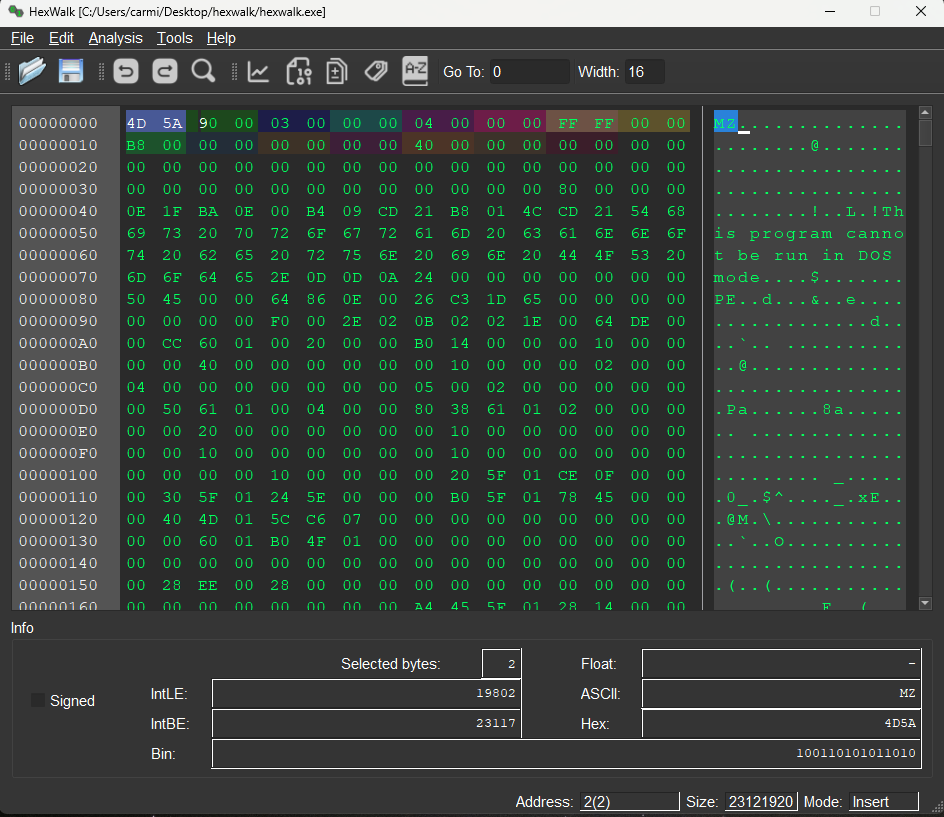 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 dimareverse/nuitka-static-unpacker
Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
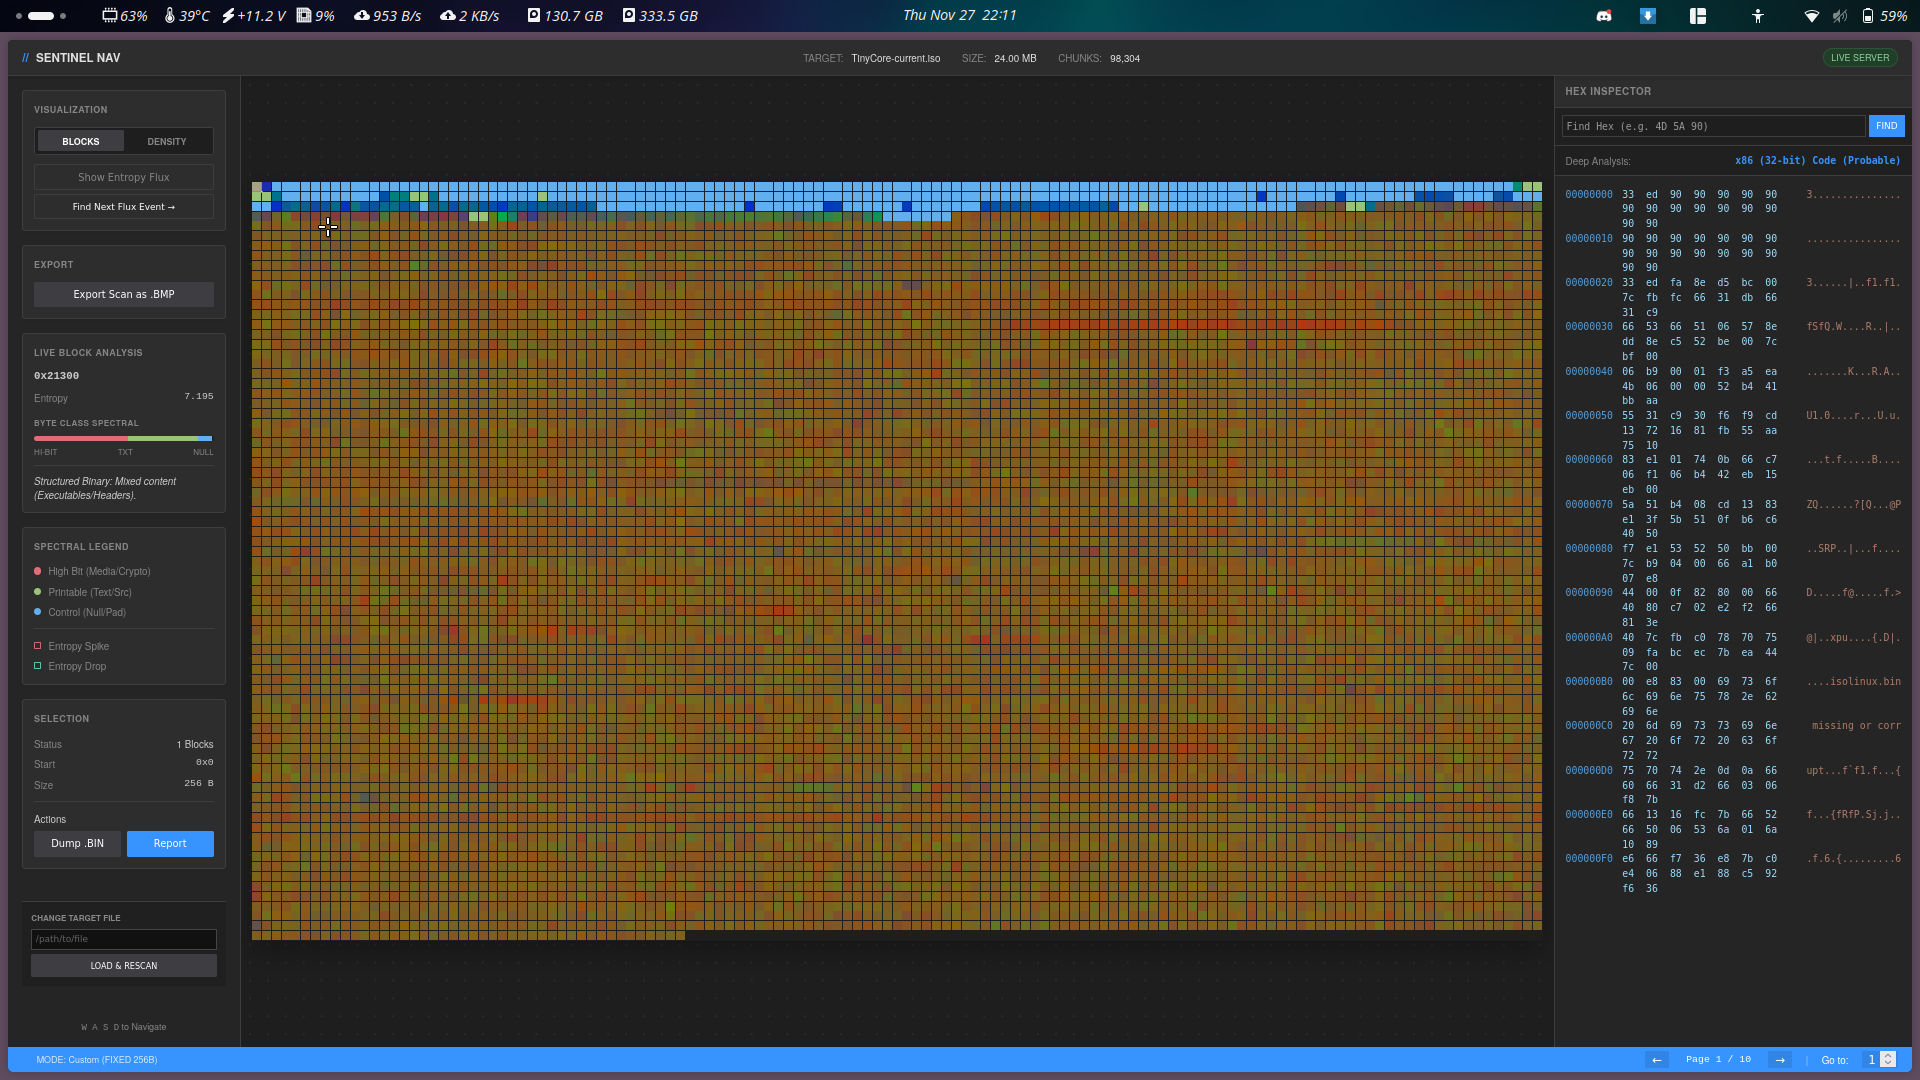 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.