

whapa
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
android-securitydata-recoverydigital-forensics+5
1.7k
b16f00t/whapaGraphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…

 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
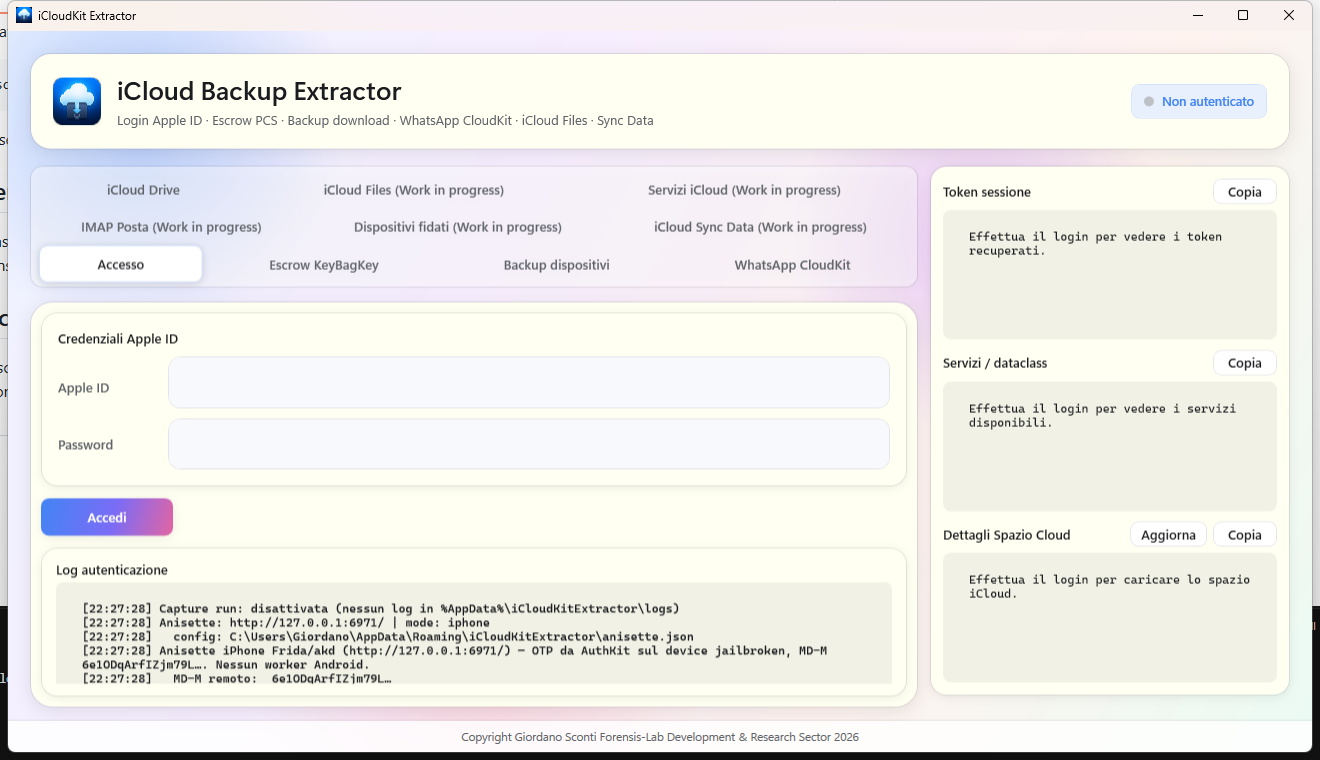 giordanosconti/icloudkitextractor
Experimental .NET/WPF forensic toolkit for iCloud auth, CloudKit/MMCS backup download, and Octagon/PCS recovery (ADP, Recovery Key, Lockdown Mode).…
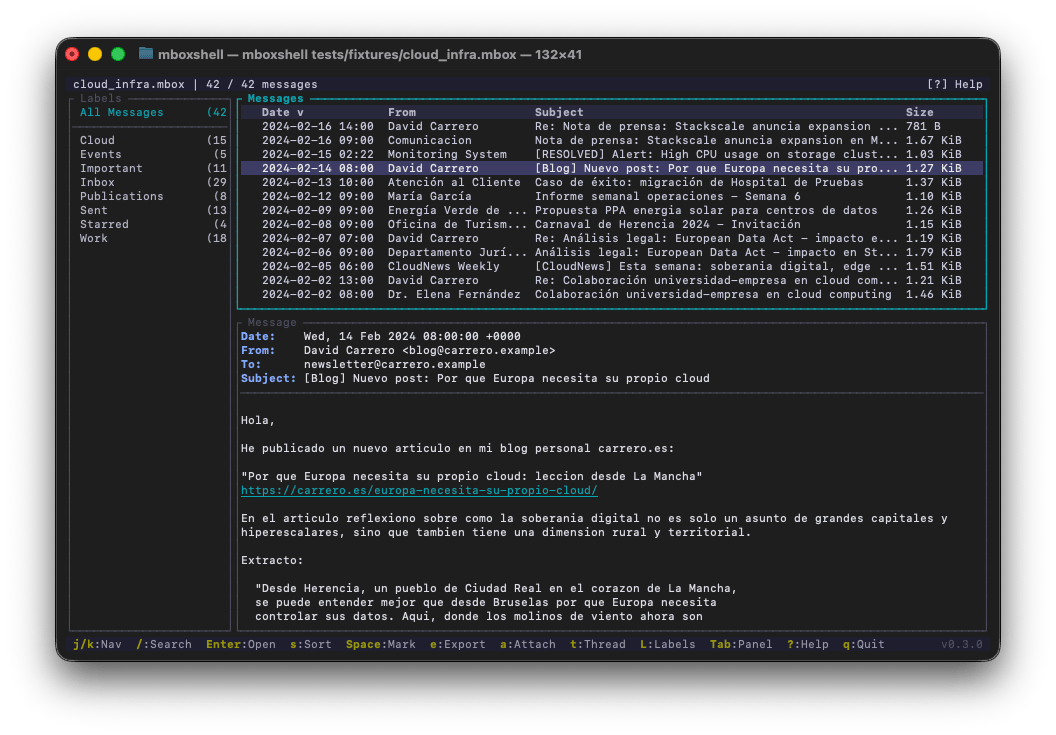 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
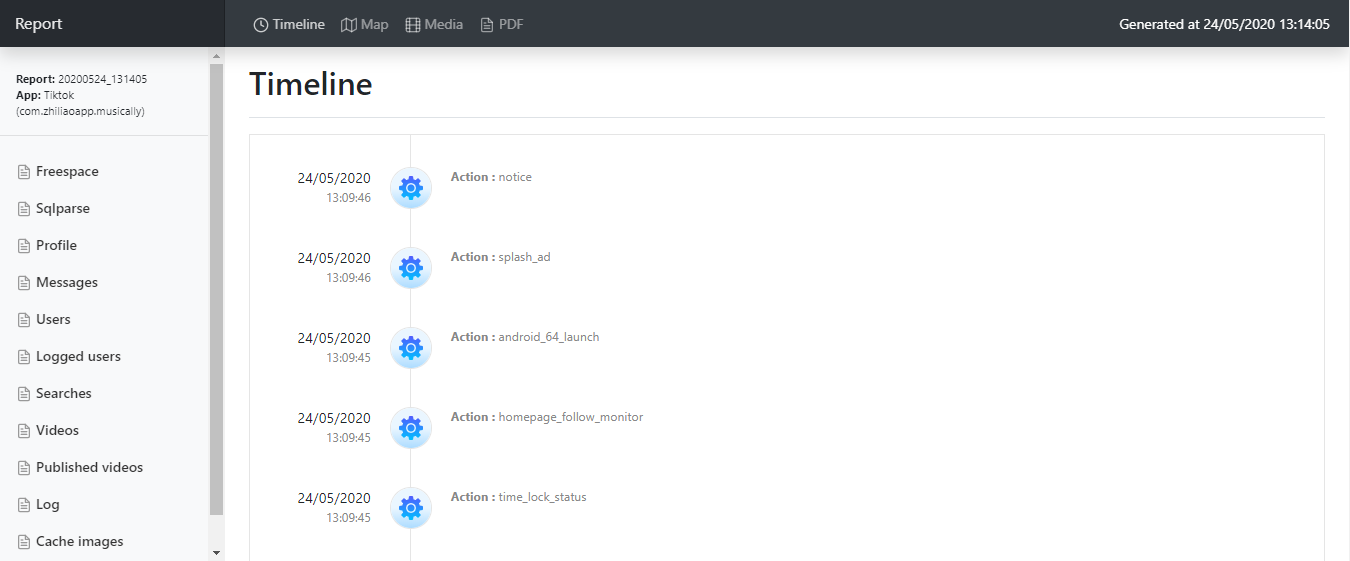 labcif/fama
Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser
 kvasirsecurity/kvasir
Kvasir: Penetration Test Data Management
 juanceresa/sift-kg
Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…
 packetlss/android-locdump
android location service cache dumper
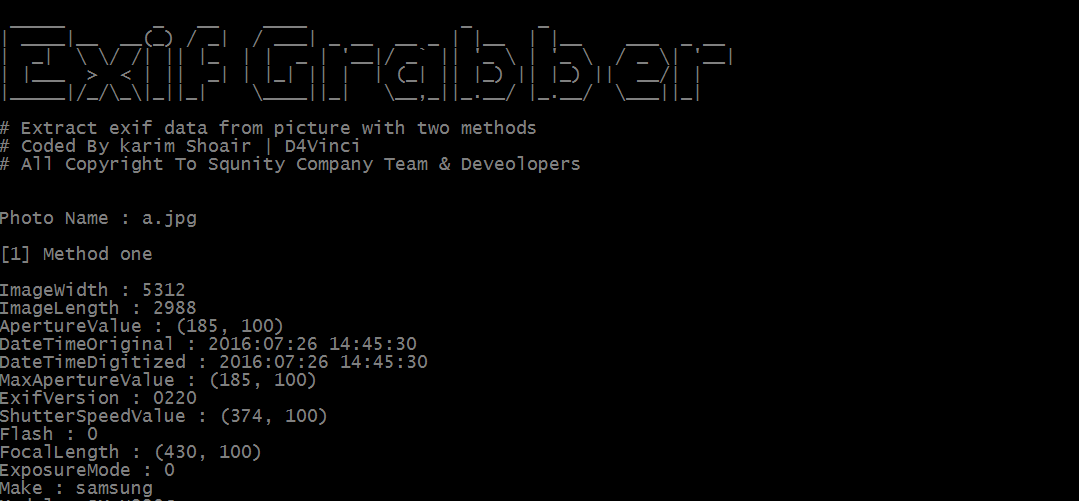 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
 radkawar/aws-firmware-dump
Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…
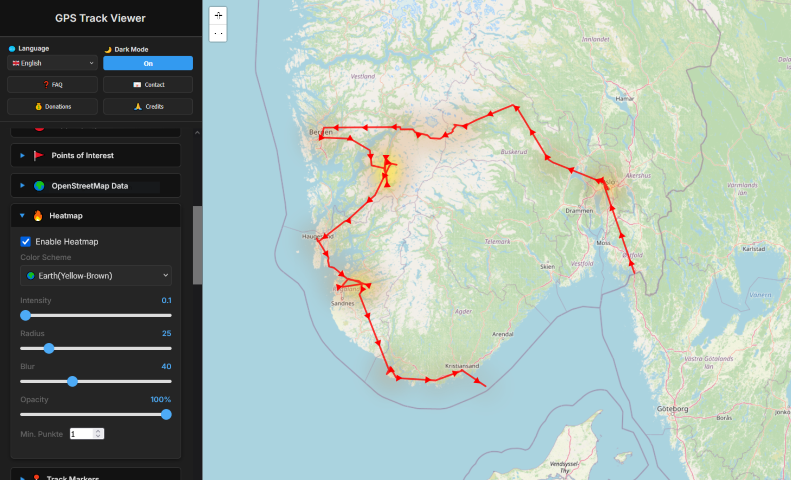 lukawe/localexifgeomap
A powerful, privacy-focused, browser-based tool to visualize and analyze GPS data from your photos. Simply drag and drop images to generate…
 nccgroup/zipdefrag
Presented at Recon Montreal 2018
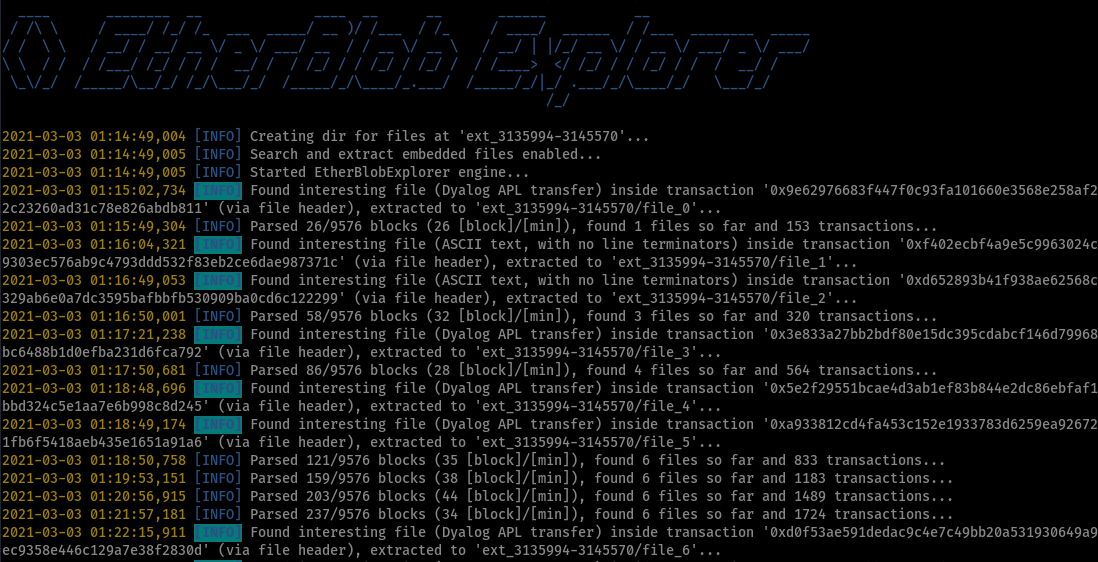 litneet64/etherblob-explorer
Search and extract blob files on the Ethereum Blockchain network