

mtkclient
 bkerler/mtkclient
Mediatek Flash and Repair Utility
android-securitydata-recoveryembedded-systems-security+5
bkerler/mtkclientMediatek Flash and Repair Utility
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

 qg5casz/walletool
Extracts cryptocurrency private keys and addresses from wallet.dat files for Bitcoin and Litecoin, enabling wallet recovery and forensic analysis.
 eugexo/security-baseline-ubuntu
Production-grade Security Baseline & Hardening Guide for Ubuntu 24.04/26.04 LTS. Kernel isolation, Emergency Panic Button, custom AppArmor/Firejail…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 sleuthkit/scalpel
File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 cgsecurity/testdisk
Recovers lost partitions and repairs boot sectors; carves 480+ file formats from damaged disks and filesystems for data recovery and forensic use.
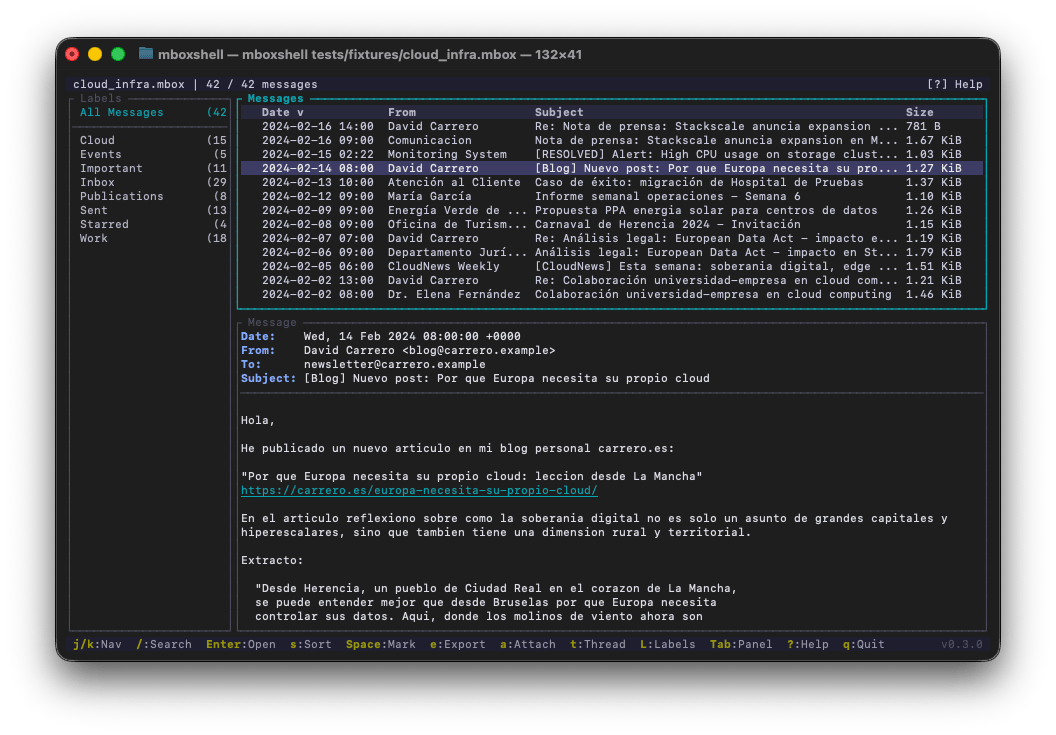 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
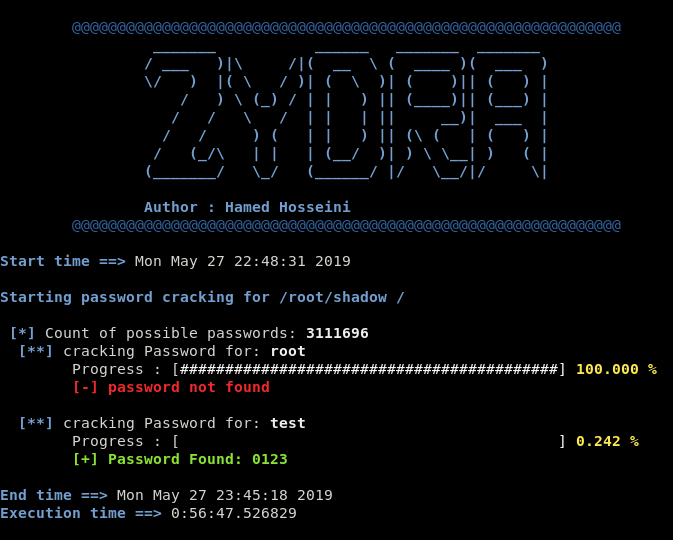 hameda2/zydra
Multi-threaded password recovery tool for RAR, ZIP, PDF, and Linux shadow files using dictionary and brute-force methods with configurable character…
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)