

mtkclient
 bkerler/mtkclient
Mediatek Flash and Repair Utility
android-securitydata-recoveryembedded-systems-security+5
1.2k
bkerler/mtkclientMediatek Flash and Repair Utility
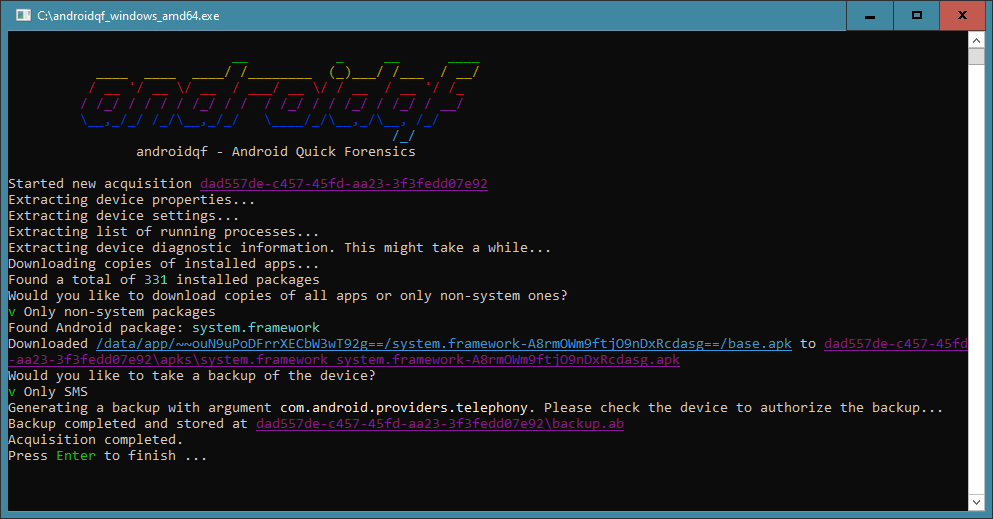 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 roxanne_ardary/nullify
Automated, policy-driven data retention and deletion system with immutable audit trails, RBAC/ABAC, multi-jurisdiction compliance, and AI/ML…
 onekey-sec/unblob
Extract files from any kind of container formats
 nelenkov/android-backup-extractor
Extract and repack Android ADB backups (ICS+). Supports encrypted archives, tar conversion, and standard I/O for forensic analysis or data recovery.
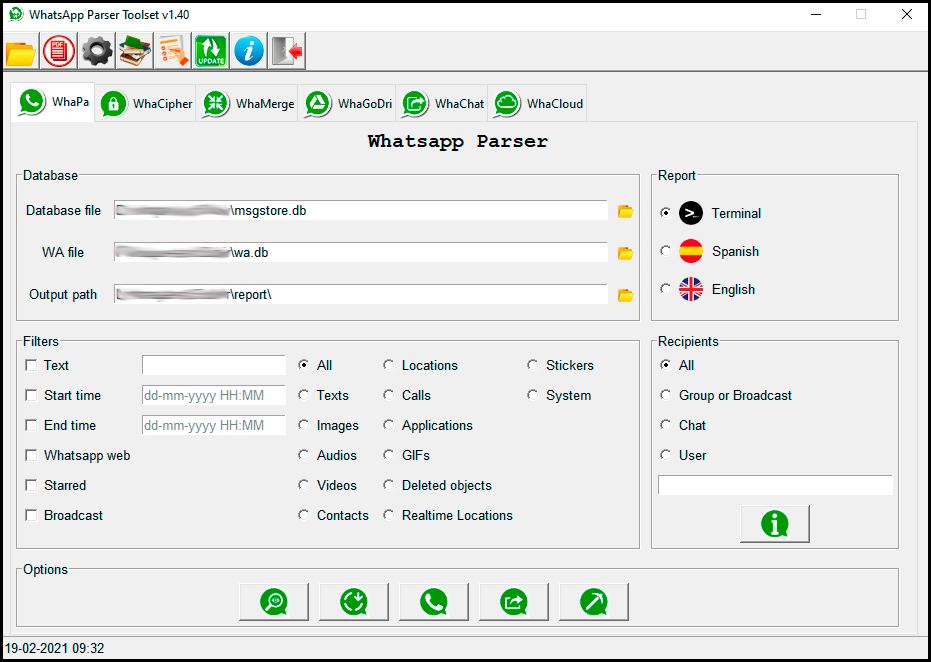 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 fmd-foss/fmd-android
Find your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…

 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 libyal/libqcow
Library and tools to access the QEMU Copy-On-Write (QCOW) image format
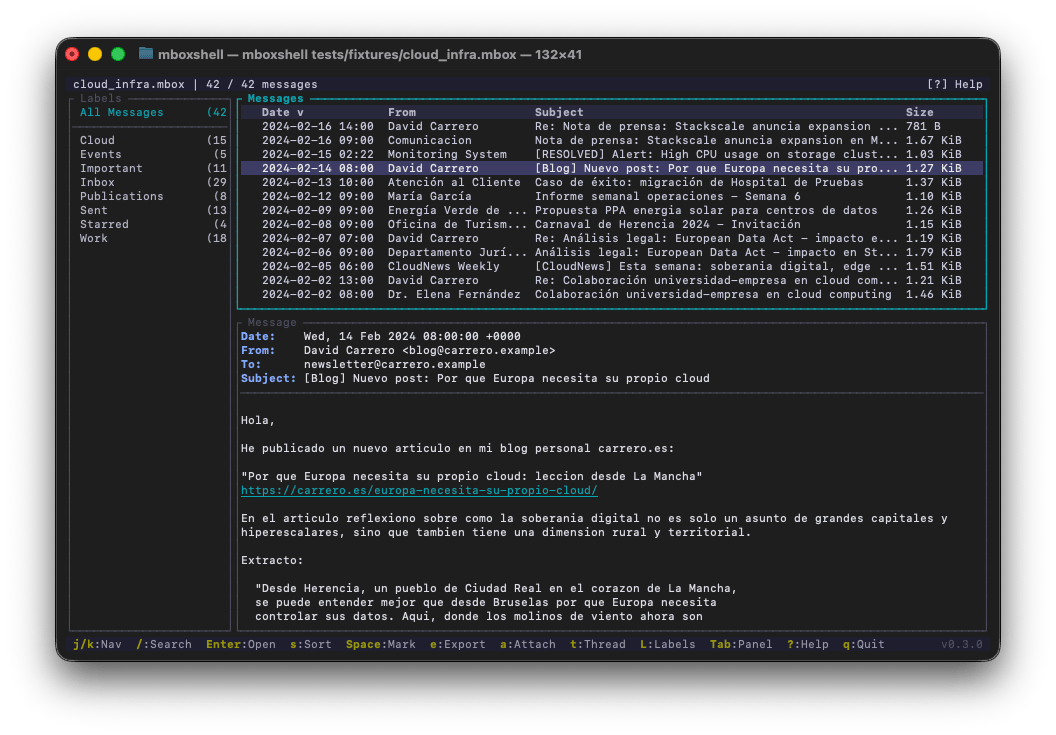 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
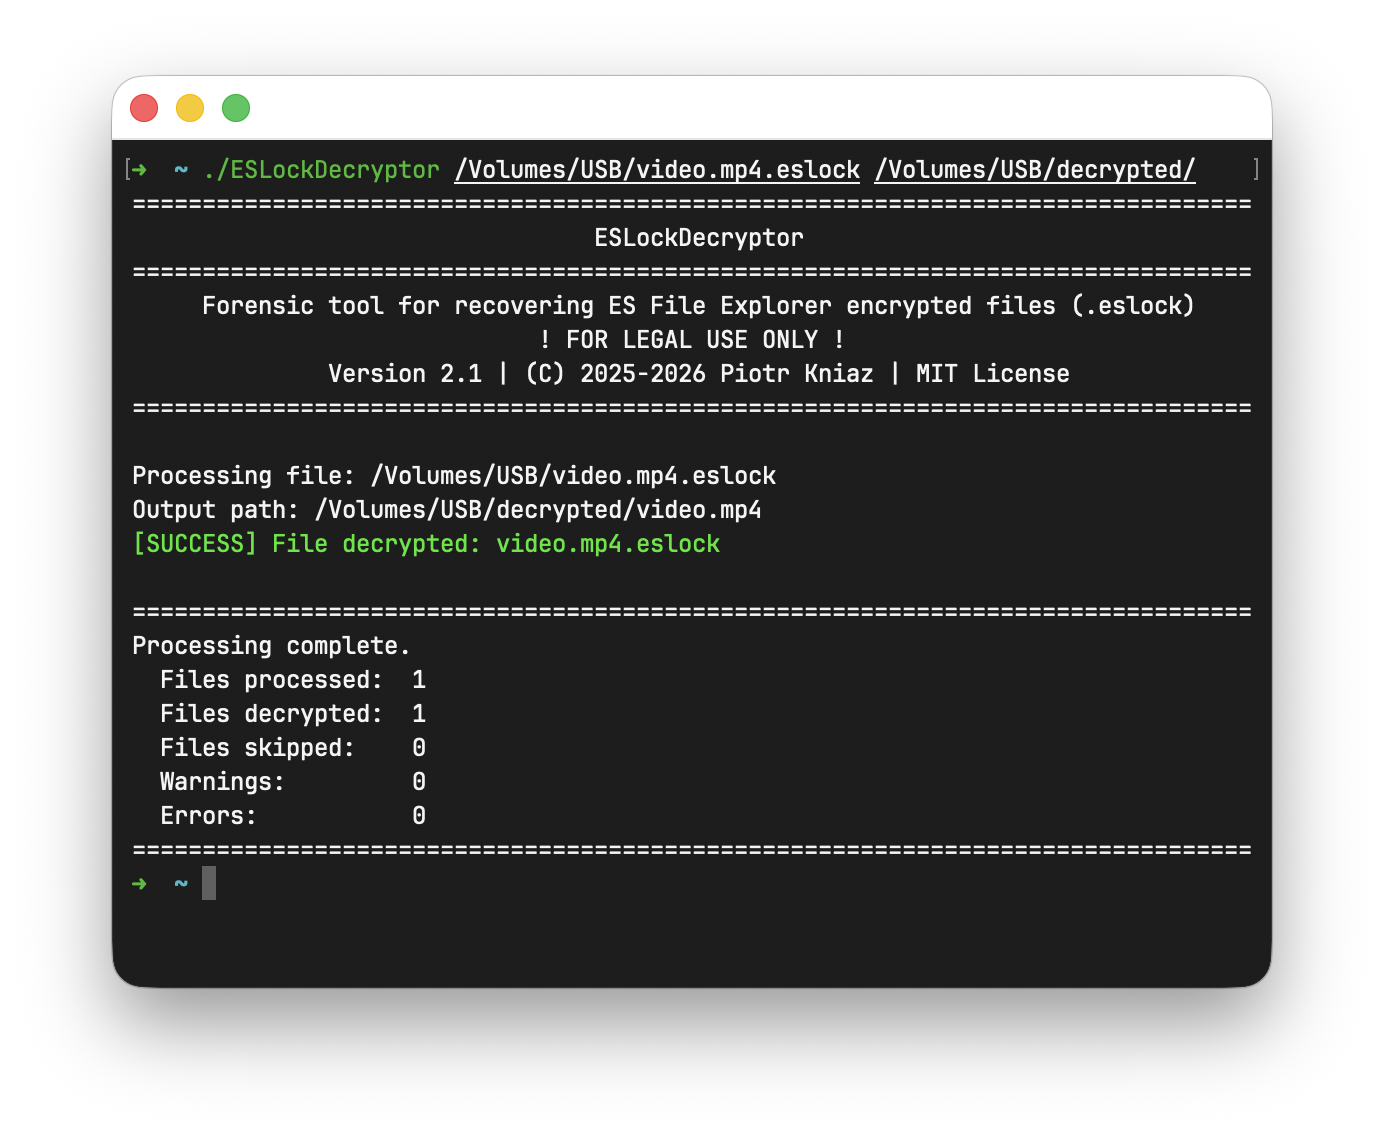 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)

 labcif/fama
Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser
 nowsecure/android-forensics
Open source Android Forensics app and framework
 libyal/libvmdk
Library and tools to access the VMware Virtual Disk (VMDK) format
 ustayready/physical-analyzer-scripts
Cellebrite Physical Analyzer python scripts to aid analysts with extended functionality
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…