
CVE-2024-12849-Poc
 nxploited/cve-2024-12849-poc
Exploit for CVE-2024-12849, an arbitrary file read vulnerability in WordPress Error Log Viewer plugin. Downloads sensitive files via unauthenticated…
data-exfiltrationexploitationpenetration-testing+2
nxploited/cve-2024-12849-pocExploit for CVE-2024-12849, an arbitrary file read vulnerability in WordPress Error Log Viewer plugin. Downloads sensitive files via unauthenticated…
 nxploited/cve-2024-7135
Proof-of-concept exploit for authenticated arbitrary file read via directory traversal in WordPress Tainacan plugin (CVE-2024-7135).
 advancedhacker101/android-c-sharp-rat-server
This is a plugin for the c# R.A.T server providing extension to android based phone systems
 shoucheng3/apache__nifi_cve-2022-33140_1-16-22
Automated data flow processing and distribution system with secure configuration, provenance tracking, and extensible plugin architecture for…
 gryfman/dlpwn
Red Team tool for covert file exfiltration via Bluetooth audio transmission, encoding binary data into FLAC signals to bypass EDR, XDR, and DLP…
 randomrobbiebf/learning-management-system
Masteriyo - LMS for WordPress <= 1.6.7 - Sensitive Information Exposure
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 thestingr/cve-2024-36991-tool
This binary POC automates the exploitation of CVE-2024-36991 by sending crafted curl requests to a vulnerable Splunk instance. It retrieves sensitive…
 d0n601/cve-2025-12585
MxChat – AI Chatbot for WordPress <= 2.5.1 - Unauthenticated Information Exposure
 error-inside/cve-2025-10897
WooCommerce Designer Pro <= 1.9.28 - Unauthenticated Arbitrary File Read
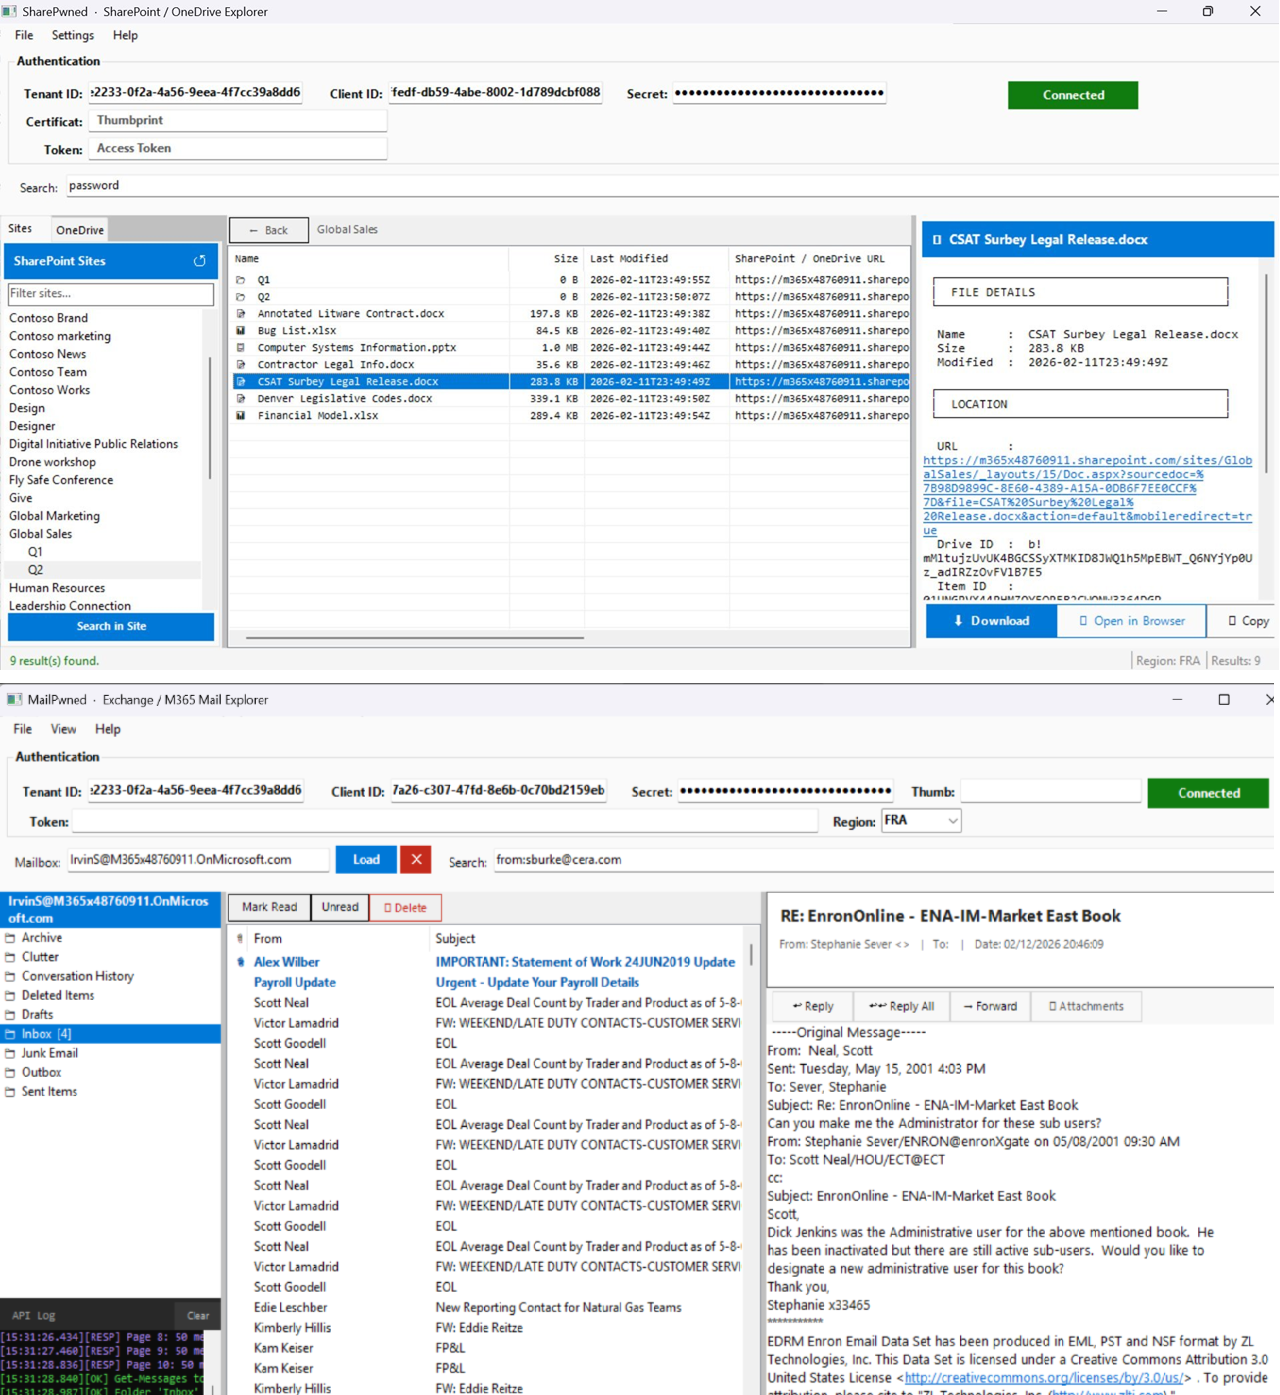 otterhacker/m365pwned
Two WinForms GUI tools for enumerating, searching, and exfiltrating data from M365 environments using application-level OAuth tokens
 nxploited/cve-2025-7401
Premium Age Verification / Restriction for WordPress <= 3.0.2 - Unauthenticated Arbitrary File Read and Write
 shell-company/qrexfil
This tool is a command line utility that allows you to convert any binary file into a QRcode movie. The data can then be reassembled visually…
 mbadanoiu/mal-014
MAL-014: Authenticated Arbitrary File Read in VMware vCenter Server
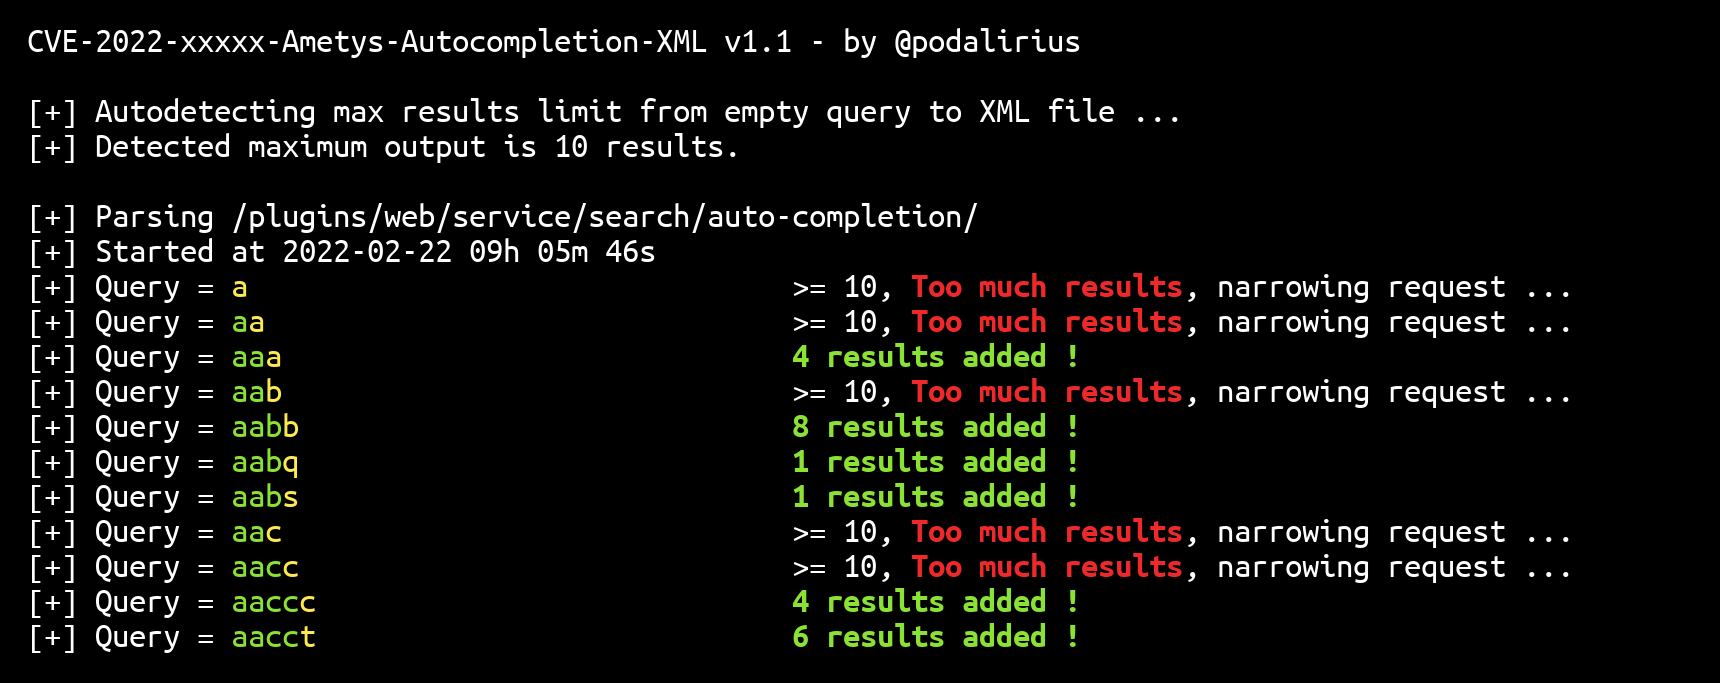 p0dalirius/cve-2022-26159-ametys-autocompletion-xml
A python exploit to automatically dump all the data stored by the auto-completion plugin of Ametys CMS to a local sqlite database file.
 luth1er/cve-2017-18345-com_joomanager-arbitrary-file-download
The Joomanager component through 2.0.0 for Joomla! has an Arbitrary File Download issue, resulting in exposing the Credentials of the DataBase.
 jnschaeffer/cve-2022-44268-detector
Detect images that likely exploit CVE-2022-44268