Langflow-cve-2026-33017-exploit

CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…

CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…

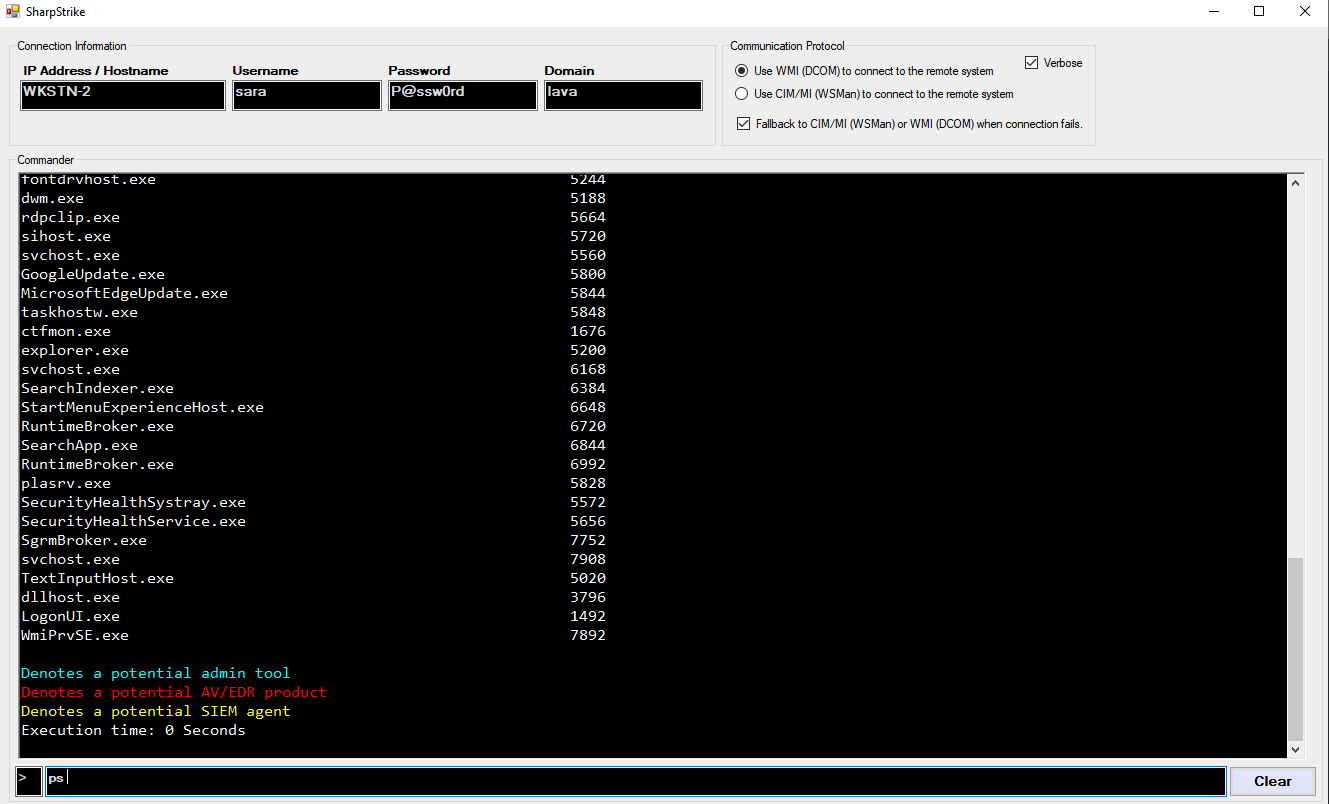
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.

React2Shell Exploitation Tool (CVE-2025-55182)

Exploit tool for CVE-2025-14847, a MongoDB memory disclosure vulnerability, enabling multi-threaded extraction of sensitive data and secrets from…

Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…

a critical memory disclosure vulnerability in MongoDB's zlib compression handling. This tool allows security researchers to extract sensitive data…

Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)

Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…

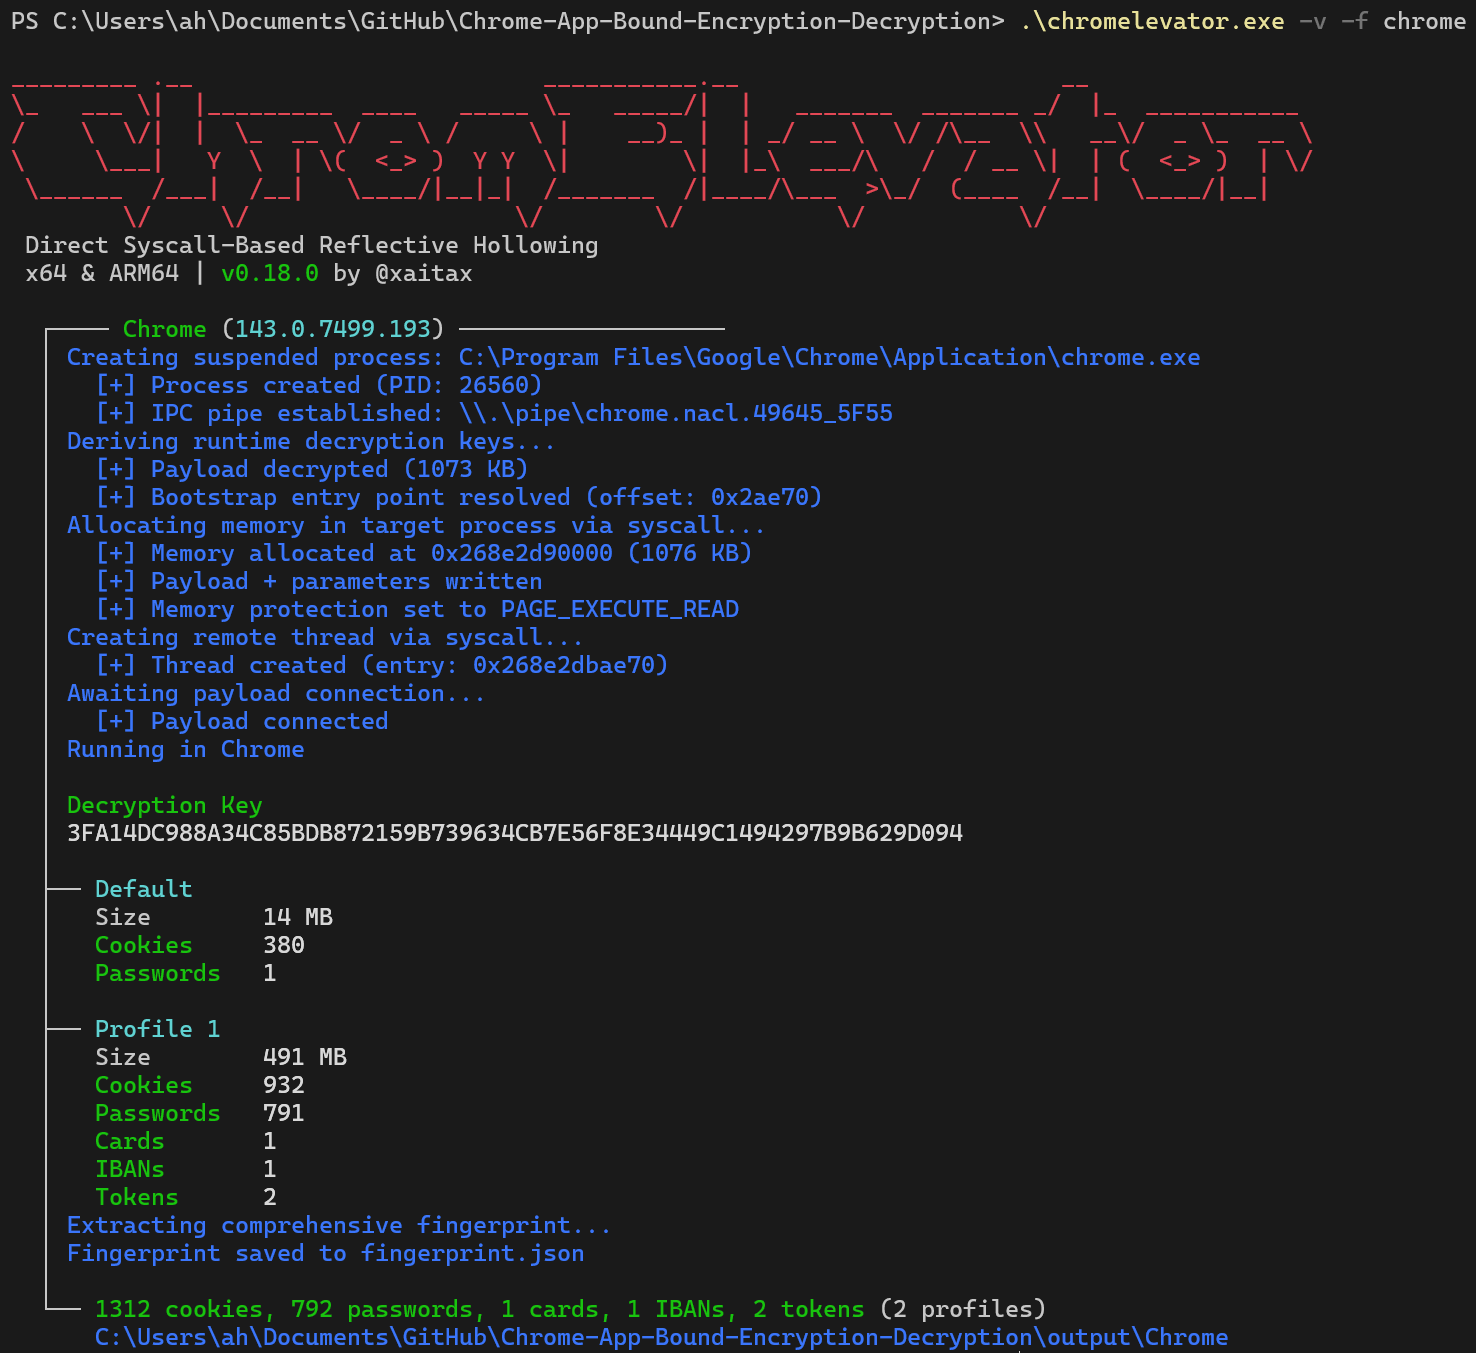
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…

scavenger : is a multi-threaded post-exploitation scanning tool for scavenging systems, finding most frequently used files and folders as well as…

Bella is a pure python post-exploitation data mining tool & remote administration tool for macOS. 🍎💻

Tool for helping in the exploitation of path traversal vulnerabilities in Java web applications

SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit

CVE-2025-48932 - Unauthenticated SQL injection exploit for Invision Community ≤ 4.7.20. Fully automated exploitation with database enumeration,…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

👁️ (s)AINT is a Spyware Generator for Windows systems written in Java. [Discontinued]

Python exploit for CVE-2020-17518, allowing arbitrary file write via Apache Flink REST API. Supports single target and batch scanning from a file.

CVE-2022-41678: Dangerous MBeans Accessible via Jolokia API in Apache ActiveMQ