POC-ES-File-Explorer-CVE-2019-6447

Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.

Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.

This is a SMS And Call Bomber For Linux And Termux

A Telegram Mass Surveillance Bot in Python

This is a plugin for the c# R.A.T server providing extension to android based phone systems

A command-line utility to exploit Android Zygote injection (CVE-2024-31317)

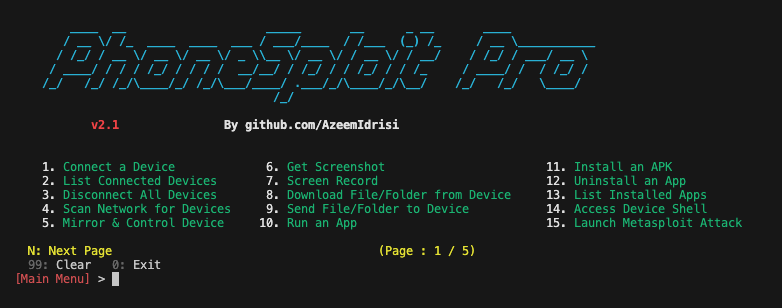
An all-in-one hacking tool to remotely take over Android devices.

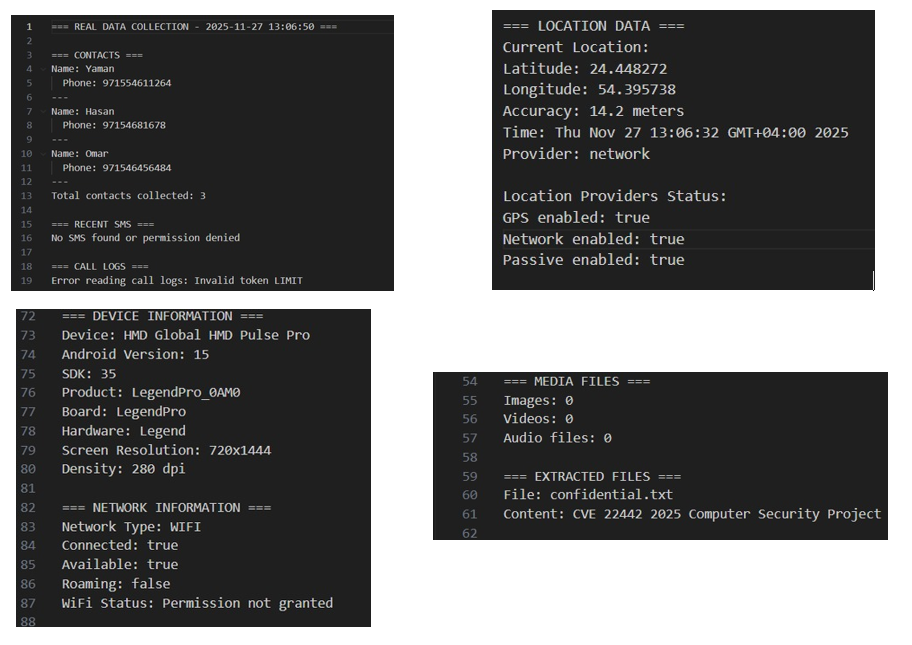
Controlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.

A Remote Administration Tool for Android devices

Exfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely

Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…

CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…

Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…

This is a toolkit that uses CVE-2024-31317 to extract private app data via ADB or spawn a shell with an app's UID.

Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, exploiting WebKit (CVE-2025-24201) and Core Media (CVE-2025-24085) to achieve sandbox…

Proof-of-concept Python script demonstrating iOS file exfiltration via malicious symlink in device backup restoration, targeting the…

iOS Shortcut-based keylogger designed to capture keystrokes and exfiltrate data from compromised devices.

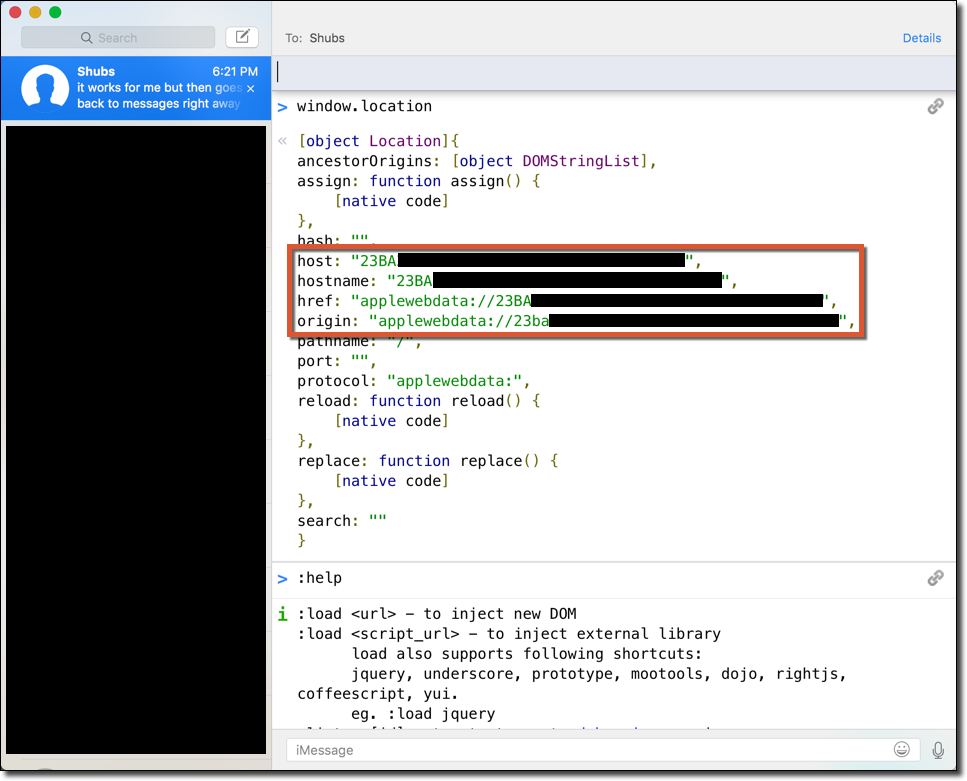
Extraction of iMessage Data via XSS

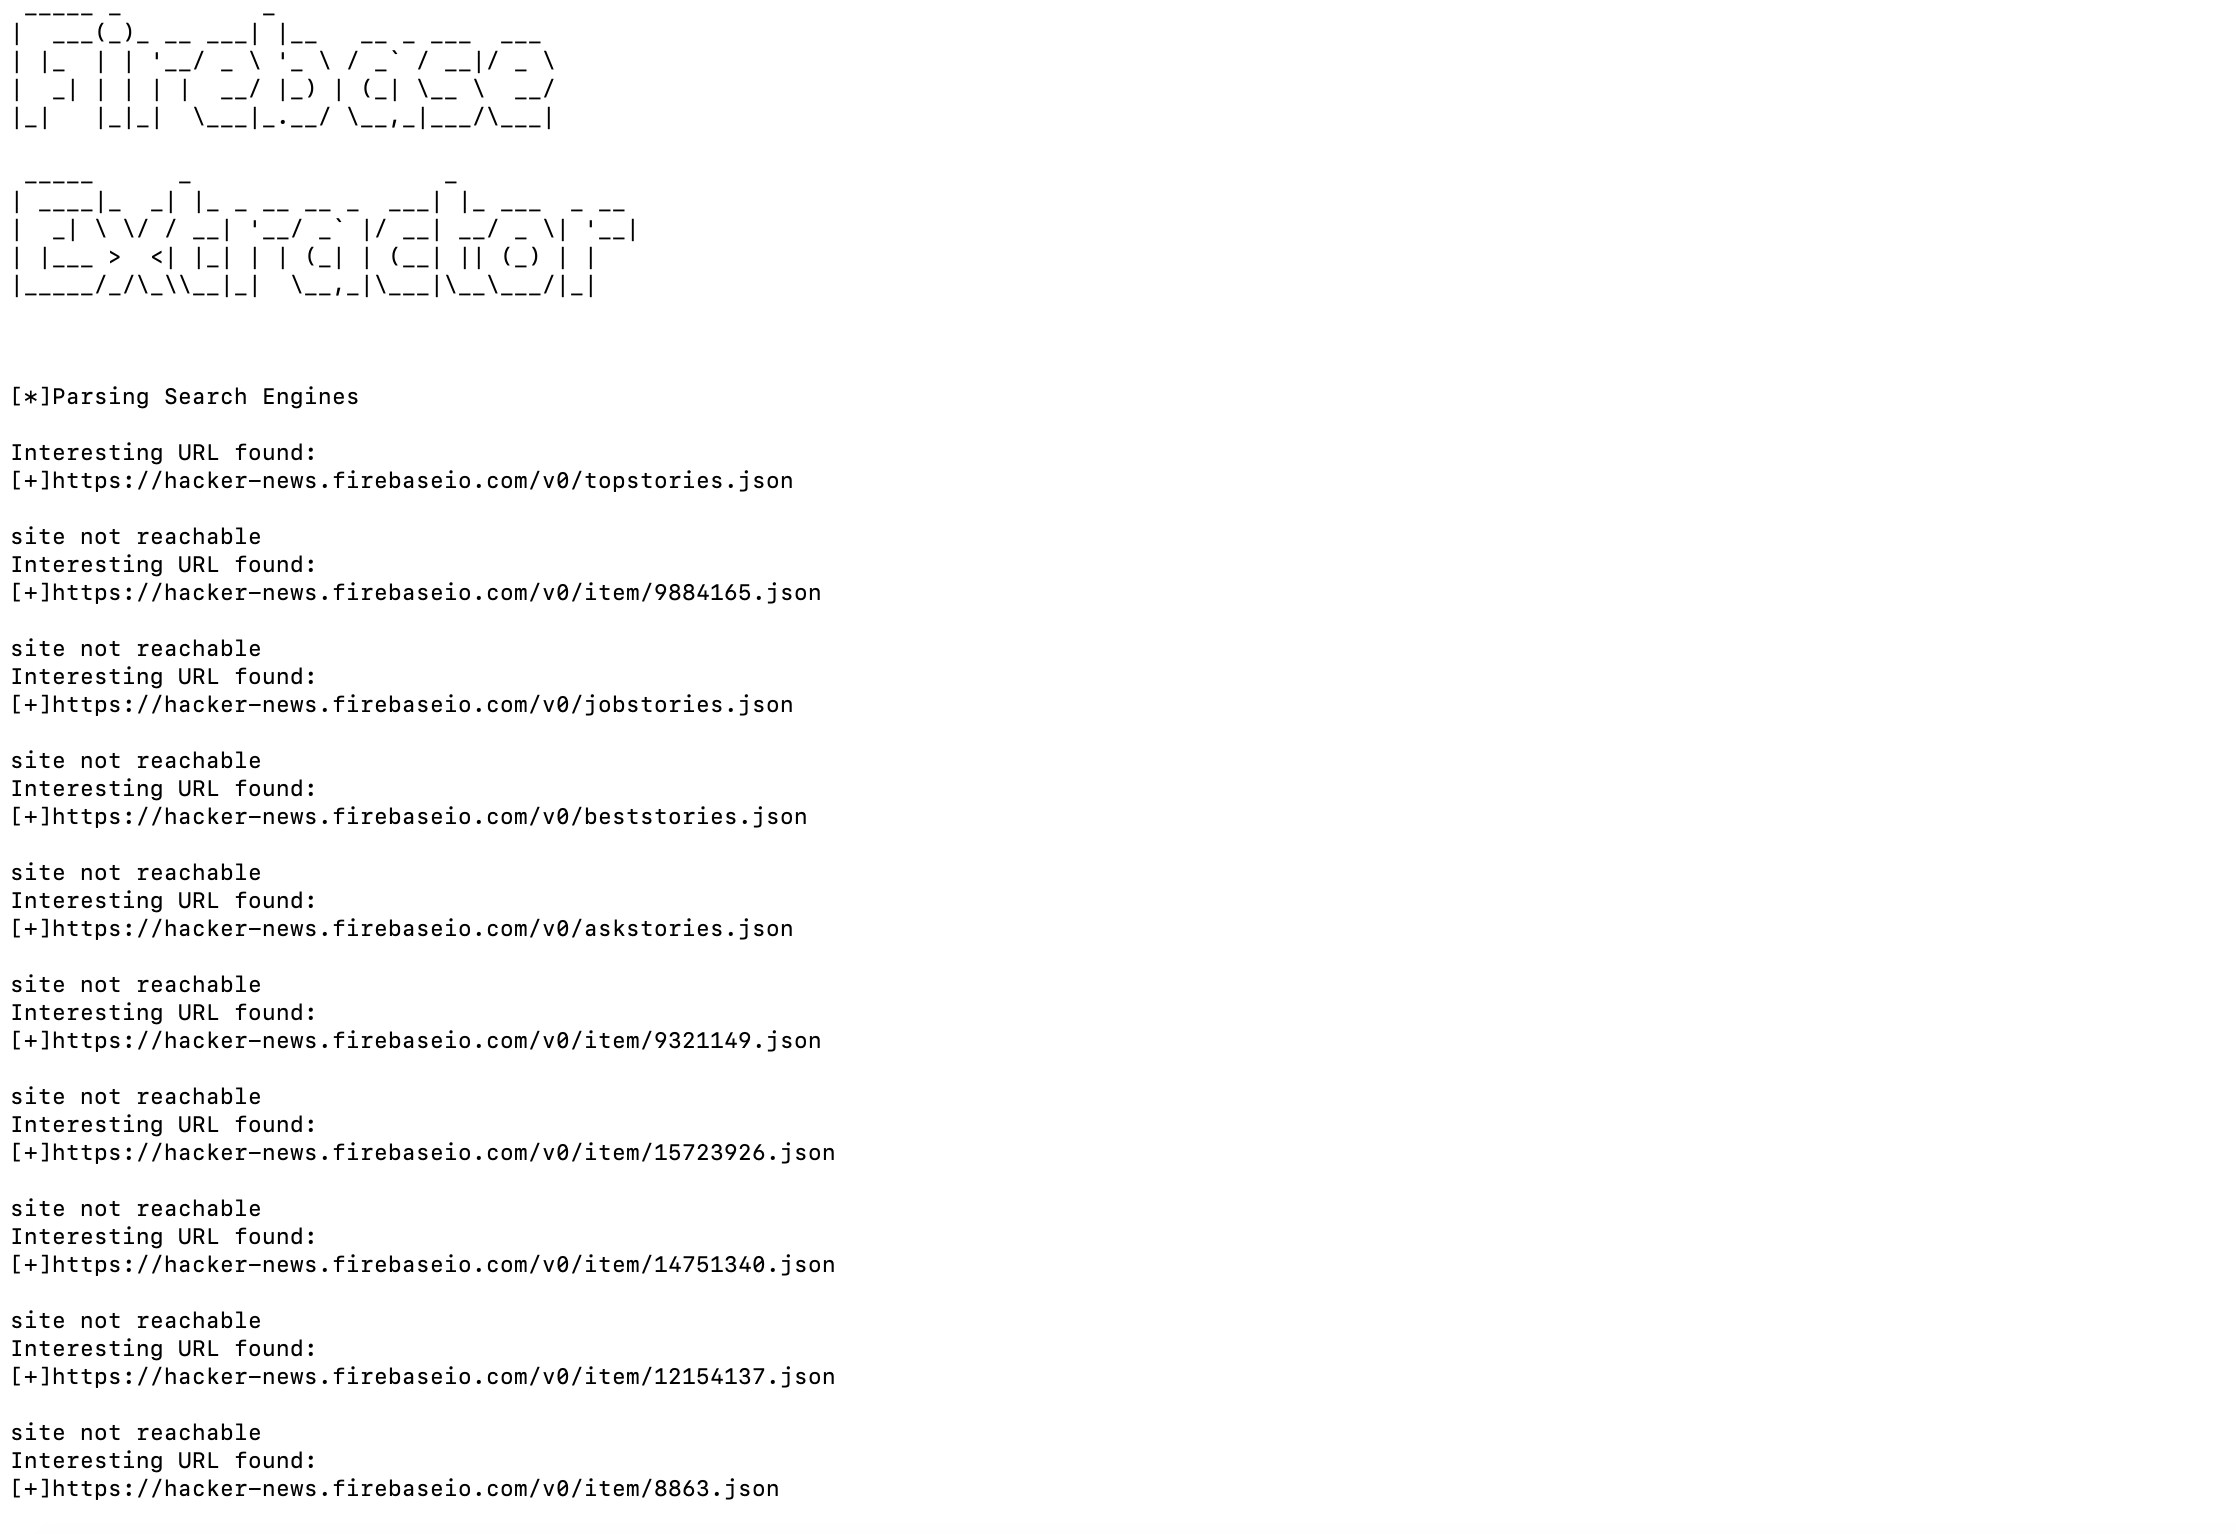
A tool written in python for scraping firebase data