
Active-Directory-Exploitation-Cheat-Sheet
 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
curated-resourcesdata-exfiltrationeducation+6
integration-it/active-directory-exploitation-cheat-sheetA cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 agwa/git-crypt
Transparent file encryption in git
 thalesgroup-cert/watcher
AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
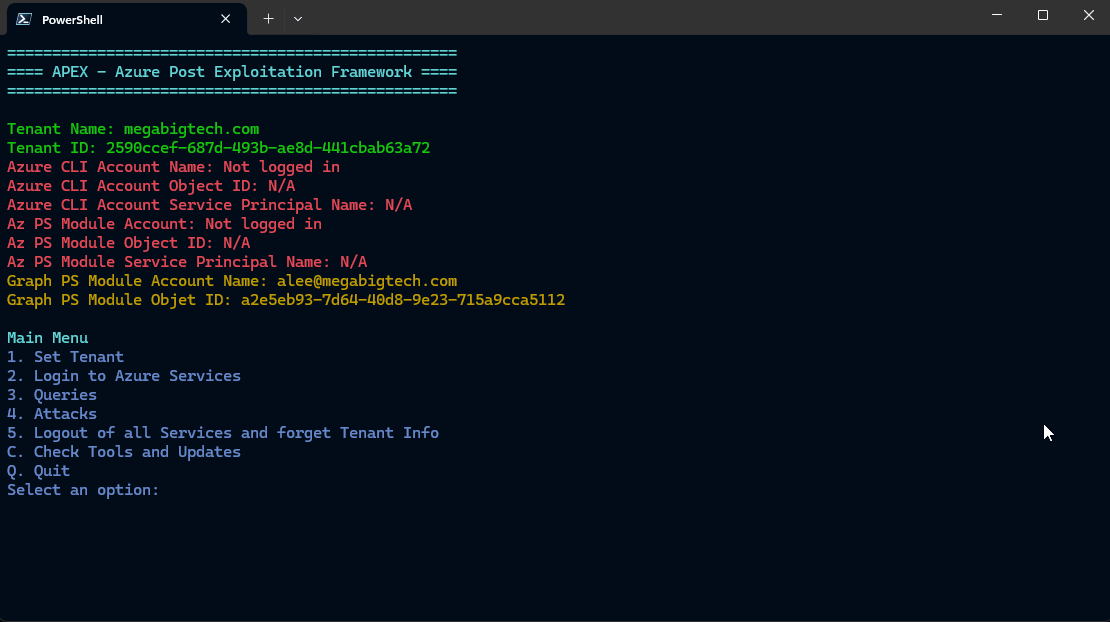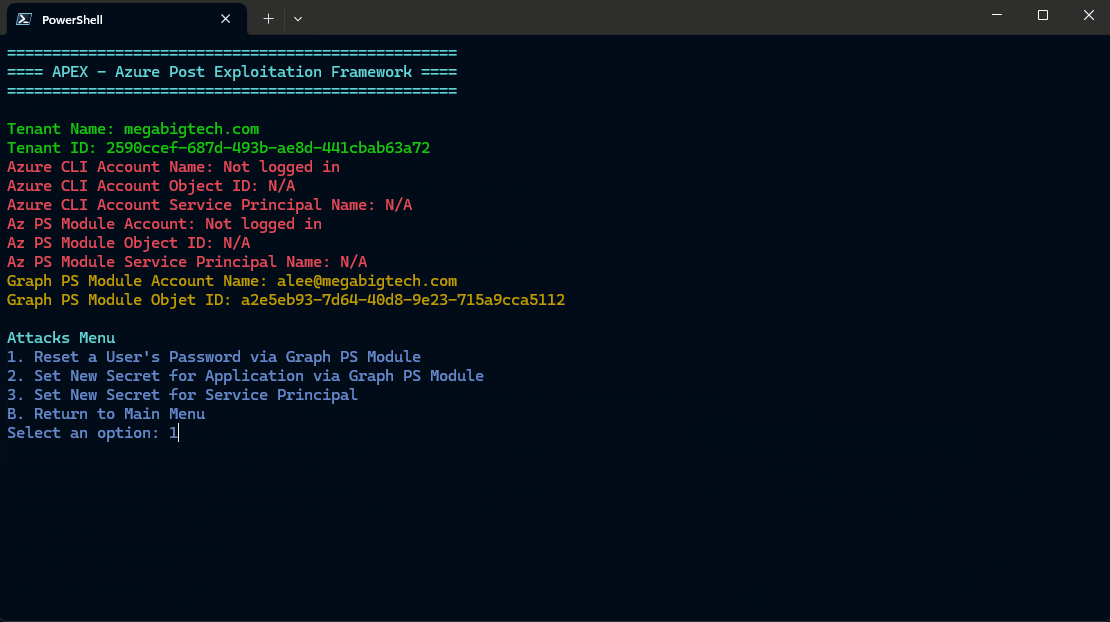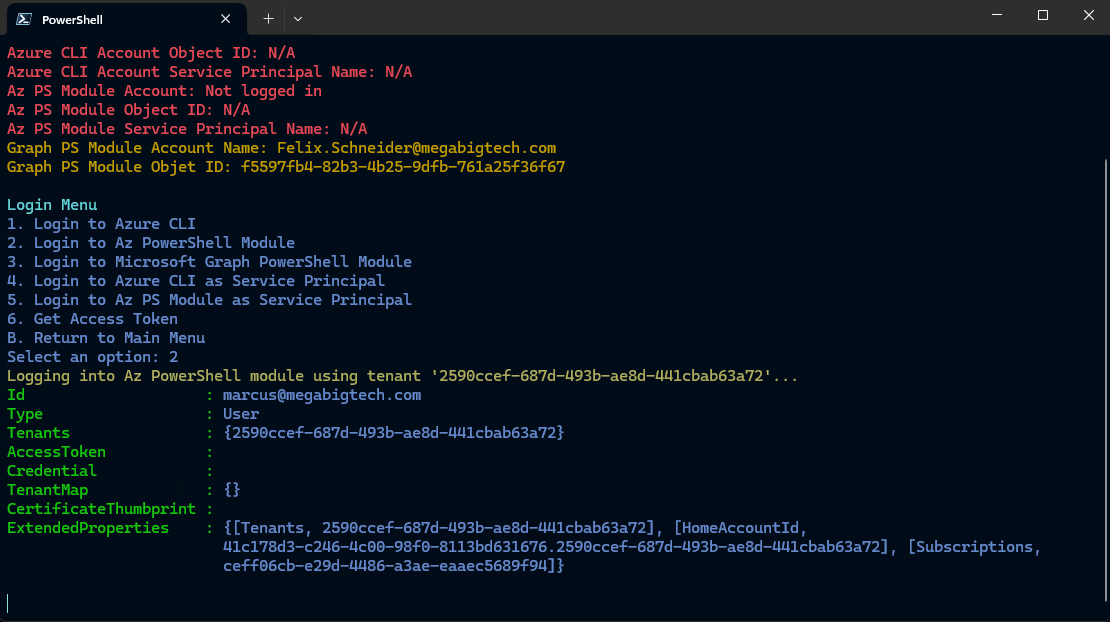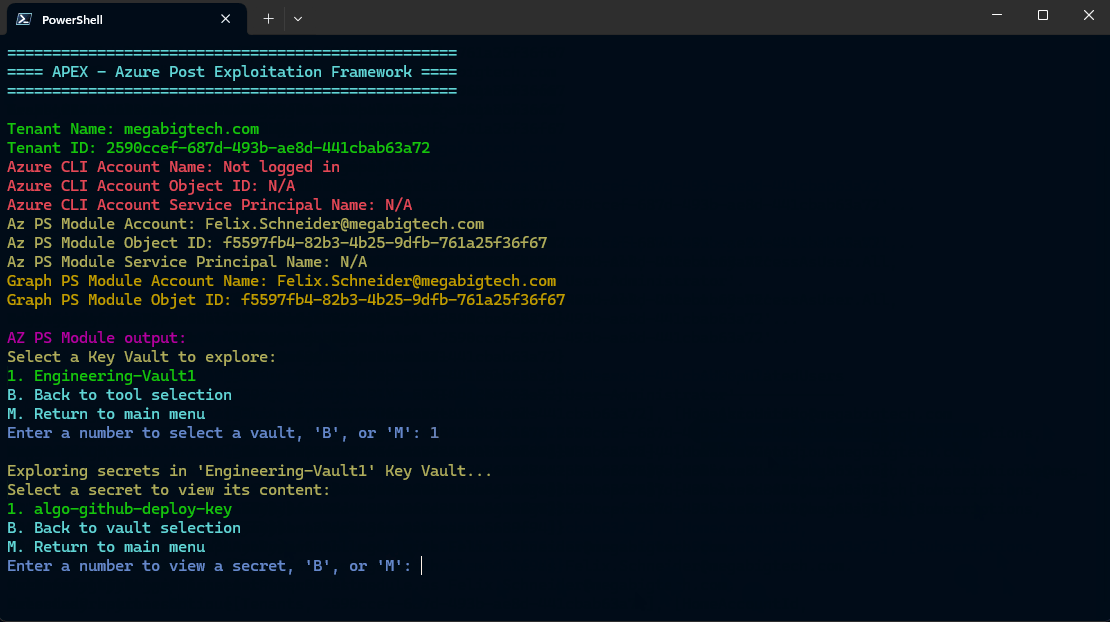 luemmelsec/apex
Azure Post Exploitation Framework
 nccgroup/onelogicalmyth_shell
A HTA shell to assist with breakout assessments.
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
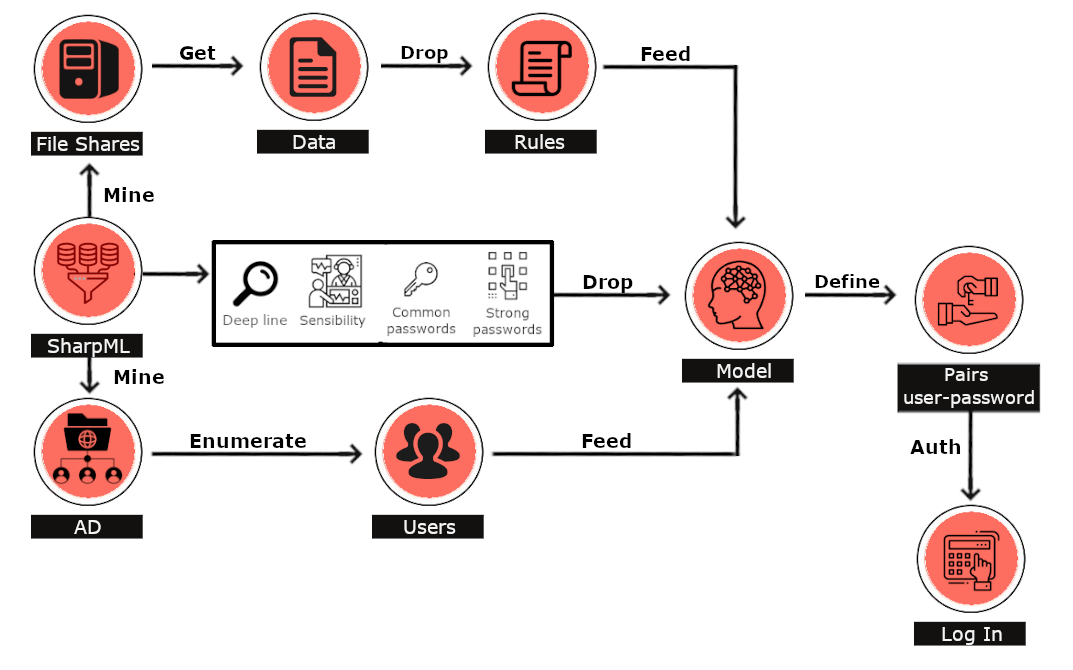 hunniccyber/sharpml
Machine Learning Network Share Password Hunting Toolkit
 6mile/gimmepatz
Personal Access Token (PAT) recon tool for bug bounty hunters, pentesters & red teams
 0ggp4r1s/osint-pattern-analyzer
Automated OSINT tool for phone number discovery, pattern detection, and cross-platform correlation.
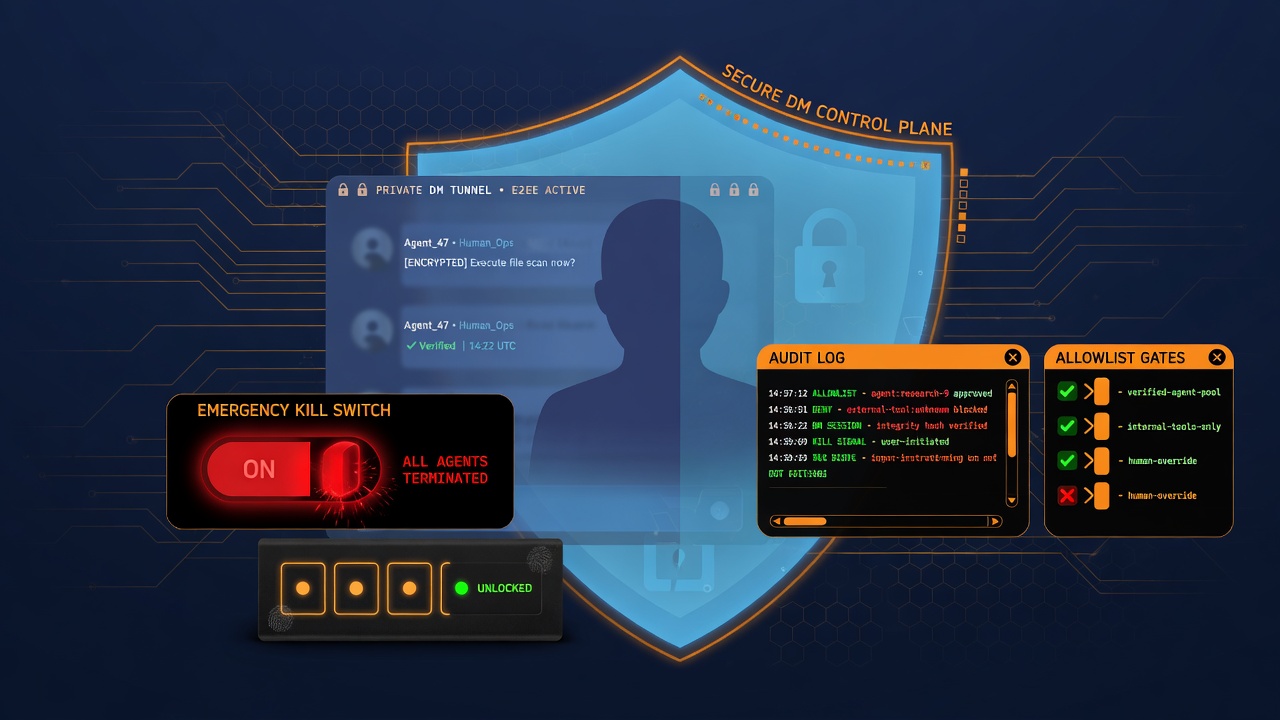
 wattocyber/agentic-dm-gateway
Security control plane for LLM agents: allowlists, owner kill switch, PIN sessions, rate limits, prompt-injection detection, and output scrubbing to…
 tea-on/cve-2021-29447-authenticated-xxe-wordpress-5.6-5.7
POC to exploit WordPress 5.6-5.7 (PHP 8+) Authenticated XXE Injection.
 gmh5225/jataayu
LLM-backed AI agent security — inbound injection detection + outbound privacy protection
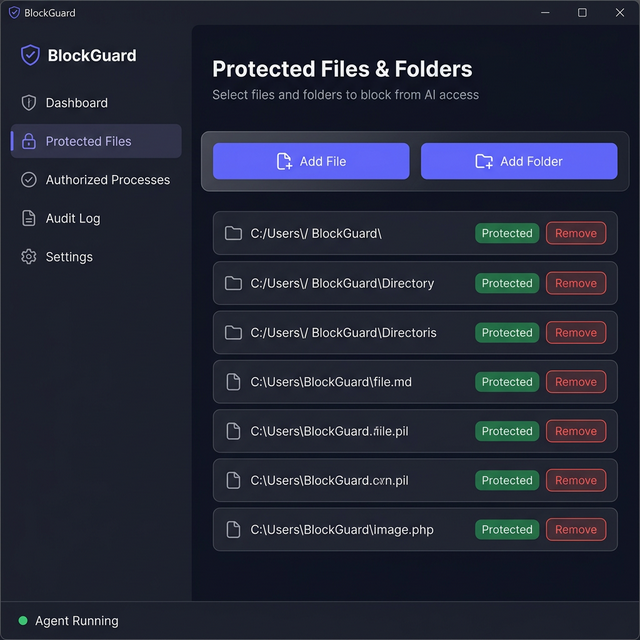 m2l33k/blockguard
BlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…
 antman1p/gdir-thief
Red Team tool for exfiltrating the target organization's Google People Directory that you have access to, via Google's API.
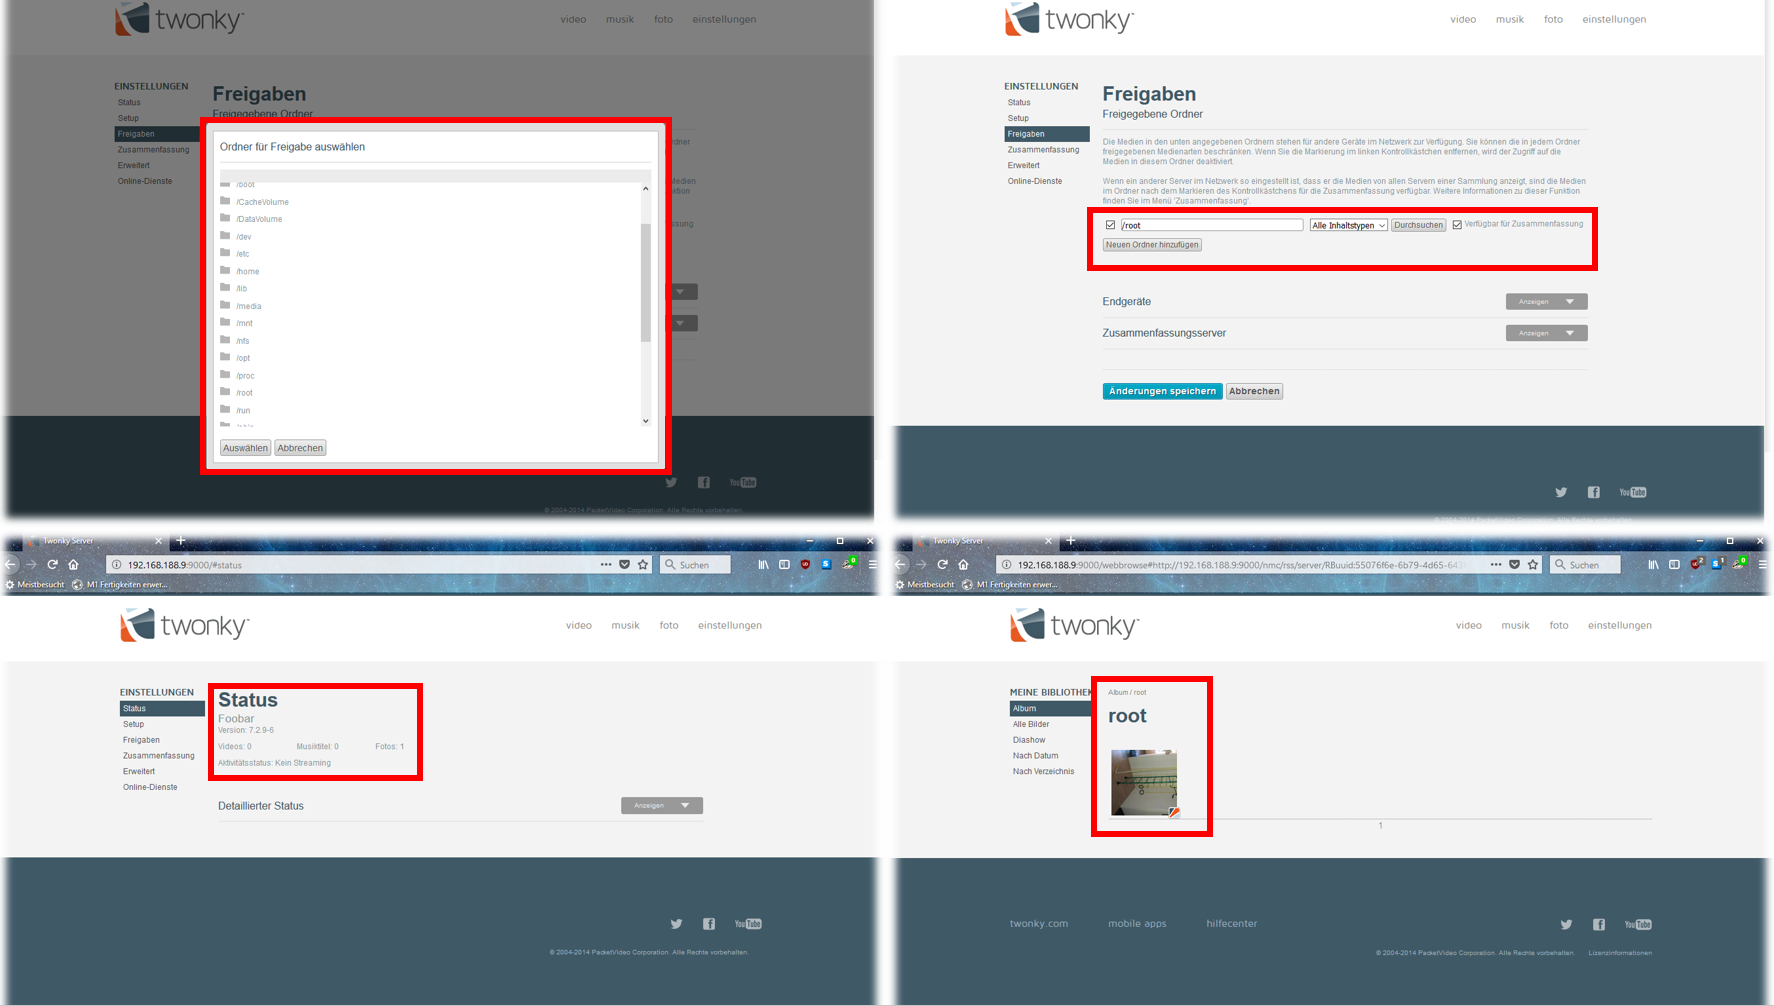 mechanico/sharingiscaring
TwonkyMedia Server 7.0.11-8.5 Directory Traversal CVE-2018-7171
 smarttfoxx/cve-2025-65321
Language Sloth Sloth Bot 1.0 is vulnerable to Directory Traversal in the gif() and png() functions. The functions build file paths using unsanitized…
 jfriedli/cve-2025-11973
Proof-of-concept exploit for CVE-2025-11973 demonstrating local file inclusion (LFI) in WordPress via file:// protocol, with automated exfiltration…