
File-Injector
 carlospuenteg/file-injector
File Injector is a script that allows you to store any file in an image using steganography
cryptographydata-exfiltrationencryption-decryption-tools+1
444
carlospuenteg/file-injectorFile Injector is a script that allows you to store any file in an image using steganography
 p0dalirius/cve-2021-31800-impacket-smb-server-arbitrary-file-read-write
A path traversal in smbserver.py allows an attacker to read/write arbitrary files on the server.
 3gstudent/ntfsdump
Use to copy a file from an NTFS partitioned volume by reading the raw volume and parsing the NTFS structures.
 dutchcoders/transfer.sh
Easy and fast file sharing from the command-line.
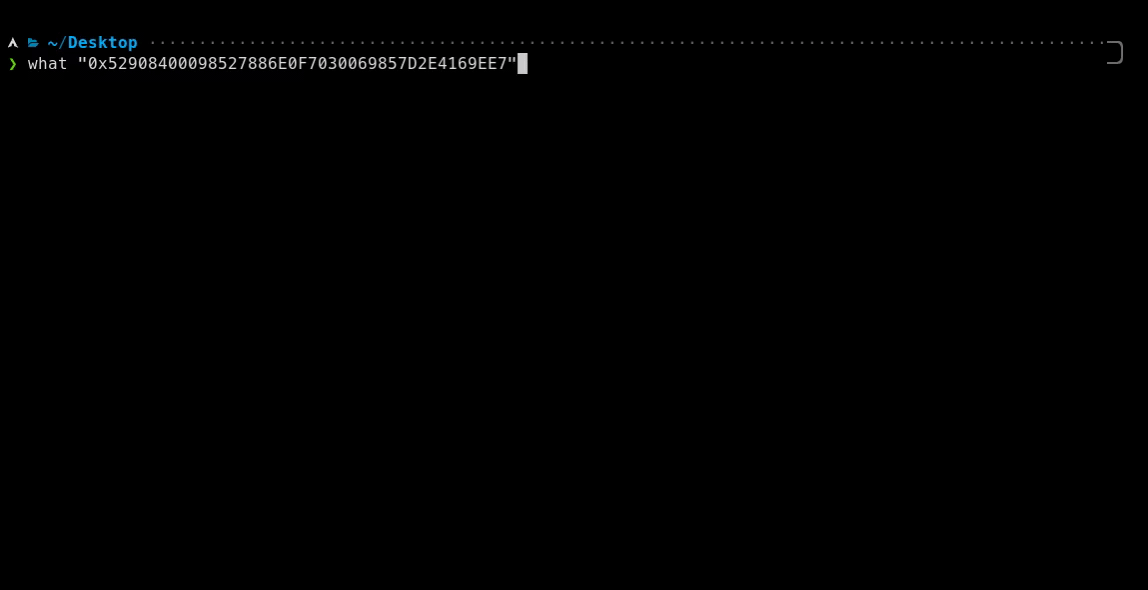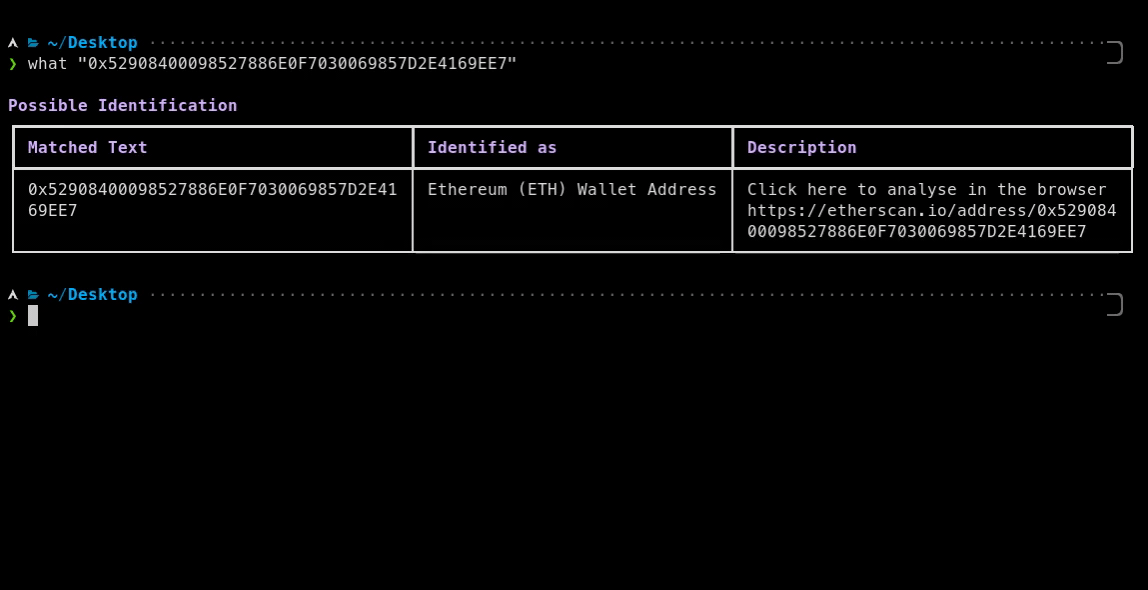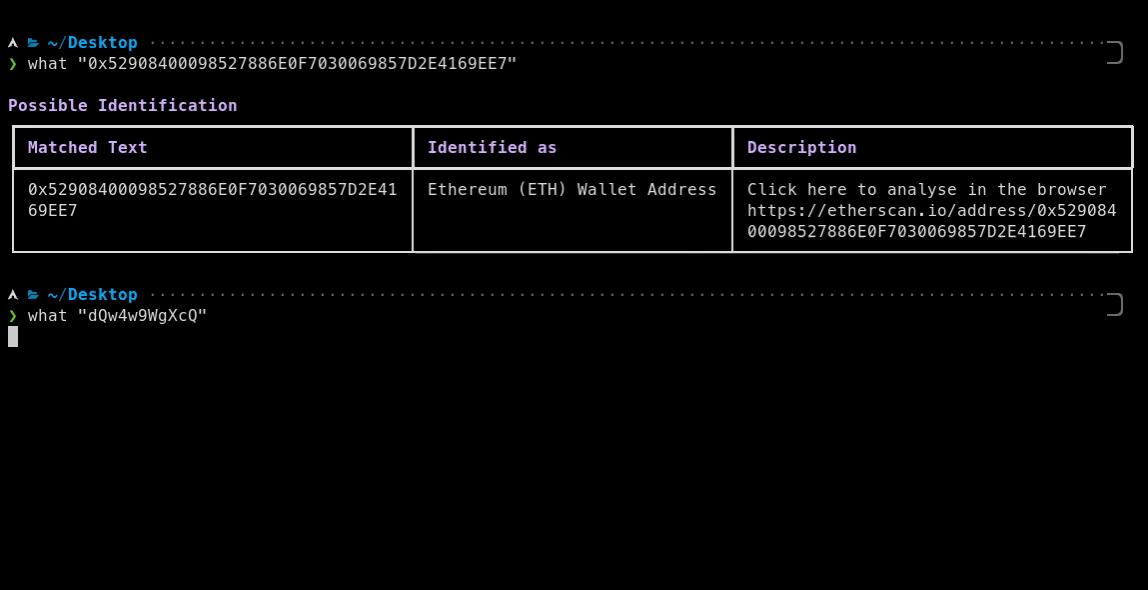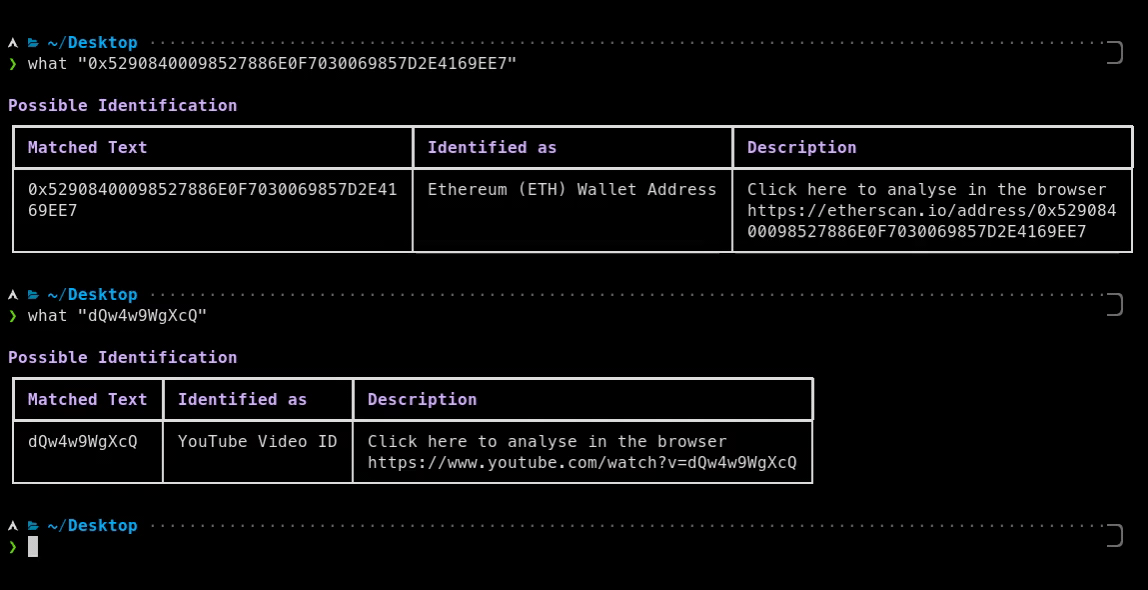 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
 agwa/git-crypt
Transparent file encryption in git
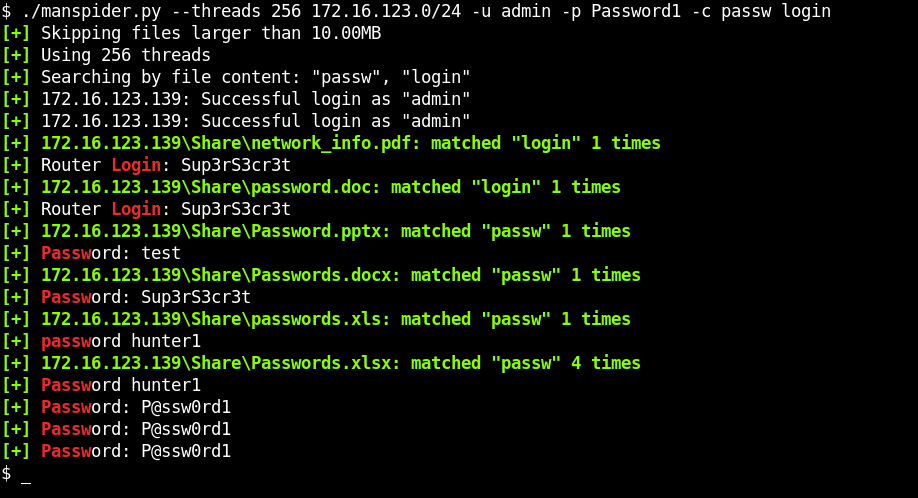 blacklanternsecurity/manspider
Spider entire networks for juicy files sitting on SMB shares. Search filenames or file content - regex supported!
 iagox86/dnscat2
Encrypted command-and-control tunnel over DNS protocol. Creates stealthy C&C channels for penetration testing, with file transfer, shell access, and…
 davidbuchanan314/tweetable-polyglot-png
Pack up to 3MB of data into a tweetable PNG polyglot file.
 ggerganov/wave-share
Serverless, peer-to-peer, local file sharing through sound
 fs0c131y/esfileexploreropenportvuln
ES File Explorer Open Port Vulnerability - CVE-2019-6447
 threatexpert/gonc
Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.
 jas502n/grafana-cve-2021-43798
Grafana Unauthorized arbitrary file reading vulnerability
 mrd0x/evilselenium
Weaponizes Selenium to automate credential theft, cookie dumping, email exfiltration, and file extraction from Chromium browsers for red team…
 maldev-academy/embedpayloadinpng
Embed a payload inside a PNG file
 shell-company/qrexfil
This tool is a command line utility that allows you to convert any binary file into a QRcode movie. The data can then be reassembled visually…
 fin3ss3g0d/secretsdump.py
Enhanced version of secretsdump.py from Impacket. Adds multi-threading and accepts an input file with a list of target hosts for simultaneous secrets…
 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…