
CVE-2025-51643
 nastycrow/cve-2025-51643
Documentation of CVE-2025-51643: physical SPI flash extraction on Meitrack T366G-L GPS tracker enabling firmware dump, plaintext credential…
data-exfiltrationembedded-systems-securityexploitation+6
nastycrow/cve-2025-51643Documentation of CVE-2025-51643: physical SPI flash extraction on Meitrack T366G-L GPS tracker enabling firmware dump, plaintext credential…
 samyk/keysweeper
KeySweeper is a stealthy Arduino-based device, camouflaged as a functioning USB wall charger, that wirelessly and passively sniffs, decrypts, logs…
 sq5bpf/etherify
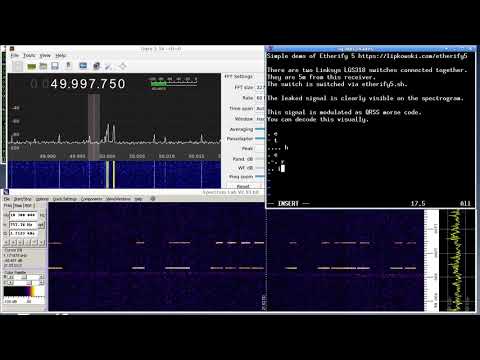
Etherify - bringing the ether back to ethernet
 kernel364/cve-2024-29973
Proof-of-concept exploit for command injection vulnerability in Zyxel NAS devices. Demonstrates arbitrary command execution via crafted HTTP…