

SteaLinG
 de3vil/stealing
The SteaLinG is an open-source penetration testing framework designed for social engineering
data-exfiltrationpayload-generationpenetration-testing-frameworks+4
249
de3vil/stealingThe SteaLinG is an open-source penetration testing framework designed for social engineering
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 azhariramadhan/cve-2026-39047
Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…
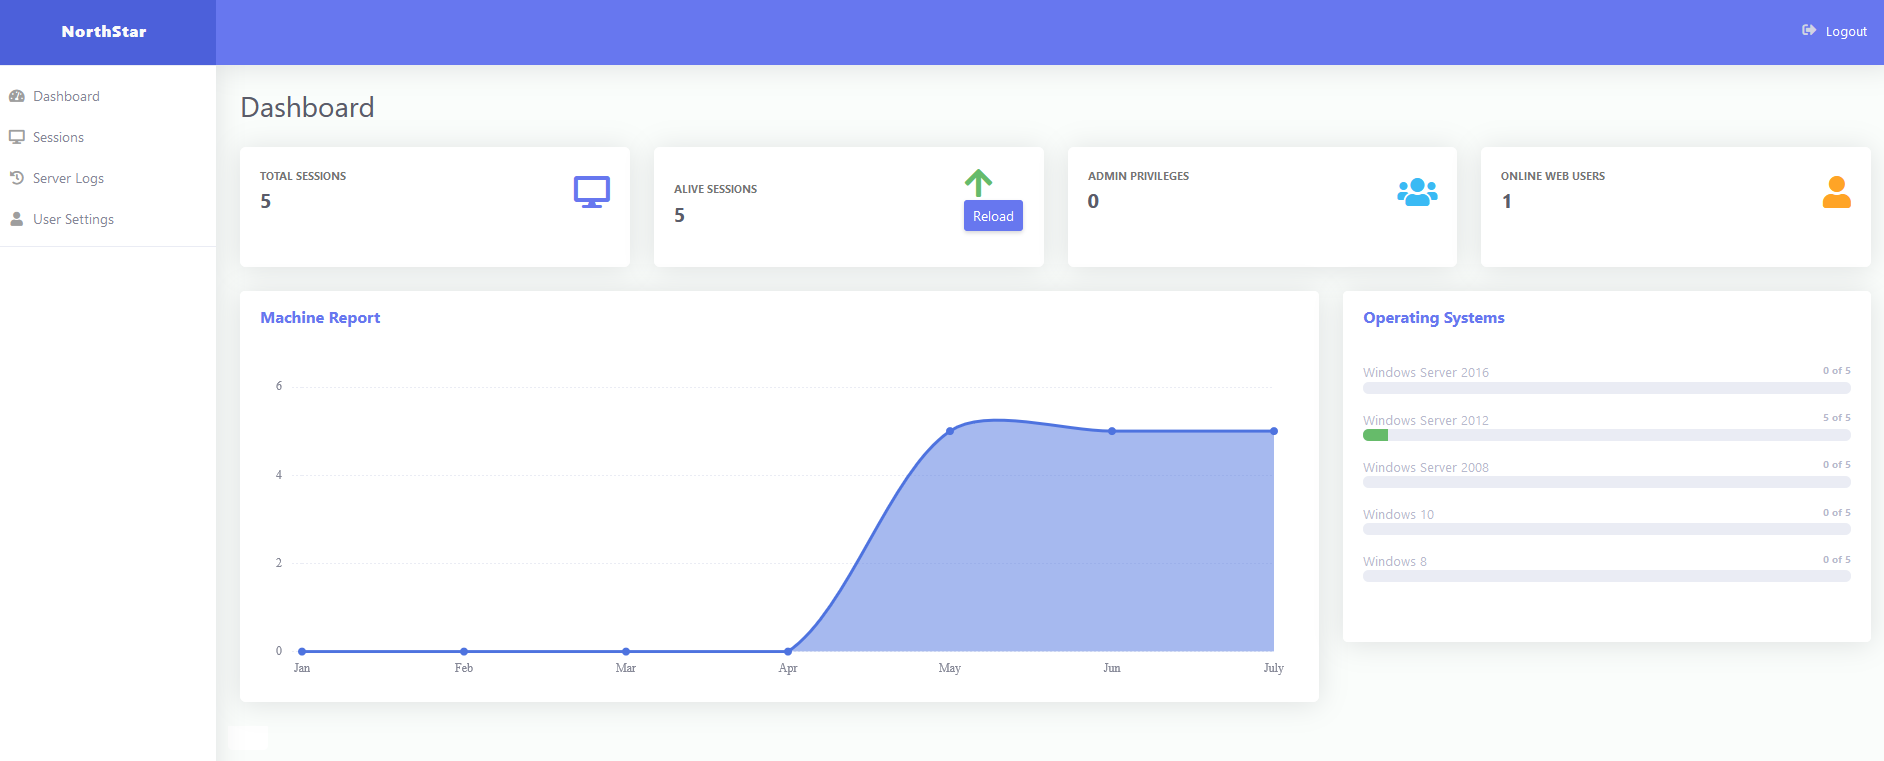 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 bishopfox/sliver
Adversary Emulation Framework
 cerberusmrxi/langflow-cve-2026-33017-exploit
CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…
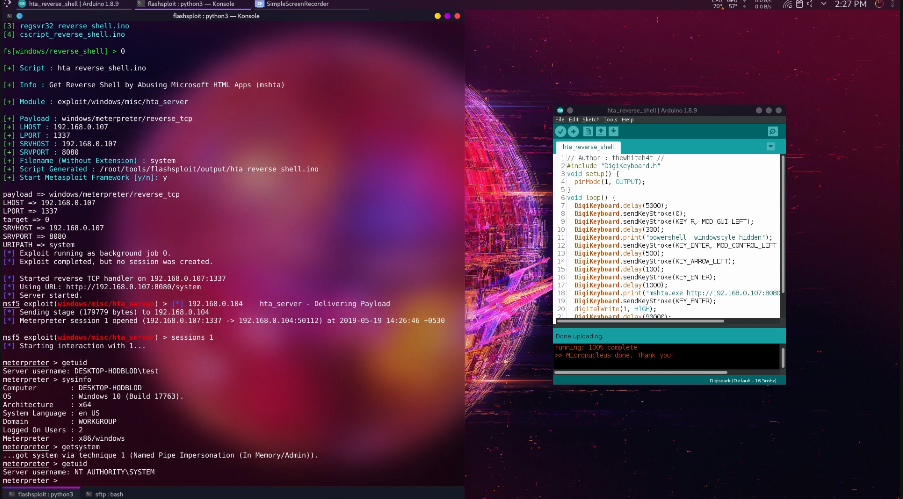 thewhiteh4t/flashsploit
Exploitation Framework for ATtiny85 Based HID Attacks
 nox-project/nox-framework
High-performance OSINT/CTI framework for automated identity pivoting and risk analysis across 120+ sources.
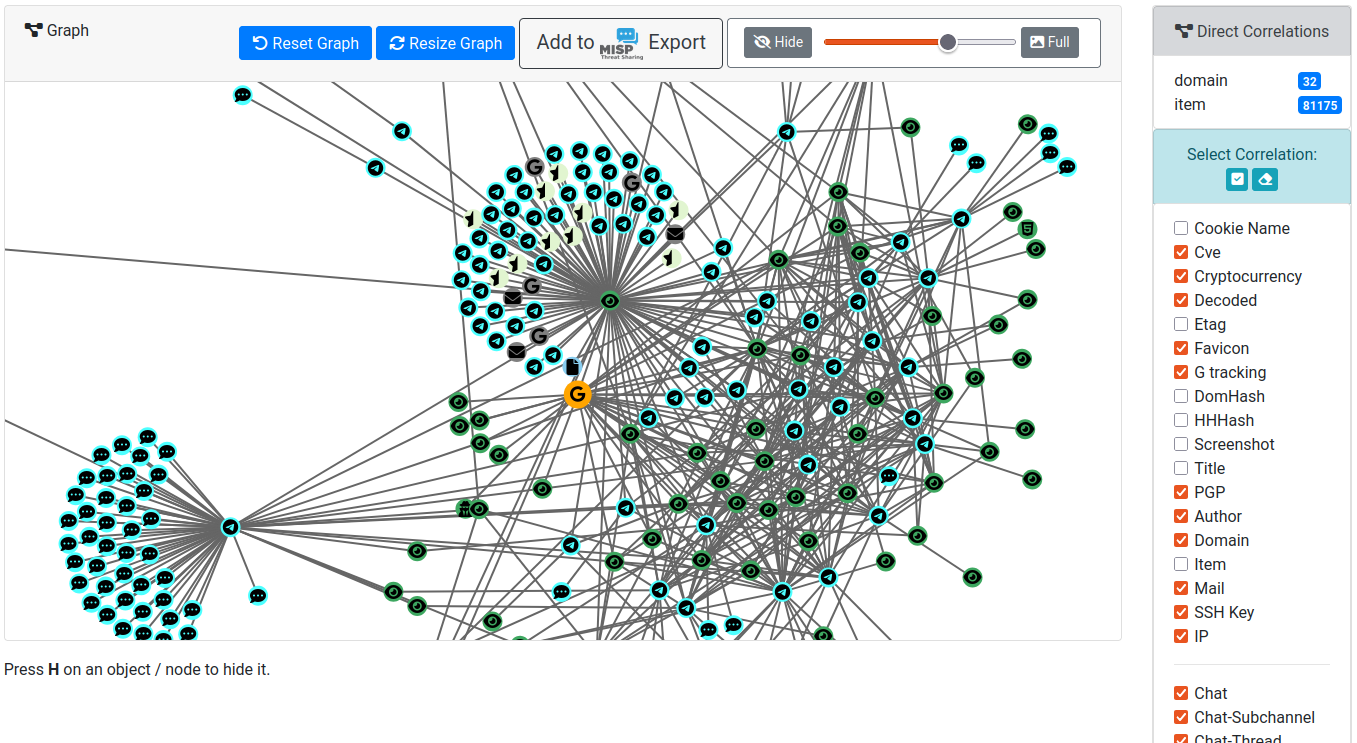 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
 flangvik/teamfiltration
Cross-platform framework for enumerating O365 accounts, password spraying, exfiltrating emails/Teams/OneDrive data, and backdooring EntraID accounts…
 luemmelsec/apex
Azure Post Exploitation Framework
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 scumfrog/fiberbreak
React2Shell Exploitation Tool (CVE-2025-55182)