phonepe-sensitive-data-exposure-cve-2025-5154

CVE-2025-5154: Proof-of-concept for unencrypted local storage of authentication tokens, PII, and KYC data in the PhonePe Android app, enabling…

CVE-2025-5154: Proof-of-concept for unencrypted local storage of authentication tokens, PII, and KYC data in the PhonePe Android app, enabling…

利用CVE-2024-0044 在Android12、13 没有root'下进行数据备份 用法./CVE-2024-0044-EXP.sh <package_name>

CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13

Python exploit for CVE-2019-6447 enabling arbitrary file read on ES File Explorer 4.1.9.7.4 for Android. Demonstrates mobile vulnerability…

Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.

Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…

PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…

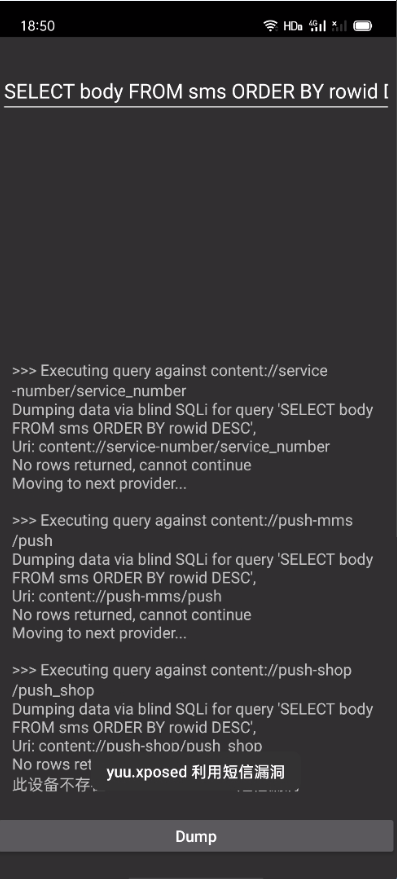
ColorOS短信漏洞,以及用户自救方案

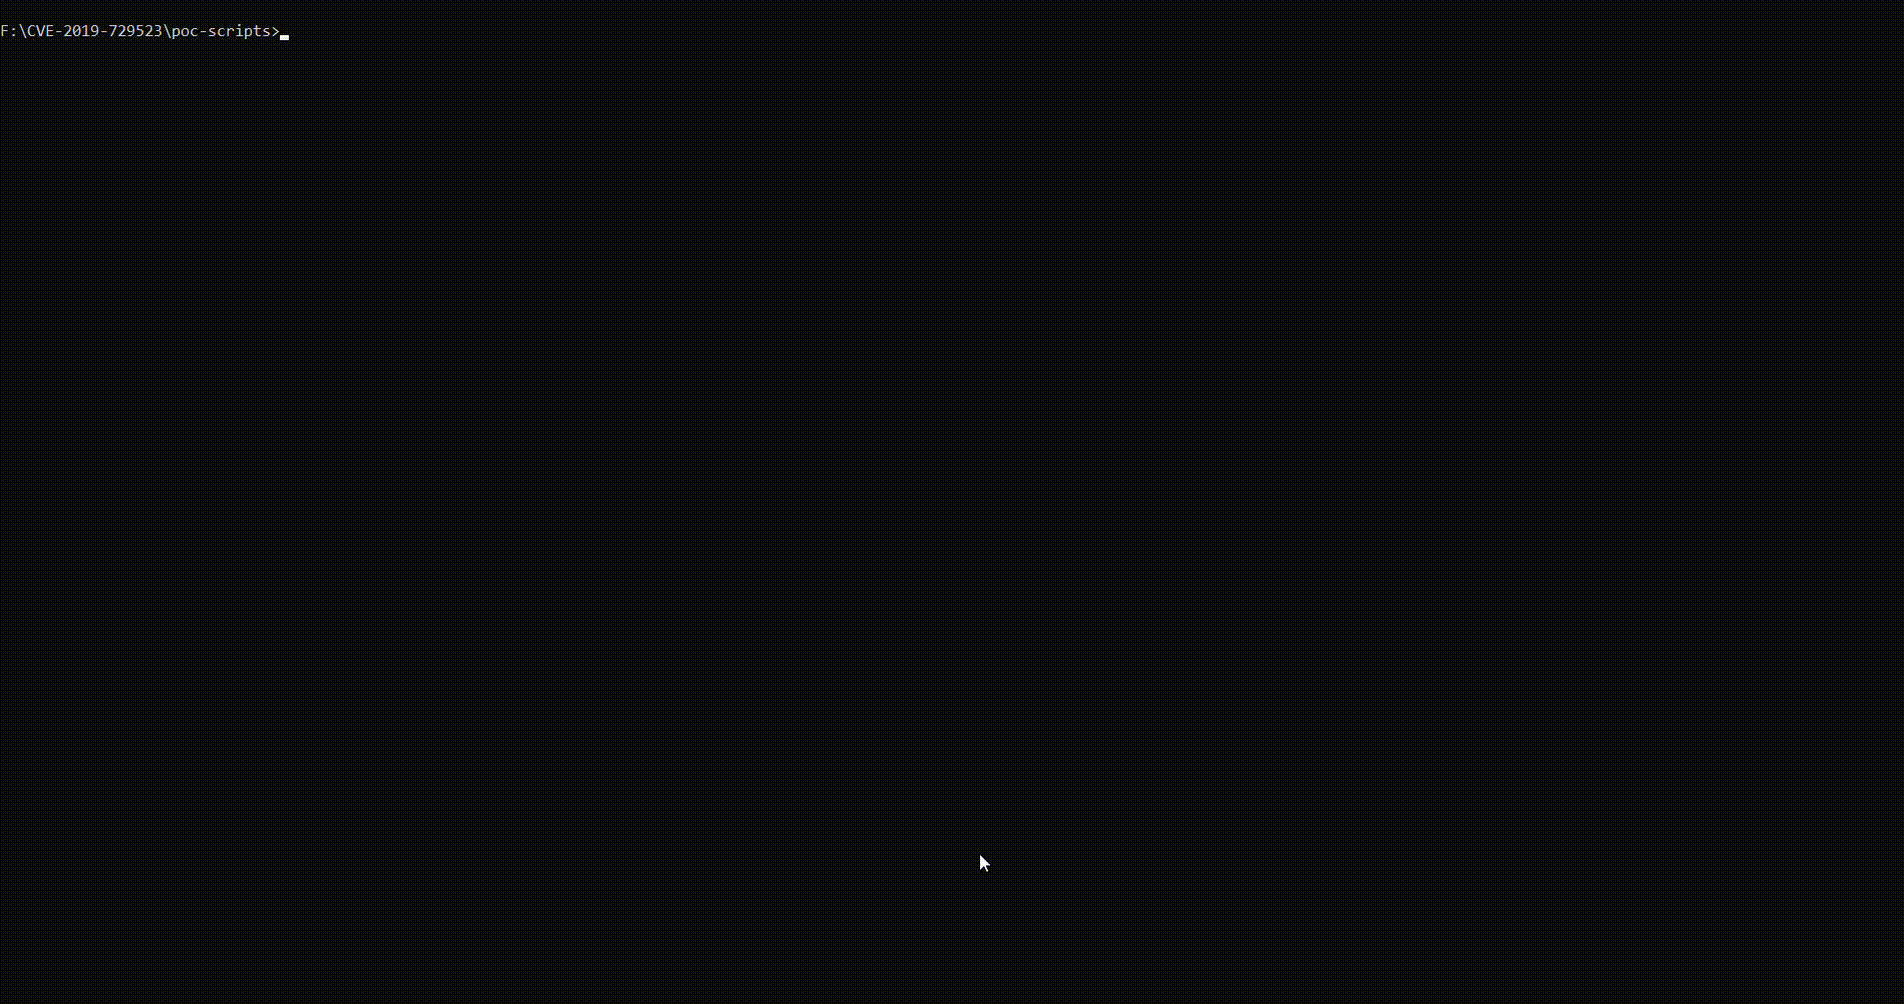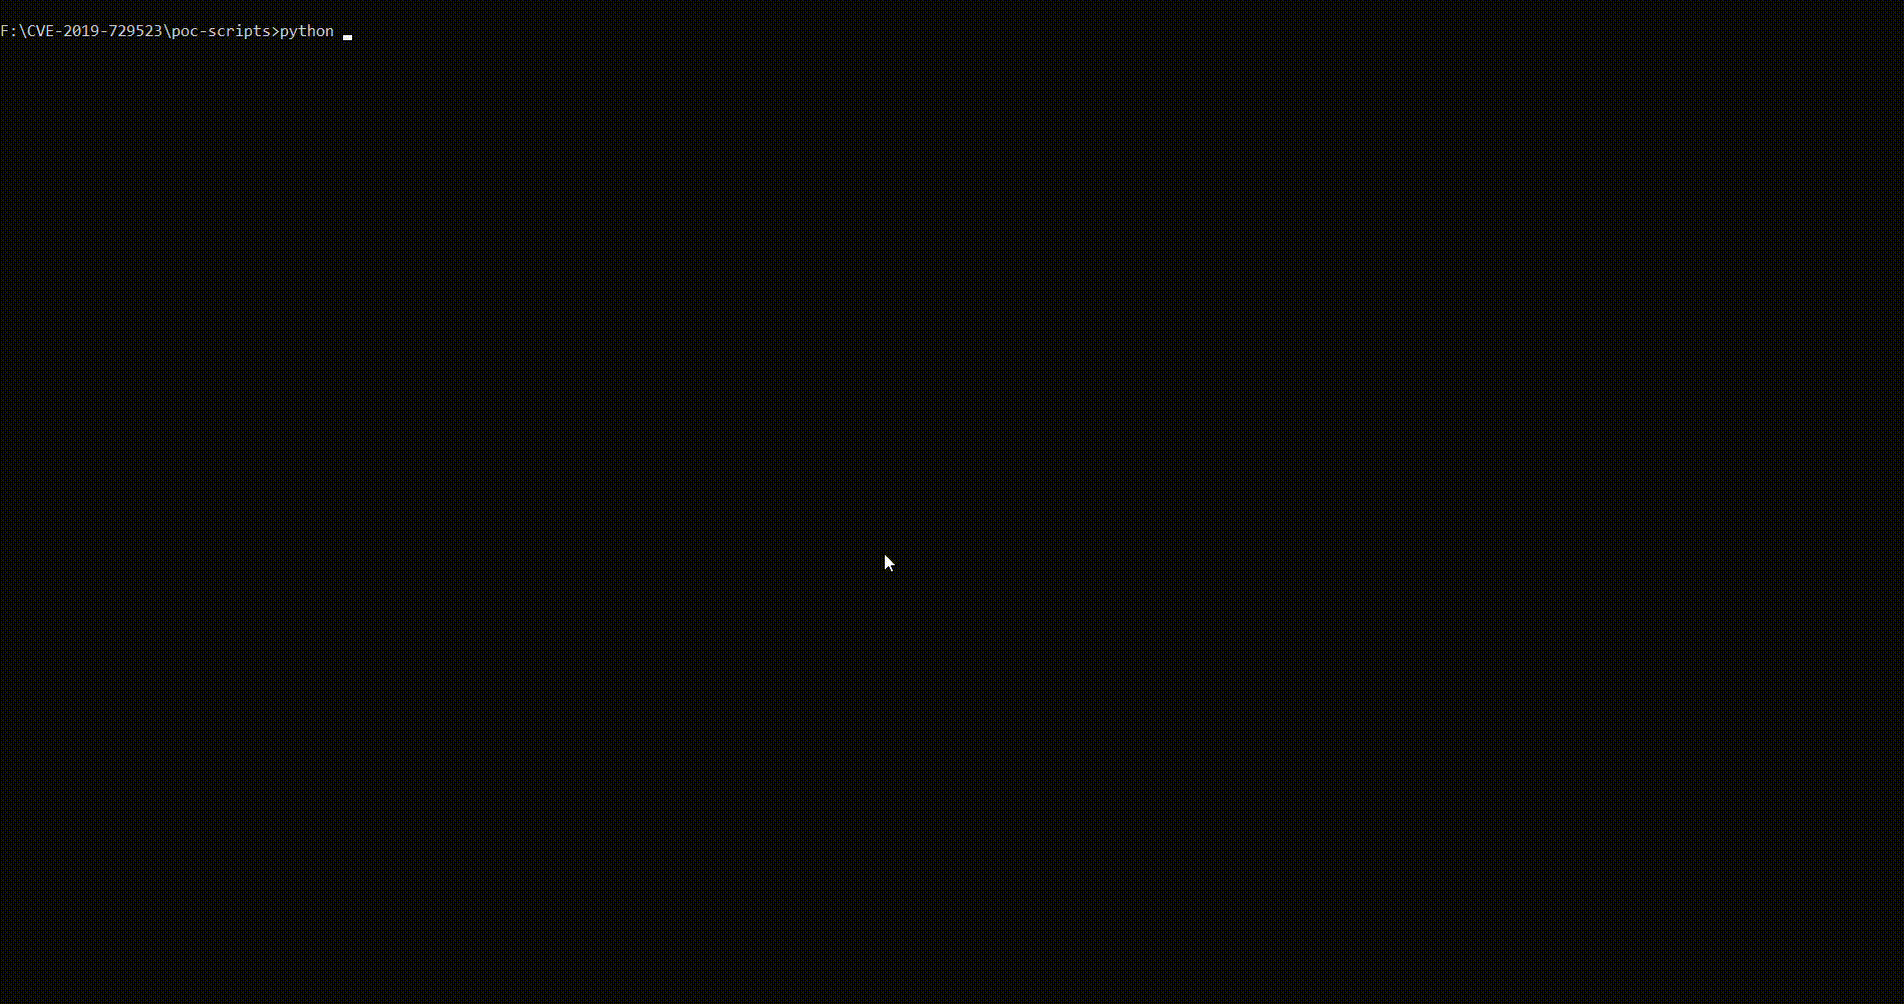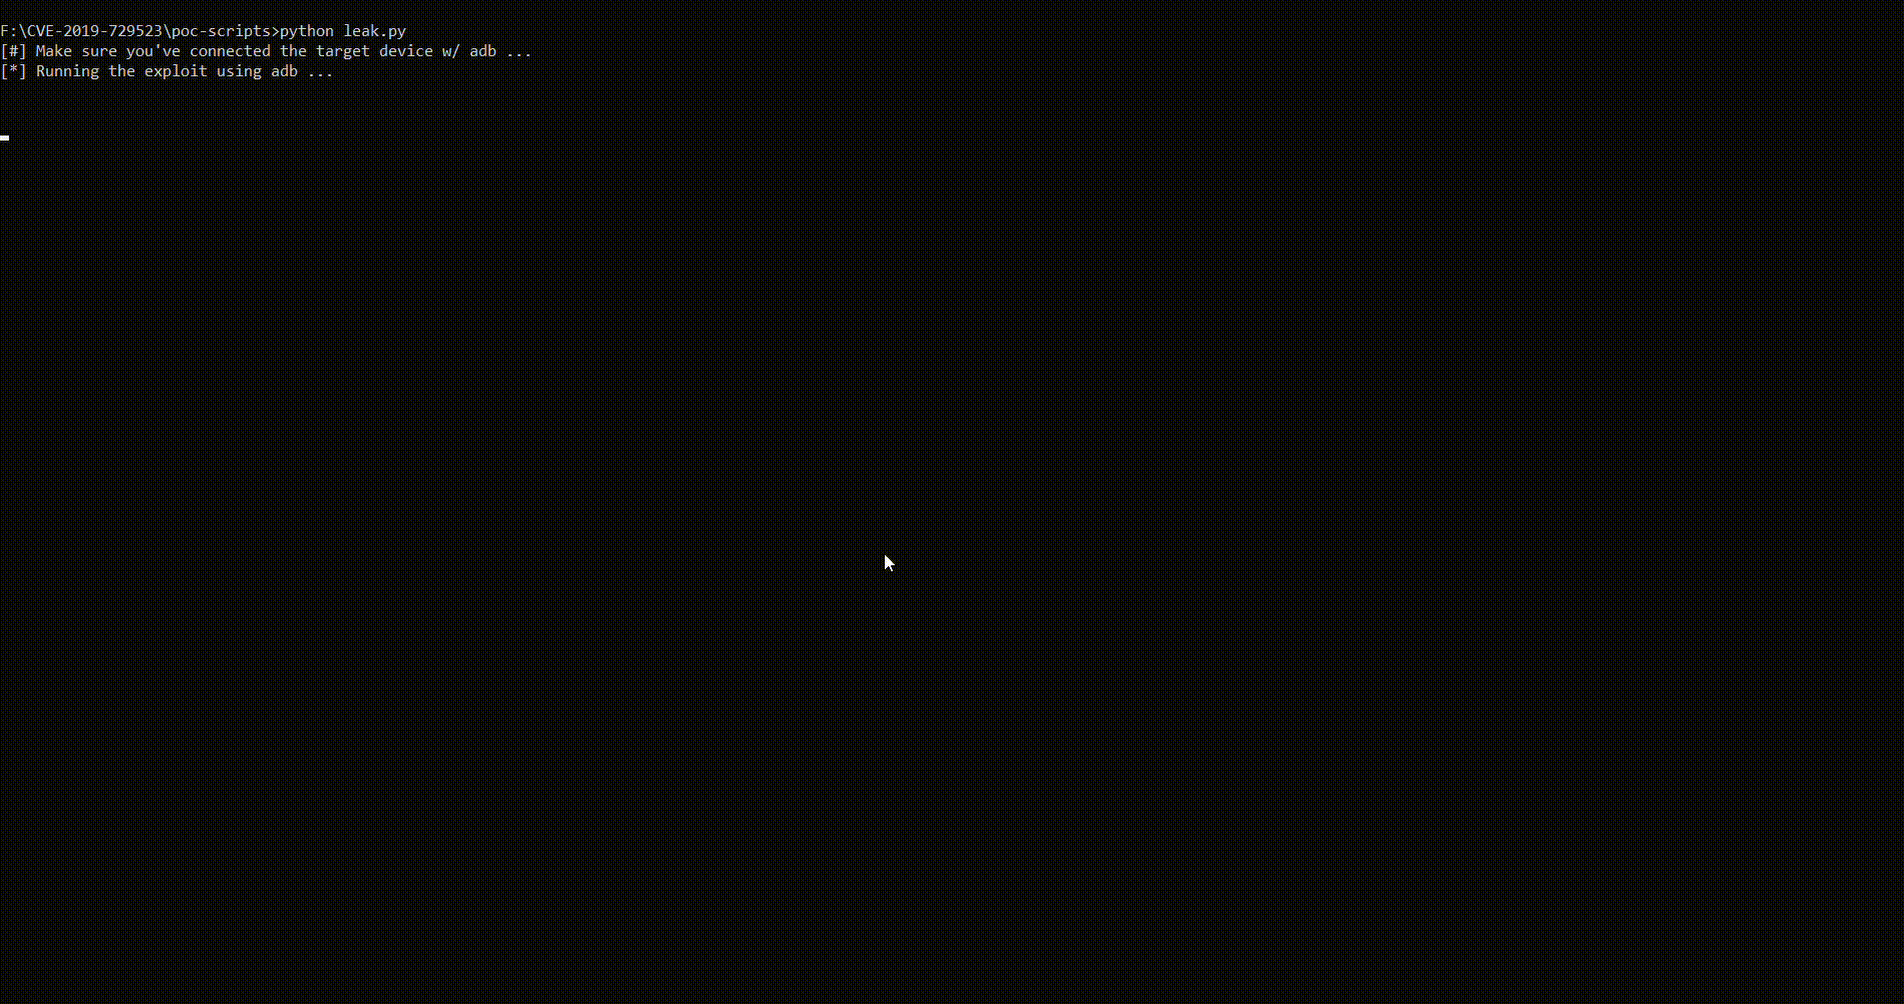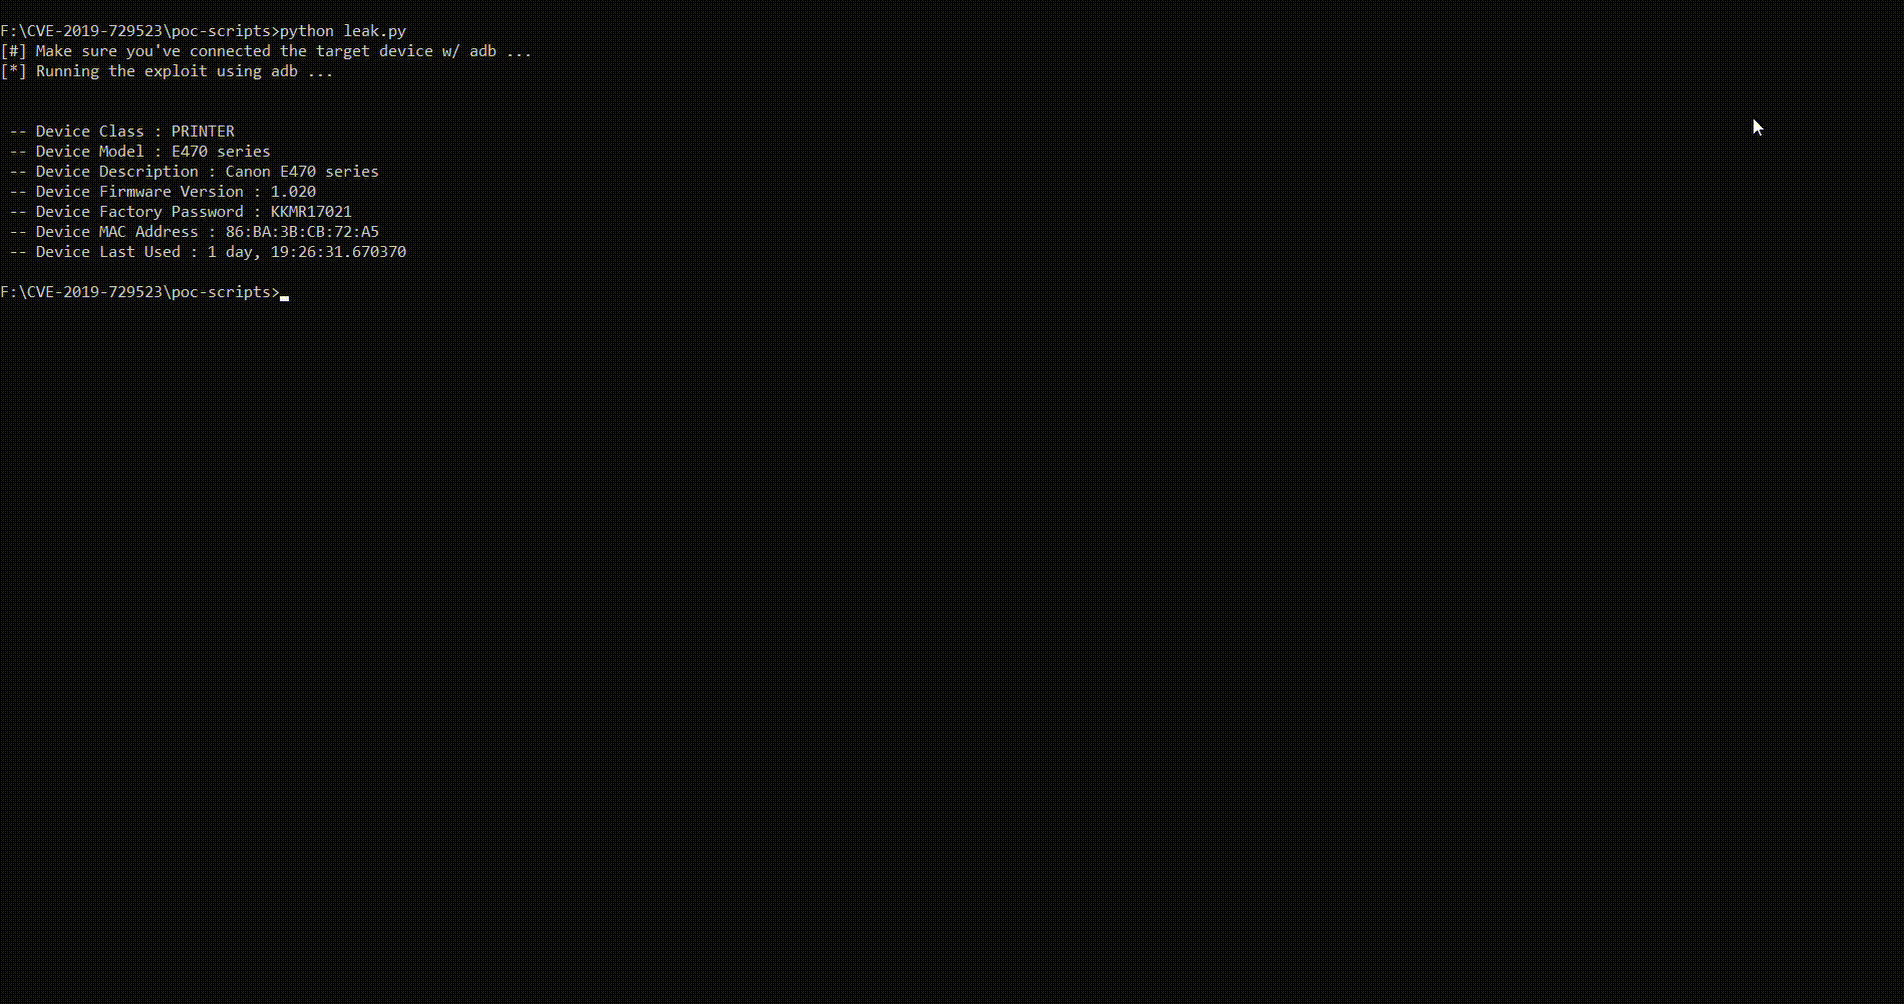
POC for CVE-2019-14339 Canon PRINT 2.5.5

Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration

A python based tool for exploiting and managing Android devices via ADB

Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…