
CVE-2025-10951
 1amunvalid/cve-2025-10951
Proof-of-concept checker for CVE-2025-10951, an unauthenticated path traversal in ml-logger, validating arbitrary file read via /glob and /stream…
data-exfiltrationexploitationinformation-gathering+3
1amunvalid/cve-2025-10951Proof-of-concept checker for CVE-2025-10951, an unauthenticated path traversal in ml-logger, validating arbitrary file read via /glob and /stream…

 toxy4ny/bl00dym4ry
Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…
 kyrieklay/cve-2026-37107
Proof-of-concept and technical write-up for CVE-2026-37107, an authenticated SSRF in HTMLy v3.1.1's feed import that enables arbitrary file read via…
 nxploited/cve-2025-7401
Premium Age Verification / Restriction for WordPress <= 3.0.2 - Unauthenticated Arbitrary File Read and Write
 fl0ydsec/cve-2026-91136
Mass scanner and PoC exploit for CVE-2026-91136, an unauthenticated arbitrary file read in the Divi Plus WordPress plugin via the svg_image REST…
 thestingr/cve-2024-36991-tool
This binary POC automates the exploitation of CVE-2024-36991 by sending crafted curl requests to a vulnerable Splunk instance. It retrieves sensitive…
 3ndg4me/adtran-personal-phone-manager-vulns
A repository hosting write ups for the 0 days CVE-2021-25679, CVE-2021-25680, and CVE-2021-25681
 george0papasotiriou/cve-2026-21015-php-filter-chain-arbitrary-file-read
PoC exploit for CVE-2026-21015 that abuses PHP filter chains to read arbitrary files through a vulnerable include() call, disclosing source and…
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
 gagaltotal/cve-2026-85706-gitlab-poc
Go exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE Workhorse via URL-encoding bypass, with concurrent requests and…
 cerberusmrxi/cve-2025-55182-advanced-react-server-components-rce-exploit
Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…
 darabium/cve-2024-28987
**CVE-2024-28987** is a critical vulnerability in SolarWinds Web Help Desk (WHD) that allows remote attackers to access sensitive ticket information…
 huseyn0vs/cve-2026-16540-simplyscheduleappointments
CVE-2026-16540 — Simply Schedule Appointments < 1.6.12.6 Unauthenticated Appointment Data Disclosure and Mass Deletion
 themehackers/cve-2026-22804
This repository contains a Proof of Concept (PoC) exploit for the Stored Cross-Site Scripting (XSS) vulnerability in Termix, which can lead to Local…
 abdulazizalsewedy/cve-2021-29447
Step-by-step demonstration of CVE-2021-29447, a WordPress Media Library XXE vulnerability leaking sensitive files via crafted WAVE uploads, including…
 smarttfoxx/cve-2025-65321
Language Sloth Sloth Bot 1.0 is vulnerable to Directory Traversal in the gif() and png() functions. The functions build file paths using unsanitized…
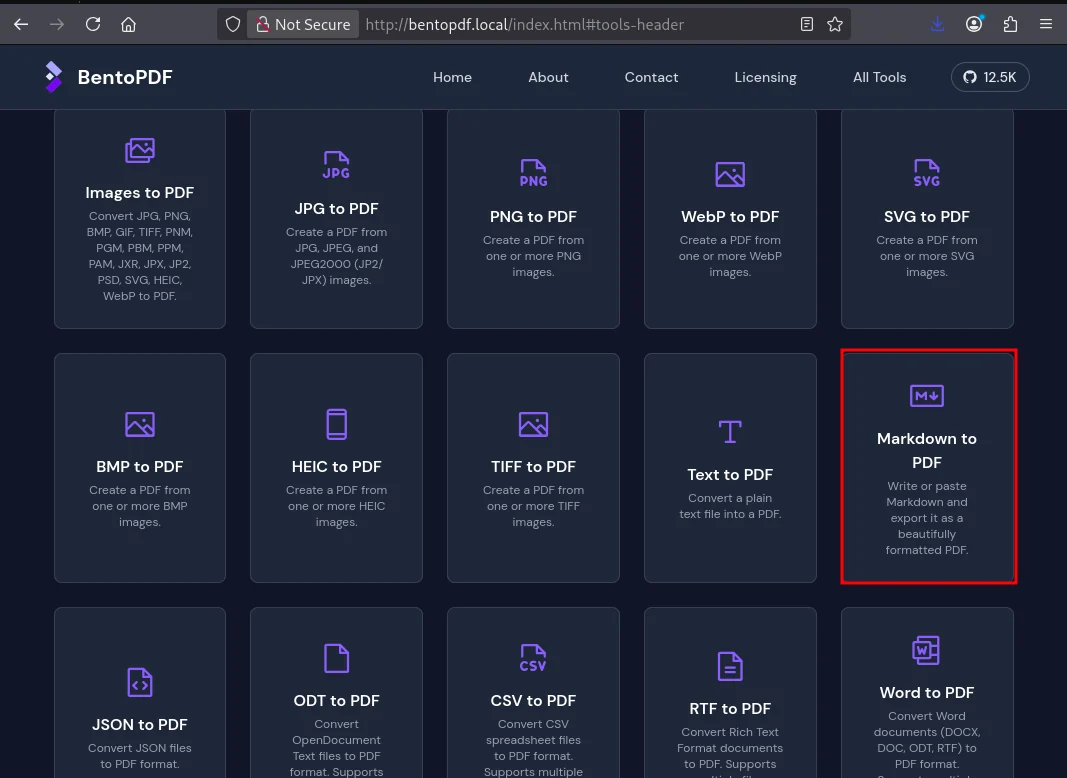 astaruf/cve-2026-41653
Proof-of-concept exploit for CVE-2026-41653, a stored XSS in BentoPDF that enables silent file exfiltration and WASM supply-chain hijacking.
 emanuelepns/immich-exfiltration-demo
Cybersecurity demo exploiting CVE-2026-35455 with automatic API key generation and exfiltration