
grafeo
 mnemonic-no/grafeo
Open platform for modelling, collection and exchange of knowledge
data-exfiltrationinformation-gatheringthreat-intelligence+1
165
mnemonic-no/grafeoOpen platform for modelling, collection and exchange of knowledge
 infostealers-stats/data-breach
A continuously updated resource that catalogs confirmed data breaches from across the globe. Each entry includes the breach name, usually aligned…
 joelgmsec/fakedatagen
Generates fully valid fake identities in Spanish format, including names, emails, bank details, and extended info, with optional zip compression and…
 bsysop/servicenow
Scans ServiceNow instances for widget-simple-list plugin misconfigurations that expose data via the API, supporting single URLs, URL lists,…
 pwardle/not-a-mused
Proof-of-concept exploiting an undocumented Muse dictation endpoint setting, letting a local unprivileged process redirect dictation traffic to…
 albertrg99/redditosint
Reddit OSINT by username. Discover indexed posts, comments, deleted and live content, activity patterns, exposed identifiers, and an overall exposure…
 prodefense/hawk
Golang tool designed to exfiltrate passwords found via the sshd and su services
 eqstlab/cve-2026-85706
PoC and Docker lab for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via the commits API route bypass and urlencoded error…
 mustafadalga/wildlogger
This is a keylogger that collects all the data and e-mail it in a set time with system information which includes device S/N and hardware specs,…
 momika233/cve-2022-3656
Proof-of-concept exploit for CVE-2022-3656, a Chrome/Chromium vulnerability enabling theft of sensitive files like encrypted wallets and cloud…
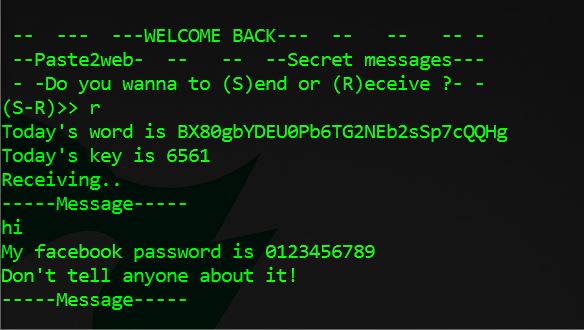 d4vinci/paste2web
A python3 script that uses cl1p website to send and receive secret messages
 ac3lives/kyocera-cve-2022-1026
An unauthenticated data extraction vulnerability in Kyocera printers, which allows for recovery of cleartext address book and domain joined passwords
 bhavikmalhotra/threatpad
Open-source collaborative note-taking platform for cybersecurity and CTI teams. IOC auto-extraction, STIX 2.1 export, real-time editing, RBAC,…
 robertaitch/telegram-story-scraper
A Python script that allows you to automatically scrape and download stories from your Telegram friends using the Telethon library. The script…
 taurusomar/pulsegram
Python-based keylogger with Telegram bot integration for capturing keystrokes, clipboard content, and screenshots in authorized security testing…
 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
 deathshotxd/cve-2025-52691-apt-poc
An enhanced proof-of-concept exploit for CVE-2025-52691 (SmarterMail Arbitrary File Upload RCE) with APT-level features like stealth obfuscation,…
 absholi7ly/apache-ofbiz-directory-traversal-exploit
Exploit for Apache OFBiz CVE-2024-32113 path traversal via crafted XML-RPC requests, enabling arbitrary file read and potential command execution on…